The Uptycs threat research team discovered the first ransomware binary attributed to the RTM ransomware-as-a-service (RaaS) provider. The new variant of the encryptor targets Linux, NAS, and ESXi hosts, it appears to be based on the source code of Babuk ransomware that was leaked online in 2021. The encryptor uses a combination of ECDH on Curve25519 (asymmetric encryption) and Chacha20 (symmetric encryption) to encrypt files.
Researchers from cybersecurity firm Trellix first detailed this month the tactics, techniques, and procedures of the emerging cybercriminal gang called ‘Read The Manual RTM Locker. The group operates a ransomware-as-a-service (RaaS) and provides its malicious code to a network of affiliates by imposing strict rules. The group aims at flying below the radar, and like other groups, doesn’t target systems in the CIS region.
The group also avoids targeting morgues, hospitals, COVID-19 vaccine-related organizations, critical infrastructure, law enforcement, and other prominent companies to attract as little attention as possible.
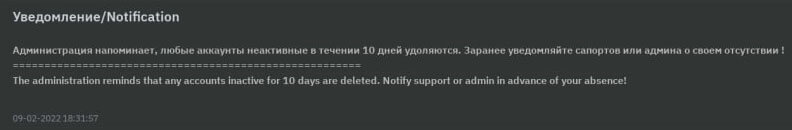
The affiliates are obliged to remain active, or their account will be removed after 10 days without notifying them upfront.
The gang’s affiliates must keep the RTM Locker malware builds private to prevent they can be analyzed. The researchers discovered that the samples contain a self-delete mechanism which is invoked once the victim’s device is encrypted. The group threatens to ban every affiliate who does leak samples.
RTM Locker specifically targets ESXi hosts and the malicious code supports the following two ESXi commands:
“RTM Locker was identified during Uptycs’ dark web hunting. Its malware is specifically geared toward ESXi hosts, as it contains two related commands. Its initial access vector remains unknown. Both asymmetric and symmetric encryption make it impossible to decrypt files without the attacker’s private key.” reads the analysis published by Uptycs.
At the time of this writing, the initial access vector is unknown.
Once encrypted the files, the ransomware drops a ransom note in each directory containing the encrypted files. The note contains instructions to contact the operators via Tox, the group threatens to leak stolen files if the victims will not contact them within 48 hours.
Blogger Awards 2022 – VOTE FOR YOUR WINNERS
Vote for me in the sections:
Please nominate Security Affairs as your favorite blog.
Nominate here: https://docs.google.com/forms/d/e/1FAIpQLSfaFMkrMlrLhOBsRPKdv56Y4HgC88Bcji4V7OCxCm_OmyPoLw/viewform
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Uptycs)
MonsterCloud owner Zohar Pinhasi allegedly paid ransomware demands behind clients’ backs, then charged them millions…
The U.S. offers $10M for Zhang Yu, accused of helping run HAFNIUM attacks that compromised…
Threat actors are exploiting CVE-2026-21589, a critical Atlassian flaw that can expose sensitive files across…
SonicWall patched a CVSS 10 pre-auth SSRF flaw in SMA1000 appliances that could let unauthenticated…
FBI and Secret Service warn FortiBleed, a credential-harvesting campaign against Fortinet firewalls, has compromised 86,644…
Over 100 hacked websites used fake Cloudflare checks to trick visitors into installing LunexStealer through…
This website uses cookies.