 Pierluigi Paganini
 October 29, 2026
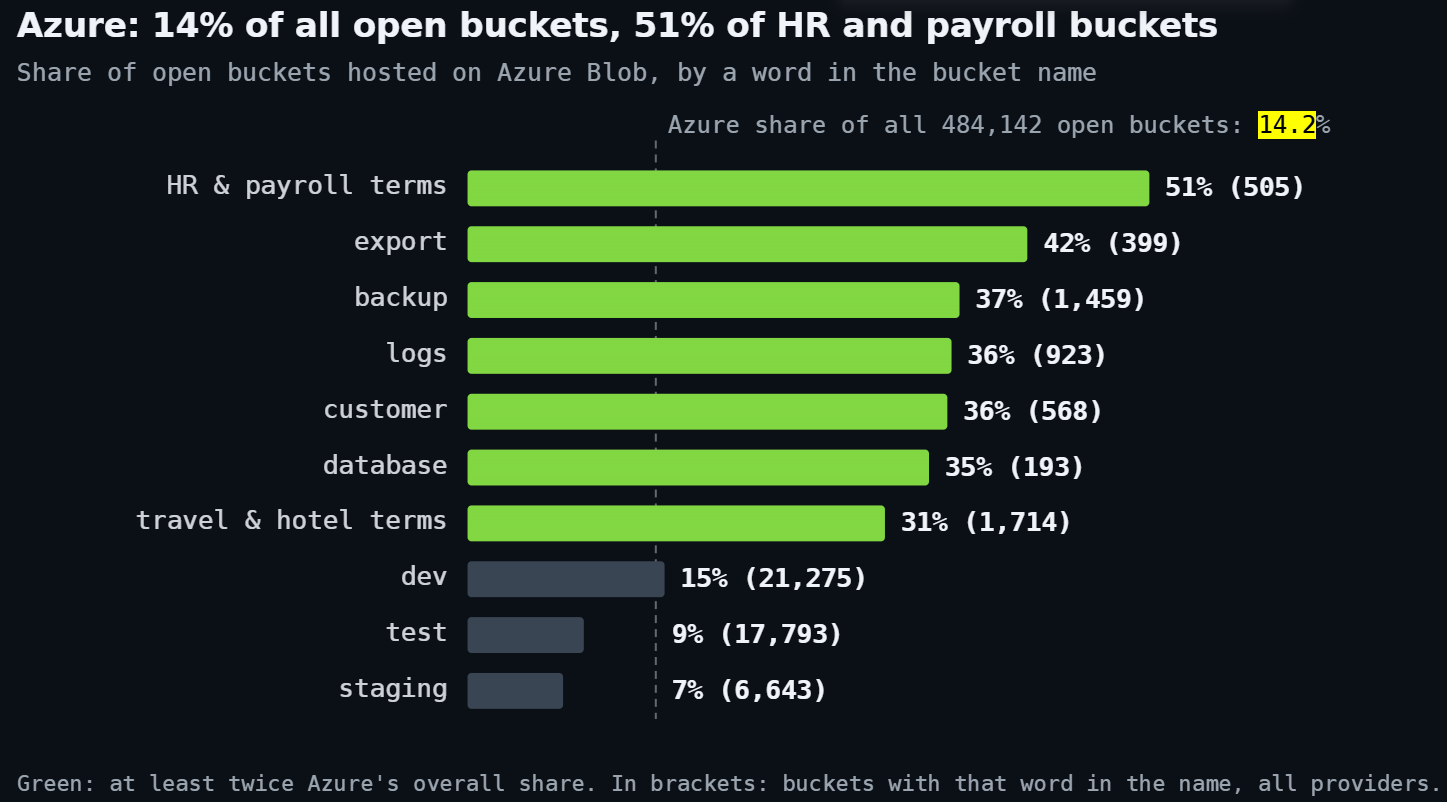
42 publicly listable cloud buckets containing 18 billion files, including exposed credentials, database dumps and backups. The Ransomnews research team counted 484,142 publicly listable cloud storage buckets in October 2026, holding 18.05 billion files. They built the count from the search engines that index open cloud storage and published it as the Ransomnews Cloud Exposure […]
 Pierluigi Paganini
October 22, 2026
SafePay ransomware has hit 600+ organizations since 2024, using stolen credentials, VPN access and double extortion to pressure victims into paying. CISA, the FBI, the US Secret Service, Germany’s Landeskriminalamt Rheinland-Pfalz, and two UK law enforcement agencies jointly published an advisory this week on SafePay, a ransomware group they describe as one of the most […]
 Pierluigi Paganini
September 14, 2026
Frontier AI is compressing the attack lifecycle from vulnerability discovery to exploitation, forcing defenders to detect, patch and respond at machine speed. Cybersecurity has always been a race between attackers and defenders. ENISA’s latest assessment suggests that frontier AI is changing the speed of that race, and the gap between discovering a vulnerability and exploiting […]
 Pierluigi Paganini
September 12, 2026
AI is becoming an operational force for cybercrime, surveillance, propaganda, fraud and weapons development, lowering the cost and scale of attacks. Artificial intelligence (AI) is becoming more than a tool for people who want to do something malicious. It is increasingly becoming part of the operational machinery itself. That is the main message emerging from […]
 Pierluigi Paganini
August 26, 2026
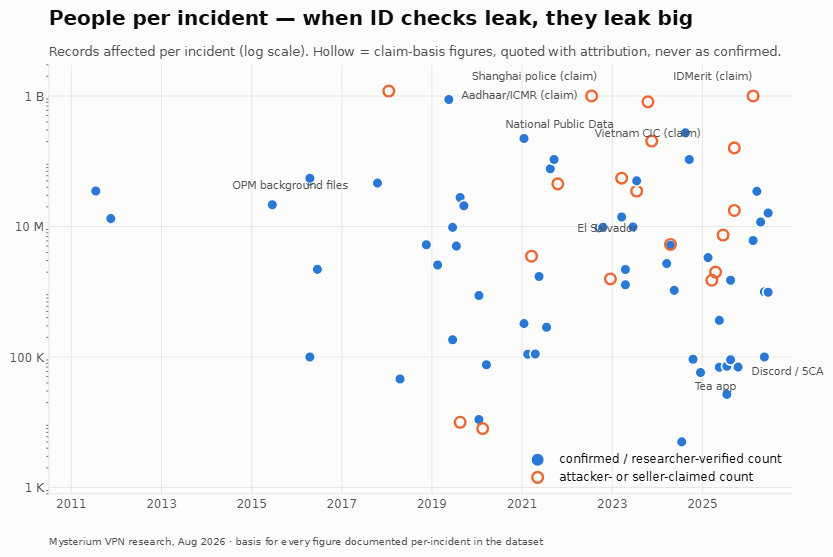
88 ID-verification breaches exposed billions of records, highlighting the growing risks of collecting sensitive identity and biometric data. A new report from Mysterium VPN compiles 88 documented incidents since 2011 where data collected specifically to verify someone’s identity or age got breached, exposed, or sold. The confirmed and researcher-verified total sits at 2.15 billion records, […]
 Pierluigi Paganini
July 31, 2026
An AI-assisted audit found 29 flaws in GlobaLeaks, showing LLMs make large-scale code reviews faster, cheaper, and accessible. GlobaLeaks, a mature whistleblowing platform that had already undergone six independent professional audits over the past thirteen years, was subjected to an LLM-assisted security review that cost roughly USD 3,140 in API calls. The review identified 29 […]
 Pierluigi Paganini
July 27, 2026
A new report links 148 ransomware attacks to Italian organizations in H1 2026, with manufacturing the most targeted sector. Six months, 148 confirmed ransomware claims against Italian targets, and one sector taking the brunt of it. That’s the headline number from a new semi-annual tracker compiled by ransomNews under its RedACT project, which pulls together […]
 Pierluigi Paganini
July 24, 2026
US agencies warn Russian group Laundry Bear is exploiting a patched Zimbra flaw to steal email accounts from organizations running unpatched servers. The Cybersecurity and Infrastructure Security Agency (CISA), National Security Agency (NSA), Federal Bureau of Investigation (FBI) and other U.S. government and international partners published a joint advisory to warn that the Russia-linked APT […]
 Pierluigi Paganini
July 15, 2026
US and allies warn of Russian APT groups targeting routers and network devices to compromise critical infrastructure worldwide. The US and allied governments warn that Russian state-sponsored APT groups are scanning and exploiting poorly secured network devices, especially routers, to access critical infrastructure. Groups linked to FSB Center 16, including Berserk Bear, Energetic Bear, Ghost […]
 Pierluigi Paganini
July 10, 2026
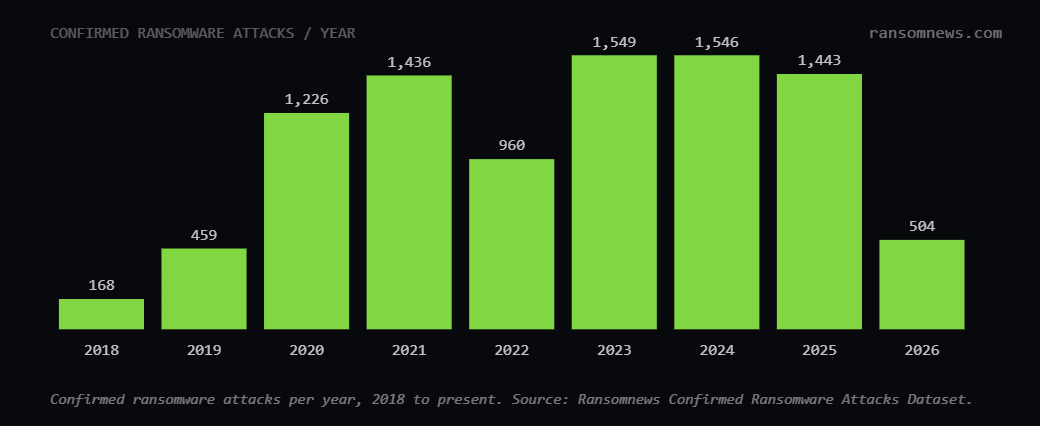
Ransomware remains above 1,400 attacks yearly since 2023. Qilin leads in 2026, while the U.S. remains the main target. Ransomnews has independently confirmed 9,291 ransomware attacks worldwide between January 2018 and July 2026, tracking incidents only when verified through victim disclosures, regulatory filings, official statements, or credible press reporting. Leak-site listings alone don’t qualify, operators […]
Malware / November 02, 2026
Security / November 02, 2026