 Pierluigi Paganini
 October 17, 2026
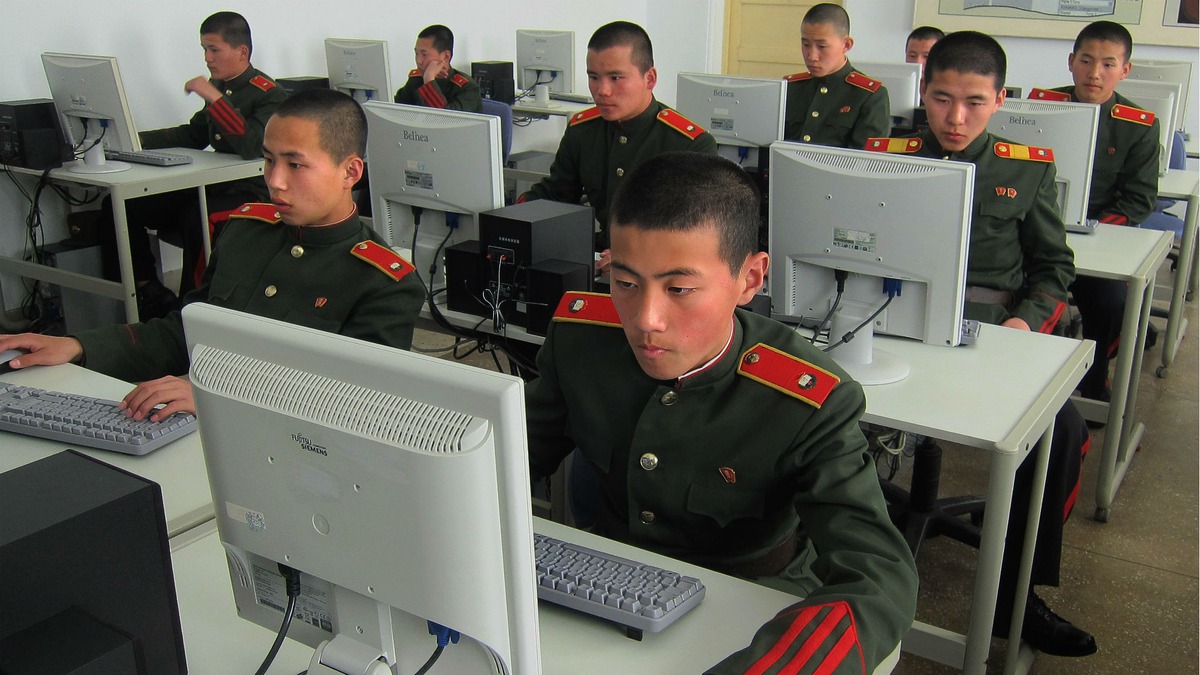
The FBI raided 40 Texas homes over a North Korean scheme that used fake IT workers to target 70 US companies and generate $3 million. The Justice Department (DoJ) announced coordinated enforcement actions this week targeting North Korea’s long-running scheme to place fake IT workers inside American companies. Two US nationals were arrested, 14 people […]
 Pierluigi Paganini
October 08, 2026
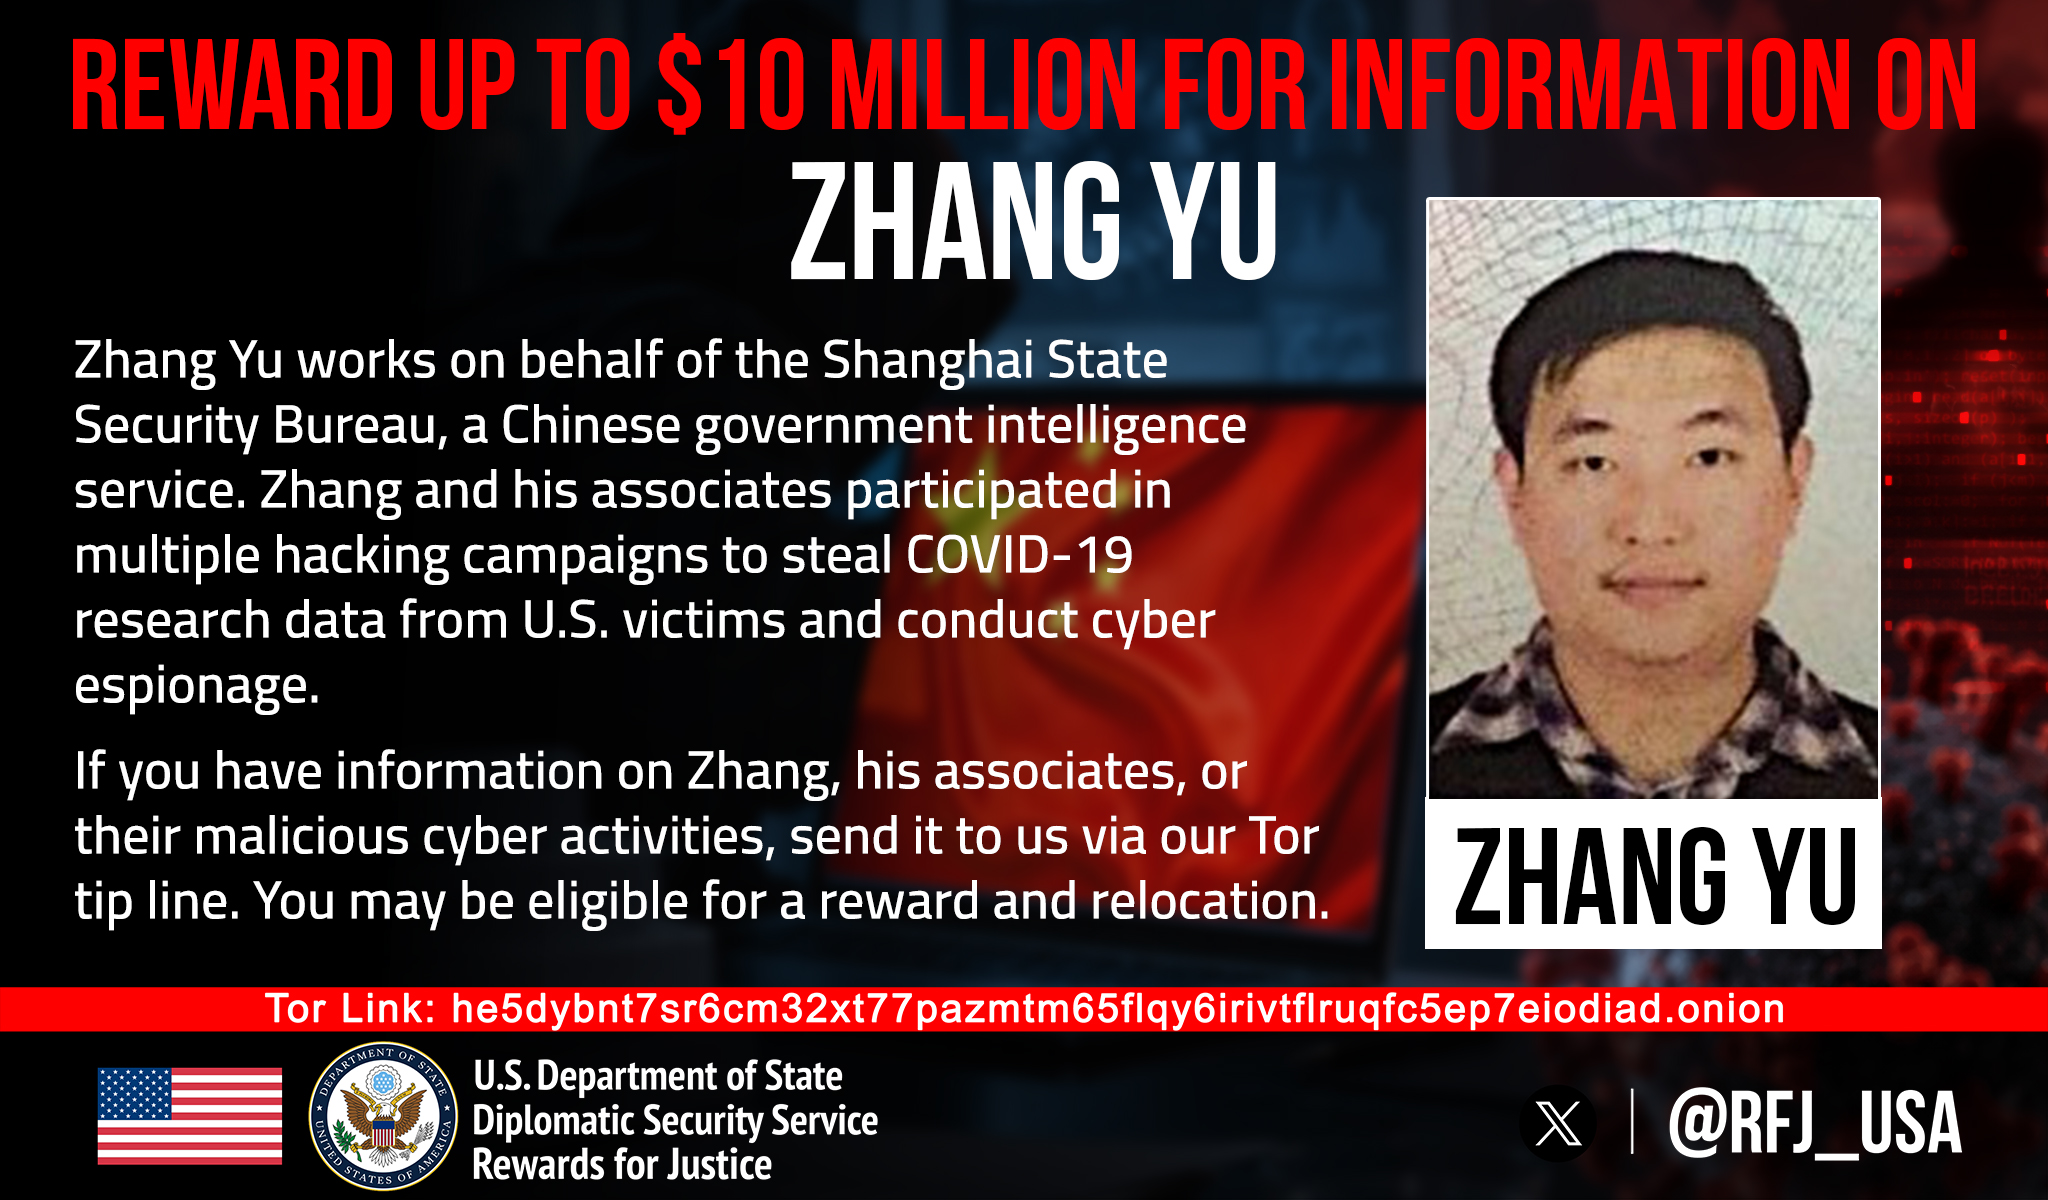
The U.S. offers $10M for Zhang Yu, accused of helping run HAFNIUM attacks that compromised thousands of organizations worldwide. The U.S. State Department is offering a $10 million reward for information leading to the arrest of Zhang Yu. He is accused of being a key figure in the HAFNIUM campaign, the 2021 operation that targeted […]
 Pierluigi Paganini
October 05, 2026
MI5 warns UK universities that over 100 academics may have unknowingly worked on research funded by a Chinese institute linked to the MSS. On September 30, MI5 published a formal warning naming the China General Technology Research Institute, CGTRI, also called CAGT in some translations, as an outfit with very strong ties to China’s Ministry […]
 Pierluigi Paganini
October 03, 2026
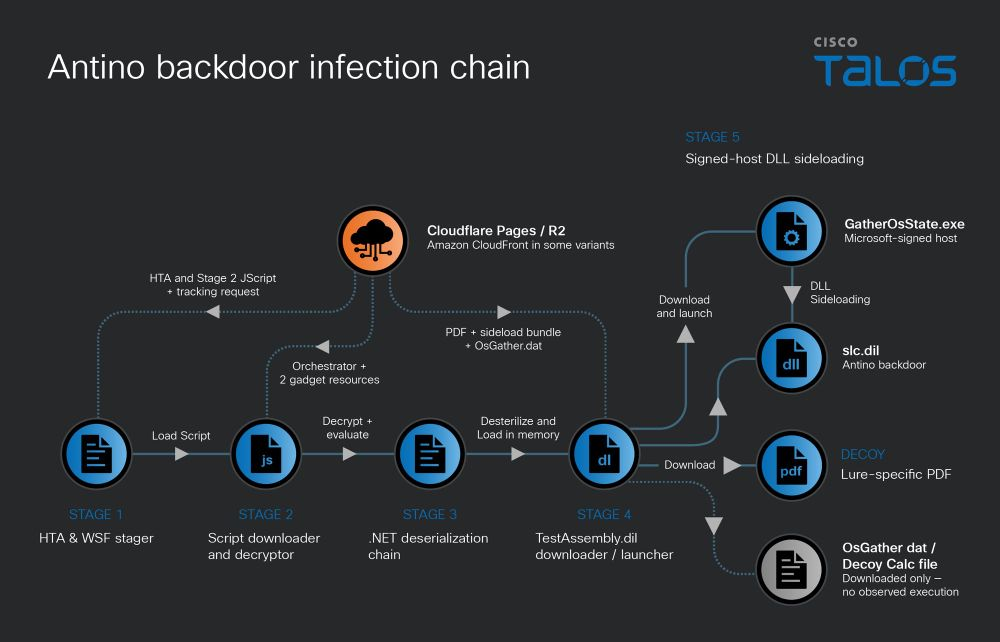
Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments. Cisco Talos has been tracking a cluster of espionage activity since September 2025 that it calls UAT-11587, and by July 2026 the group had hit at least 16 government and policy organizations across eight […]
 Pierluigi Paganini
September 30, 2026
DOJ charges against Oxygen Forensics reveal the Russian-linked firm also sold forensic software to EU projects and European police forces for years. Last week’s Justice Department indictment of Oxygen Forensics looked, at first, like an American procurement scandal. CEO Lee Reiber and Russian co-founder Oleg Davydov stand accused of hiding that the company was Russian-owned […]
 Pierluigi Paganini
September 20, 2026
An AI-generated intelligence report falsely identified weapons on a Chinese ship, nearly triggering a US military operation during the Iran war. According to CNN, four sources familiar with the episode say an intelligence report circulated through the military claiming a Chinese vessel in the Middle East was carrying components for a nuclear weapons program. The […]
 Pierluigi Paganini
September 17, 2026
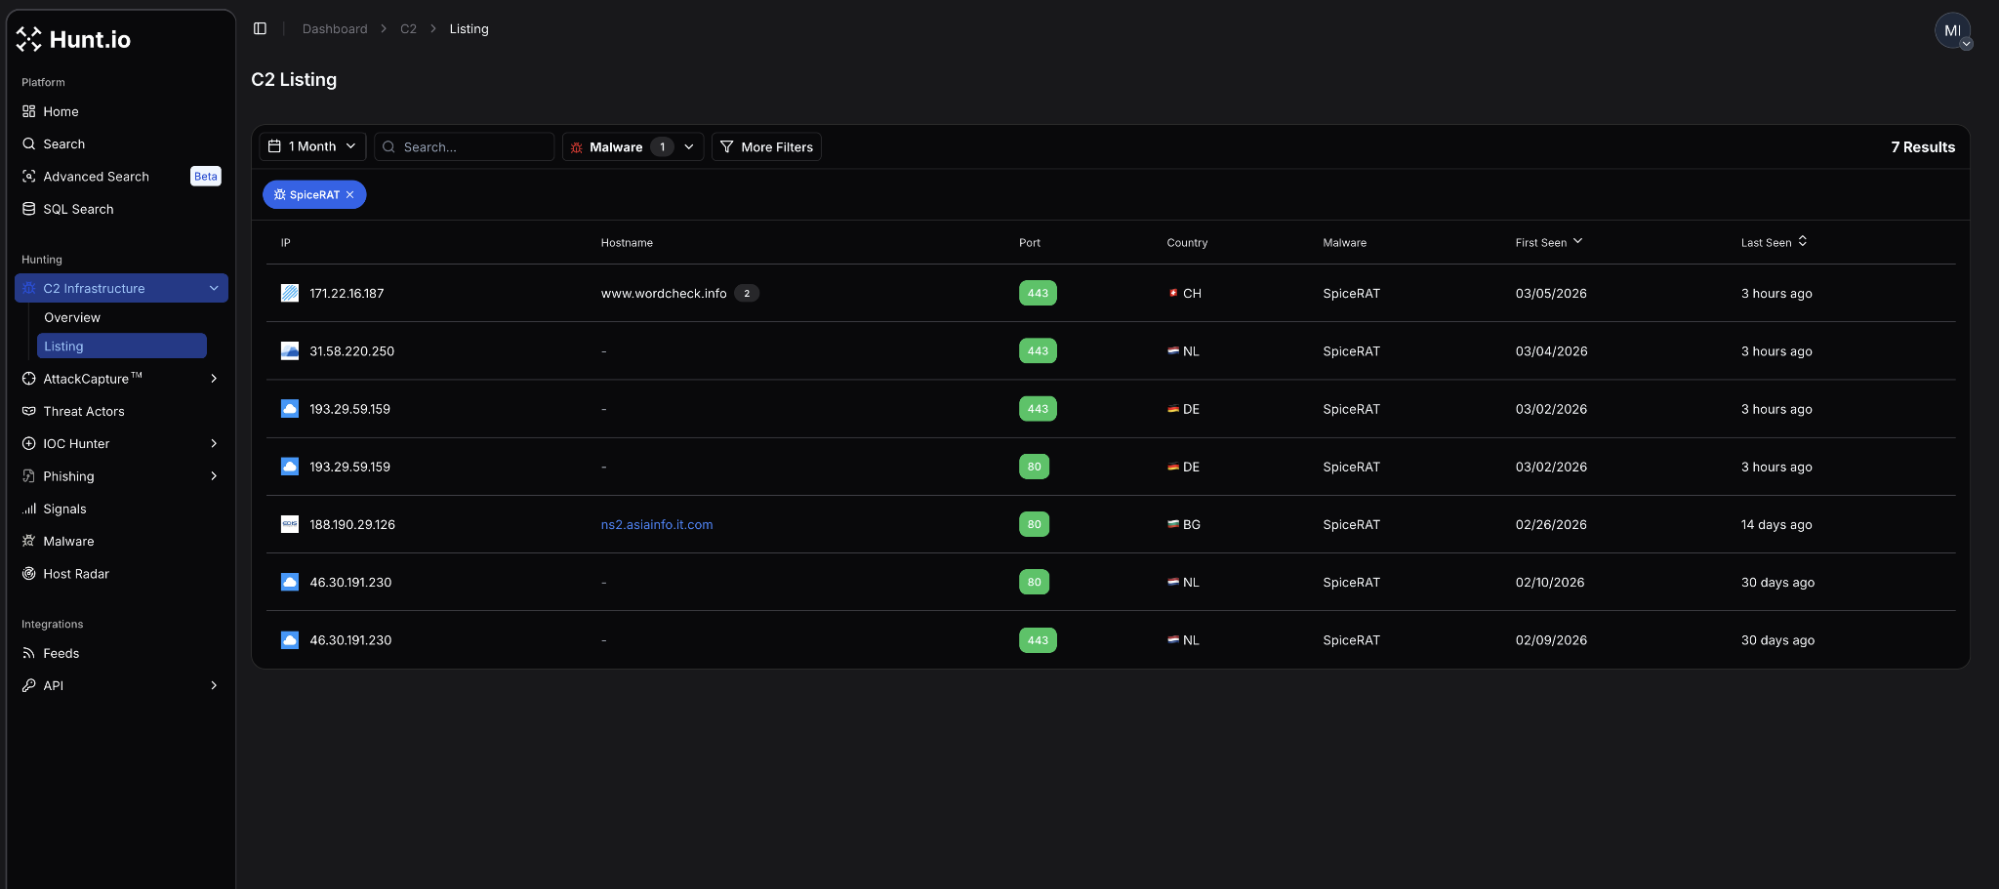
Hunt.io links SpiceRAT, NodeEdgeRAT and NomadRAT to a four-year SilkParasite campaign targeting governments and critical sectors in Central Asia. Hunt.io and researcher Guy Yasur have traced a tight cluster of SpiceRAT command‑and‑control servers that predate and extend Bitdefender’s August 2026 SilkParasite report. The work doesn’t dissect malware samples; it maps the network side of the […]
 Pierluigi Paganini
September 17, 2026
UK, US, and Dutch agencies expose Chosen Brick, Iranian malware used to track and harass dissidents, journalists, and activists via Telegram. The UK, the US, and the Netherlands published a joint advisory warning about a Windows malware family, dubbed Chosen Brick, that Iran’s intelligence services use to track down dissidents, journalists, and activists, and the […]
 Pierluigi Paganini
September 10, 2026
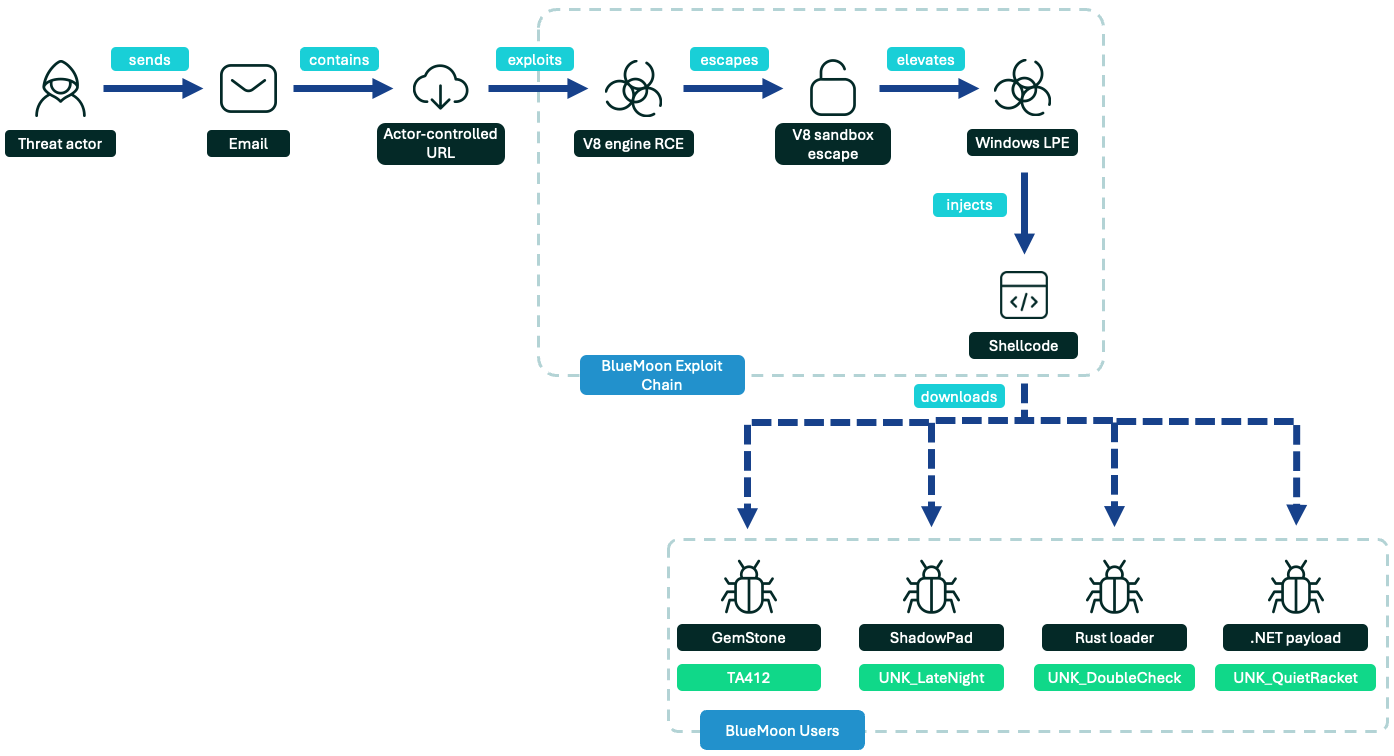
Four espionage groups used the BlueMoon Chrome+Windows exploit kit within 12 days. Researchers suspect AI development. Proofpoint published a detailed analysis of a Chrome-and-Windows exploit kit it tracks as BlueMoon that four nation-state actors adopted within roughly two weeks of the first observed use. Google’s Threat Intelligence Group, Microsoft’s MSTIC, and Volexity all contributed to […]
 Pierluigi Paganini
September 03, 2026
Serbian activists were targeted with zero-click Pegasus and NoviSpy spyware, exposing a major surveillance campaign ahead of elections. A member of Serbia’s student protest movement had their iPhone infected with NSO Group‘s Pegasus spyware without ever clicking a link or opening a file. The Citizen Lab confirmed the infection in collaboration with the SHARE Foundation, […]