 Pierluigi Paganini
 July 28, 2024
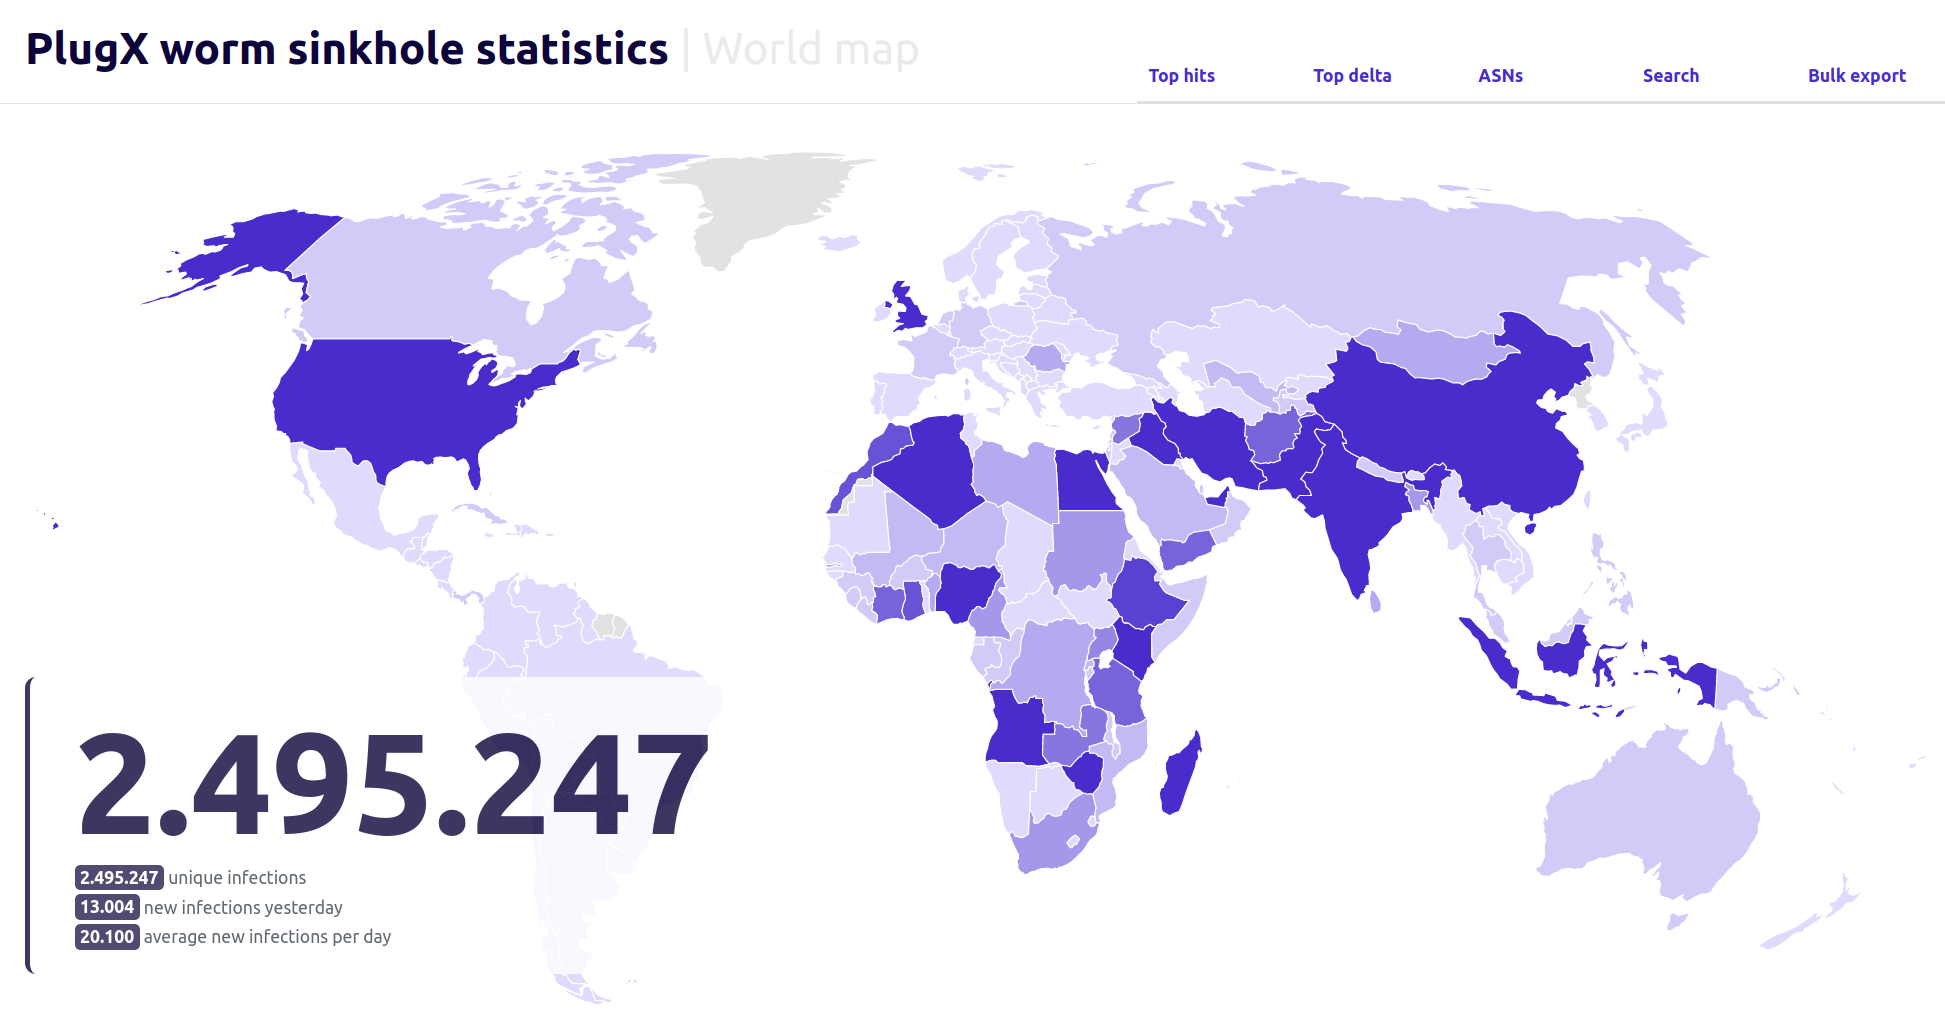
French authorities and Europol are conducting a “disinfection operation” targeting hosts compromised by the PlugX malware. The French authorities, with the help of Europol, have launched on July 18, 2024, a “disinfection operation” to clean hosts infected with the PlugX malware. Following a report by the cybersecurity firm Sekoia.io, the Paris Public Prosecutor’s Office launched […]
 Pierluigi Paganini
July 28, 2024
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape. Play Ransomware Group’s New Linux Variant Targets ESXi, Shows Ties With Prolific Puma Fake Browser Updates Lead to BOINC Volunteer Computing Software Impact of FrostyGoop ICS Malware on Connected OT Systems A Novel Static Analysis […]
 Pierluigi Paganini
July 28, 2024
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Ukraine’s cyber operation shut down the ATM services of major Russian banks A bug in Chrome Password Manager […]
 Pierluigi Paganini
July 27, 2024
Ukraine launched a massive cyber operation that shut down the ATM services of the biggest Russian banks on July 27, reported the Kyiv Post. Ukraine has launched a massive cyberattack against ATMs of Russian banks, the cyber operation began on July 23. “This is an opportune moment to fully implement the Kremlin’s long-desired ‘import substitution’ […]
 Pierluigi Paganini
July 26, 2024
Google addressed a Chrome’s Password Manager bug that caused user credentials to disappear temporarily for more than 18 hours. Google has addressed a bug in Chrome’s Password Manager that caused user credentials to disappear temporarily. An 18-hour outage impacted Google Chrome’s Password Manager on Wednesday, impacting users who rely on the tool to store and […]
 Pierluigi Paganini
July 26, 2024
The Internet Systems Consortium (ISC) released BIND security updates that fixed several remotely exploitable DoS bugs in the DNS software suite. The Internet Systems Consortium (ISC) released security updates for BIND that address DoS vulnerabilities that could be remotely exploited. An attacker can exploit these vulnerabilities to disrupt DNS services. ISC addressed four high-severity vulnerabilities […]
 Pierluigi Paganini
July 26, 2024
Terrorist groups are increasingly using cyberspace and digital communication channels to plan and execute attacks. Yesterday Federal Bureau of Investigation (FBI) Director Christopher Wray expressed growing concerns over the potential for a coordinated foreign terrorist attack in the United States. During his testimony to the House Oversight Committee, Mr. Wray cited the ISIS-K attack on […]
 Pierluigi Paganini
July 25, 2024
Progress Software addressed a critical remote code execution vulnerability, tracked as CVE-2024-6327, in the Telerik Report Server. Telerik Report Server is a web-based application designed for creating, managing, and delivering reports in various formats. It provides tools for report design, scheduling, and secure delivery, allowing organizations to centralize their reporting processes. Progress Software addressed a critical […]
 Pierluigi Paganini
July 25, 2024
A critical flaw in some versions of Docker Engine can be exploited to bypass authorization plugins (AuthZ) under specific circumstances. A vulnerability, tracked as CVE-2024-41110 (CVSS score of 10.0), in certain versions of Docker Engine can allow an attacker to bypass authorization plugins (AuthZ) under specific circumstances. “An attacker could exploit a bypass using an API request with […]
 Pierluigi Paganini
July 25, 2024
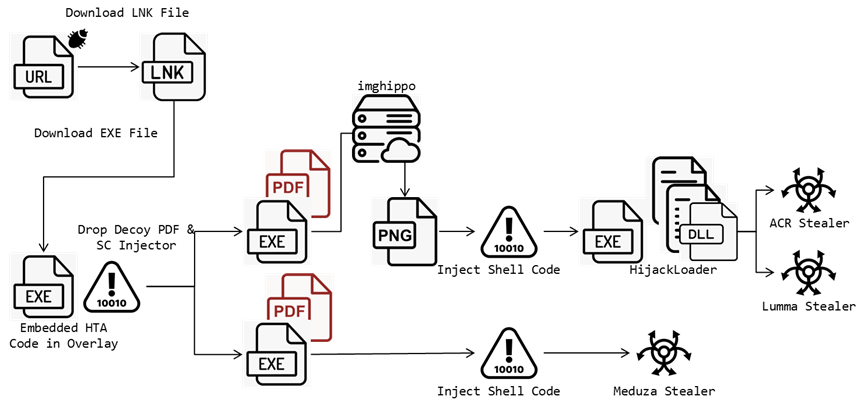
The CVE-2024-21412 flaw in the Microsoft Defender SmartScreen has been exploited to deliver information stealers such as ACR Stealer, Lumma, and Meduza. Fortinet FortiGuard Labs researchers observed a malware campaign exploiting the vulnerability CVE-2024-21412 (CVSS score: 8.1) to spread information stealer, such as ACR Stealer, Lumma, and Meduza. The CVE-2024-21412 is an Internet Shortcut Files Security Feature Bypass Vulnerability. The flaw […]
Malware / September 21, 2026