 Pierluigi Paganini
 August 02, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter TAG-195 Upgrades MaaS Ecosystem with Modular Tools Inside a DPRK BlueNoroff ClickFix Kit SourTrade: Browser-Assembled Malware Delivered Through Malvertising MedusaHVNC: A Hidden Desktop That Steals Live Windows Sessions Unpacking “Cruciferra”: An Analysis of a […]
 Pierluigi Paganini
August 02, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Russian Hackers Hijack Hotel Wi-Fi to Steal Microsoft 365 Tokens Adobe fixed a maximum-severity vulnerability flaw in […]
 Pierluigi Paganini
August 02, 2026
After attacks hit 30+ Minnesota water systems, CISA urged utilities to remove internet-exposed PLCs and strengthen OT security. Between Sunday and Monday, July 26 and 27, a coordinated cyberattack hit operational technology (OT) systems at more than 30 community water utilities across the state, according to Minnesota IT Services (MNIT). “A coordinated cyberattack targeted operational technology […]
 Pierluigi Paganini
August 01, 2026
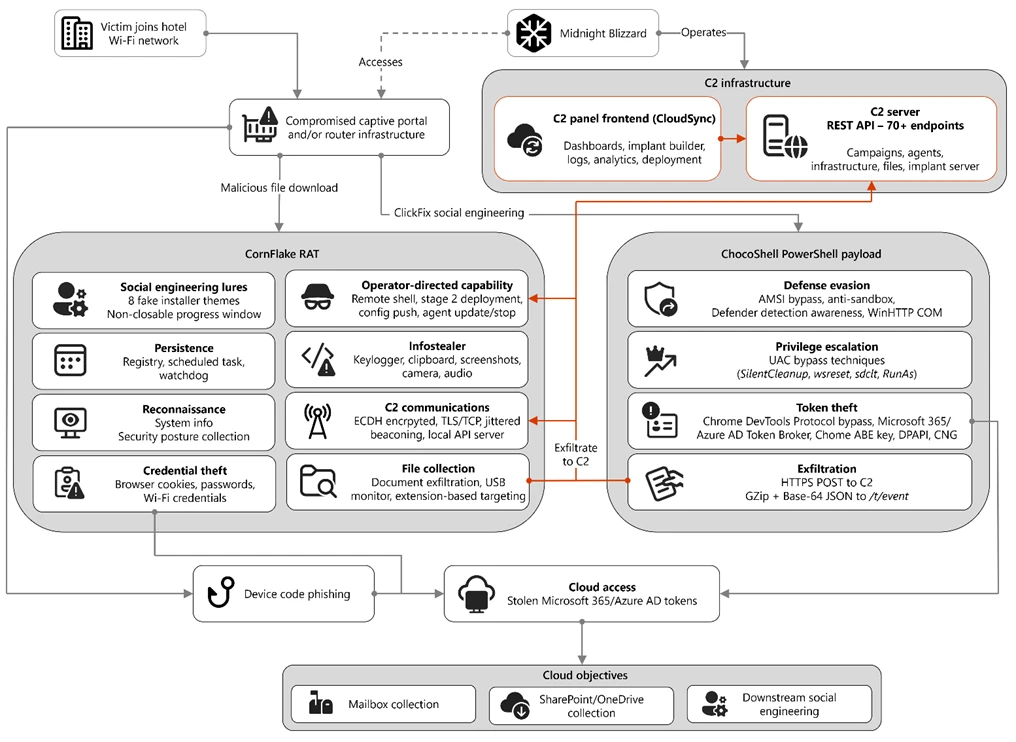
Microsoft says Russian hackers hijacked hotel Wi-Fi portals to spread malware and steal Microsoft 365 tokens from travelers. Microsoft Threat Intelligence disclosed CaptiveCrunch, a campaign it attributes to Storm-2945, an operational sub-cluster of Midnight Blizzard, the Russian SVR-linked group also known as APT29 and Cozy Bear. Since early May 2026, Storm-2945 has been manipulating DNS […]
 Pierluigi Paganini
August 01, 2026
Adobe fixed a maximum severity vulnerability in Campaign Classic that could let attackers run code remotely without user interaction. Adobe has addressed a critical vulnerability, tracked as CVE-2026-48449 (CVSS score of 10.0), in Adobe Campaign Classic, the company’s enterprise marketing automation platform. The flaw is caused by incorrect authorization and could allow attackers to execute […]
 Pierluigi Paganini
July 31, 2026
South Korea warned that nation-state actors are using phishing and compromised websites to silently infect citizens and businesses. South Korea agencies (The National Intelligence Service, the National Police Agency, the Korea Internet & Security Agency, and the Financial Security Institute) jointly published an advisory warning that a state-backed hacking group is actively targeting South Korean […]
 Pierluigi Paganini
July 31, 2026
Google says AI found and helped fix 1,072 Chrome security bugs in two releases, dramatically accelerating vulnerability detection and patching Google’s Chrome Security team published a detailed account of how AI models have transformed their vulnerability management pipeline, and the headline figure is difficult to dismiss: in the last two Chrome releases alone, the team […]
 Pierluigi Paganini
July 31, 2026
An AI-assisted audit found 29 flaws in GlobaLeaks, showing LLMs make large-scale code reviews faster, cheaper, and accessible. GlobaLeaks, a mature whistleblowing platform that had already undergone six independent professional audits over the past thirteen years, was subjected to an LLM-assisted security review that cost roughly USD 3,140 in API calls. The review identified 29 […]
 Pierluigi Paganini
July 31, 2026
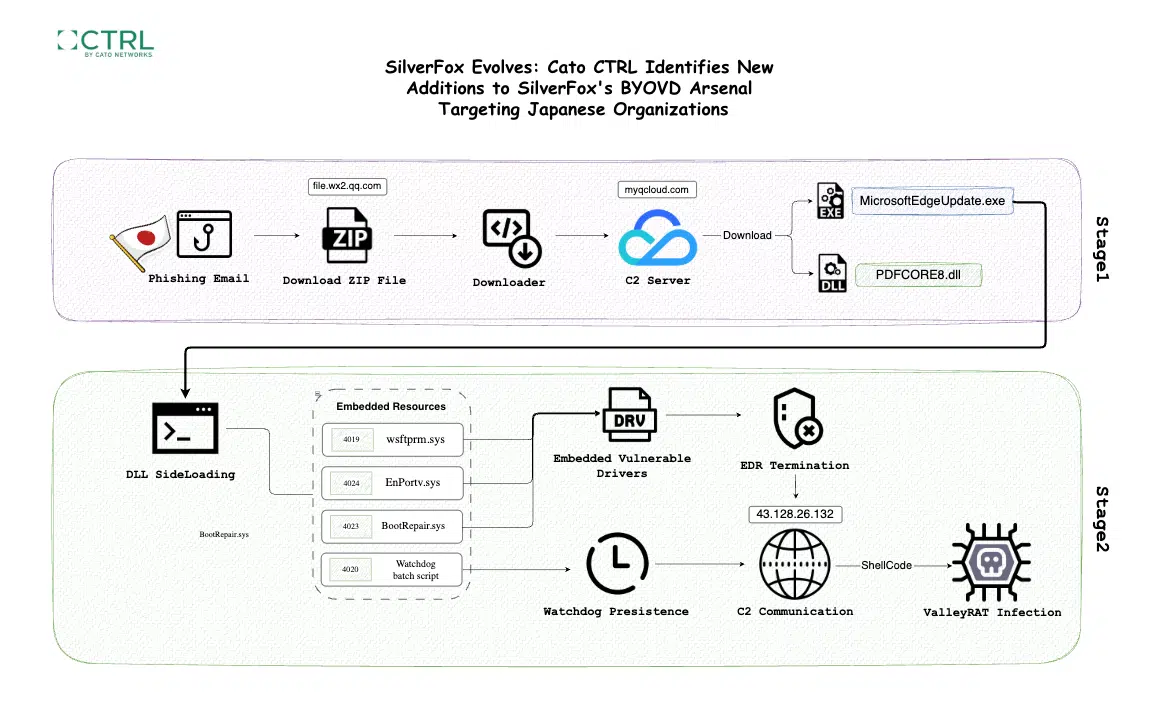
SilverFox targeted a Japanese manufacturer with new DLL sideloading techniques, kernel drivers, and resilient ValleyRAT persistence mechanisms. Cato CTRL documented a new SilverFox campaign targeting a Japanese industrial manufacturer. The attack chain adds two previously undocumented DLL-sideloading hosts, two kernel drivers not previously associated with SilverFox, and a dual-layer recovery architecture that keeps ValleyRAT running […]
 Pierluigi Paganini
July 30, 2026
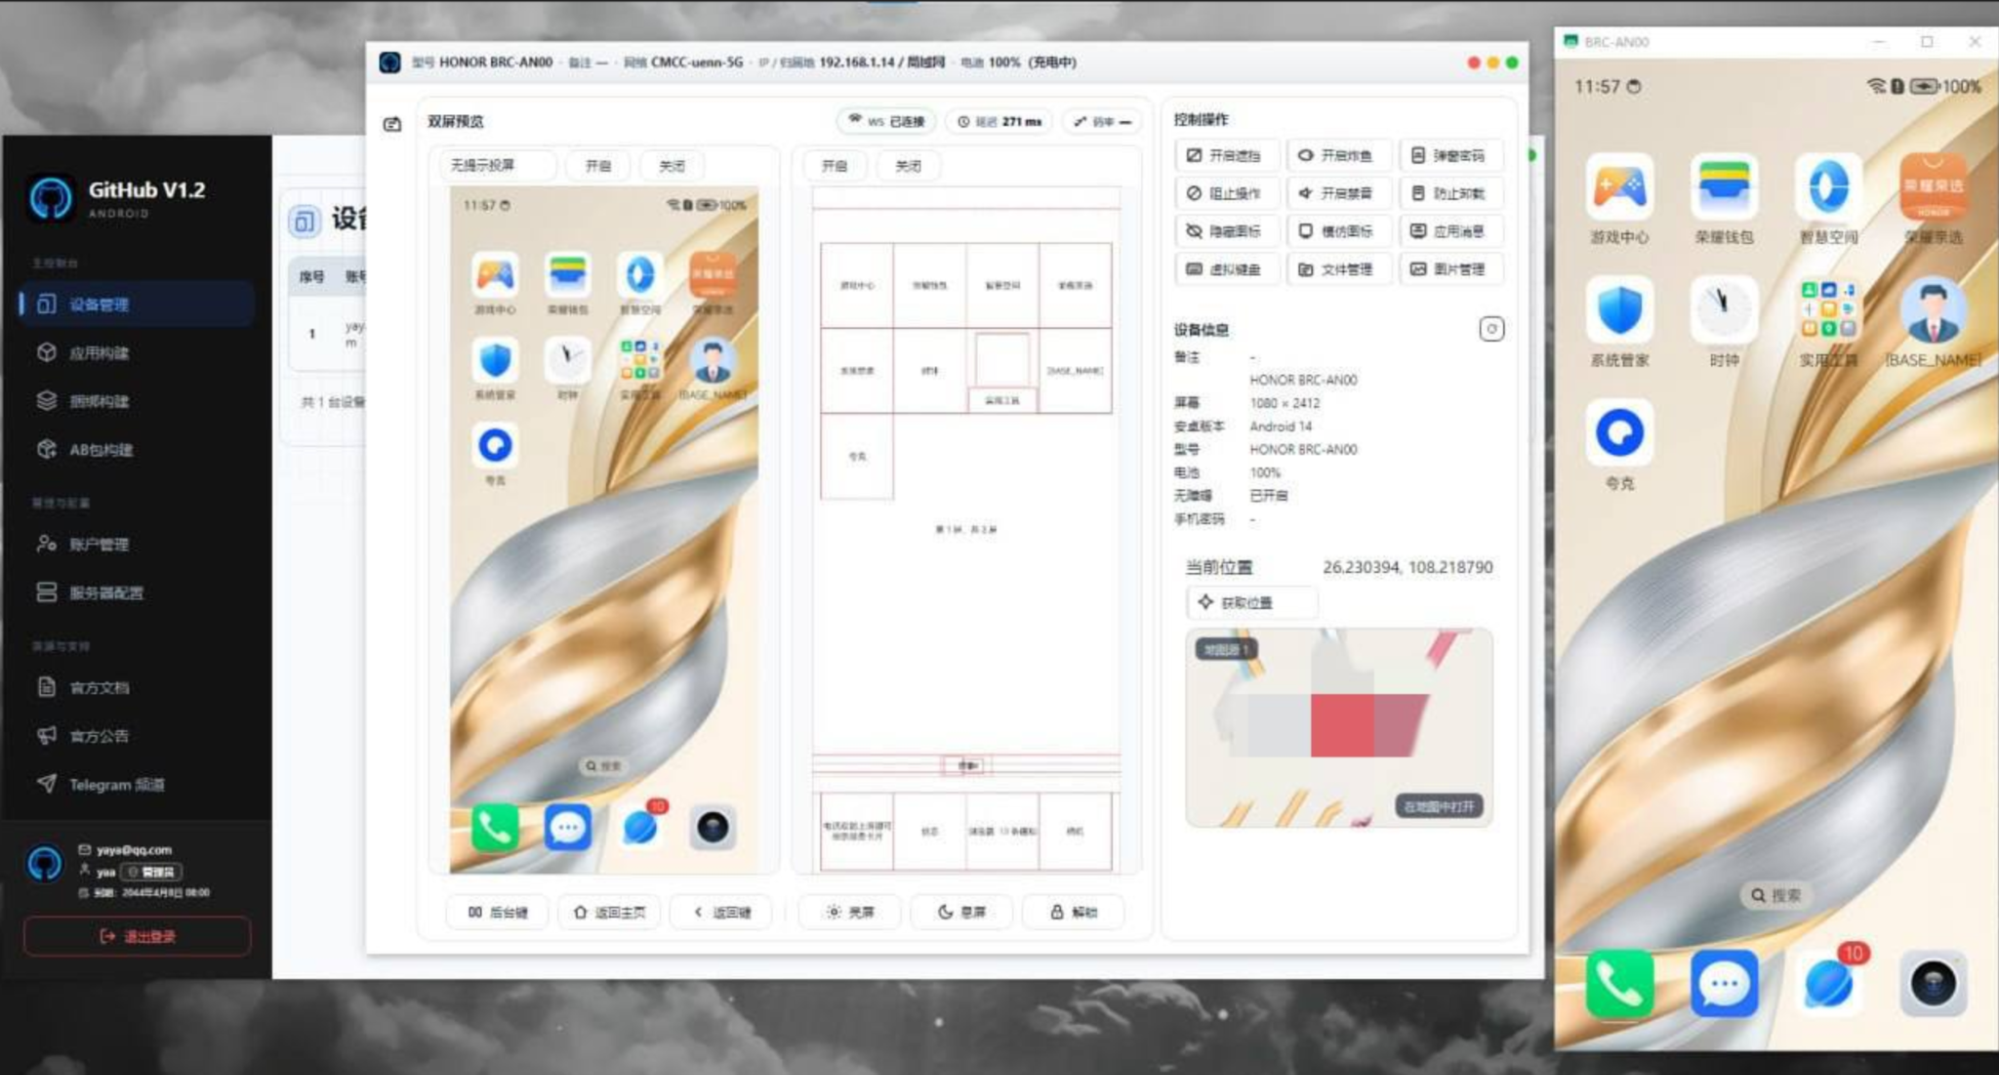
Researchers linked the Flying Eagle Android RAT to fake police apps, uncovering 170 servers in a growing cybercrime ecosystem. Hunt.io researchers and independent journalist NetAskari started with a fraudulent Android app impersonating a Chinese Provincial Public Security Bureau service and ended up mapping a sprawling criminal ecosystem built around a leaked Android RAT framework called […]
Security / November 12, 2026
Data Breach / November 11, 2026
Malware / November 11, 2026