Pierluigi Paganini
 October 24, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Collabora Online flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a Collabora Collabora Online – Built-in CODE Server flaw, tracked as CVE-2026-110447 (CVSS score of 9.2), to its Known Exploited Vulnerabilities (KEV) catalog. Collabora Online – Built-in CODE Server is […]
 Pierluigi Paganini
October 24, 2026
AI companies need usage data to align pricing with costs, improve products, identify churn risks, and grow revenue through informed decisions. The AI Paradox There is a paradox: AI companies exist to extract intelligence from data, yet many have almost no visibility into how their own software is being used. They design complex models, introduce […]
 Pierluigi Paganini
October 24, 2026
Capcom disclosed a data breach exposing 11.7 million email addresses and account details after hackers accessed its CAPCOM ID service. Japanese gaming company Capcom has disclosed a data breach discovered on October 19 involving its CAPCOM ID service, which provides access to online services and games. As of October 22, attackers stole 11,774,247 email addresses, […]
Pierluigi Paganini
October 24, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Arista VeloCloud Orchestrator flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a critical Arista VeloCloud Orchestrator flaw, tracked as CVE-2026-114625 (CVSS score of 9.4), to its Known Exploited Vulnerabilities (KEV) catalog. VeloCloud Orchestrator (VCO) is the central management system for […]
 Pierluigi Paganini
October 23, 2026
PHP warns of a new, unlikely code execution flaw, CVE-2026-115560, and advises disabling session upload progress until a fix is released. PHP has warned of a new code execution vulnerability, tracked as CVE-2026-115560, just two days after releasing emergency patches for the critical PHP2Shell flaws. The vulnerability affects only a specific PHP configuration that PHP […]
 Pierluigi Paganini
October 23, 2026
A New Mexico judge ordered Meta to pay $25 billion for misleading users about privacy, setting a record penalty. Meta plans to appeal. This week a New Mexico judge ordered Meta to pay the state $25 billion. The order follows a jury finding that the company deceived Facebook users about their privacy, and it’s the […]
 Pierluigi Paganini
October 23, 2026
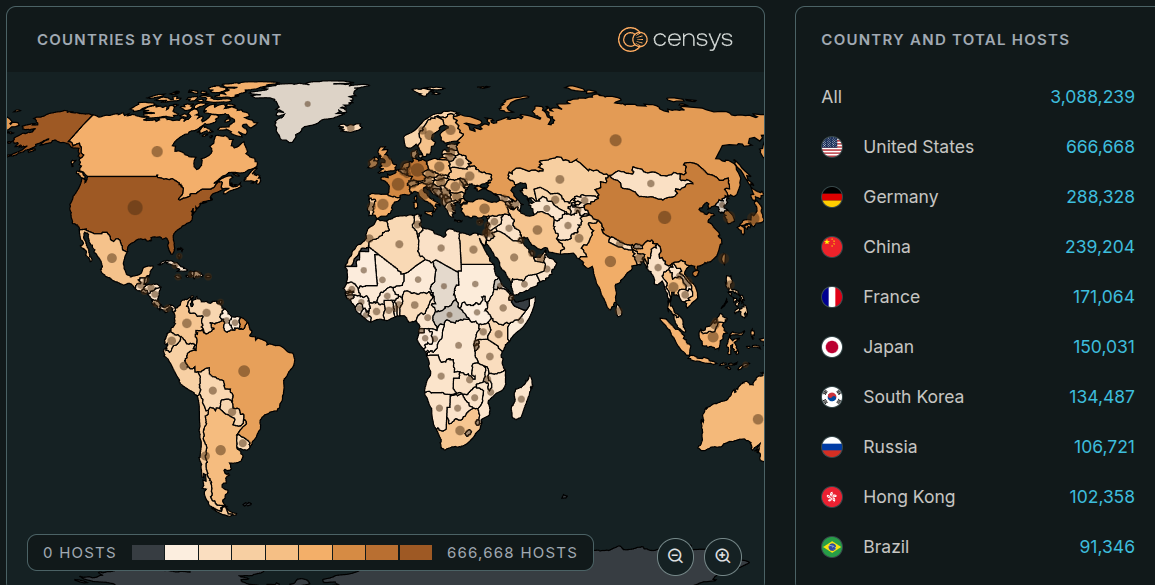
PHP2Shell attacks have surged into the millions, but no successful exploitation is confirmed. Patch it immediately. On October 21, PHP released emergency patches for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2), affecting every PHP version that handles web requests. The bug code dates back to PHP 5.4 from 2012, lives […]
 Pierluigi Paganini
October 23, 2026
INTERPOL’s Operation Serengeti III led to 1,462 arrests, disrupted 10,909 malicious networks and recovered $105 million across 21 countries. INTERPOL announced the results of Operation Serengeti III, a multinational cybercrime crackdown that led to 1,462 arrests, disrupted 10,909 malicious networks and recovered more than $105 million in illicit funds. The operation brought together law enforcement […]
 Pierluigi Paganini
October 22, 2026
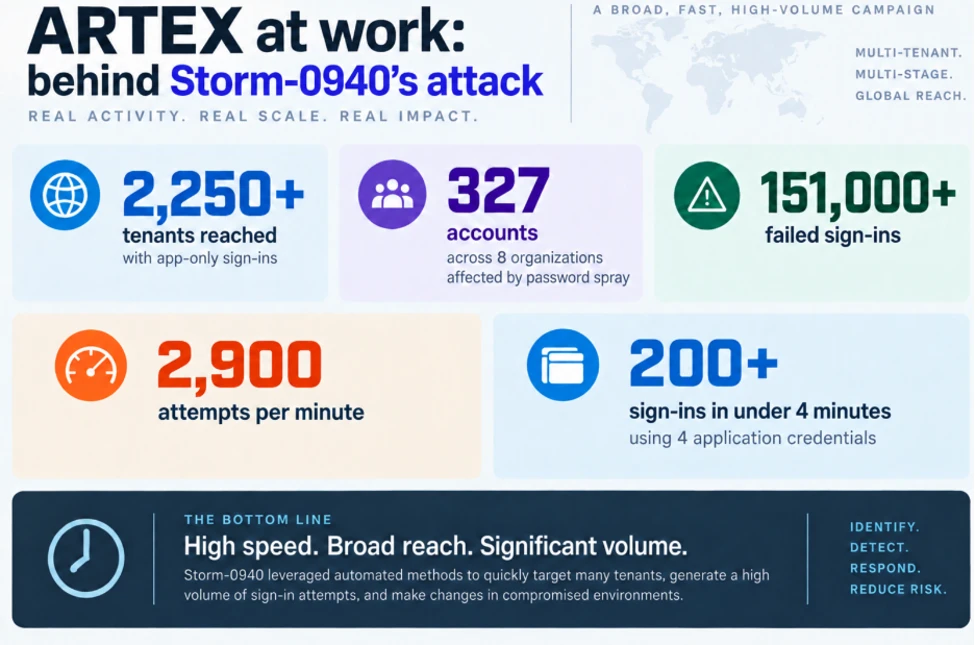
China-linked Storm-0940 used AI tool ARTEX to target 2,250 Microsoft 365 tenants, exploiting stolen ConnectWise credentials at machine speed. Microsoft published a detailed technical report naming Storm-0940, a China state-aligned group, as the actor behind the ConnectWise Cloud Backup supply chain compromise. The group used ARTEX, an open-source AI-driven penetration testing framework, to run attacks […]
 Pierluigi Paganini
October 22, 2026
A critical Signal flaw could keep calls active after hang-up, exposing microphone or camera. Update to a fixed version immediately. A critical vulnerability, tracked as CVE-2026-113380 (CVSS score 9.3 of 10), in Signal ’s calling library could allow a malicious caller to interfere with call termination, potentially leaving the victim’s microphone and camera active after […]
Malware / November 11, 2026