 Pierluigi Paganini
 July 12, 2024
A critical vulnerability in Exim mail server allows attackers to deliver malicious executable attachments to mailboxes. Attackers can exploit a critical security flaw, tracked as CVE-2024-39929 (CVSS score of 9.1), in the Exim mail transfer agent to deliver malicious attachments to target users’ inboxes. Exim is a widely used Mail Transfer Agent (MTA) designed to […]
 Pierluigi Paganini
July 12, 2024
Resecurity has identified a new campaign by the Smishing Triad that is targeting India to steal personal and payment data at scale Resecurity (USA) identified a new campaign targeting India Post (Department of Posts, India) by the Smishing Triad, which reportedly started amplifying around July 8, 2024, based on multiple victim reports and the detection […]
 Pierluigi Paganini
July 11, 2024
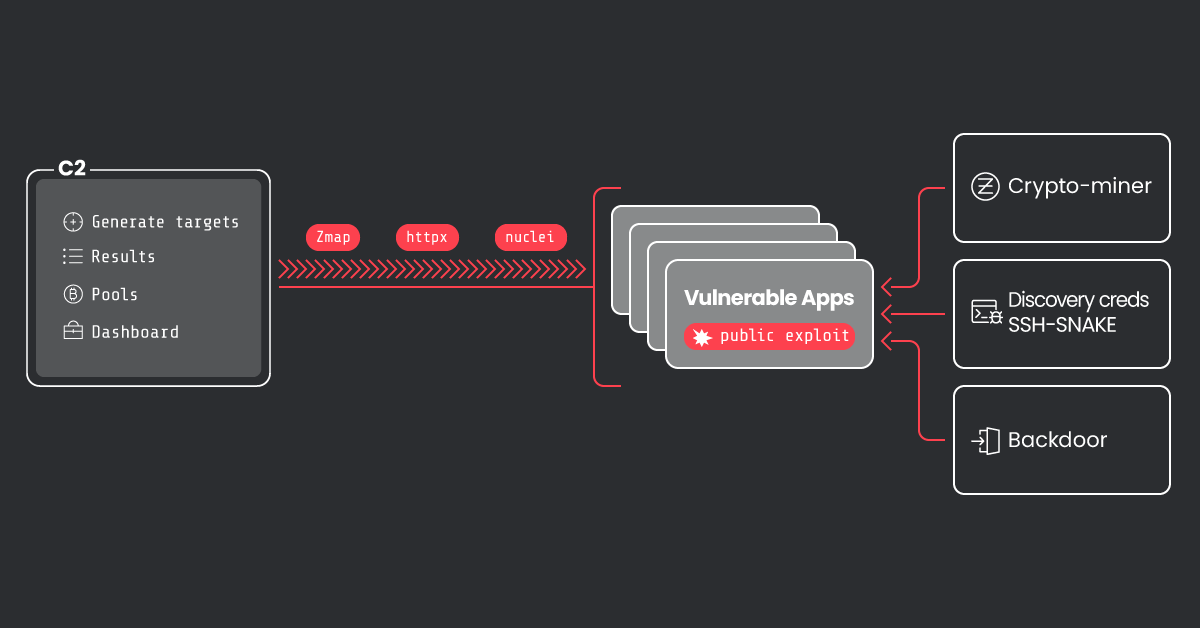
A threat actor known as CrystalRay targeted 1,500 victims since February using tools like SSH-Snake and various open-source utilities. The Sysdig Threat Research Team (TRT) first spotted the threat actor CrystalRay on February 2024 and observed it using the SSH-Snake open-source software penetration testing tool. The experts collected new evidence that revealed that the threat actor expanded its operations. […]
 Pierluigi Paganini
July 11, 2024
Multiple threat actors exploit a recently disclosed security PHP flaw CVE-2024-4577 to deliver multiple malware families. The Akamai Security Intelligence Response Team (SIRT) warns that multiple threat actors are exploiting the PHP vulnerability CVE-2024-4577 to deliver multiple malware families, including Gh0st RAT, RedTail cryptominers, and XMRig. “Threat actors continued the speedy-time-from-disclosure-to-exploitation trend and were quick […]
 Pierluigi Paganini
July 11, 2024
The US and its allies disrupted an AI-powered Russia-linked bot farm on the social media platform X relying on the Meliorator AI software. The U.S. FBI and Cyber National Mission Force, along with Dutch and Canadian intelligence and security agencies, warned social media companies about Russian state-sponsored actors using covert AI software, Meliorator, in disinformation […]
 Pierluigi Paganini
July 10, 2024
A vulnerability affects some versions of the OpenSSH secure networking suite, it can potentially lead to remote code execution. The vulnerability CVE-2024-6409 (CVSS score: 7.0) impacts select versions of the OpenSSH secure networking suite, it can be exploited to achieve remote code execution (RCE). The issue is a possible race condition in cleanup_exit() in openssh’s […]
 Pierluigi Paganini
July 10, 2024
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft Windows and Rejetto HTTP File Server bugs to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Below are the descriptions of the flaws added to the KEV catalog: CVE-2024-23692 (CVSS score […]
 Pierluigi Paganini
July 08, 2024
Threat actors leaked the largest password compilation ever, known as RockYou2024, on a popular hacking forum. The Cybernews researchers reported that threat actors leaked the largest password compilation ever, known as RockYou2024, on a popular hacking forum. The compilation (“rockyou2024.txt”) contains 9,948,575,739 unique plaintext passwords was posted on July 4th by a user with the […]
 Pierluigi Paganini
July 08, 2024
Threat actors are exploiting Ghostscript vulnerability CVE-2024-29510 to bypass the sandbox and achieve remote code execution. Threat actors are actively exploiting a Ghostscript vulnerability, tracked as CVE-2024-29510, that can allow them to escape the –dSAFER sandbox and achieve remote code execution. Ghostscript is an interpreter for the PostScript language and for PDF files. It is […]
 Pierluigi Paganini
July 08, 2024
Apple removed several virtual private network (VPN) apps from its App Store in Russia following a request from the Russian Government. Russia is tightening its citizens’ control over Internet access and forced Apple to remove several virtual private network (VPN) apps from its App Store in Russia following a request from Russia’s state communications watchdog […]
Malware / September 25, 2026
Malware / September 25, 2026