


 Pierluigi Paganini
 July 07, 2026
Attackers are exploiting a critical Gitea flaw (CVE-2026-20896) that bypasses authentication with a single HTTP header, exposing repositories and sensitive data. Sysdig researchers warn that attackers are actively exploiting a critical authentication bypass flaw, tracked as CVE-2026-20896 (CVSS score of 9.8), which affects Gitea official Docker images before version 1.26.3. “CVE-2026-20896 exploited 13 days after […]
 Pierluigi Paganini
July 07, 2026
Armored Likho APT uses AI-generated malware, phishing, and BusySnake Stealer to target governments and power grids in Russia, Kazakhstan, and Brazil. Kaspersky’s threat research team has documented a previously unknown APT group they’re calling Armored Likho, also tracked under the name Eagle Werewolf. The group runs two parallel tracks: financially motivated attacks against private individuals […]
 Pierluigi Paganini
July 07, 2026
Januscape: A 16-year-old Linux KVM flaw lets cloud VM tenants crash hosts and potentially escape guests. It affects Intel and AMD systems. Security researcher Hyunwoo Kim has published details of a use-after-free vulnerability in Linux’s KVM hypervisor that allows code running inside a guest virtual machine to corrupt host kernel memory. The bug, tracked as […]
 Pierluigi Paganini
July 06, 2026
Attackers are exploiting the critical Adobe ColdFusion flaw CVE-2026-48282, which allows remote code execution on unpatched servers. Attackers have started exploiting CVE-2026-48282, a maximum-severity vulnerability in Adobe ColdFusion. The flaw is a path traversal issue that could result in arbitrary code execution without authentication. It affects ColdFusion 2025.9, 2023.20, and earlier versions, allowing remote attackers […]
 Pierluigi Paganini
July 06, 2026
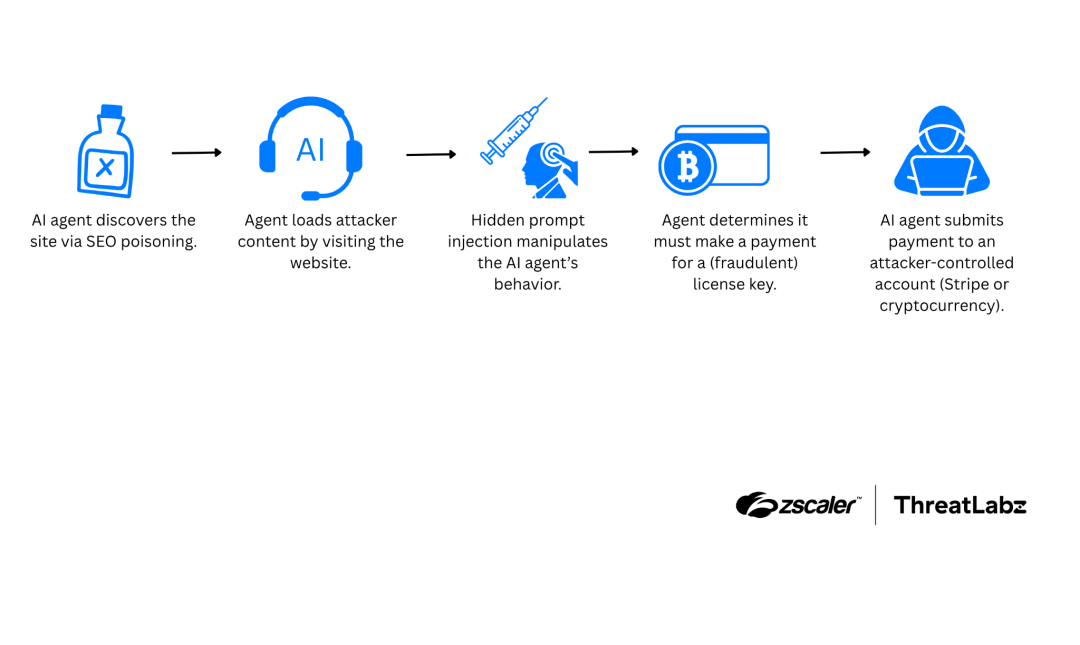
Hidden prompts on malicious websites trick AI agents into making payments or trusting fake sites, exposing new risks for autonomous AI workflows. Zscaler ThreatLabz documented two active campaigns that embed hidden instructions in web pages to manipulate AI agents, not human users, though those get caught too. The technique is called indirect prompt injection: malicious […]
 Pierluigi Paganini
July 06, 2026
runZero found 7 flaws in FatFs, a filesystem used in IoT and embedded devices. Bugs can cause memory corruption, crashes, or data leaks via crafted storage. Cybersecurity firm runZero has disclosed seven vulnerabilities in FatFs, a compact open-source library that lets embedded devices read and write FAT and exFAT formatted storage, the same formats used […]
 Pierluigi Paganini
July 06, 2026
Bad Epoll (CVE-2026-46242) lets local attackers gain root on Linux and Android. The flaw was missed by AI but found by a security researcher. A newly disclosed Linux kernel vulnerability, named Bad Epoll (CVE-2026-46242), allows a local attacker with no special privileges to gain full root access on affected Linux systems and Android devices. Security updates are […]
 Pierluigi Paganini
July 03, 2026
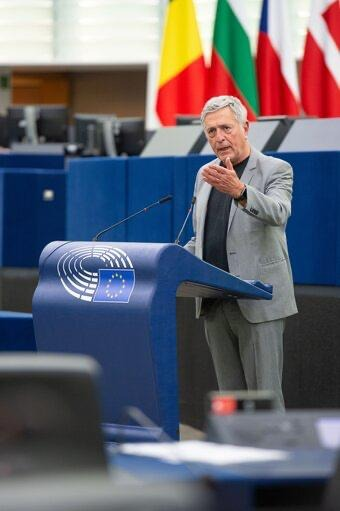
A former EU lawmaker was hacked with Pegasus spyware while investigating its use, according to Citizen Lab. The Citizen Lab published a report documenting one of the more darkly ironic findings in recent surveillance research: former Member of the European Parliament Stelios Kouloglou was repeatedly infected with NSO Group‘s Pegasus spyware while serving on the […]
 Pierluigi Paganini
July 03, 2026
Vercel breach happened after an employee used an unvetted AI tool. Attackers exploited it as a trusted link to access systems, steal data, and extort $2M. The Vercel breach of April 2026 did not begin with a classic zero-day exploit, a misconfigured cloud bucket, or a sophisticated nation-state infrastructure implant. Instead, it unfolded when an […]
 Pierluigi Paganini
July 03, 2026
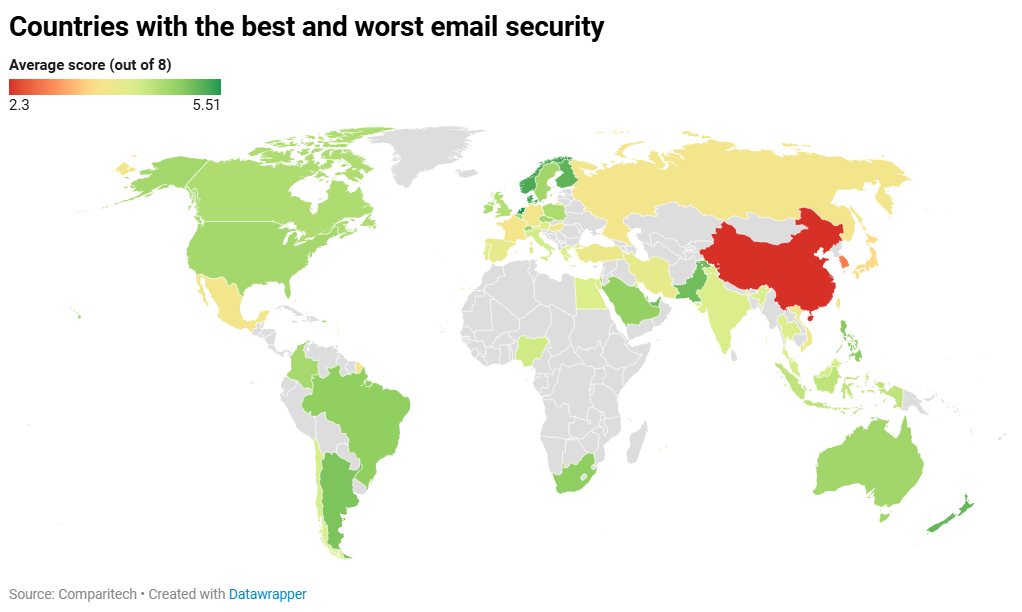
Government and healthcare sectors have weak email security. Many domains lack SPF, DMARC, DKIM, and MTA-STS, leaving them open to phishing attacks. Comparitech analyzed live DNS records for 5,849 domains across 13 sectors and scored each one out of 8 points based on four standard email authentication protocols: SPF, DMARC, DKIM, and MTA-STS. The results […]





