


 Pierluigi Paganini
 January 19, 2023
Popular email marketing and newsletter platform Mailchimp was hacked and the data of dozens of customers were exposed. The popular email marketing and newsletter platform Mailchimp was hacked twice in the past six months. The news of a new security breach was confirmed by the company, the incident exposed the data of 133 customers. Threat […]
 Pierluigi Paganini
January 18, 2023
SSRF vulnerabilities in four Microsoft Azure services could be exploited to gain unauthorized access to cloud resources. Researchers at the security firm Orca discovered that four different Microsoft Azure services were vulnerable to server-side request forgery (SSRF) attacks. Threat actors could have exploited the flaws to gain unauthorized access to cloud resources. Vulnerable services included […]
 Pierluigi Paganini
January 17, 2023
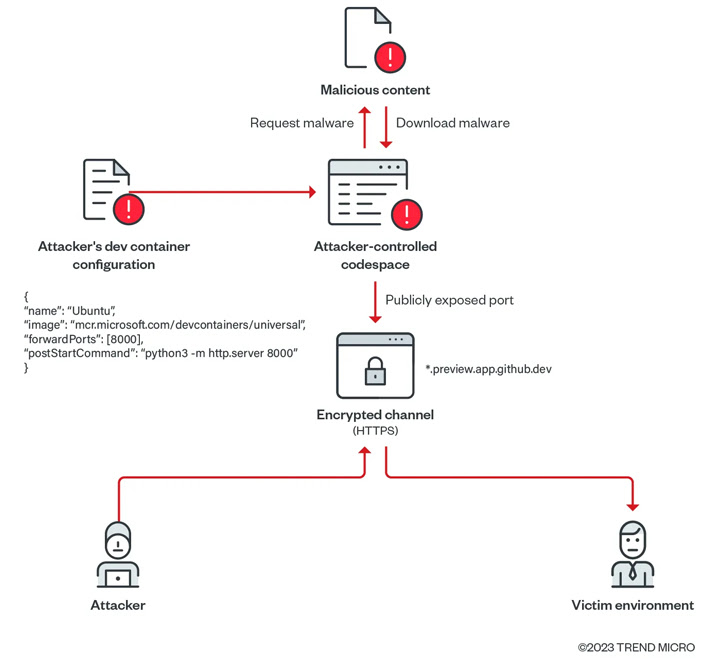
Researchers demonstrated how to abuse a feature in GitHub Codespaces to deliver malware to victim systems. Trend Micro researchers reported that it is possible to abuse a legitimate feature in the development environment GitHub Codespaces to deliver malware to victim systems. Users can customize their project for GitHub Codespaces by committing configuration files to their repository, which […]
 Pierluigi Paganini
January 17, 2023
A PoC exploit code for the unauthenticated remote code execution vulnerability CVE-2022-47966 in Zoho ManageEngine will be released soon. The CVE-2022-47966 flaw is an unauthenticated remote code execution vulnerability that impacts multiple Zoho products with SAML SSO enabled in the ManageEngine setup. The issue also impacts products that had the feature enabled in the past. The […]
 Pierluigi Paganini
January 16, 2023
Antivirus firm Avast released a free decryptor for the BianLian ransomware family that allows victims to recover locked files. Security firm Avast has released a free decryptor for the BianLian ransomware to allow victims of the malware to recover locked files. The BianLian ransomware emerged in August 2022, the malware was employed in attacks against organizations in […]
 Pierluigi Paganini
January 16, 2023
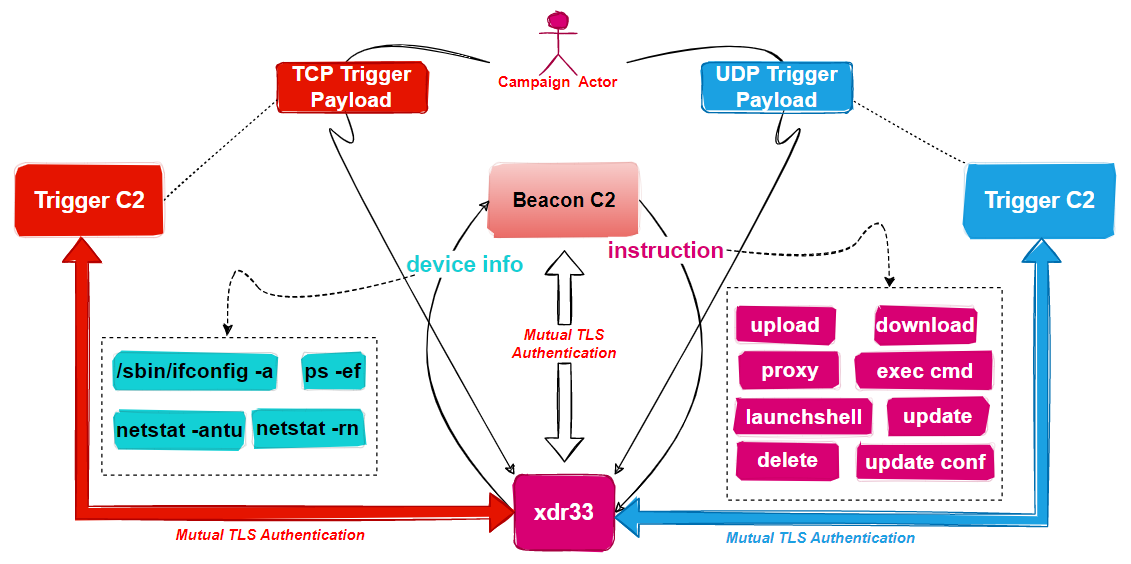
Netlab 360 observed unidentified threat actors using a new backdoor based on the US CIA’s Project Hive malware suite. Researchers from Qihoo Netlab 360 reported that unidentified threat actors using a new backdoor based on the US CIA’s Project Hive malware suite. “Hive provides a covert communications platform for a whole range of CIA malware to send exfiltrated […]
 Pierluigi Paganini
January 16, 2023
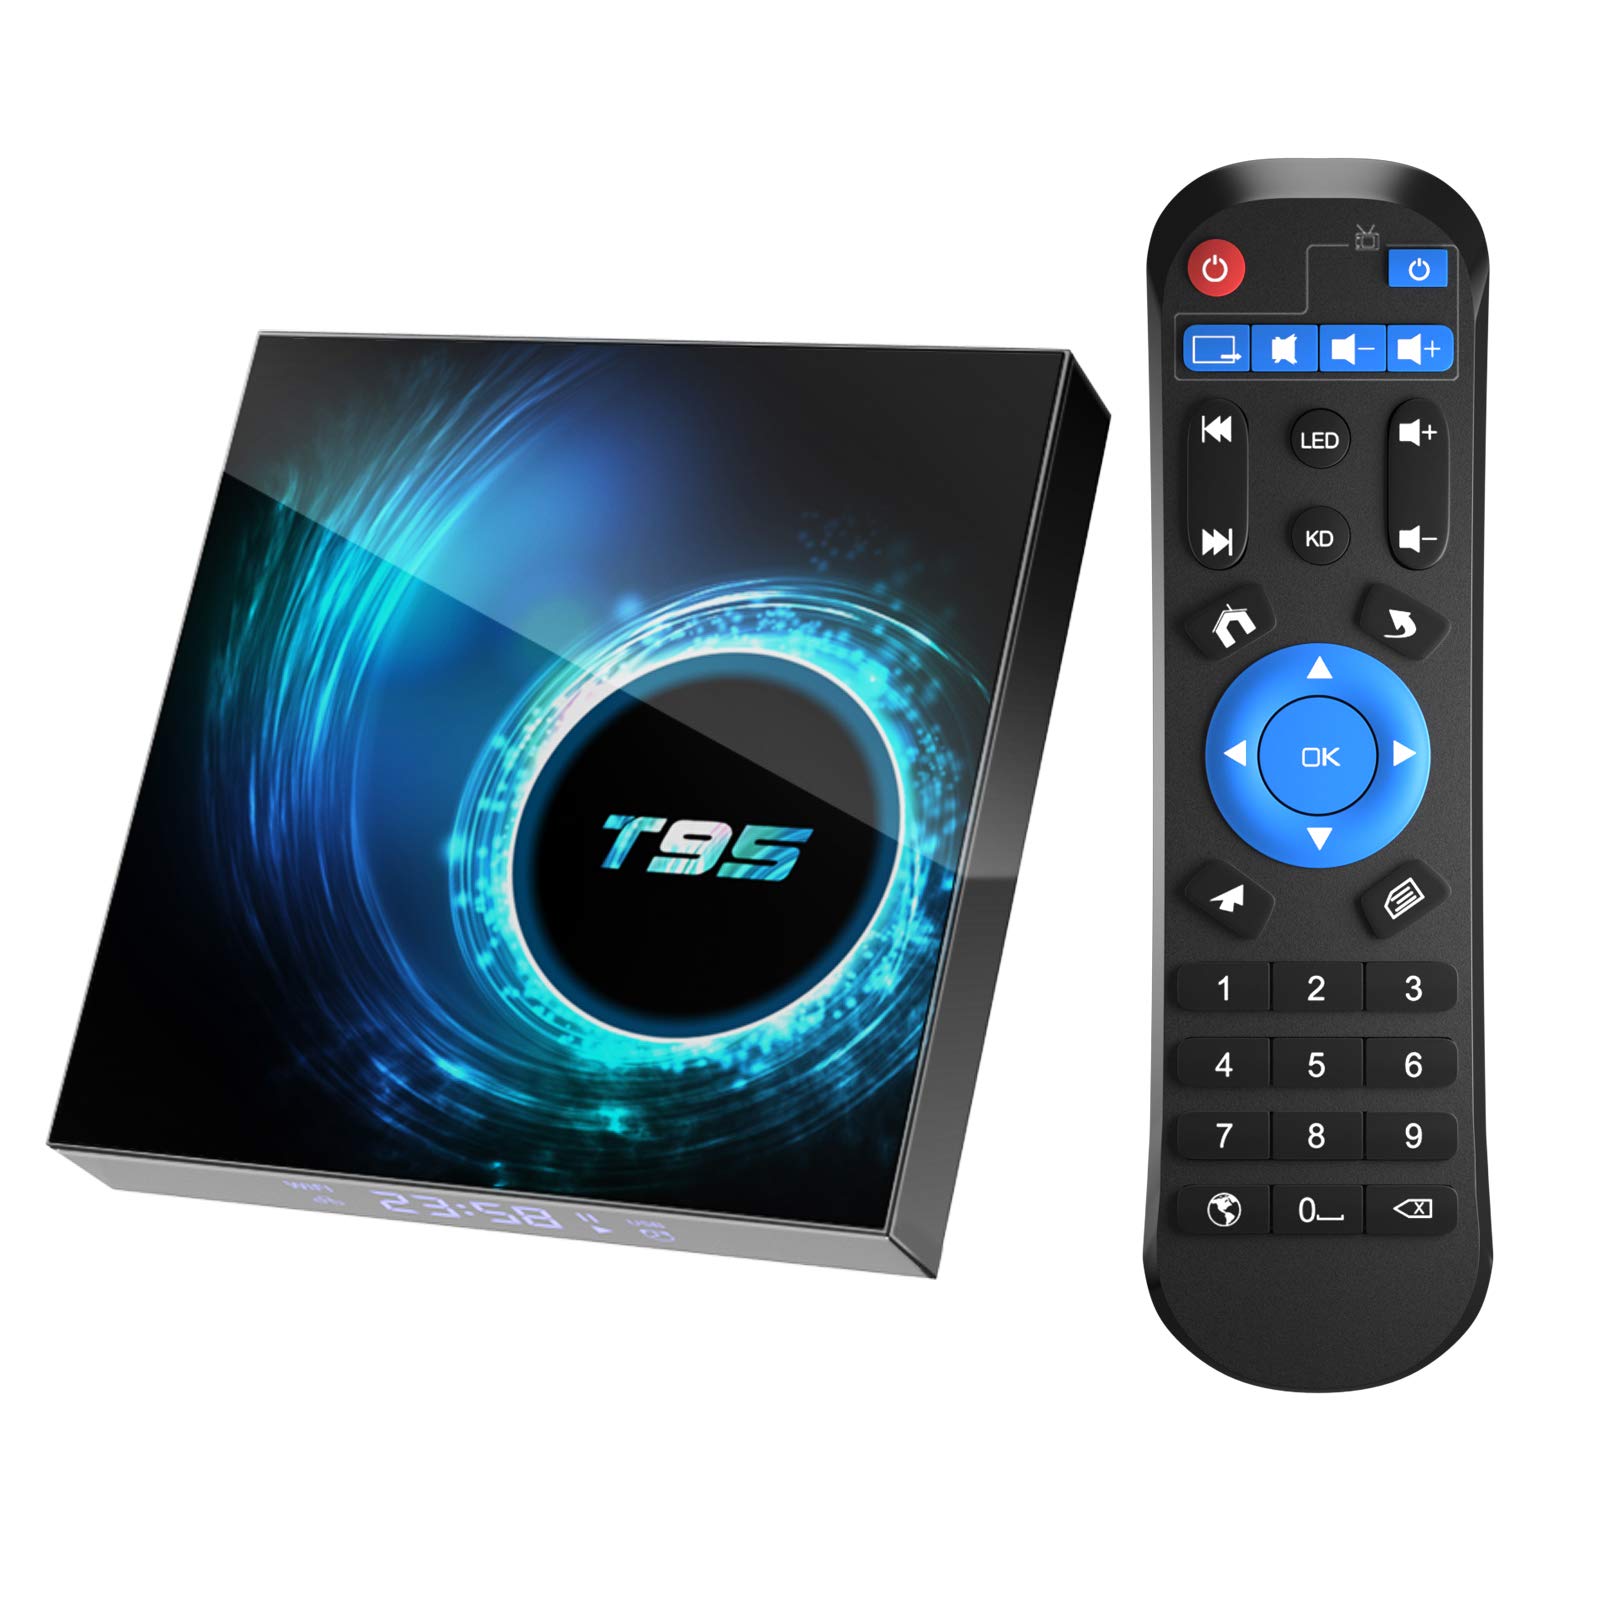
Expert discovered that the T95 Android TV box, available for sale on Amazon and AliExpress, came with sophisticated pre-installed malware. Security researcher, Daniel Milisic, discovered that the T95 Android TV box he purchased on Amazon was infected with sophisticated pre-installed malware. This Android TV box model is available on Amazon and AliExpress for as low […]
 Pierluigi Paganini
January 15, 2023
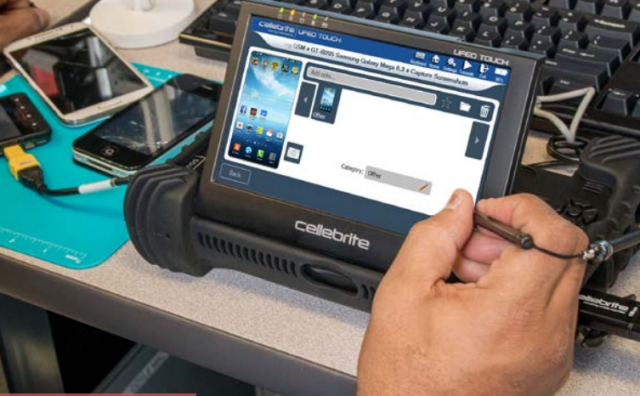
1.7 TB of data stolen from Cellebrite, a digital intelligence company that provides tools for law enforcement, were leaked online. The Israeli mobile forensics firm Cellebrite is one of the leading companies in the world in the field of digital forensics, it works with law enforcement and intelligence agencies worldwide. One of the most popular services provided […]
 Pierluigi Paganini
January 15, 2023
The Canadian Liquor Control Board of Ontario (LCBO), the largest beverage alcohol retailer in the country, disclosed Magecart attack. Canadian Liquor Control Board of Ontario (LCBO), the largest beverage alcohol retailer in the country, disclosed a Magecart attack on January 10, 2023. Threat actors compromised the Canadian Liquor Control Board of Ontario’s website and injected […]
 Pierluigi Paganini
January 14, 2023
Most internet-exposed Cacti servers are vulnerable to the critical vulnerability CVE-2022-46169 which is actively exploited in the wild. Cacti is an open-source platform that provides a robust and extensible operational monitoring and fault management framework for users. Researchers from Censys discovered that the majority of internet-exposed Cacti servers are vulnerable to the critical flaw CVE-2022-46169 […]
Security / September 28, 2026





