


 Pierluigi Paganini
 December 11, 2021
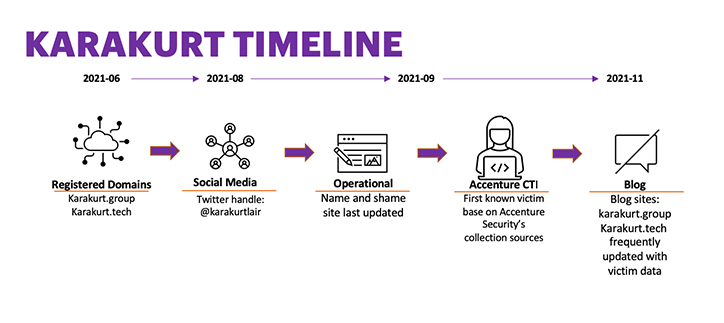
Accenture researchers detailed the activity of a new sophisticated cybercrime group, called Karakurt, behind recent cyberattacks. Accenture researchers detailed the activity of a sophisticated financially motivated threat actor called Karakurt. The activity of the group was first spotted in June 2021, but the group has been more active in Q3 2021. In June 2021 the […]
 Pierluigi Paganini
December 11, 2021
Cybereason researchers released a “vaccine” that mitigates the critical ‘Log4Shell’ Apache Log4j code execution vulnerability. Chinese security researcher p0rz9 publicly disclosed a Proof-of-concept exploit for a critical remote code execution zero-day vulnerability, tracked a CVE-2021-44228 (aka Log4Shell), in the Apache Log4j Java-based logging library. p0rz9 revealed that the CVE-2021-44228 can only be exploited if the log4j2.formatMsgNoLookups option is set to false. The Log4j is widely […]
 Pierluigi Paganini
December 10, 2021
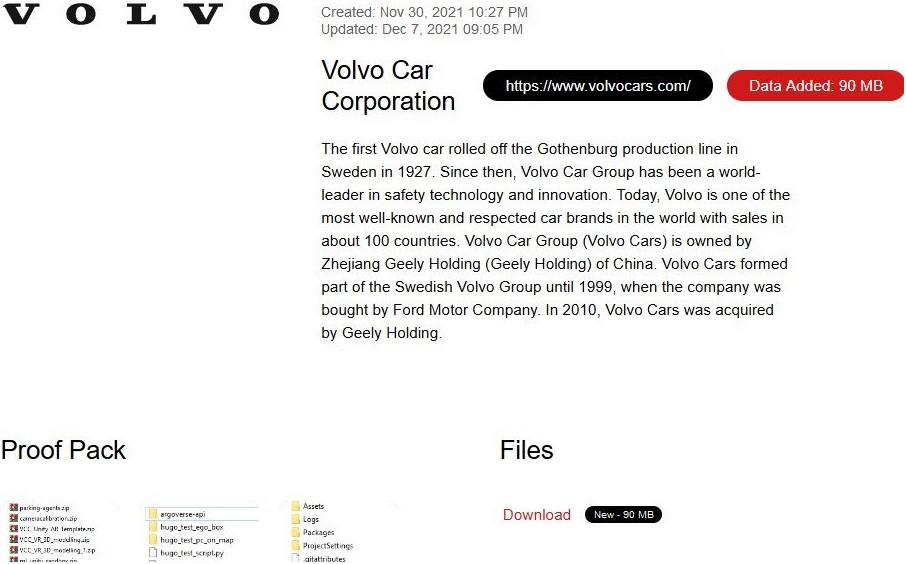
Swedish automotive manufacturer Volvo Cars revealed that has suffered a cyberattack that resulted in the theft of R&D data. Swedish automotive manufacturer Volvo Cars revealed that threat actors have stolen R&D data from its systems. In 2010, Volvo Cars became a subsidiary of the Chinese manufacturer Geely Holding Group, which confirmed that it “has become […]
 Pierluigi Paganini
December 10, 2021
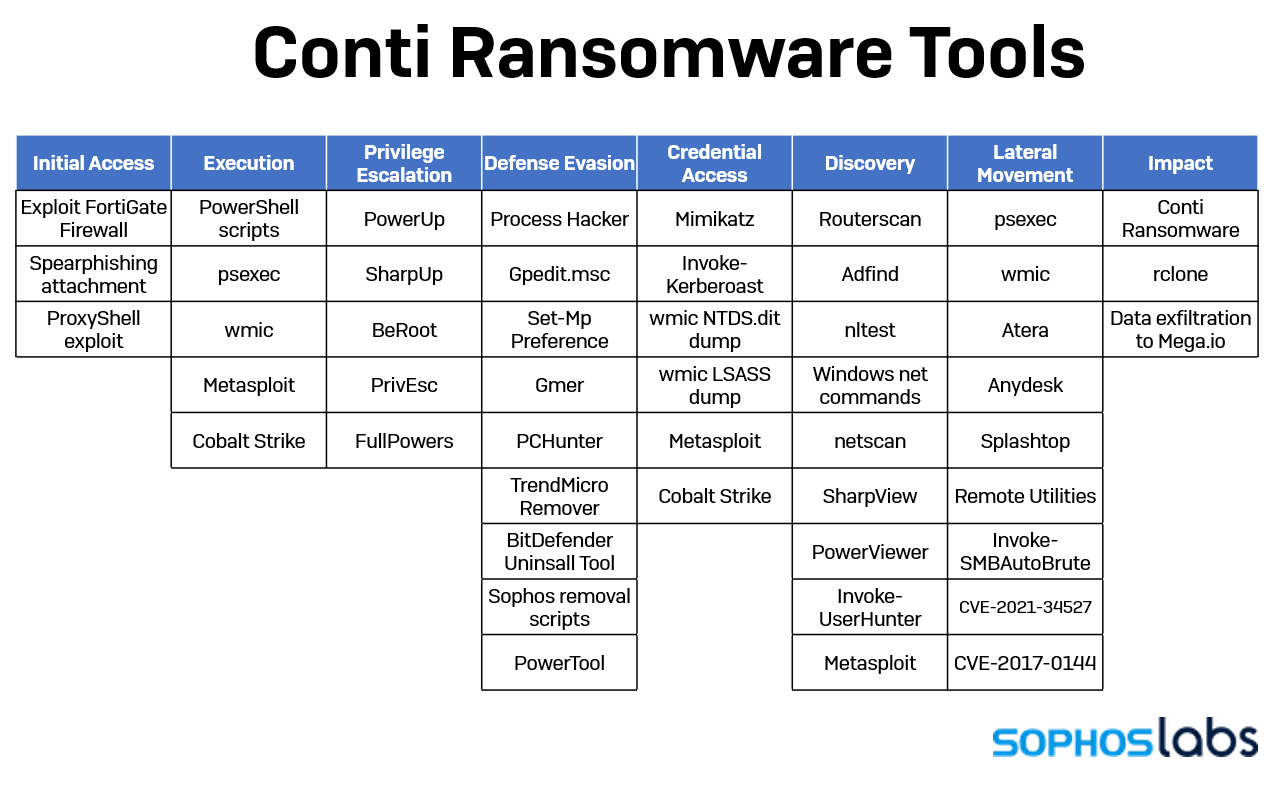
The Australian Cyber Security Centre (ACSC) warns of Conti ransomware attacks again multiple Australian organizations. The Australian Cyber Security Centre (ACSC) warns of Conti ransomware attacks against multiple Australian organizations from various sectors since November. “The ACSC is aware of multiple instances of Australian organisations that have been impacted by Conti ransomware in November and […]
Pierluigi Paganini
December 10, 2021
Experts publicly disclose Proof-of-concept exploits for a critical zero-day vulnerability in the Apache Log4j Java-based logging library. Experts publicly disclose Proof-of-concept exploits for a critical remote code execution zero-day vulnerability, tracked a CVE-2021-44228 (aka Log4Shell), in the Apache Log4j Java-based logging library. The Chinese security researcher p0rz9 who publicly disclosed the PoC exploit code revealed […]
 Pierluigi Paganini
December 10, 2021
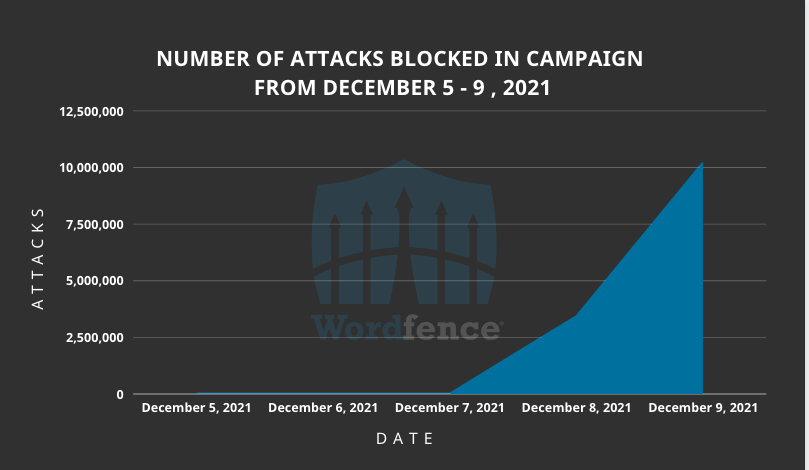
Wordfence experts detected a massive wave of attacks in the last couple of days that targeted over 1.6 million WordPress sites. Wordfence researchers spotted a massive wave of attacks in the days that are targeting over 1.6 million WordPress sites from 16,000 IPs. “Today, on December 9, 2021, our Threat Intelligence team noticed a drastic uptick in attacks […]
 Pierluigi Paganini
December 09, 2021
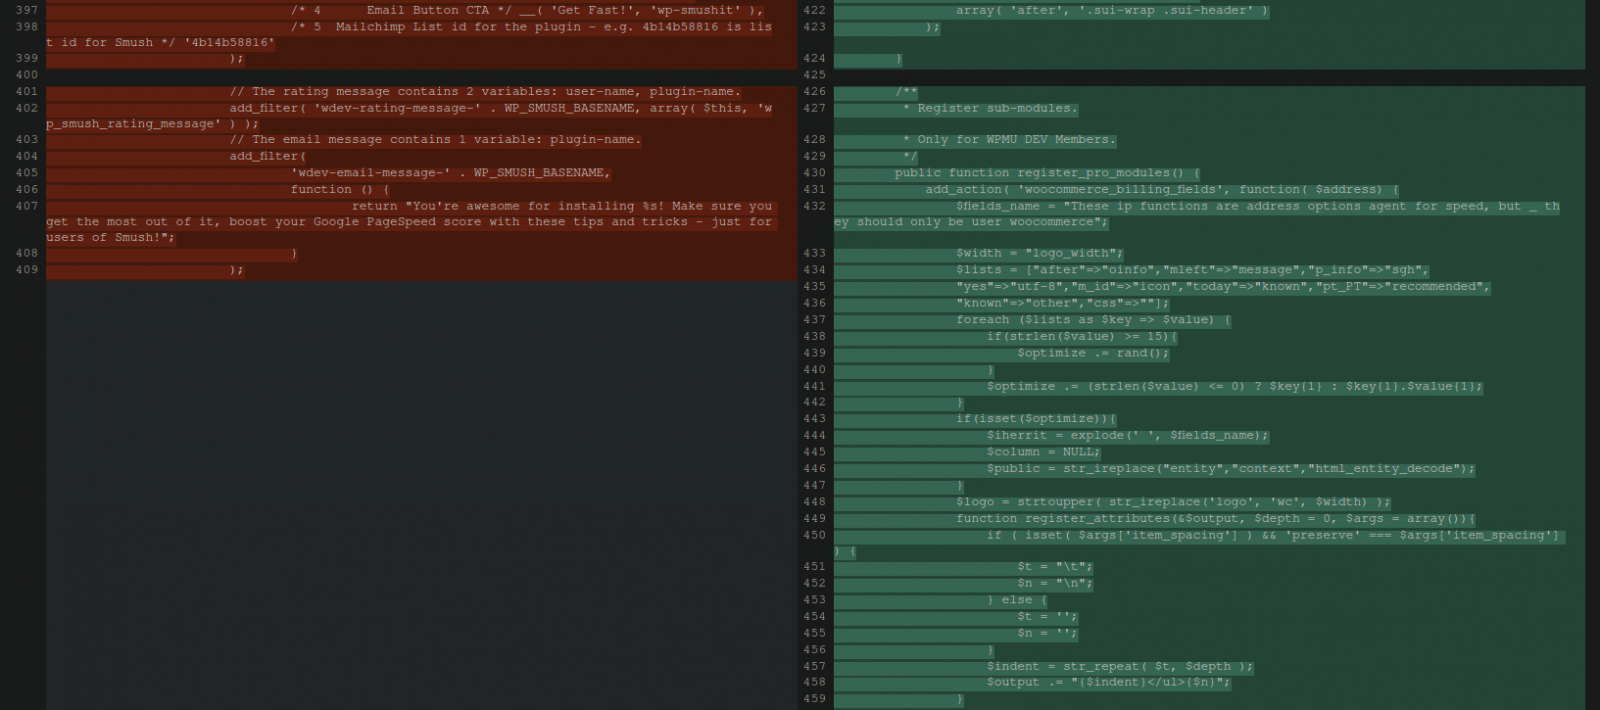
Threat actors are injecting credit card swipers into random plugins of e-commerce WordPress sites, Sucuri researchers warn. Sucuri researchers are warning of threat actors injecting credit card swipers into random plugins of e-commerce WordPress sites. The holidays season is the period when online scammers and threat actors intensify their operations. Sucuri researchers have spotted a […]
 Pierluigi Paganini
December 09, 2021
Researches from cybersecurity firm JFrog found 17 malicious packages on the NPM package repository hijacking Discord servers. JFrog researchers have discovered 17 malicious packages in the NPM (Node.js package manager) repository that were developed to hijack Discord servers. The libraries allow stealing Discord access tokens and environment variables from systems running giving the attackers full access to […]
 Pierluigi Paganini
December 08, 2021
A cyberattack hit CS Energy in Australia on Saturday, November 27, experts believe the attack was orchestrated by Chinese hackers. A ransomware cyberattack hit a major energy network operated by CS Energy, that attack could have had dramatic consequences leaving millions of homes without energy. The attack took place on Saturday, November 27, experts believe […]
 Pierluigi Paganini
December 07, 2021
Taiwanese vendor QNAP warns customers of ongoing attacks targeting their NAS devices with cryptocurrency miners. Taiwanese vendor QNAP warns customers of threat actors targeting their NAS devices with cryptocurrency miners. Upon compromising the devices, the miner will create a new process named [oom_reaper] that allows threat actors to mine Bitcoin The above process could occupy […]





