



 Pierluigi Paganini
 May 22, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Trend Micro Apex One and Langflow flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Windows Shell and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities (KEV) catalog. Below are the flaws added to the catalog: CVE-2025-34291 (CVSS score of 9.4) is […]
 Pierluigi Paganini
May 22, 2026
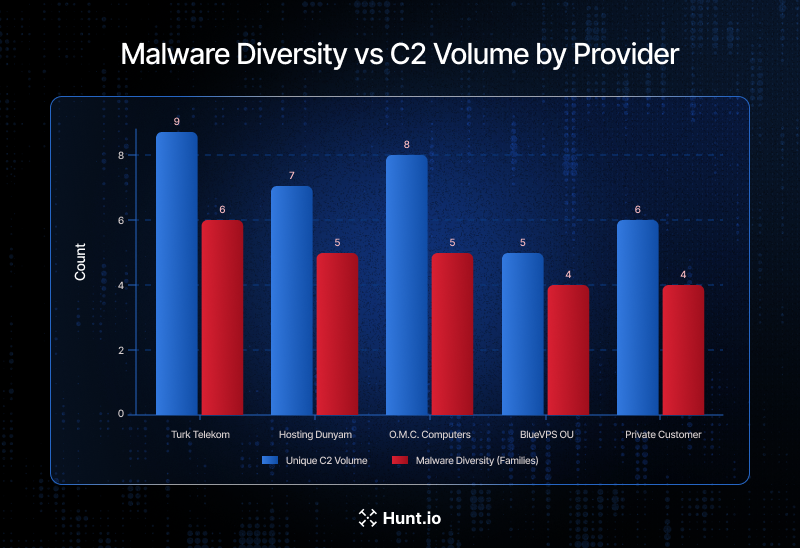
Hunt.io mapped 1,350+ C2 servers across the Middle East, revealing how a small group of providers quietly supports major malware activity. For years, threat intelligence focused mostly on malware families, phishing domains, and individual indicators. But a new report from Hunt.io shows why defenders may need to pay closer attention to something more boring, hosting […]
Pierluigi Paganini
May 21, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft and Adobe flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Windows Shell and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities (KEV) catalog. Below are the flaws added to the catalog: CVE-2008-4250 (CVSS v3.1 score of 9.8) is a […]
 Pierluigi Paganini
May 21, 2026
Attackers bypassed MFA on patched SonicWall Gen6 VPNs because admins missed extra manual steps required to fully fix the flaw. There is a particular kind of security failure that is harder to catch than an unpatched system: a patched system where the patch did not actually work because nobody followed all the steps. That is […]
 Pierluigi Paganini
May 20, 2026
PinTheft is a Linux LPE flaw in the RDS subsystem with public exploit code. Arch Linux users face the highest risk and should patch immediately. The wave of Linux local privilege escalation vulnerabilities showing up with working exploit code is not slowing down. The latest is PinTheft, discovered by the V12 security team, which affects […]
 Pierluigi Paganini
May 20, 2026
Microsoft acknowledged the YellowKey BitLocker bypass flaw and released mitigations, urging admins to disable autofstx.exe and enable TPM+PIN. A week after Chaotic Eclipse publicly dropped the YellowKey vulnerability, Microsoft acknowledged it and published a mitigation. Not a patch, a mitigation. The distinction matters, and we will get to why. The flaw, tracked as CVE-2026-45585 (CVSS […]
 Pierluigi Paganini
May 20, 2026
One employee installed a trojanized VS Code extension. Result: ~3,800 GitHub internal repositories exfiltrated. TeamPCP claims credit, wants $50K. There is something almost ironic about GitHub, the platform that hosts the code for most of the world’s software, getting breached through a trojanized plugin for a code editor. But that is exactly what happened, and […]
 Pierluigi Paganini
May 20, 2026
A Huawei zero-day flaw reportedly caused Luxembourg’s 2025 nationwide outage, disrupting landline, 4G/5G, and emergency services On July 23, 2025, a nationwide telecom outage in Luxembourg was reportedly triggered by a previously undisclosed flaw in Huawei enterprise routers. The attack disrupted landline, 4G, 5G, and emergency communications for more than three hours after specially crafted […]
 Pierluigi Paganini
May 19, 2026
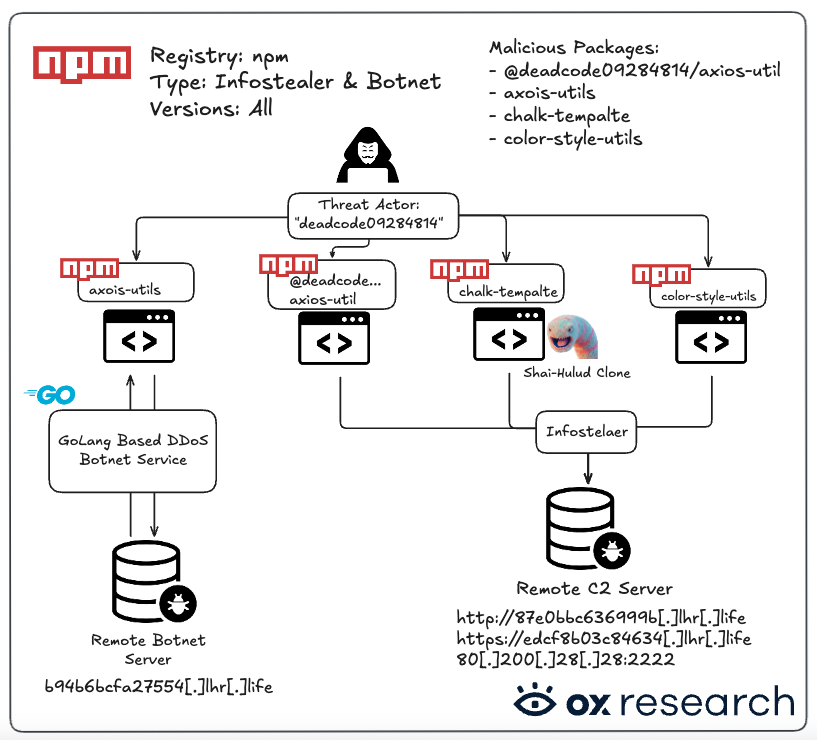
Shai-Hulud worm copycats are already attacking NPM developers after its source code leaked, enabling fast supply chain exploitation. The first copycats of the Shai-Hulud worm have already started showing up online, only a few days after the malware’s source code was dumped on GitHub. Researchers had warned this would happen almost immediately, and they were […]
 Pierluigi Paganini
May 18, 2026
Grafana confirmed a GitHub token breach that exposed source code, but said no customer data or systems were affected. Grafana Labs confirmed a security incident after the extortion group Coinbase Cartel listed it on a leak site and claimed data theft on May 15. The breach was triggered by a compromised token that gave attackers […]






