


 Pierluigi Paganini
 August 29, 2020
North Korea-linked APT group BeagleBoyz intensified its operations since February, US CISA, Department of the Treasury, FBI, and USCYBERCOM warn. According to a joint advisory issued by the Cybersecurity and Infrastructure Security Agency (CISA), the Department of the Treasury, the Federal Bureau of Investigation (FBI), and U.S. Cyber Command (USCYBERCOM) North Korea-linked APT group BeagleBoyz […]
 Pierluigi Paganini
August 28, 2020
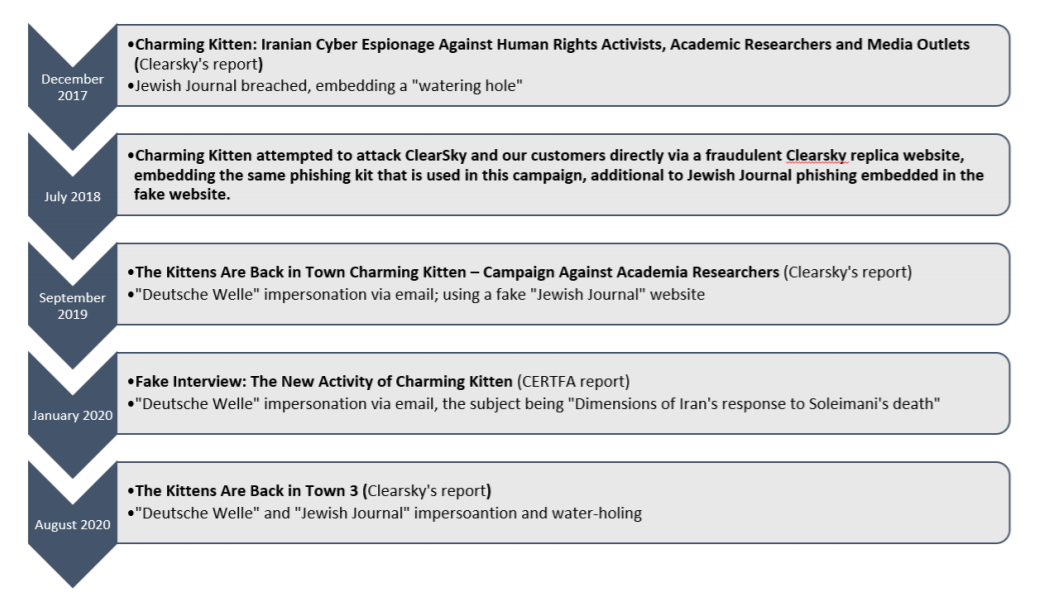
The Iran-linked Charming Kitten APT group leveraged on WhatsApp and LinkedIn to carry out phishing attacks, researchers warn. Clearsky security researchers revealed that Iran-linked Charming Kitten APT group is using WhatsApp and LinkedIn to conduct spear-phishing attacks. Iran-linked Charming Kitten group, (aka APT35, Phosphorus, Newscaster, and Ajax Security Team) made the headlines in 2014 when experts at iSight issued a report describing the most elaborate net-based spying […]
 Pierluigi Paganini
August 28, 2020
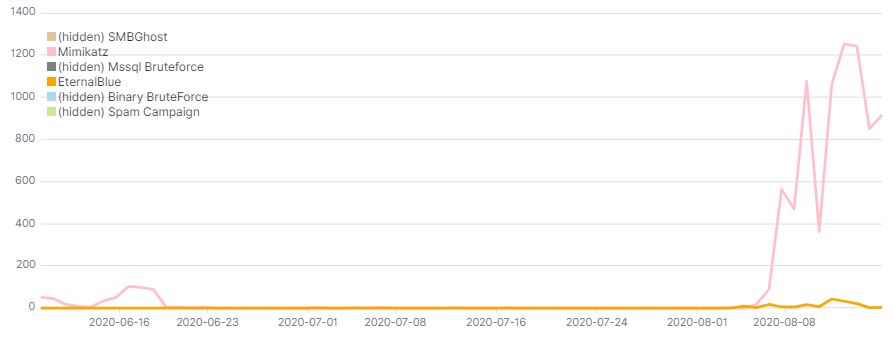
A new variant of the infamous Lemon_Duck cryptomining malware has been updated to targets Linux devices. Security researchers from Sophos have spotted a new variant of the Lemon_Duck cryptomining malware that has been updated to compromise Linux machines via SSH brute force attacks. The new variant also exploits SMBGhost bug in Windows systems, and is also able to target servers running Redis […]
 Pierluigi Paganini
August 27, 2020
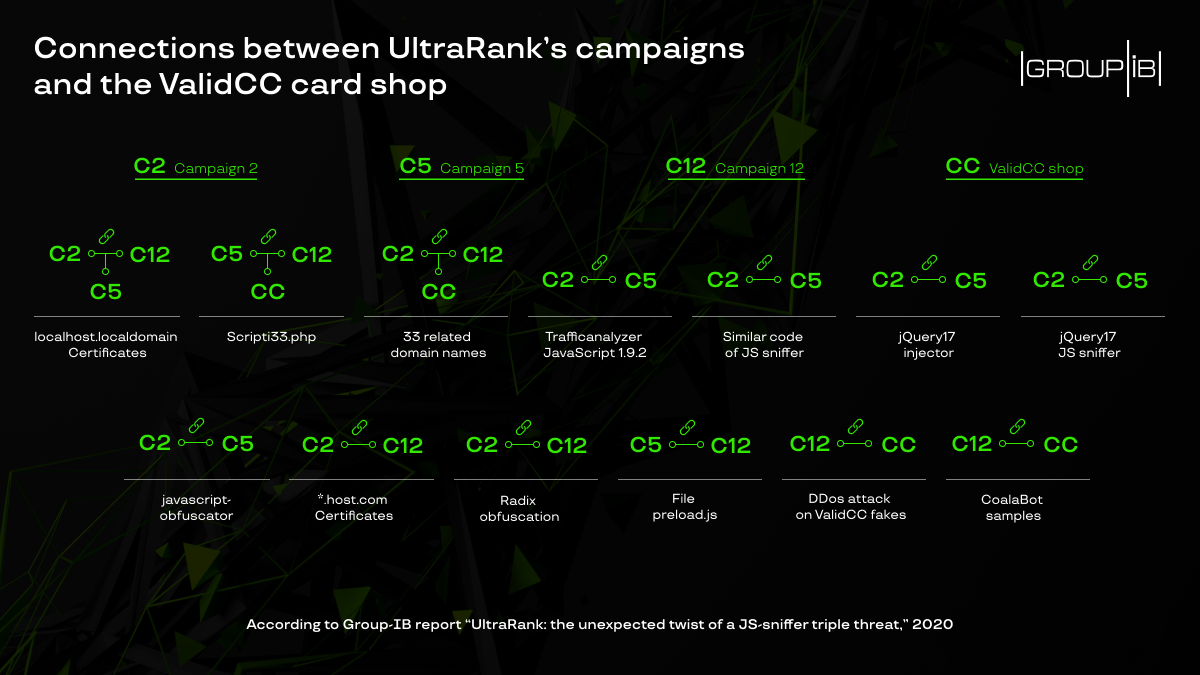
Group-IB security researchers provide evidence linking three campaigns with the use of various JS-sniffer families. Singapore – Group-IB, a global threat hunting and intelligence company headquartered in Singapore, today released its analytical report “UltraRank: the unexpected twist of a JS-sniffer triple threat.” In its report, Group-IB Threat Intelligence experts provide evidence linking three campaigns with the use of various JavaScript-sniffer families […]
 Pierluigi Paganini
August 27, 2020
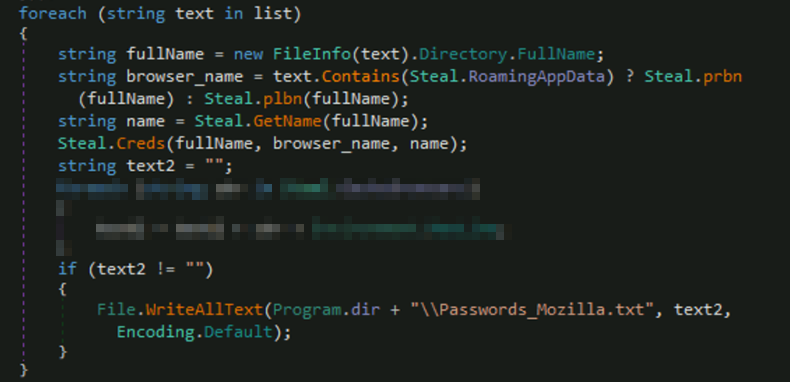
Microsoft warned of a recently uncovered piece of malware, tracked as Anubis that was designed to steal information from infected systems. This week, Microsoft warned of a recently uncovered piece of malware, tracked as Anubis, that was distributed in the wild to steal information from infected systems. Anubis is the name of an Android malware […]
 Pierluigi Paganini
August 27, 2020
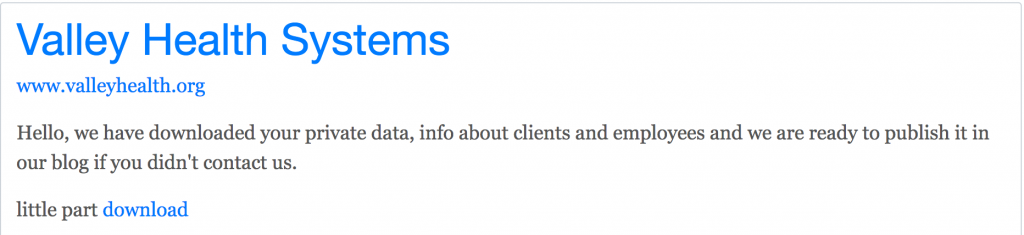
REvil ransomware operators claimed to have breached another healthcare organization, the victim is Valley Health Systems. During ordinary monitoring activity of data leaks, the Cyble Research Team identified a leak disclosure post published by the REvil ransomware operators claiming to have breached a healthcare organization, the Valley Health Systems. Healthcare organizations are a privileged target of […]
 Pierluigi Paganini
August 26, 2020
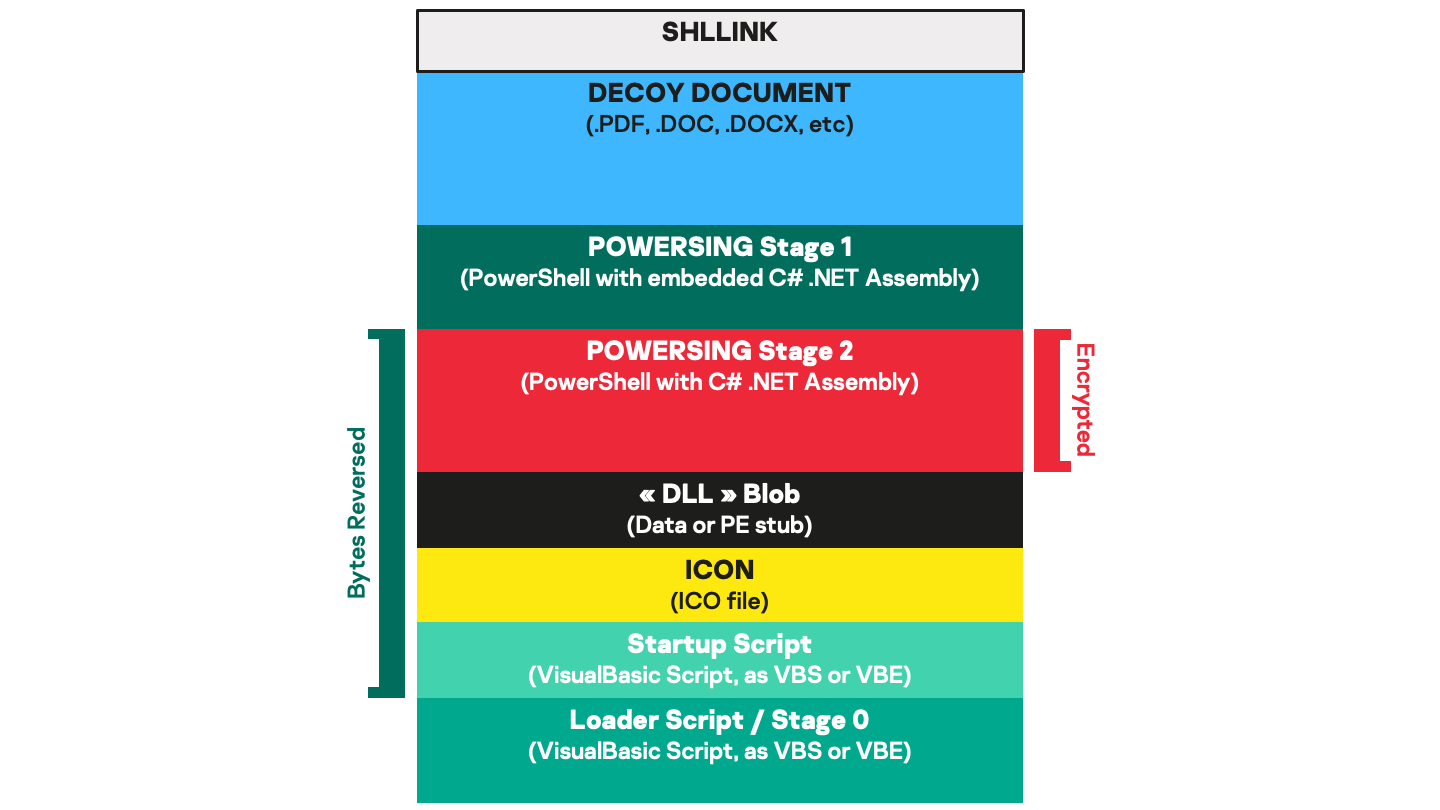
A hack-for-hire group, tracked as DeathStalker, has been targeting organizations in the financial sector since 2012 Kaspersky researchers say. DeathStalker is a hack-for-hire group discovered by Kaspersky, it has been targeting organizations worldwide, mainly law firms and financial entities, since 2012. Victim organizations are small and medium-sized businesses located in Argentina, China, Cyprus, India, Israel, […]
 Pierluigi Paganini
August 26, 2020
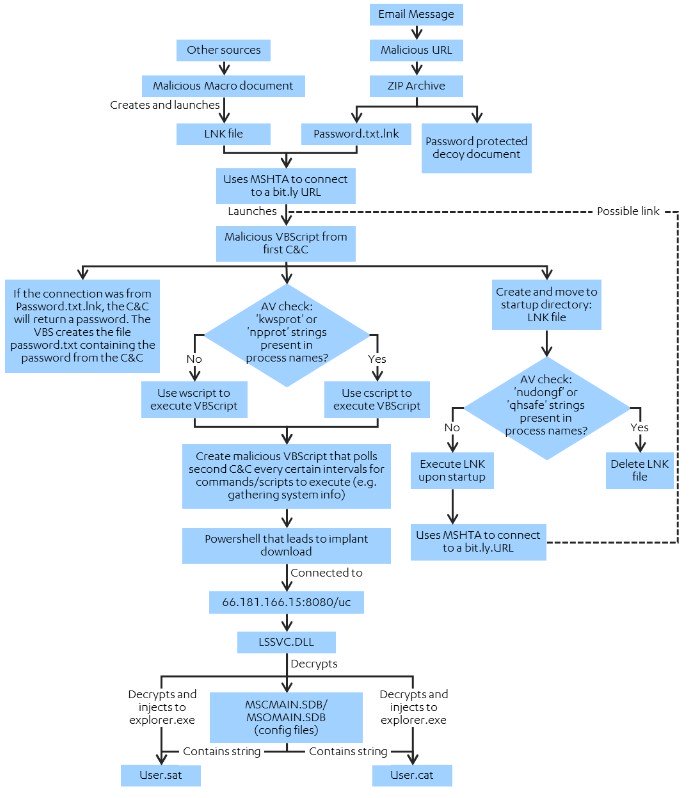
North Korea-linked Lazarus APT group targets cryptocurrency organizations with fake job offers in an ongoing spear-phishing campaign. North Korea-linked Lazarus APT group (aka HIDDEN COBRA) has been observed while using LinkedIn lures in a spear-phishing campaign targeting the cryptocurrency organizations worldwide, including in the United States, the United Kingdom, Germany, Singapore, the Netherlands, Japan. The activity of […]
 Pierluigi Paganini
August 24, 2020
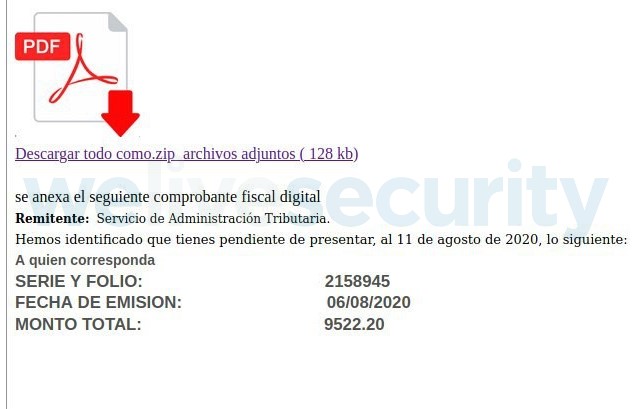
Operators of Grandoreiro Latin American banking trojan have launched a new campaign using emails posing as the Agencia Tributaria in order to infect new victims. Operators behind the Grandoreiro banking trojan, which is popular in Latin America, have been using emails posing as the Agencia Tributaria to trick victims into installing the malware. The campaign began […]
 Pierluigi Paganini
August 24, 2020
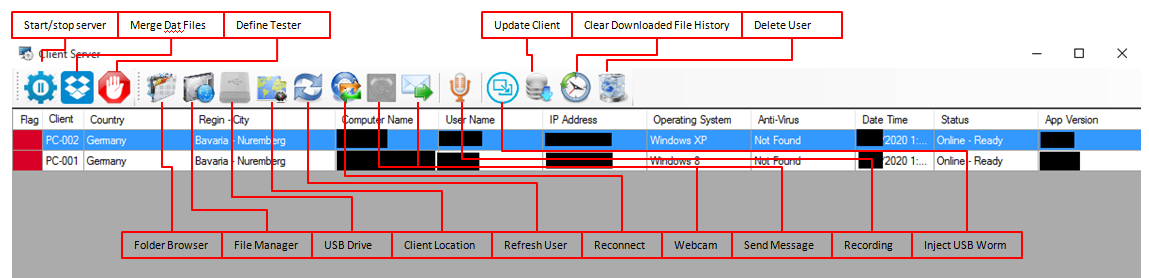
The Transparent Tribe cyber-espionage group continues to improve its arsenal while targets Military and Government entities. The Transparent Tribe APT group is carrying out an ongoing cyberespionage campaign aimed at military and diplomatic targets worldwide. The group upgraded its Crimson RAT by adding a management console and implementing a USB worming capability that allows it […]






