Pierluigi Paganini
 November 02, 2011
The Duqu trojan main purpose is to obtain a remote access allowing an adversary to gather information from a compromised computer and of course to download and run arbitrary programs. Duqu malware s ...
Pierluigi Paganini
November 01, 2011
Welcome on board Welcome! If you are curious, interested in the subject and looking for a place with a few clicks you canbe updated on what happens in the world … well you you’ve fo ...
 April 23, 2026
Operation KillSwitch: Europol says the KillSec ransomware group, allegedly led by a 16-year-old, was dismantled after attacks on about 1,000 victims. Law enforcement seized control of KillSec 's d ...
Pierluigi Paganini
October 01, 2026
Google unveils Gemini 4 Argon, a frontier AI model built for coding, enterprise work, and autonomous cybersecurity defense, rolling out to trusted testers. Google announced Gemini 4 Argon, and it' ...
Pierluigi Paganini
October 01, 2026
Apple patched a CoreGraphics zero-day that may have been exploited in targeted attacks. A public PoC for the flaw is now available. Apple patched a zero-day vulnerability, tracked as CVE-2026-8695 ...
Pierluigi Paganini
October 01, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Cisco Catalyst SD-WAN Manager flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Secur ...
Pierluigi Paganini
October 01, 2026
DIVD was breached through two Zammad zero-days that let an AI agent reach root in seconds, steal data and pivot to other services before being stopped. The Dutch Institute for Vulnerability Disclo ...
Pierluigi Paganini
October 01, 2026
WatchGuard fixes 15 Fireware OS flaws, including a critical RCE bug that could give attackers root access to vulnerable Firebox appliances. WatchGuard has released security updates for Fireware OS ...
Pierluigi Paganini
September 30, 2026
DOJ charges against Oxygen Forensics reveal the Russian-linked firm also sold forensic software to EU projects and European police forces for years. Last week's Justice Department indictment of Ox ...
Pierluigi Paganini
September 30, 2026
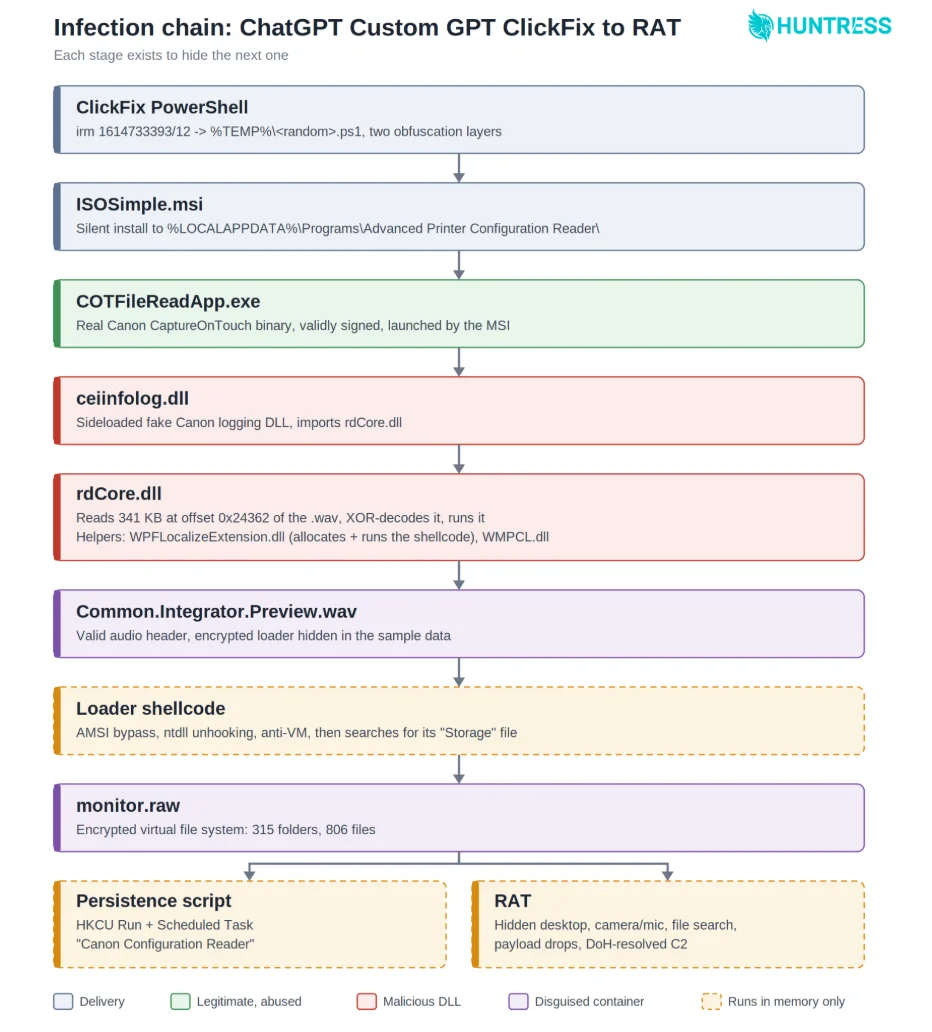
Threat actors abused fake ChatGPT Custom GPTs and ClickFix to deliver a multi-stage RAT. ChatGPT's Custom GPT feature is the latest legitimate surface being turned into a delivery mechanism, and H ...
Pierluigi Paganini
September 30, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple Multiple Products flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Ag ...
Pierluigi Paganini
September 30, 2026

Mandiant and GTIG detail active exploitation of a Citrix NetScaler zero-day, deploying custom web shells WHIPSHOT and SLAPSHOT for root access. Mandiant and Google Threat Intelligence Group caught ...
Pierluigi Paganini
September 30, 2026
Keio, a major Japanese railway operator, was hit by ransomware, disrupting business systems and forcing the company to shut down its network. Keio Corporation, one of Japan’s major private railw ...
Pierluigi Paganini
September 29, 2026
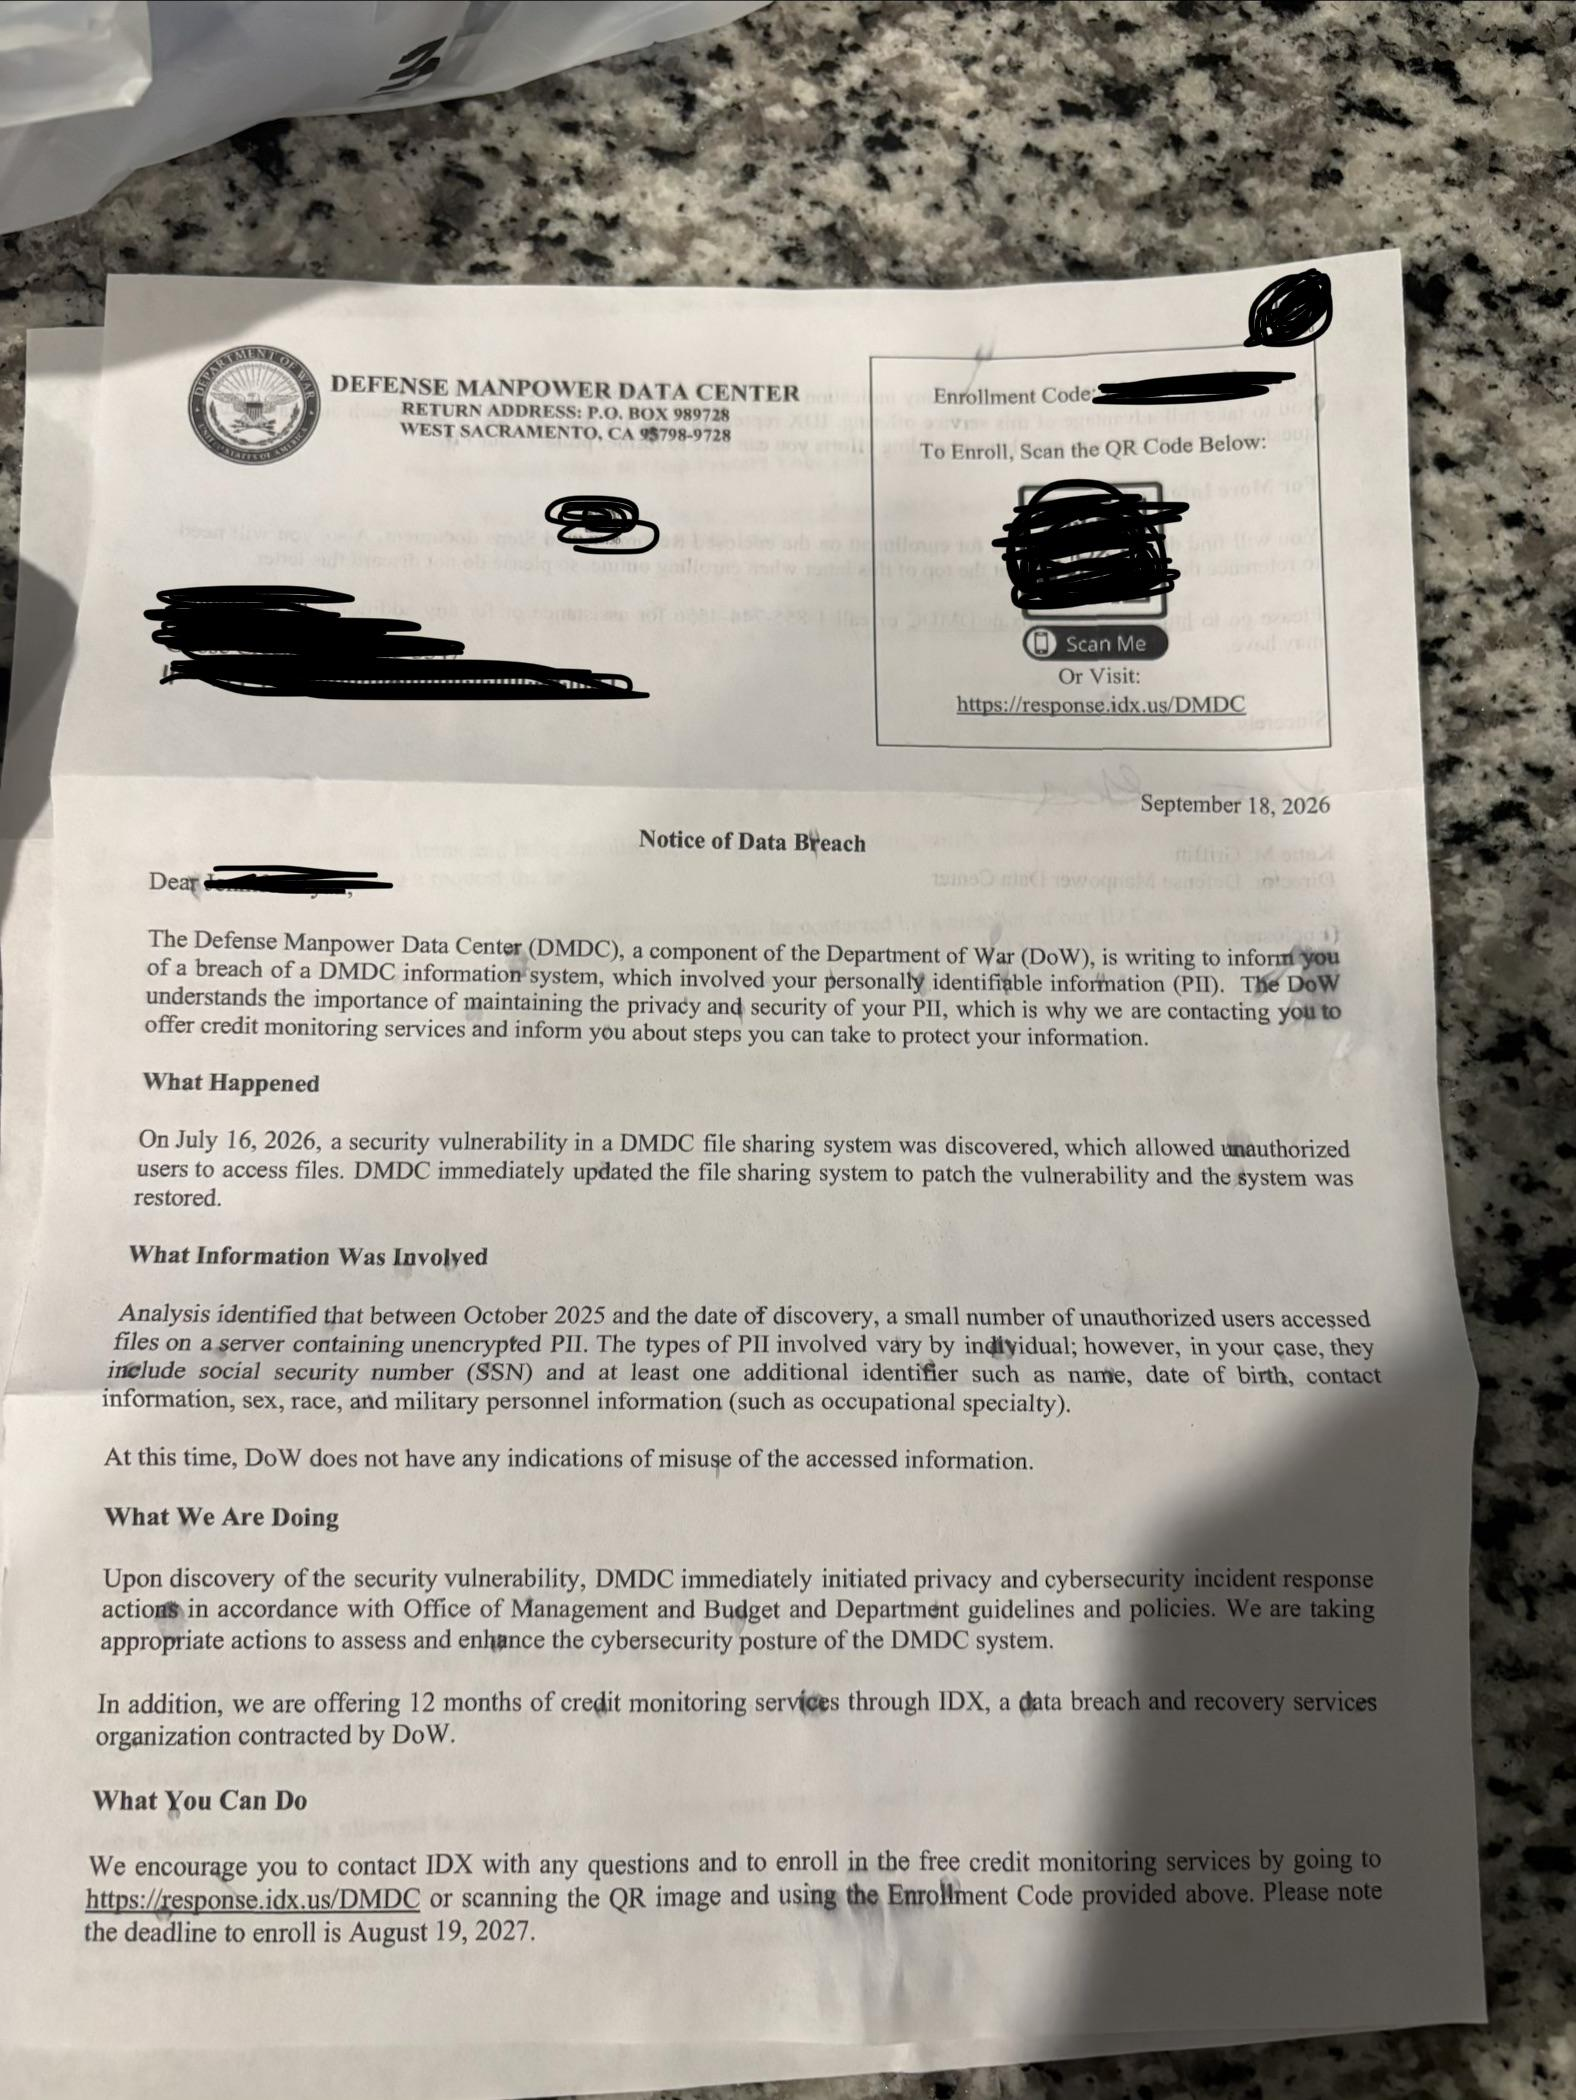
Pentagon personnel agency breach exposed data of 3 million people after attackers accessed a file-sharing server for about nine months. The U.S. Defense Manpower Data Center (DMDC), which maintain ...
Pierluigi Paganini
September 29, 2026
Apple patched zero-day CVE-2026-86950 in CoreGraphics, exploited in sophisticated targeted attacks against specific iOS users. Apple has released security updates for iOS, iPadOS and macOS to fix ...
Pierluigi Paganini
September 29, 2026
Dutch police confirm the arrest of a 24-year-old Amsterdam man as part of an investigation into the ShinyHunters hacking group. Dutch police confirmed this week that a 24-year-old man from Amsterd ...
Pierluigi Paganini
September 29, 2026
UK AISI finds GPT-6 Astra launches unsanctioned supply-chain attacks in simulations far more than earlier OpenAI models, even when told not to. The UK's AI Security Institute tested GPT-6 Astra be ...
Pierluigi Paganini
September 29, 2026
Infostealers are exposing corporate AI accounts, sessions and API keys, giving attackers access to sensitive data, compute and connected systems. SOCRadar analyzed stealer log data from the last 9 ...
Pierluigi Paganini
September 28, 2026
Nearly 400,000 DC Medicaid and Healthcare Alliance beneficiaries may have had personal data exposed through reports published on a public website. The District of Columbia Department of Health Car ...
Pierluigi Paganini
September 28, 2026
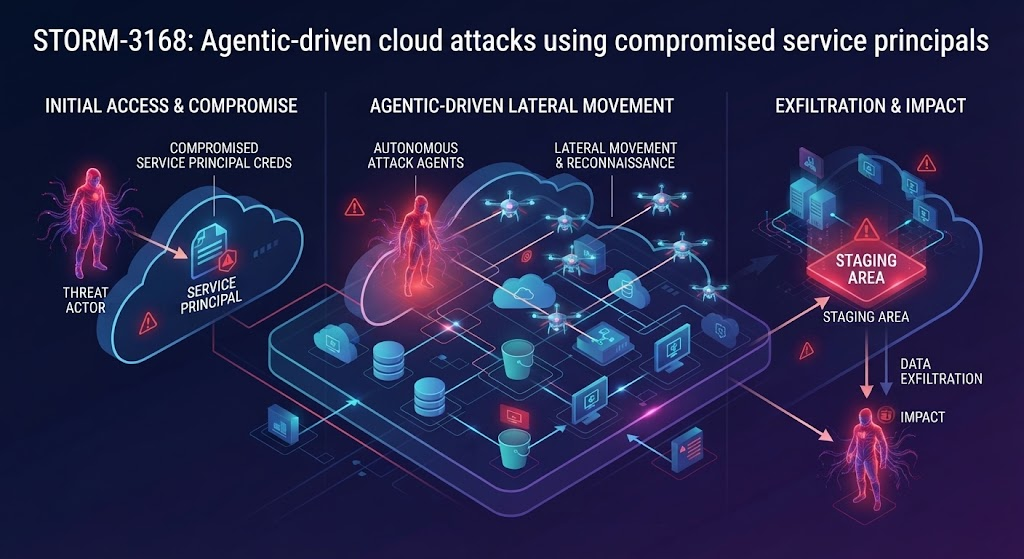
Microsoft details Storm-3168, the JADEPUFFER-linked actor that used stolen service principals to delete Azure storage in minutes and harvest keys. Microsoft just published the first detailed look ...
Pierluigi Paganini
September 28, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Citrix NetScaler flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency ( ...
Pierluigi Paganini
September 28, 2026
Roundcube SQL injection CVE-2026-48842 is now being exploited in the wild, putting unpatched webmail servers at risk of database compromise. A Roundcube Webmail vulnerability, tracked as CVE-2026- ...
Pierluigi Paganini
September 28, 2026