Pierluigi Paganini
 November 01, 2011
Welcome on board Welcome! If you are curious, interested in the subject and looking for a place with a few clicks you canbe updated on what happens in the world … well you you’ve fo ...
 April 23, 2026
October 18, 2026

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter IronChain Ransomware Threatens Businesse ...
Pierluigi Paganini
October 18, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly Security ...
Pierluigi Paganini
October 18, 2026
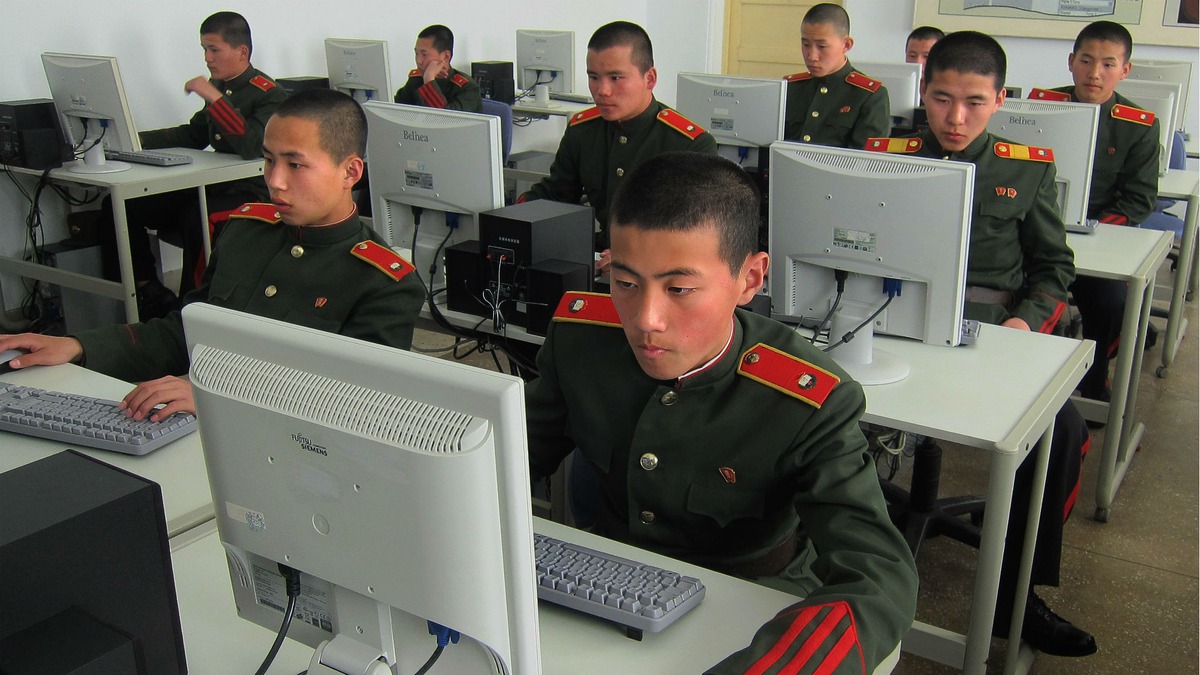
The FBI raided 40 Texas homes over a North Korean scheme that used fake IT workers to target 70 US companies and generate $3 million. The Justice Department (DoJ) announced coordinated enforcement ...
Pierluigi Paganini
October 17, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Fortinet Multiple Products and BeyondTrust Remote Support flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecu ...
Pierluigi Paganini
October 17, 2026
A cyber incident at a BAE Systems subsidiary just stopped every bankruptcy court in the US from sending notices, and the problem started a week ago. A security incident at BAE Systems Inc., the US ...
Pierluigi Paganini
October 17, 2026
India's CERT-In warns AI agents accessed confidential data undetected, while attackers used offensive AI frameworks to accelerate cyberattacks. CERT-In, India's national cyber response team, publi ...
Pierluigi Paganini
October 17, 2026
Burger King Japan disclosed a breach exposing 11.18 million app users' personal data after attackers accessed its membership system in early October. Burger King Japan has disclosed a data breach ...
Pierluigi Paganini
October 16, 2026
F5 addressed multiple vulnerabilities, including critical RCE flaws in NGINX that attackers could exploit without authentication. Security and application delivery firm F5 announced fixes for elev ...
Pierluigi Paganini
October 16, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Atlassian flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) a ...
Pierluigi Paganini
October 16, 2026
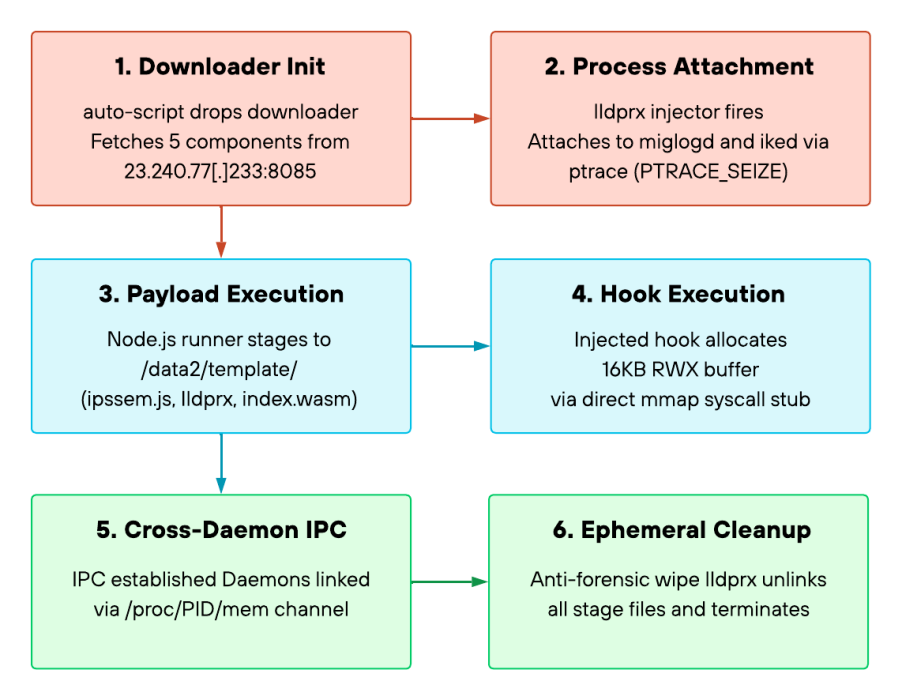
PEERSTITCH malware exploited FortiManager to expose 500+ firewalls, evade detection inside FortiOS memory, and maintain stealthy access. PEERSTITCH, a stealthy implant deployed during a prolonged ...
Pierluigi Paganini
October 16, 2026
The regulated utility company CenterPoint Energy says a data breach exposed the personal information of more than 1 million people in Texas. CenterPoint Energy is a regulated utility company used ...
Pierluigi Paganini
October 16, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Palo Alto Networks PAN-OS, Ahsay AhsayCBS, and Cisco Secure Email Gateway flaws to its Known Exploited Vulnerabilities catalog. Th ...
Pierluigi Paganini
October 15, 2026
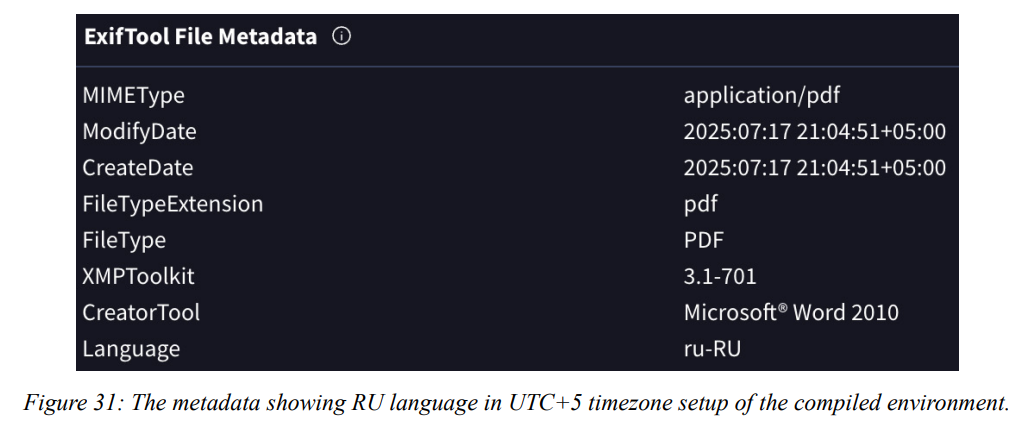
Silent Lynx, a group likely based in Kazakhstan, targets Russian energy and government entities in espionage campaigns across Central Asia. Researchers from Cisco Talos and Recorded Future publish ...
Pierluigi Paganini
October 15, 2026
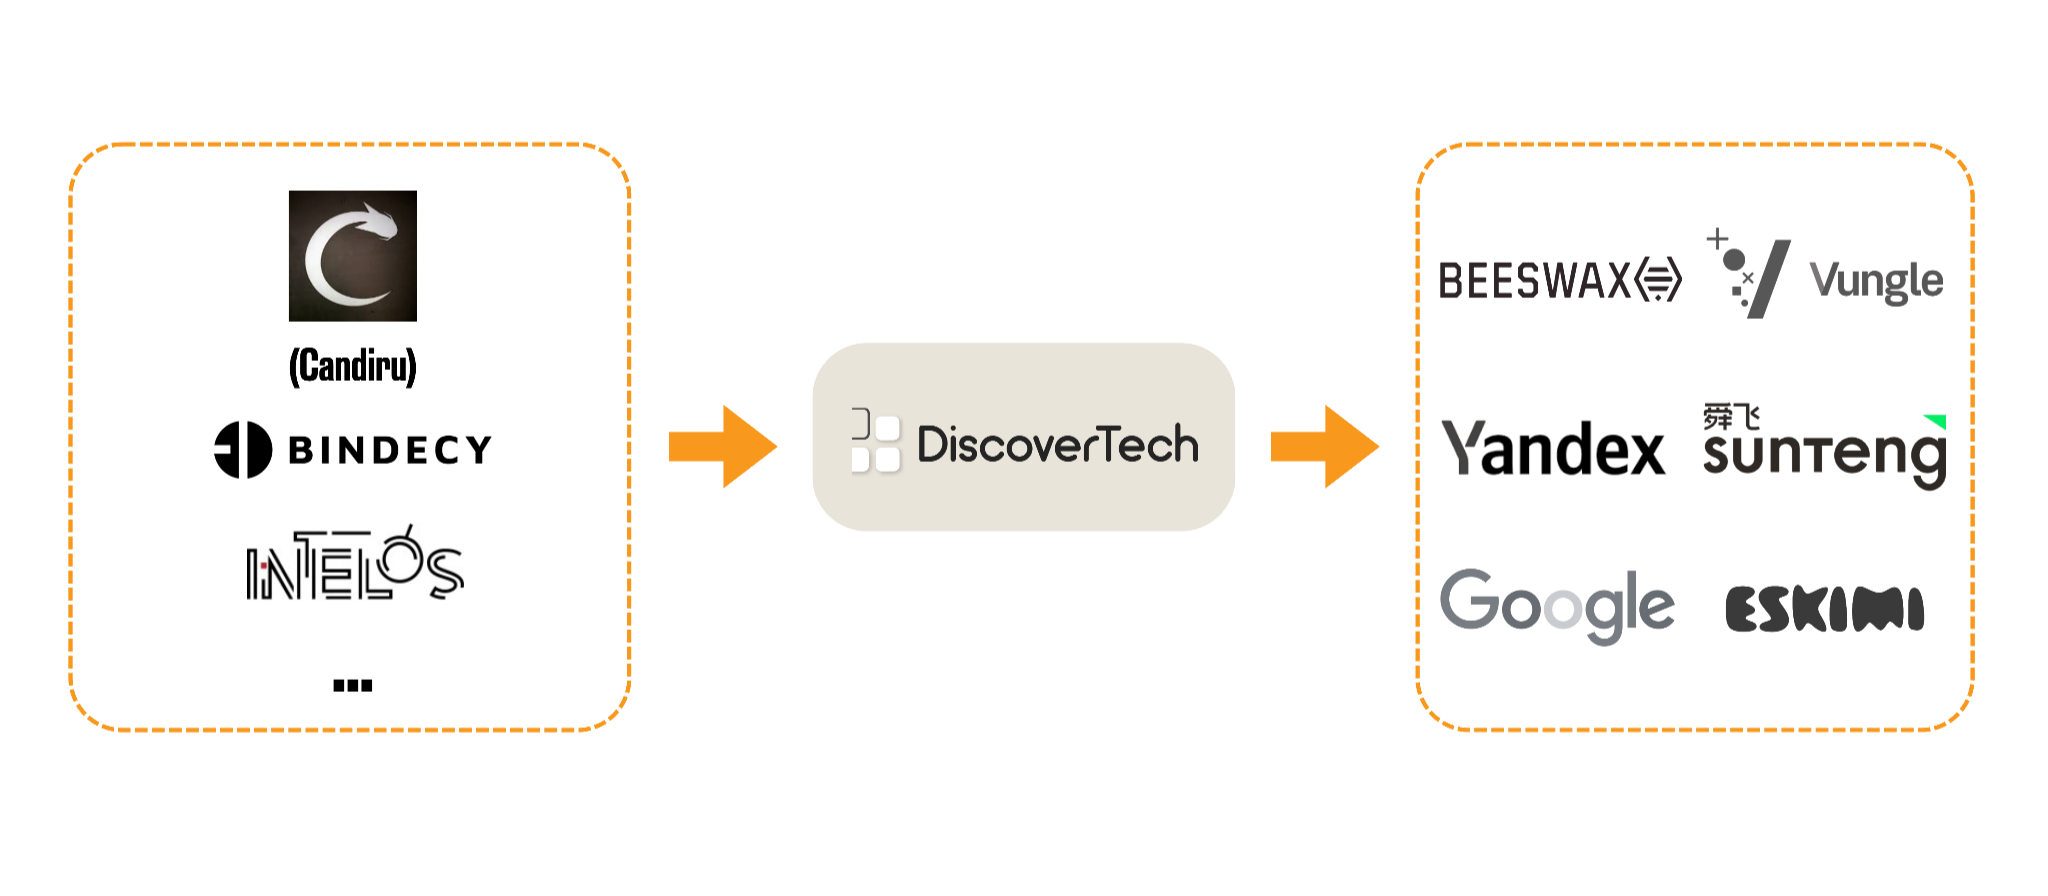
Spyware vendors use online ad infrastructure to profile targets and deliver exploits without requiring users to click anything. The investigation links Discover-Tech to Candiru, an Israeli spyware ...
Pierluigi Paganini
October 15, 2026
Attackers exploit a critical Cisco email gateway flaw to gain root access. Cisco urges customers to update scanner tools and check for compromise. Cisco confirmed this week that threat actors are ...
Pierluigi Paganini
October 15, 2026
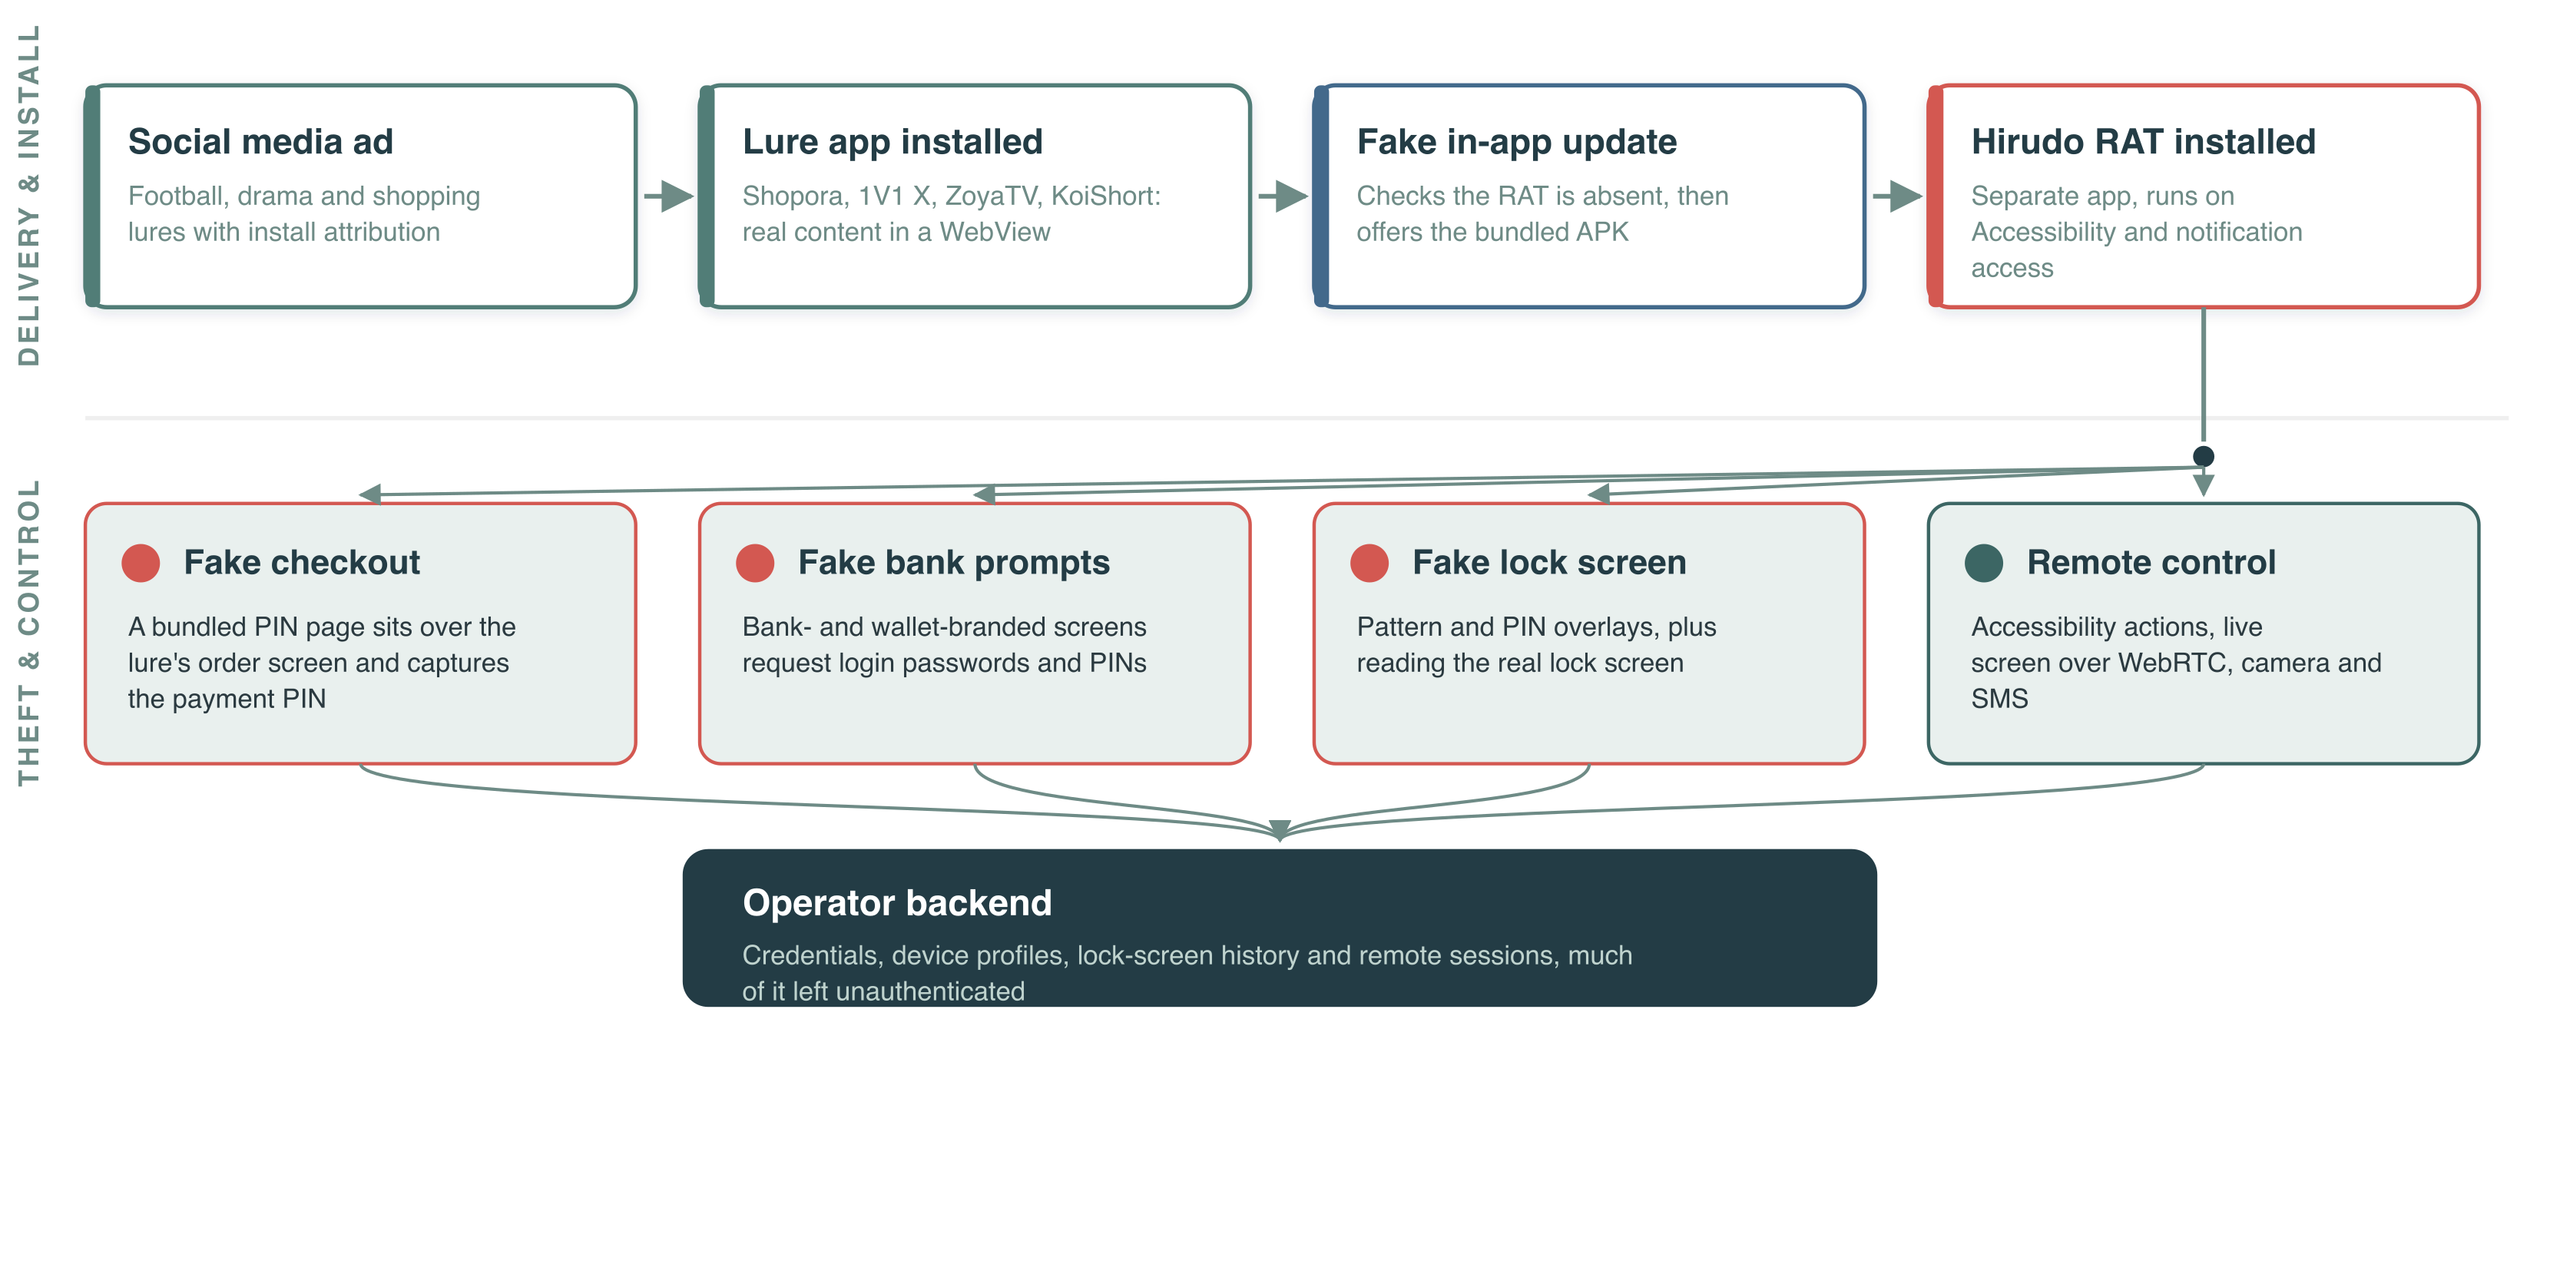
Android trojan Hirudo replaces genuine banking apps with modified versions to steal credentials and bypass security checks, enabling financial fraud. ThreatFabric researchers detailed a new Androi ...
Pierluigi Paganini
October 15, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Microsoft Windows Shell flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Ag ...
Pierluigi Paganini
October 14, 2026
Microsoft Patch Tuesday security updates for October 2026 address a record 1,415 vulnerabilities. Prioritize the exploited zero-day, critical bugs and potentially wormable vulnerabilities. Microso ...
Pierluigi Paganini
October 14, 2026
OpenAI employee charged with planting hidden audio recorders to capture sensitive discussions about AI research and company strategy. On September 30, OpenAI staff found a small audio recording de ...
Pierluigi Paganini
October 14, 2026

Ivanti VPN zero-days let attackers gain root access, steal credentials, evade detection, and prepare for wider network compromise. On October 5, Volexity started investigating suspicious activity ...
Pierluigi Paganini
October 14, 2026