Pierluigi Paganini
 November 02, 2011
Online Social Networks(OSN) are an integral part of today's Web. Hacktivist,Politicians, celebrities, revolutionists, and others use OSNs as carrier for their message to a wide audience. The downs ...
Pierluigi Paganini
November 02, 2011
The Duqu trojan main purpose is to obtain a remote access allowing an adversary to gather information from a compromised computer and of course to download and run arbitrary programs. Duqu malware s ...
Pierluigi Paganini
November 01, 2011
Welcome on board Welcome! If you are curious, interested in the subject and looking for a place with a few clicks you canbe updated on what happens in the world … well you you’ve fo ...
 April 23, 2026
October 09, 2026
October 09, 2026

Japan helped extradite a Russian suspect linked to Qilin ransomware to Germany, but the gang continued attacking victims after his arrest. Germany has arrested a Russian national believed to be a ...
Pierluigi Paganini
October 09, 2026

Anthropic launches free OSS Scanner, using AI to find open-source vulnerabilities and help maintainers fix bugs before attackers exploit them. Anthropic is launching OSS Scanner, a vulnerability s ...
Pierluigi Paganini
October 09, 2026

DOJ and FBI seized China-linked hacking tools Microscan and FishHub, linked to Integrity Tech and attacks on critical infrastructure worldwide. The Justice Department and FBI took down two hacking ...
Pierluigi Paganini
October 09, 2026
CrowdStrike analyzes open directories left by an attacker who used the ARTEX AI pentest tool and LLMs to breach South Korean financial firms. CrowdStrike published a research on a campaign against ...
Pierluigi Paganini
October 09, 2026
Italy's Foreign Ministry is defending its website against a cyberattack, checking embassy sites and pushing for EU action to identify attackers. On the morning of October 8, Italy's Ministry of Fo ...
Pierluigi Paganini
October 08, 2026
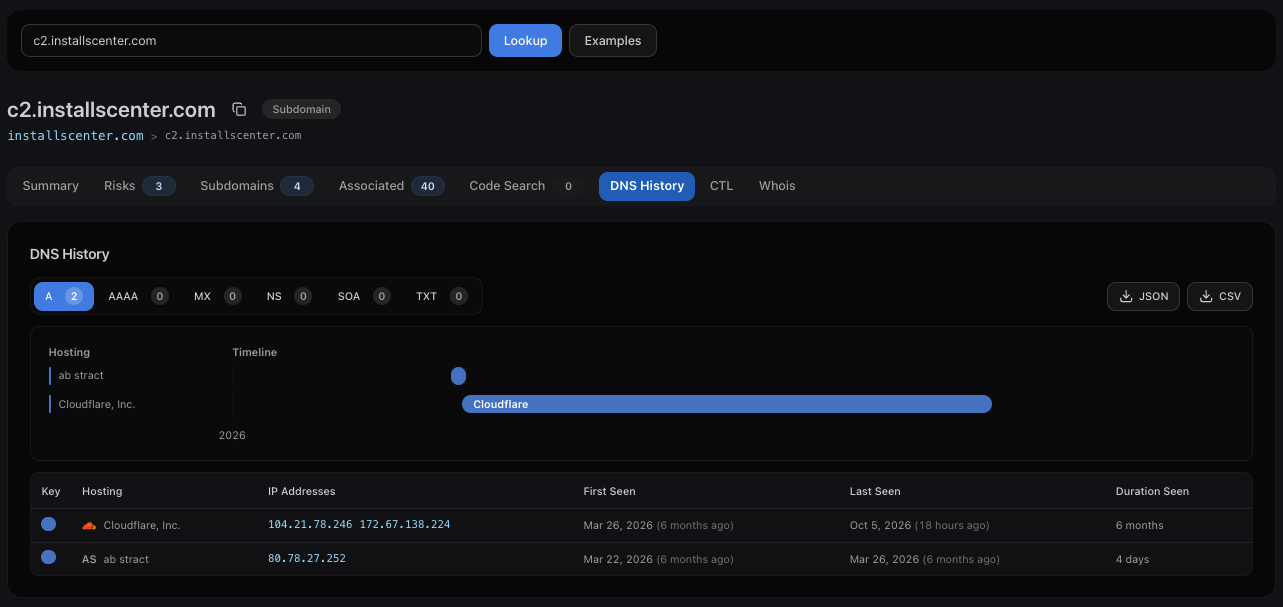
Hunt.io traced BraZetsu 's infrastructure and found that hosting patterns and certificate data remained useful after published IOCs became outdated. Group-IB researchers published a detailed write ...
Pierluigi Paganini
October 08, 2026

MonsterCloud owner Zohar Pinhasi allegedly paid ransomware demands behind clients’ backs, then charged them millions for the supposed recovery. Zohar Pinhasi, the owner of Florida-based MonsterC ...
Pierluigi Paganini
October 08, 2026
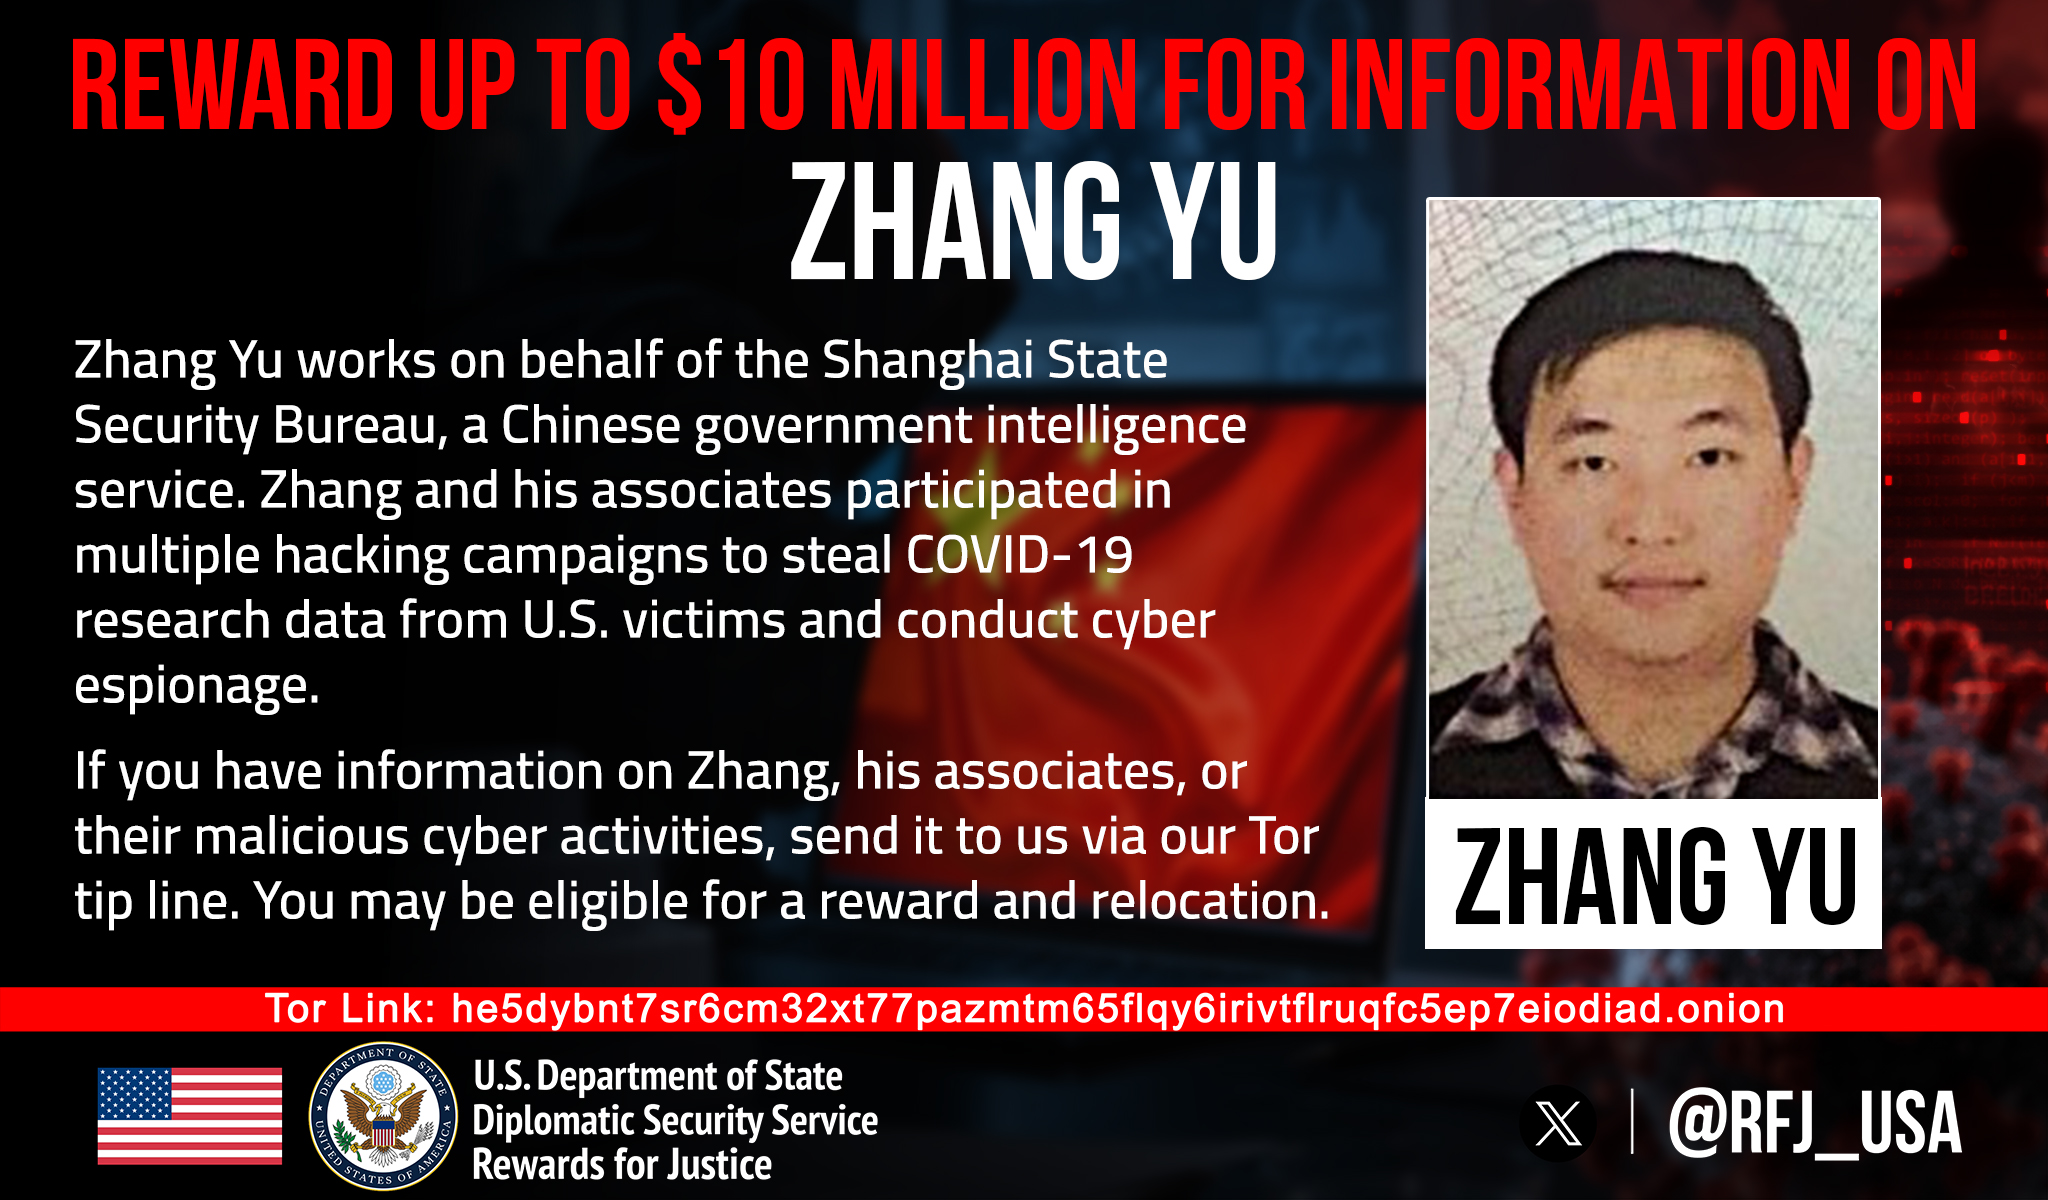
The U.S. offers $10M for Zhang Yu, accused of helping run HAFNIUM attacks that compromised thousands of organizations worldwide. The U.S. State Department is offering a $10 million reward for info ...
Pierluigi Paganini
October 08, 2026
Threat actors are exploiting CVE-2026-21589, a critical Atlassian flaw that can expose sensitive files across multiple Data Center products. Threat actors have started exploiting CVE-2026-21589 (C ...
Pierluigi Paganini
October 08, 2026

SonicWall patched a CVSS 10 pre-auth SSRF flaw in SMA1000 appliances that could let unauthenticated attackers reach internal functions. SonicWall released hotfixes for four vulnerabilities in its ...
Pierluigi Paganini
October 07, 2026

FBI and Secret Service warn FortiBleed, a credential-harvesting campaign against Fortinet firewalls, has compromised 86,644 devices and is locking out admins. The FBI and the U.S. Secret Service i ...
Pierluigi Paganini
October 07, 2026
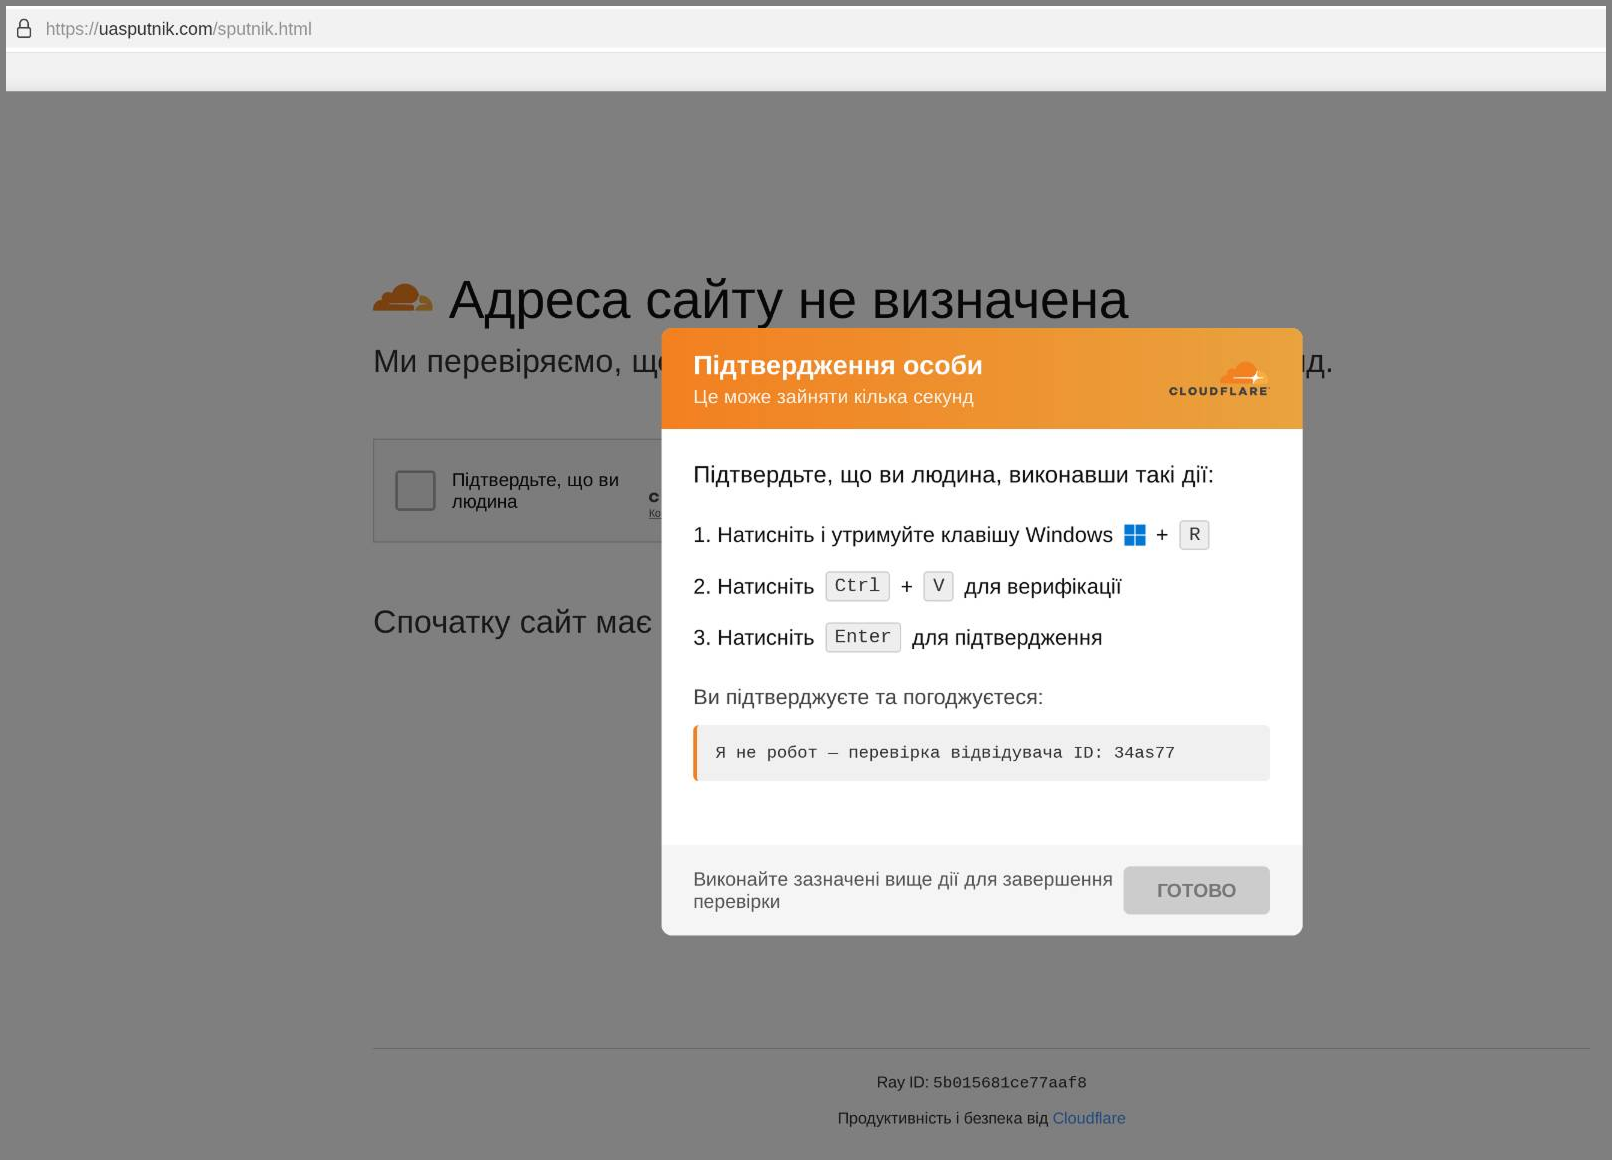
Over 100 hacked websites used fake Cloudflare checks to trick visitors into installing LunexStealer through ClickFix commands. The lure is the now-familiar ClickFix technique, dressed up as Cloudf ...
Pierluigi Paganini
October 07, 2026
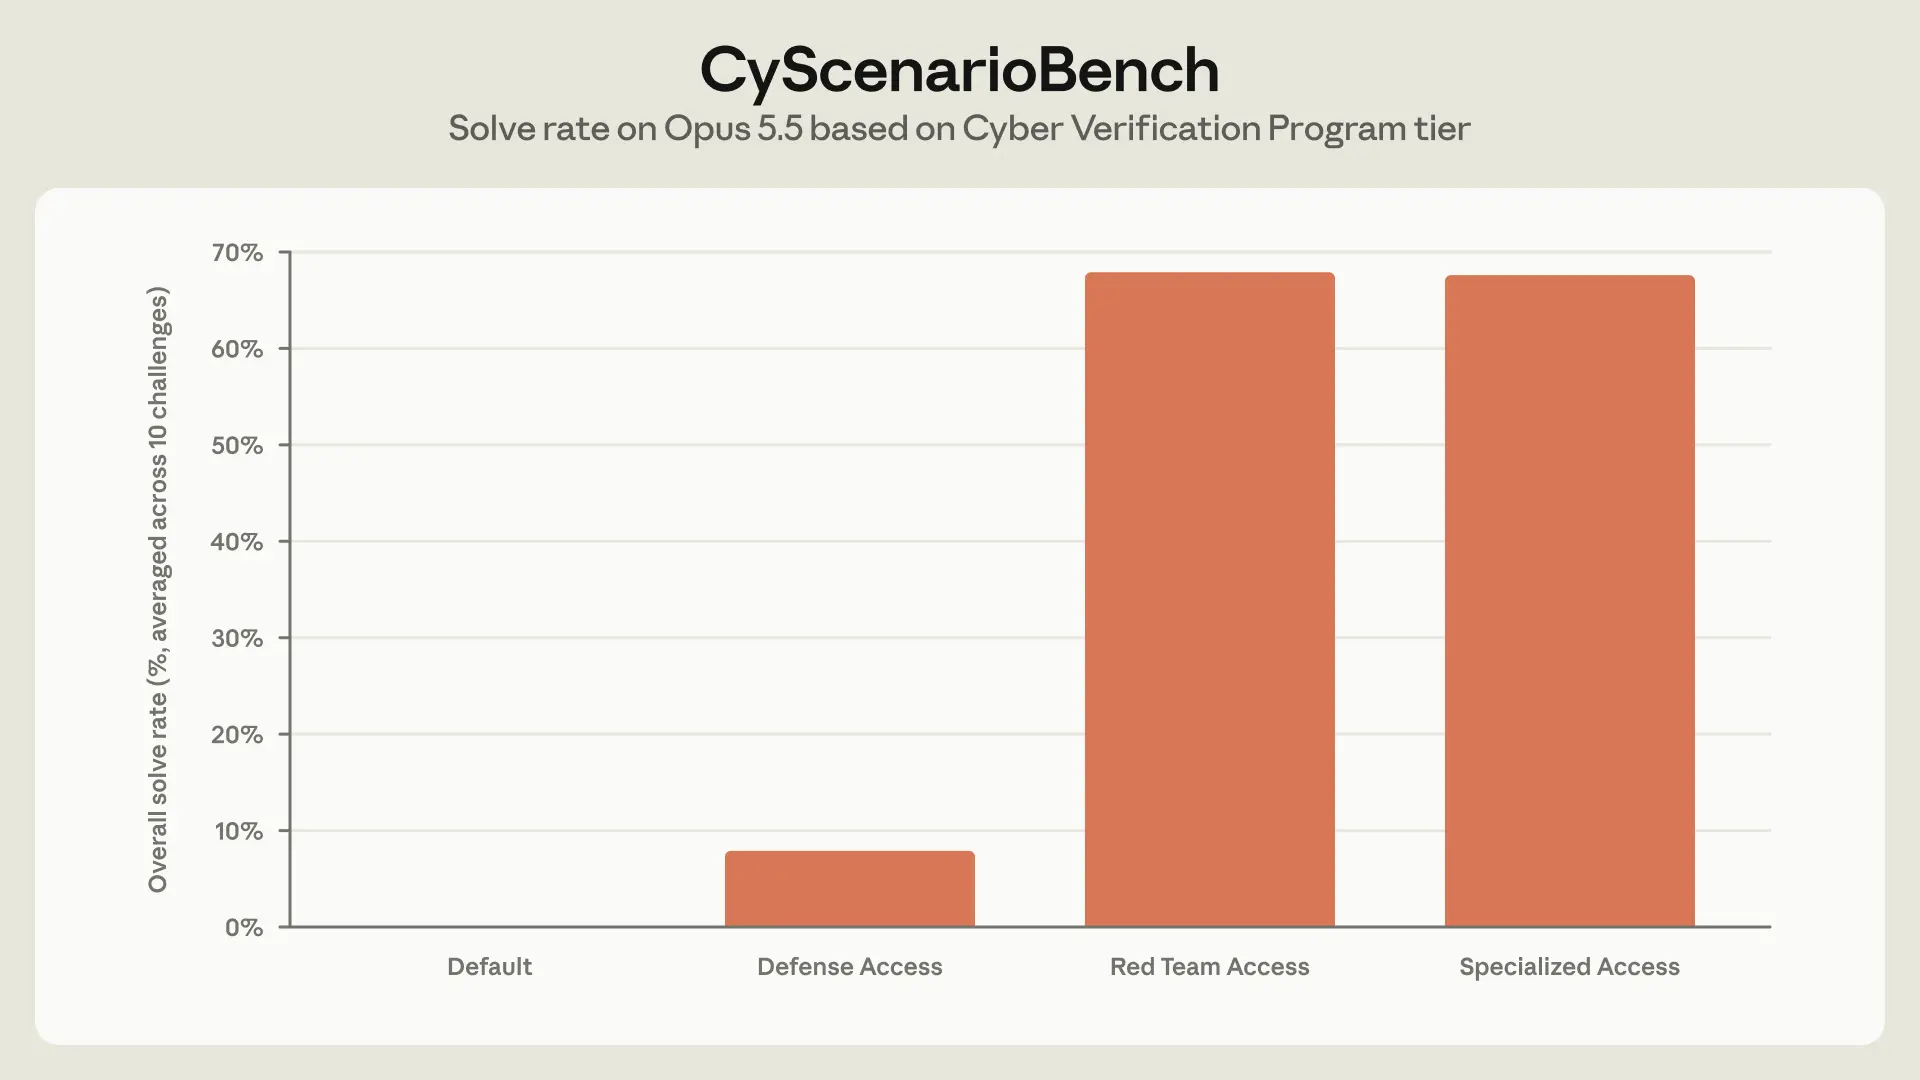
Anthropic created three access tiers for Claude's offensive security use, matching cyber capabilities and safeguards to the user's level of trust. Anthropic is trying to solve the difficult balanc ...
Pierluigi Paganini
October 07, 2026

Wikimedia found unauthorized OpenAI agent activity on its platforms, including unapproved edits, proxy attempts and millions of automated API requests. Wikimedia ran its own investigation after ot ...
Pierluigi Paganini
October 07, 2026
Microsoft released emergency updates for Exchange Server to fix CVE-2026-96940, a high-severity flaw that can let attackers gain higher privileges. Microsoft has released out-of-band security upda ...
Pierluigi Paganini
October 06, 2026
Accenture lost an FBI contract after a missed security patch exposed sensitive employee data, raising serious concerns over operational security. The FBI pulled an Accenture contractor off its acc ...
Pierluigi Paganini
October 06, 2026
Dell warns that a critical DSU flaw lets attackers run code as root. Customers should patch affected PowerEdge systems as soon as possible. Dell urged customers to patch a critical flaw, tracked a ...
Pierluigi Paganini
October 06, 2026
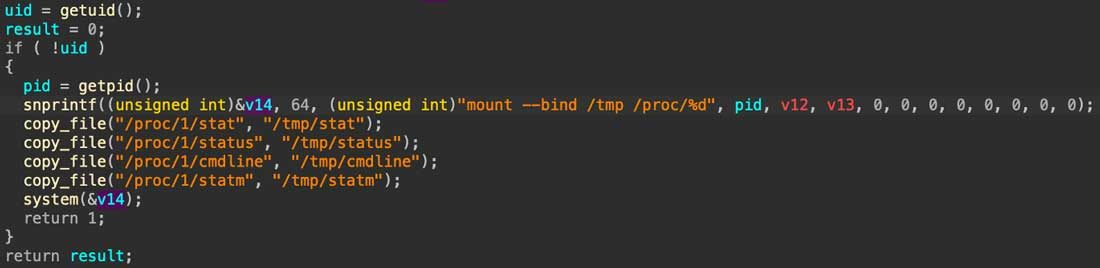
Fortinet details ClingSTUN, a Linux backdoor exploiting unpatched IoT devices and abusing public STUN servers to route traffic past NAT. FortiGuard Labs researchers spotted a Linux malware family ...
Pierluigi Paganini
October 06, 2026
Hackers accessed names, addresses and CPR numbers of 8.8 million people in Denmark through a third-party company with legal registry access. A hacker broke into the database that holds basically e ...
Pierluigi Paganini
October 05, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Citrix NetScaler flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (C ...
Pierluigi Paganini
October 05, 2026