Pierluigi Paganini
 March 29, 2020
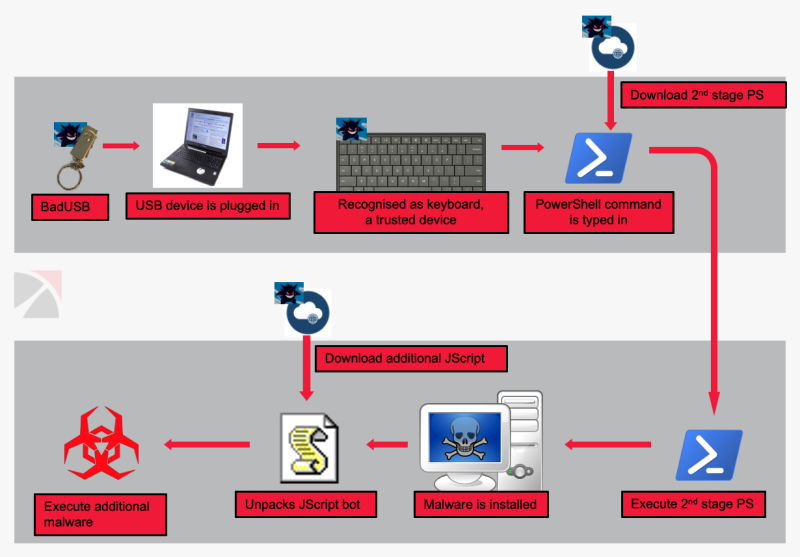
The FIN7 APT group has been targeting businesses with malicious USB drives and Teddy Bears sent to the victims, the FBI warns. The FBI is warning of a new wave of attacks carried out by the FIN7 A ...
Pierluigi Paganini
March 28, 2020
Experts discovered an easily exploitable heap-based buffer overflow flaw, tracked as CVE-2020-10245, that exists in the CODESYS web server. A critical heap-based buffer overflow flaw in a web serv ...
Pierluigi Paganini
March 28, 2020
Experts from Qihoo 360's NetLab recently spotted two zero-day campaigns targeting DrayTek enterprise-grade networking devices. Since December 2019, researchers from Qihoo 360 observed two differ ...
Pierluigi Paganini
March 28, 2020
AMD admitted that a hacker has stolen files related to some of its graphics products, but it downplayed the potential impact of the hack. AMD admitted that a hacker that goes online with the monik ...
 April 23, 2026
October 18, 2026
Attackers stole ConnectWise application credentials to access Microsoft 365 tenants, prompting the company to suspend cloud services. ConnectWise suspended its Cloud Backup service and took both S ...
Pierluigi Paganini
October 19, 2026
Attackers are exploiting vulnerability CVE-2026-106931 in SiteGuard Server Edition to run commands as root or SYSTEM. EG Secure Solutions published an urgent alert warning of CVE-2026-106931, an O ...
Pierluigi Paganini
October 19, 2026
A Broadcom Wi-Fi flaw dating back to 2010 allows attackers within Wi-Fi range to execute code on vulnerable routers without authentication. Researcher Quentin Kaiser presented a talk at Hexacon in ...
Pierluigi Paganini
October 19, 2026
Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, ...
Pierluigi Paganini
October 18, 2026
CikaBika Bot uses fake documents to infect Windows systems, then abuses Discord and Ngrok to execute commands, spy on victims, and steal files. Darktrace researchers have documented a new campaign ...
Pierluigi Paganini
October 18, 2026

Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter IronChain Ransomware Threatens Businesse ...
Pierluigi Paganini
October 18, 2026

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly Security ...
Pierluigi Paganini
October 18, 2026
The FBI raided 40 Texas homes over a North Korean scheme that used fake IT workers to target 70 US companies and generate $3 million. The Justice Department (DoJ) announced coordinated enforcement ...
Pierluigi Paganini
October 17, 2026

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Fortinet Multiple Products and BeyondTrust Remote Support flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecu ...
Pierluigi Paganini
October 17, 2026
A cyber incident at a BAE Systems subsidiary just stopped every bankruptcy court in the US from sending notices, and the problem started a week ago. A security incident at BAE Systems Inc., the US ...
Pierluigi Paganini
October 17, 2026
India's CERT-In warns AI agents accessed confidential data undetected, while attackers used offensive AI frameworks to accelerate cyberattacks. CERT-In, India's national cyber response team, publi ...
Pierluigi Paganini
October 17, 2026
Burger King Japan disclosed a breach exposing 11.18 million app users' personal data after attackers accessed its membership system in early October. Burger King Japan has disclosed a data breach ...
Pierluigi Paganini
October 16, 2026
F5 addressed multiple vulnerabilities, including critical RCE flaws in NGINX that attackers could exploit without authentication. Security and application delivery firm F5 announced fixes for elev ...
Pierluigi Paganini
October 16, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Atlassian flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) a ...
Pierluigi Paganini
October 16, 2026
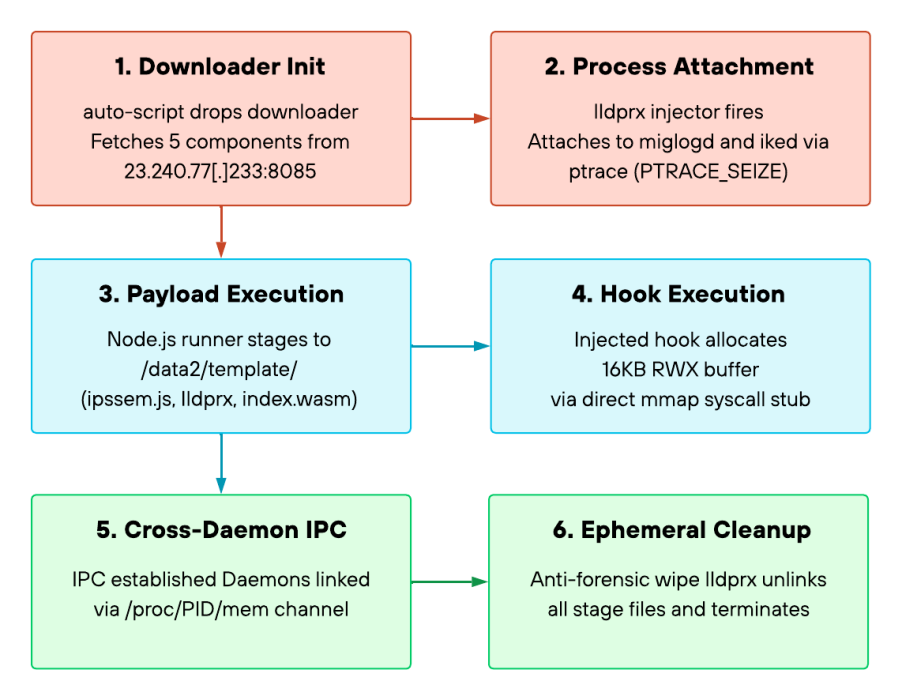
PEERSTITCH malware exploited FortiManager to expose 500+ firewalls, evade detection inside FortiOS memory, and maintain stealthy access. PEERSTITCH, a stealthy implant deployed during a prolonged ...
Pierluigi Paganini
October 16, 2026
The regulated utility company CenterPoint Energy says a data breach exposed the personal information of more than 1 million people in Texas. CenterPoint Energy is a regulated utility company used ...
Pierluigi Paganini
October 16, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Palo Alto Networks PAN-OS, Ahsay AhsayCBS, and Cisco Secure Email Gateway flaws to its Known Exploited Vulnerabilities catalog. Th ...
Pierluigi Paganini
October 15, 2026
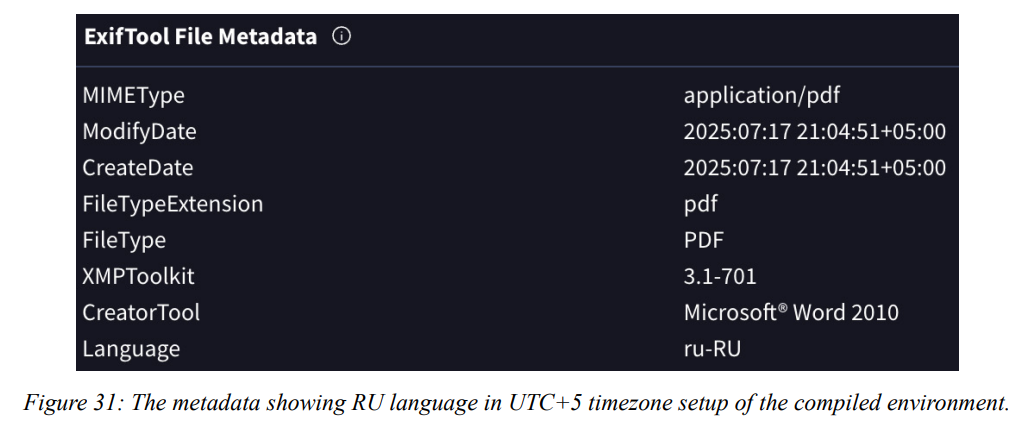
Silent Lynx, a group likely based in Kazakhstan, targets Russian energy and government entities in espionage campaigns across Central Asia. Researchers from Cisco Talos and Recorded Future publish ...
Pierluigi Paganini
October 15, 2026
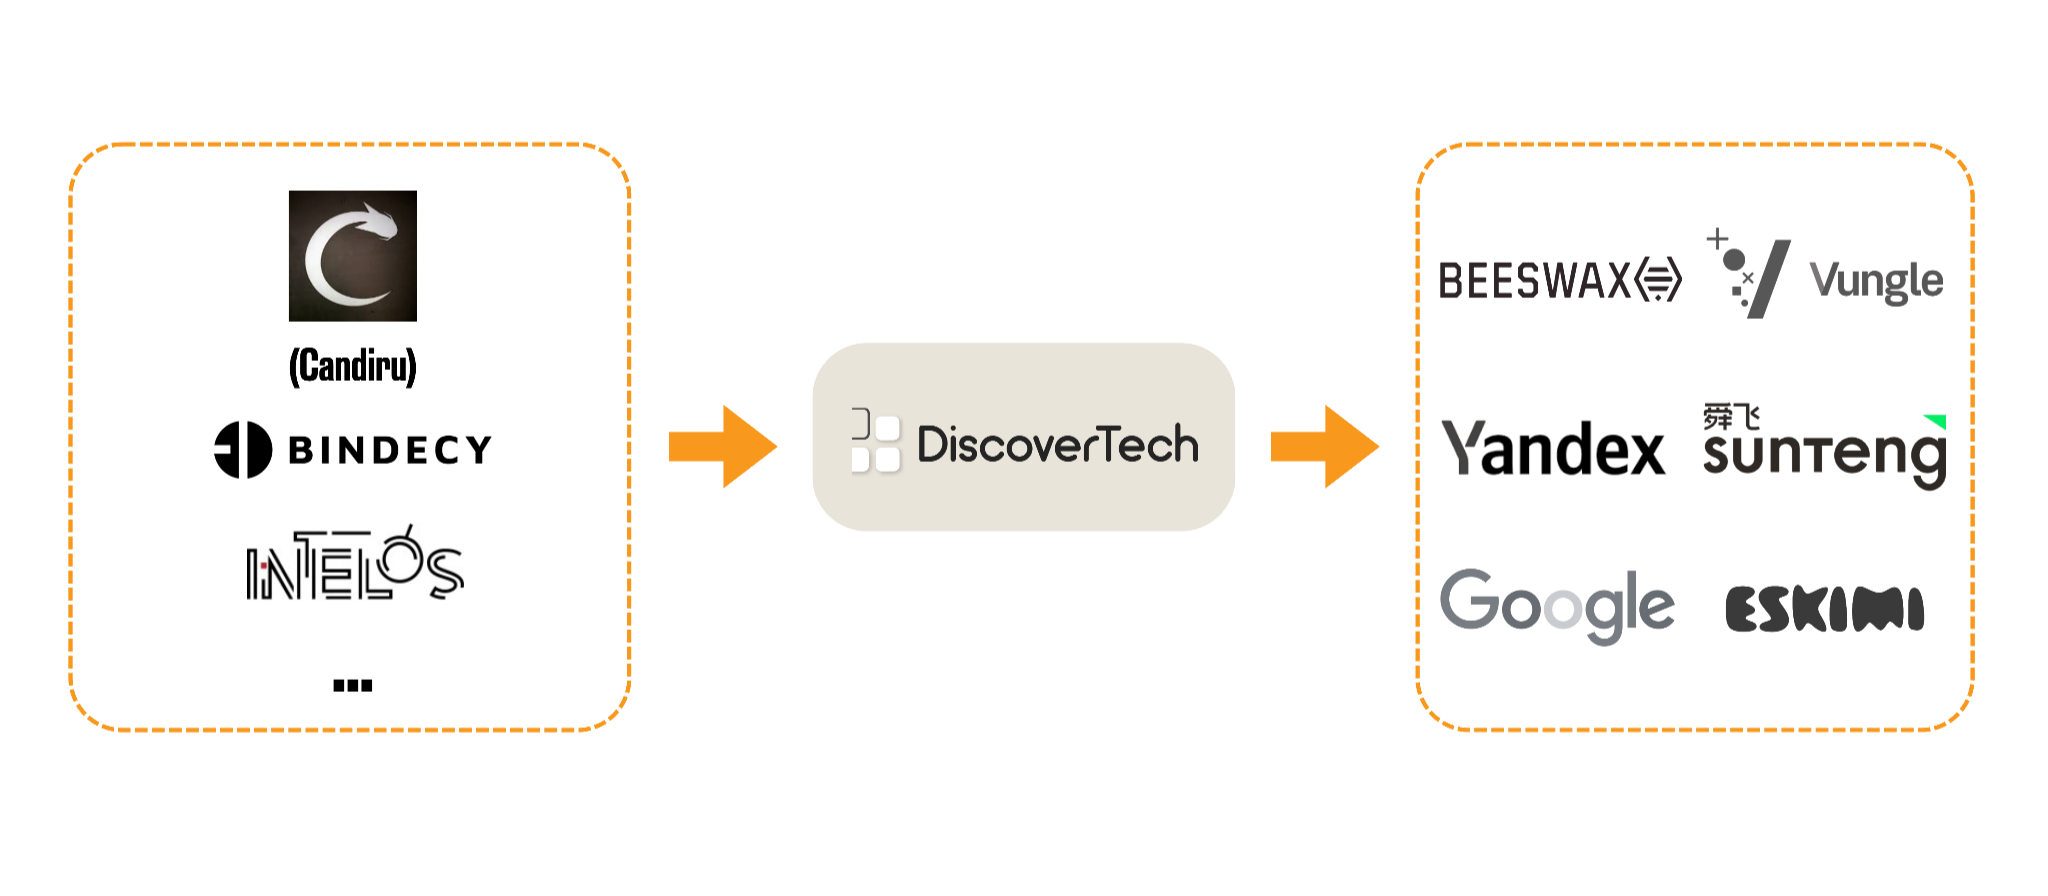
Spyware vendors use online ad infrastructure to profile targets and deliver exploits without requiring users to click anything. The investigation links Discover-Tech to Candiru, an Israeli spyware ...
Pierluigi Paganini
October 15, 2026
Attackers exploit a critical Cisco email gateway flaw to gain root access. Cisco urges customers to update scanner tools and check for compromise. Cisco confirmed this week that threat actors are ...
Pierluigi Paganini
October 15, 2026