19294 results
 Pierluigi Paganini
 December 29, 2024
A White House official confirmed that China-linked threat actor Salt Typhoon breached a ninth U.S. telecommunications company. A White House official confirmed that China-linked APT group Salt Typhoon has breached a ninth U.S. telecoms company as part of a cyberespionage campaign aimed at telco firms worldwide. “A White House official said Friday the US identified […]
 Pierluigi Paganini
December 29, 2024
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape. Now You See Me, Now You Don’t: Using LLMs to Obfuscate Malicious JavaScript Analyzing Malicious Intent in Python Code: A Case Study DigiEver Fix That IoT Thing! Botnets Continue to Target Aging D-Link Vulnerabilities OtterCookie, […]
 Pierluigi Paganini
December 28, 2024
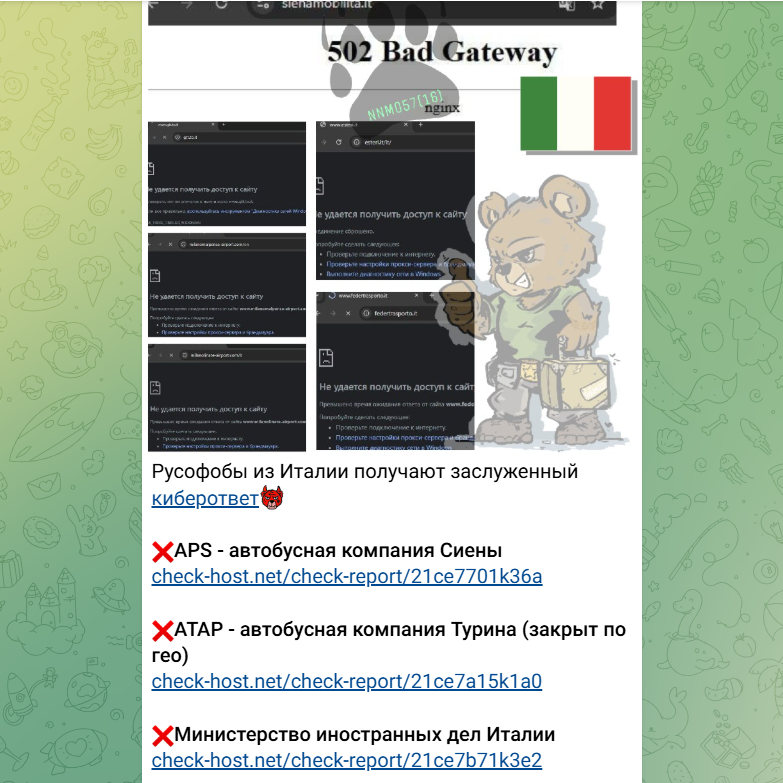
Pro-Russia group NoName057 targets Italian sites, including Malpensa and Linate airports, in a new DDoS campaign amid rising geopolitical tensions. The pro-Russia group NoName57 continues its campaign of DDoS attacks against Italian infrastructure. This time, the group of alleged hacktivists targeted multiple websites, include the sites of Malpensa and Linate airports, as well as the […]
 Pierluigi Paganini
December 28, 2024
North Korea-linked threat actors are using the OtterCookie backdoor to target software developers with fake job offers. North Korea-linked threat actors were spotted using new malware called OtterCookie as part of the Contagious Interview campaign that targets software developer community with fake job offers. The Contagious Interview campaign was first detailed by Palo Alto Networks […]
 Pierluigi Paganini
December 27, 2024
FortiGuard Labs observed increased activity from two botnets, the Mirai variant “FICORA” and the Kaiten variant “CAPSAICIN”. FortiGuard Labs researchers observed a surge in activity associated with two botnets, the Mirai variant “FICORA” and the Kaiten variant “CAPSAICIN,” in late 2024. Both botnets target vulnerabilities in D-Link devices, particularly through the HNAP interface, allowing remote […]
 Pierluigi Paganini
December 27, 2024
Palo Alto Networks addressed a high-severity PAN-OS flaw that could trigger denial-of-service (DoS) on vulnerable devices. Palo Alto Networks addressed a high-severity flaw, tracked as CVE-2024-3393 (CVSS score: 8.7), in PAN-OS software that could cause a denial-of-service (DoS) condition. An unauthenticated attacker can exploit this vulnerability to reboot the firewall by sending a malicious packet […]
 Pierluigi Paganini
December 27, 2024
A Brazilian citizen faces U.S. charges for allegedly threatening to release data stolen from a company in a March 2020 security breach. The U.S. government has charged the Brazilian citizen Junior Barros De Oliveira, 29, with allegedly threatening to release data stolen from a company during a March 2020 security breach. De Oliveira was charged […]
 Pierluigi Paganini
December 26, 2024
Akamai researchers discovered a new Mirai botnet variant targeting a vulnerability in DigiEver DS-2105 Pro DVRs. Akamai researchers spotted a Mirai-based botnet that is exploiting an remote code execution vulnerability in DigiEver DS-2105 Pro NVRs. The experts pointed out that this Mirai variant has been modified to use improved encryption algorithms. The Mirai variant incorporates ChaCha20 and […]
 Pierluigi Paganini
December 26, 2024
A ransomware attack on Pittsburgh Regional Transit (PRT) was the root cause of the agency’s service disruptions. On December 23, 2024, Pittsburgh Regional Transit (PRT) announced it was actively responding to a ransomware attack that was first detected on Thursday, December 19. Pittsburgh Regional Transit (PRT) is the public transportation agency that serves the Pittsburgh […]
 Pierluigi Paganini
December 26, 2024
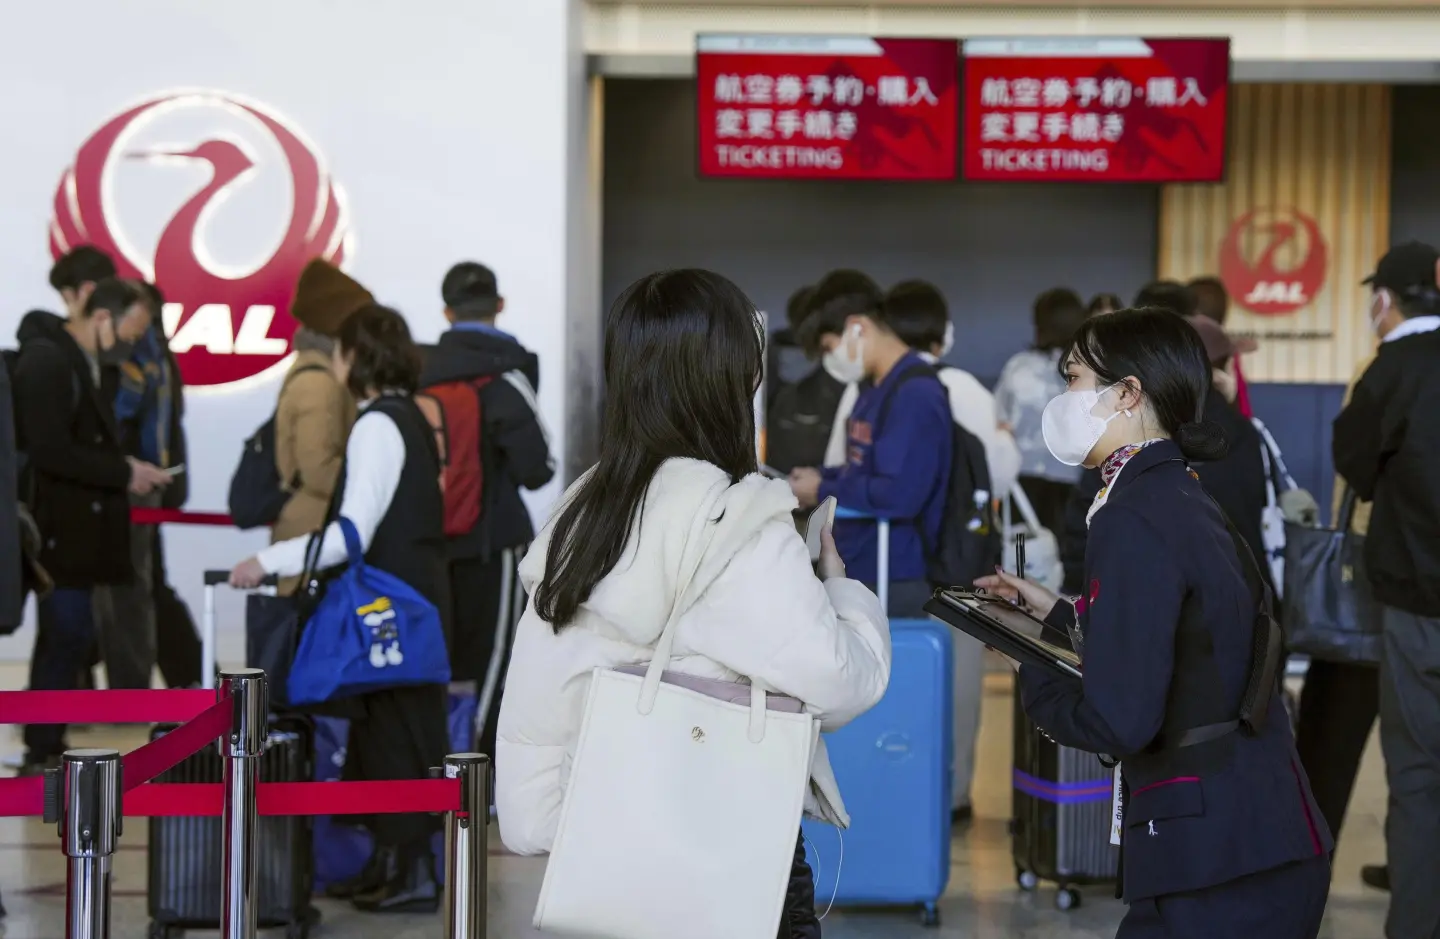
A cyberattack hit Japan Airlines (JAL), causing the suspension of ticket sales for flights departing on Thursday. A cyber attack hit Japan Airlines (JAL) on Thursday, the offensive began at 7:24 a.m. and impacted internal and external systems. The Associated Press reported that the attack disabled a router, causing system malfunctions and suspending ticket sales […]