19290 results

 Pierluigi Paganini
 June 10, 2024
Frontier Communications is notifying over 750,000 individuals that their personal information was stolen in a recent cyber attack. Last week, the RansomHub ransomware group claimed to have stolen the information of over 2 million customers from the American telecommunications company Frontier Communications. The RansomHub group claimed to have stolen 5GB of data from the telecommunications […]
 Pierluigi Paganini
June 09, 2024
A new PHP for Windows remote code execution (RCE) flaw affects version 5.x and earlier versions, potentially impacting millions of servers worldwide. Researchers at cybersecurity firm DEVCORE discovered a critical remote code execution (RCE) vulnerability, tracked as CVE-2024-4577, in the PHP programming language. An unauthenticated attacker can exploit the flaw to take full control of affected servers. PHP is […]
 Pierluigi Paganini
June 07, 2024
Chinese shopping platform Pandabuy previously paid a ransom demand to an extortion group that extorted the company again this week. The story of the attack against the Chinese shopping platform Pandabuy demonstrates that paying a ransom to an extortion group is risky to the victims. BleepingComputer first reported that Pandabuy had previously paid a ransom […]
 Pierluigi Paganini
June 07, 2024
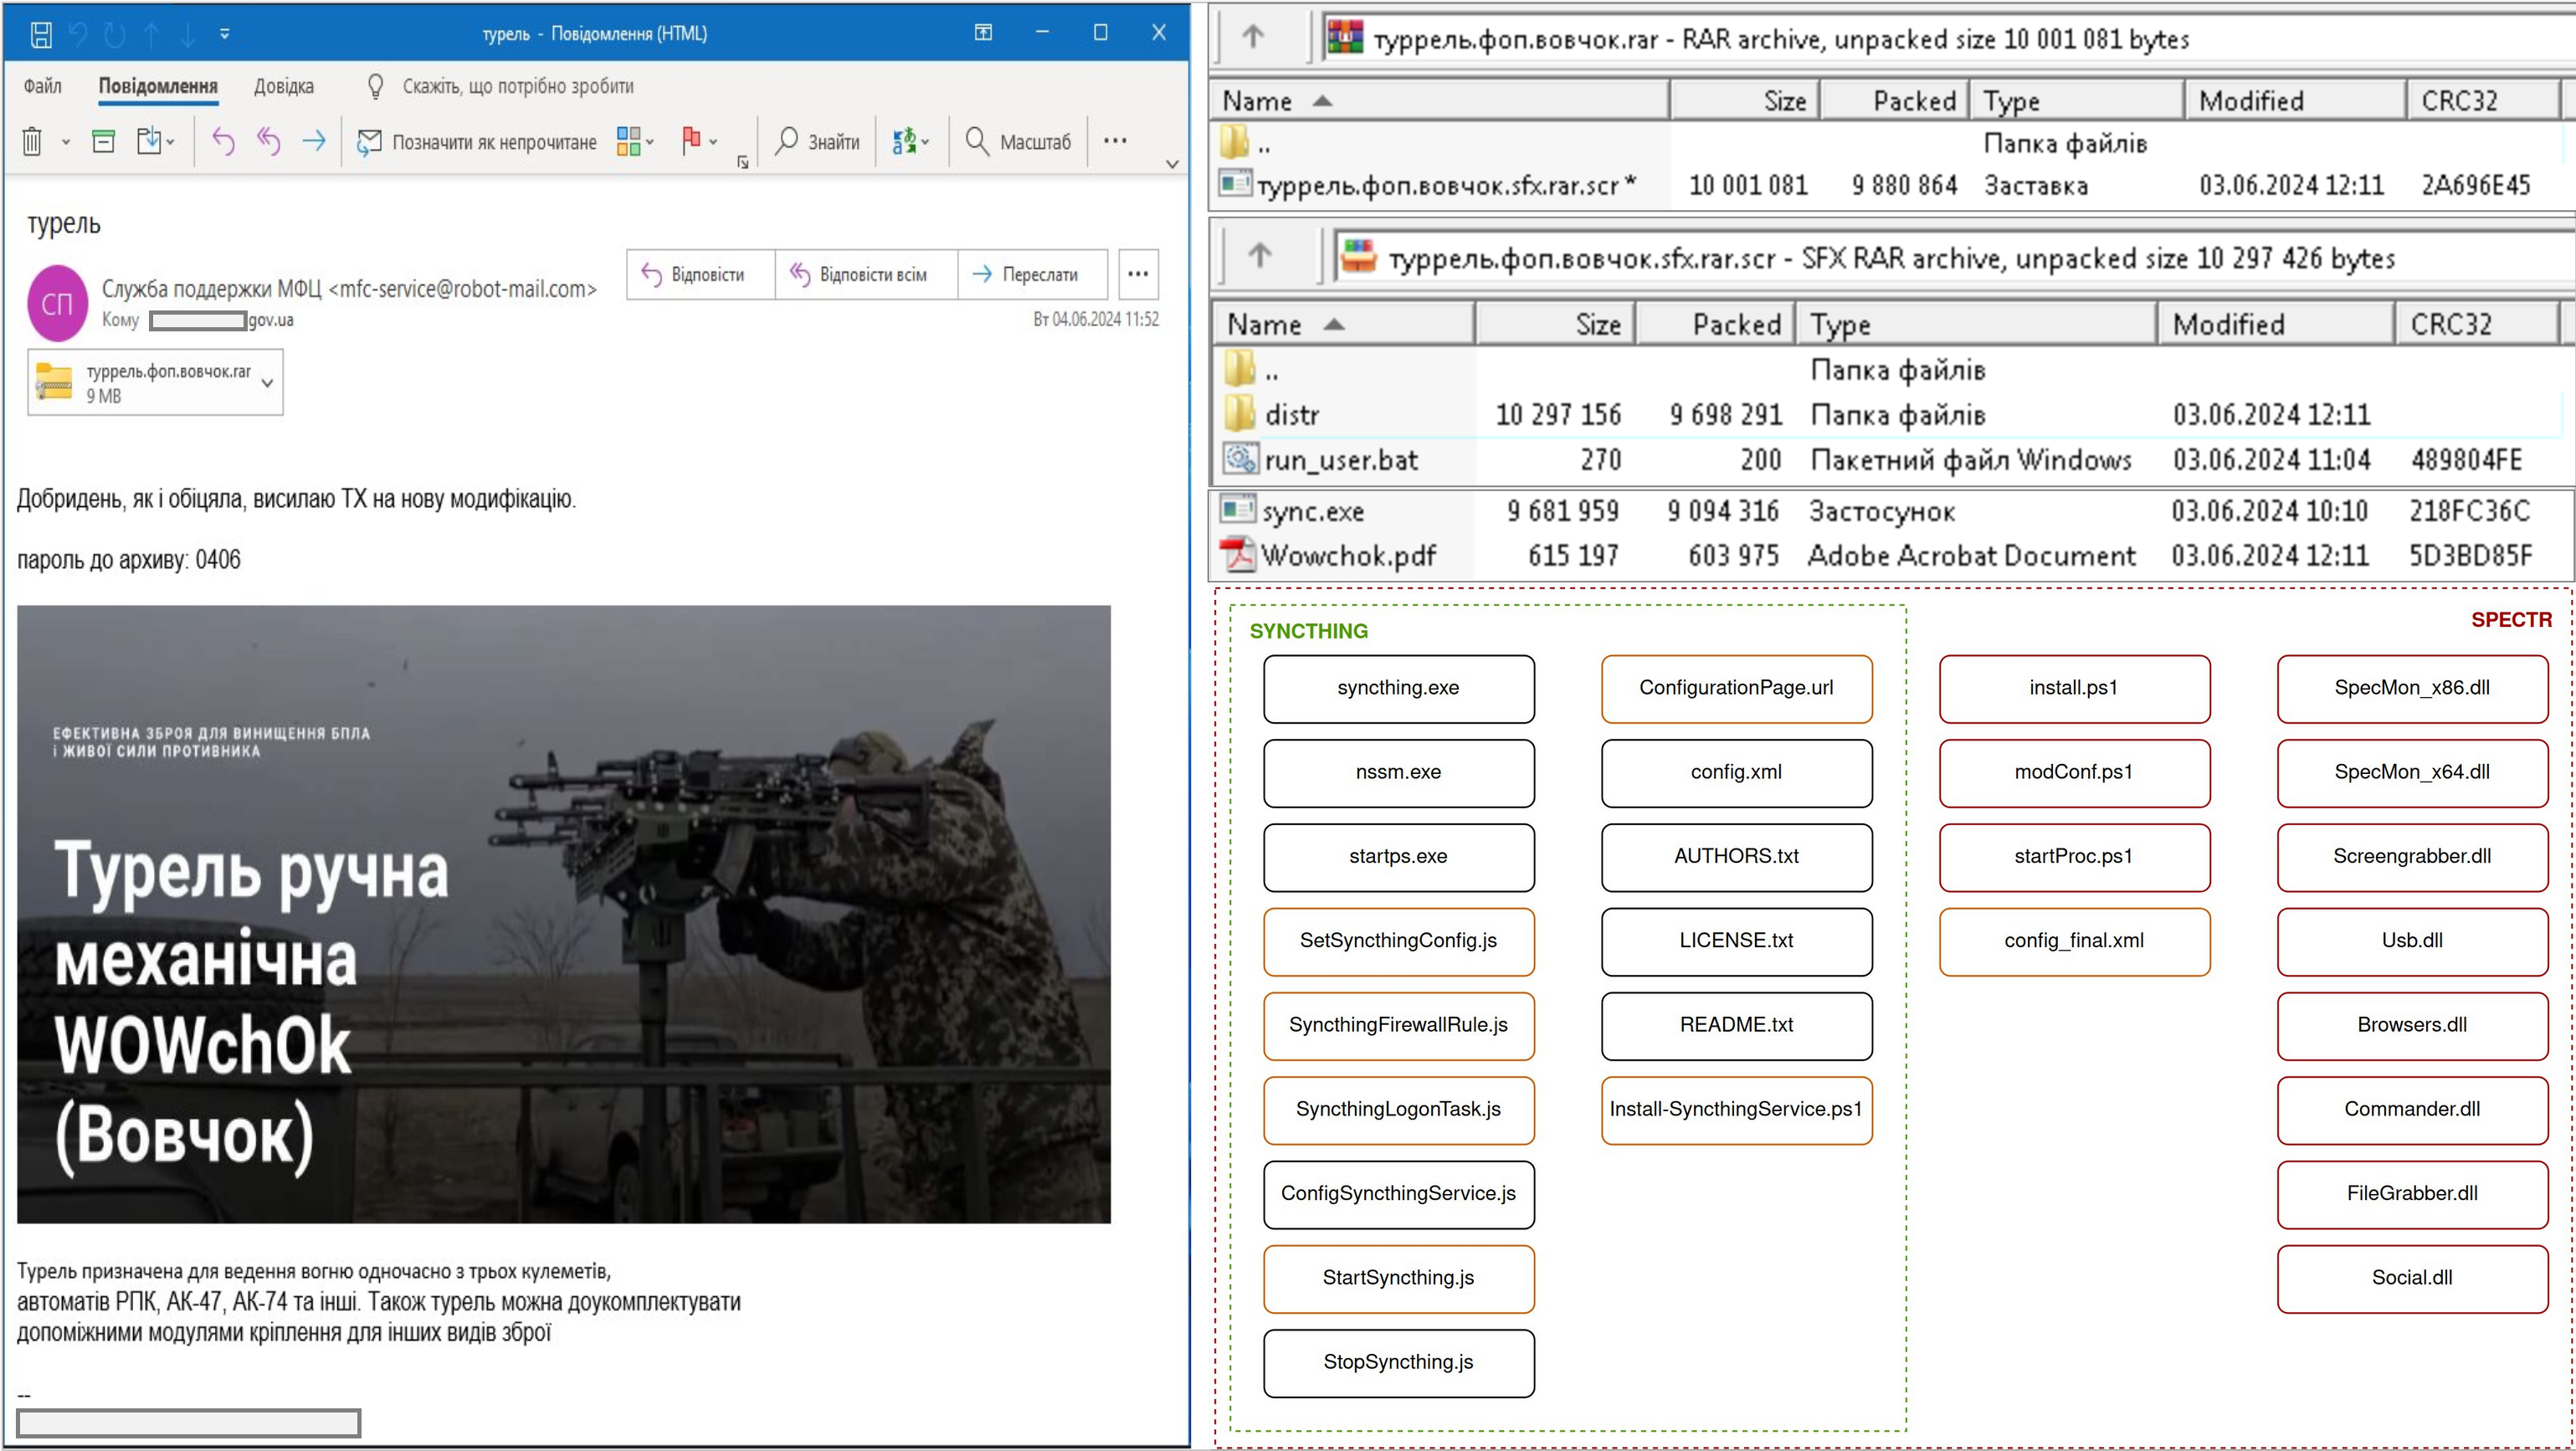
Ukraine CERT-UA warned of cyber attacks targeting defense forces with SPECTR malware as part of a cyber espionage campaign dubbed SickSync. The Computer Emergency Response Team of Ukraine (CERT-UA) warned of cyber espionage campaign targeting defense forces in the country. The Ukrainian CERT attributes the attack to the threat actor UAC-0020 which employed a malware […]
 Pierluigi Paganini
June 07, 2024
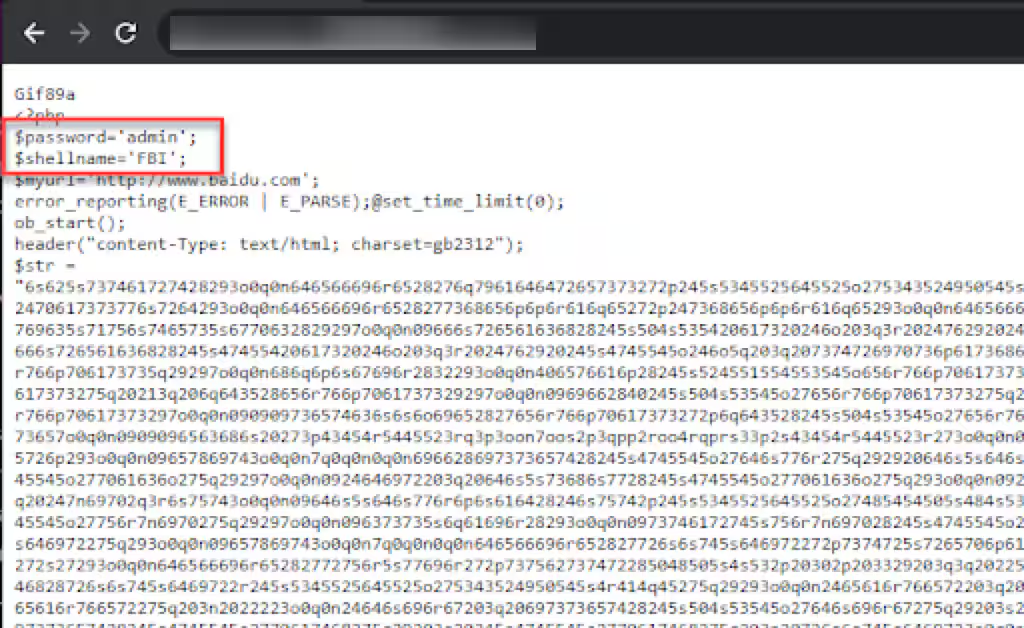
Akamai observed a Chinese-speaking group exploiting two flaws, tracked as CVE-2018-20062 and CVE-2019-9082, in ThinkPHP applications. Akamai researchers observed a Chinese threat actor exploiting two old remote code execution vulnerabilities, tracked as CVE-2018-20062 and CVE-2019-9082, in ThinkPHP. The campaign seems to have been active since at least October 2023, it initially targeted a limited number of customers/organizations […]
 Pierluigi Paganini
June 06, 2024
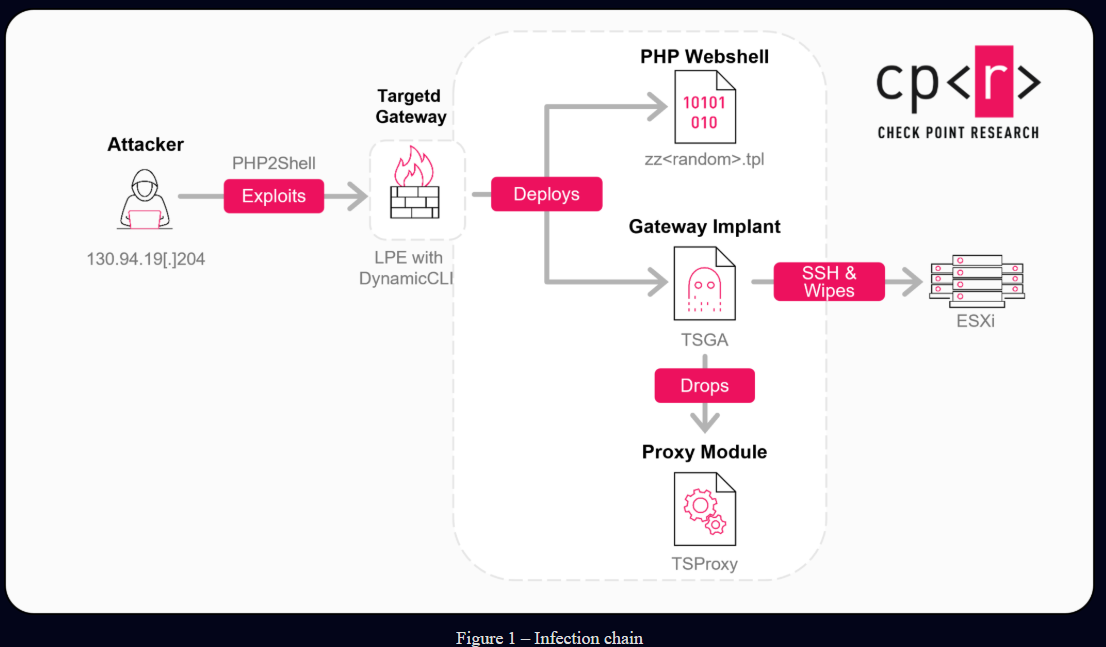
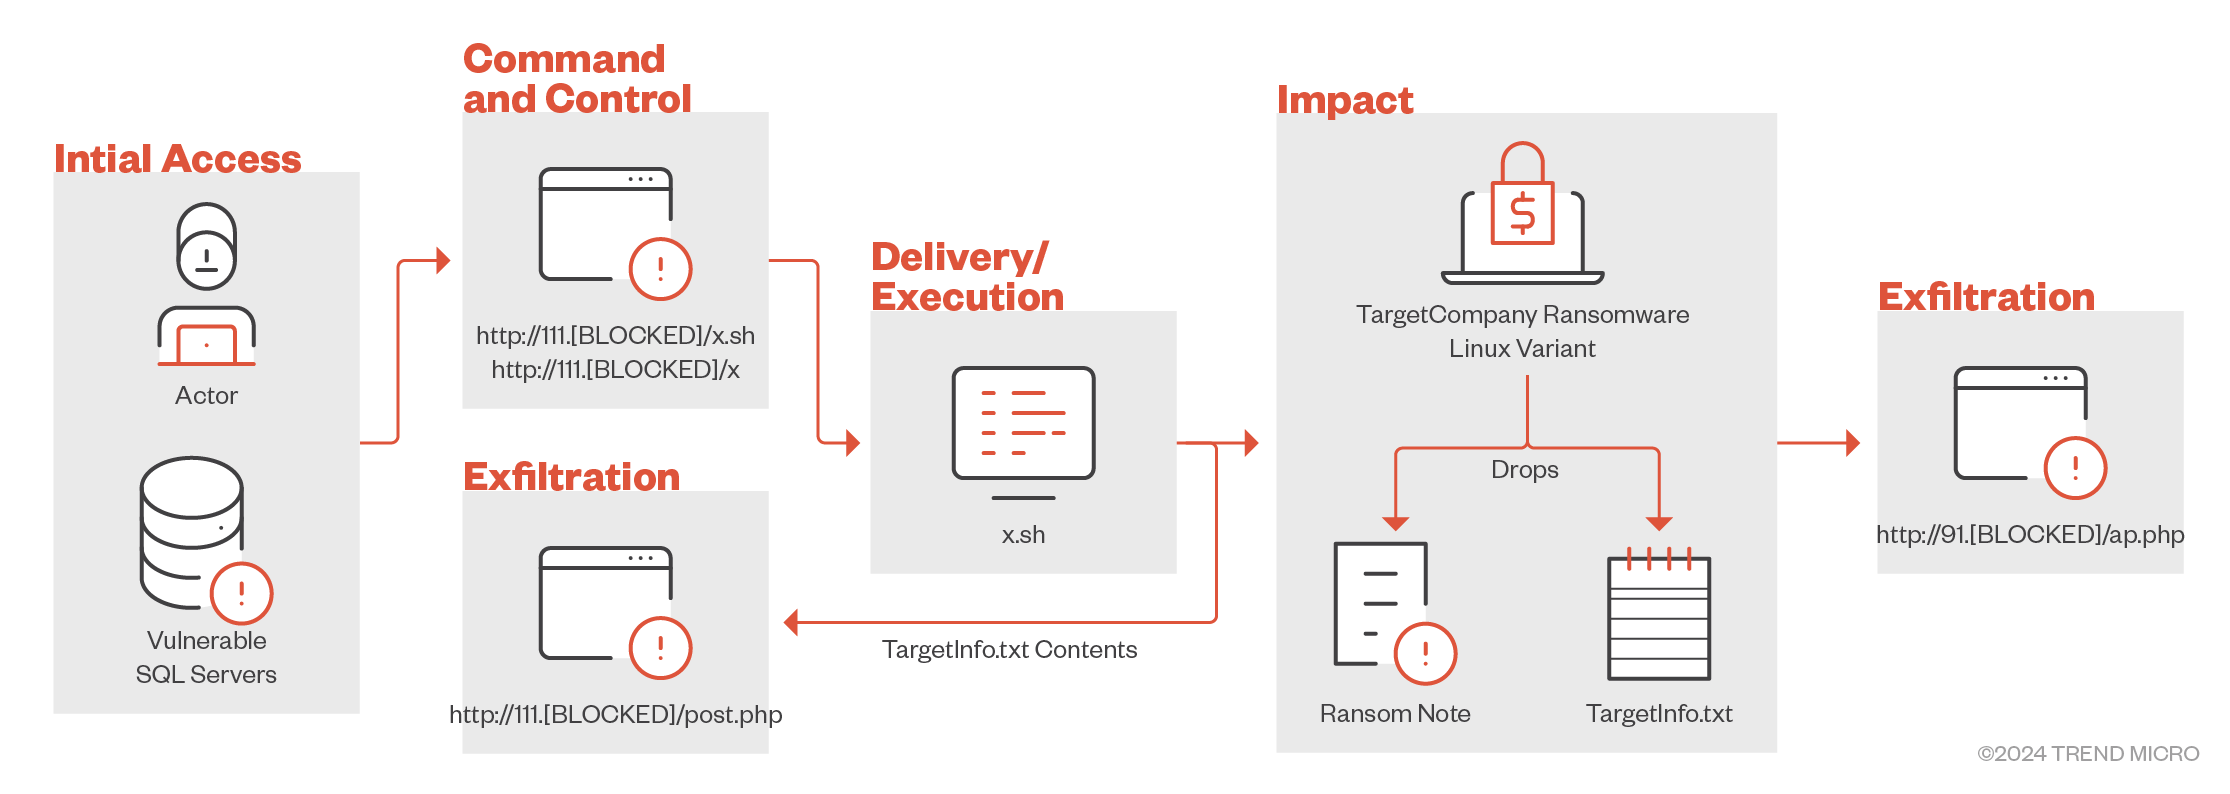
A new Linux variant of the TargetCompany ransomware family targets VMware ESXi environments using a custom shell script. A new variant of the TargetCompany ransomware group uses a custom shell script as a means of payload delivery and execution, this is the first time the technique was observed in the wild. The script was also used […]
 Pierluigi Paganini
June 06, 2024
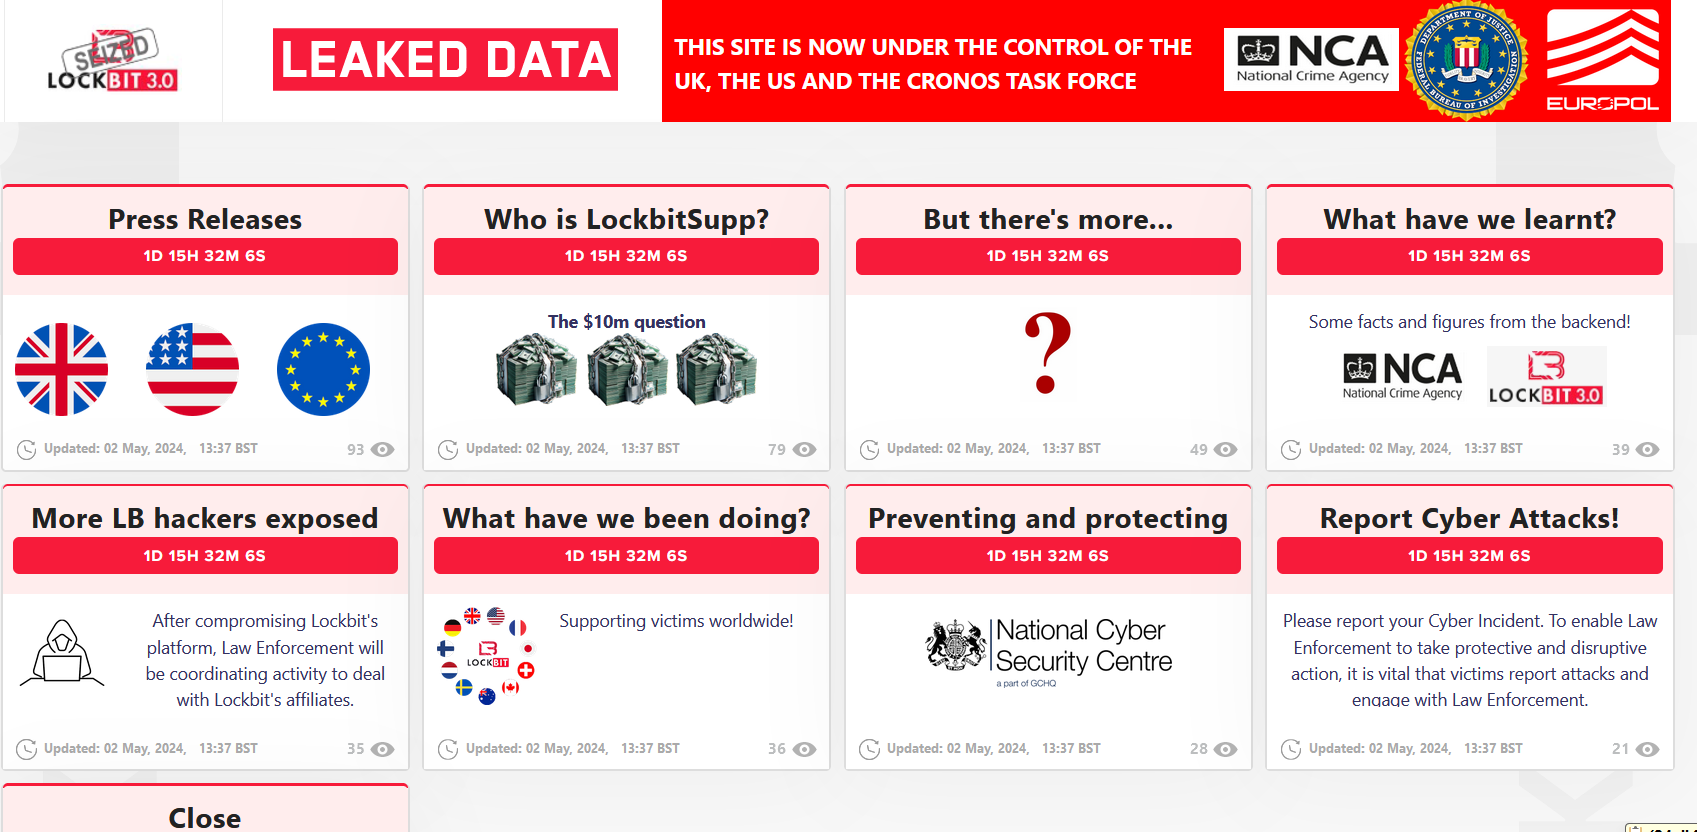
The FBI is informing victims of LockBit ransomware it has obtained over 7,000 LockBit decryption keys that could allow some of them to decrypt their data. The FBI is inviting victims of LockBit ransomware to come forward because it has obtained over 7,000 LockBit decryption keys that could allow them to recover their encrypted data […]
 Pierluigi Paganini
June 06, 2024
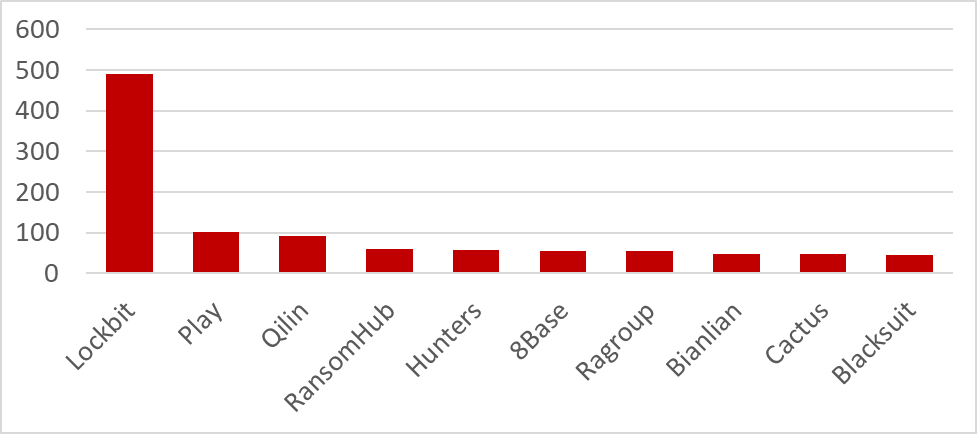
Researchers believe the RansomHub ransomware-as-a-service is a rebranded version of the Knight ransomware operation. Cybersecurity experts who analyzed the recently emerged ransomware operation RansomHub speculate that is is a rebranded version of Knight ransomware. Knight, also known as Cyclops 2.0, appeared in the threat landscape in May 2023. The malware targets multiple platforms, including Windows, […]
 Pierluigi Paganini
June 05, 2024
Cybersecurity researchers demonstrated how malware could potentially steal data collected by the new Windows Recall tool. The Recall feature of Microsoft Copilot+ is an AI-powered tool designed to help users search for past activities on their PC. The data collected by the tool is stored and processed locally. After its presentation, it raised security and […]
 Pierluigi Paganini
June 05, 2024
Cisco addressed vulnerabilities that were exploited to compromise the Webex meetings of the German government. In early May, German media outlet Zeit Online revealed that threat actors exploited vulnerabilities in the German government’s implementation of the Cisco Webex software to access internal meetings. In March, the German authorities admitted the hack by Russia-linked actors of […]