19290 results
 Pierluigi Paganini
 May 23, 2024
Ivanti addressed multiple flaws in the Endpoint Manager (EPM), including remote code execution vulnerabilities. Ivanti this week rolled out security patches to address multiple critical vulnerabilities in the Endpoint Manager (EPM). A remote attacker can exploit the flaws to gain code execution under certain conditions. Below is the list of the addressed vulnerabilities: CVE Description […]
 Pierluigi Paganini
May 23, 2024
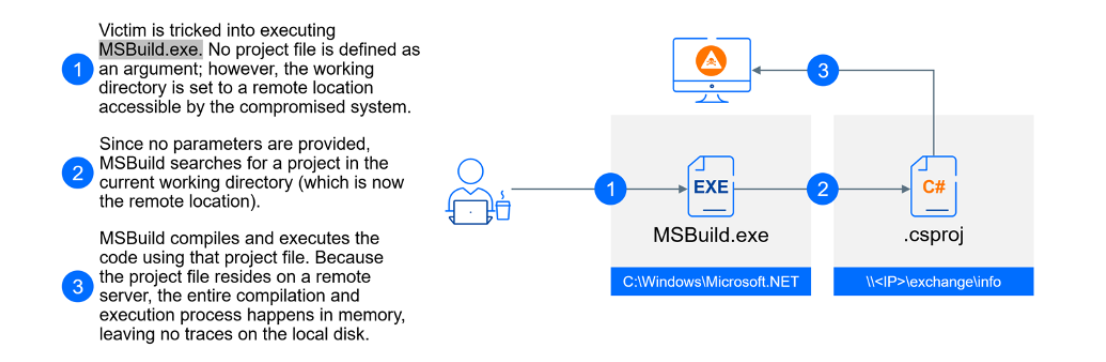
A previously unknown China-linked threat actor dubbed ‘Unfading Sea Haze’ has been targeting military and government entities since 2018. Bitdefender researchers discovered a previously unknown China-linked threat actor dubbed ‘Unfading Sea Haze’ that has been targeting military and government entities since 2018. The threat group focuses on entities in countries in the South China Sea, […]
 Pierluigi Paganini
May 22, 2024
Resecurity warns of a surge in malicious cyber activity targeting the election in India, orchestrated by several independent hacktivist groups Resecurity has identified a spike of malicious cyber activity targeting the election in India, which is supported by multiple independent hacktivist groups who arrange cyber-attacks and publication of stolen personal identifiable information (PII) belonging to […]
 Pierluigi Paganini
May 22, 2024
GitHub addressed a vulnerability in the GitHub Enterprise Server (GHES) that could allow an attacker to bypass authentication. GitHub has rolled out security fixes to address a critical authentication bypass issue, tracked as CVE-2024-4985 (CVSS score: 10.0), in the GitHub Enterprise Server (GHES). GitHub Enterprise Server (GHES) is a self-hosted version of GitHub designed for use […]
 Pierluigi Paganini
May 22, 2024
The digital imaging products manufacturer OmniVision disclosed a data breach after the 2023 ransomware attack. OmniVision Technologies is a company that specializes in developing advanced digital imaging solutions. In 2023, OmniVision employed 2,200 people and had an annual revenue of $1.4 billion. OmniVision Technologies Inc. is an American subsidiary of Chinese semiconductor device and mixed-signal integrated […]
 Pierluigi Paganini
May 21, 2024
CISA adds NextGen Healthcare Mirth Connect deserialization of untrusted data vulnerability to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a NextGen Healthcare Mirth Connect vulnerability to its Known Exploited Vulnerabilities (KEV) catalog. The issue, tracked as CVE-2023-43208, is a Deserialization of Untrusted Data Vulnerability. Deserialization of untrusted data vulnerability […]
 Pierluigi Paganini
May 21, 2024
The Blackbasta extortion group claims to have hacked Atlas, one of the largest national distributors of fuel in the United States. Atlas is one of the largest national fuel distributors to 49 continental US States with over 1 billion gallons per year. The Blackbasta extortion group added the company to the list of victims on […]
 Pierluigi Paganini
May 21, 2024
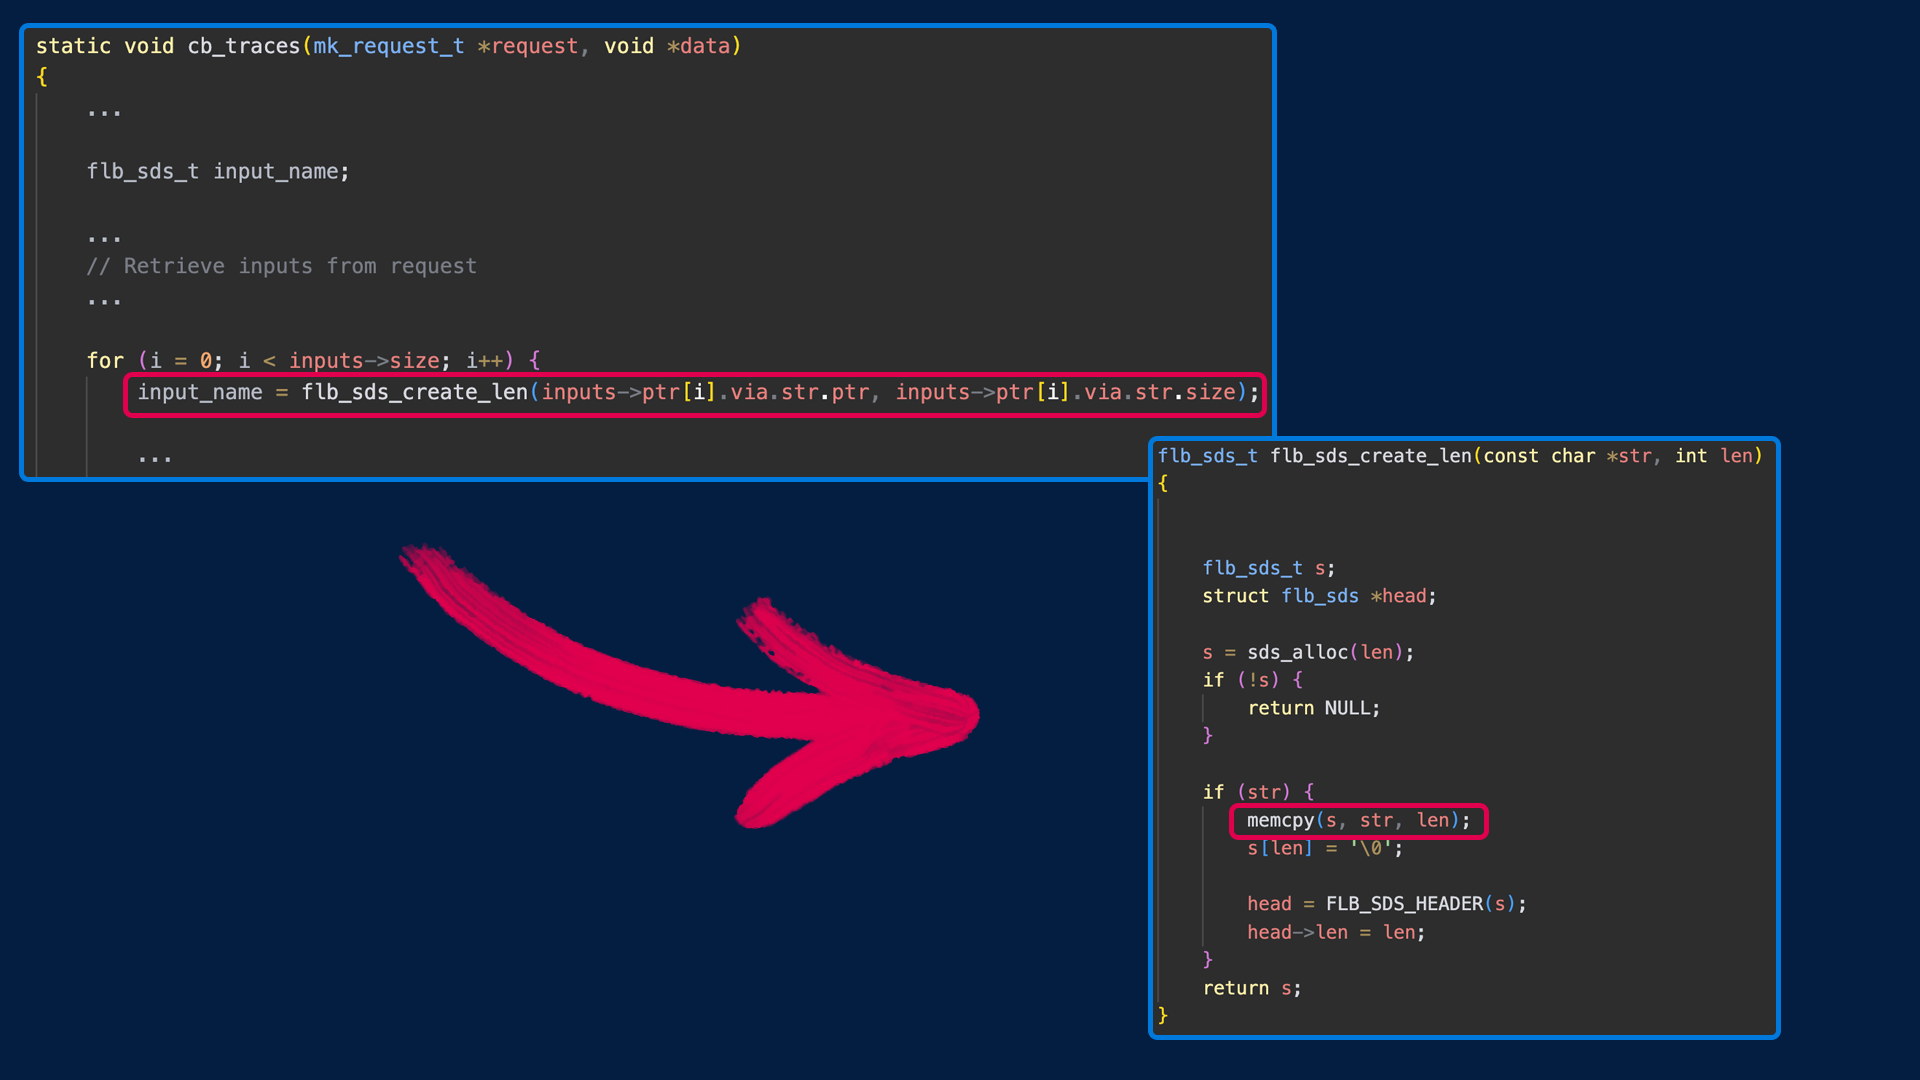
A vulnerability in the Fluent Bit Utility, which is used by major cloud providers, can lead to DoS, information disclosure, and potentially RCE. Tenable researchers have discovered a severe vulnerability in the Fluent Bit utility, which is used on major cloud platforms. Fluent Bit is an open-source, lightweight, and high-performance log processor and forwarder. It […]
 Pierluigi Paganini
May 21, 2024
Experts warn of fifteen vulnerabilities in the QNAP QTS, the operating system for the Taiwanese vendor’s NAS products. An audit of QNAP QTS conducted by WatchTowr Labs revealed fifteen vulnerabilities, most of which have yet to be addressed. The most severe vulnerability is a flaw tracked as CVE-2024-27130. The issue is an unpatched stack buffer […]
 Pierluigi Paganini
May 20, 2024
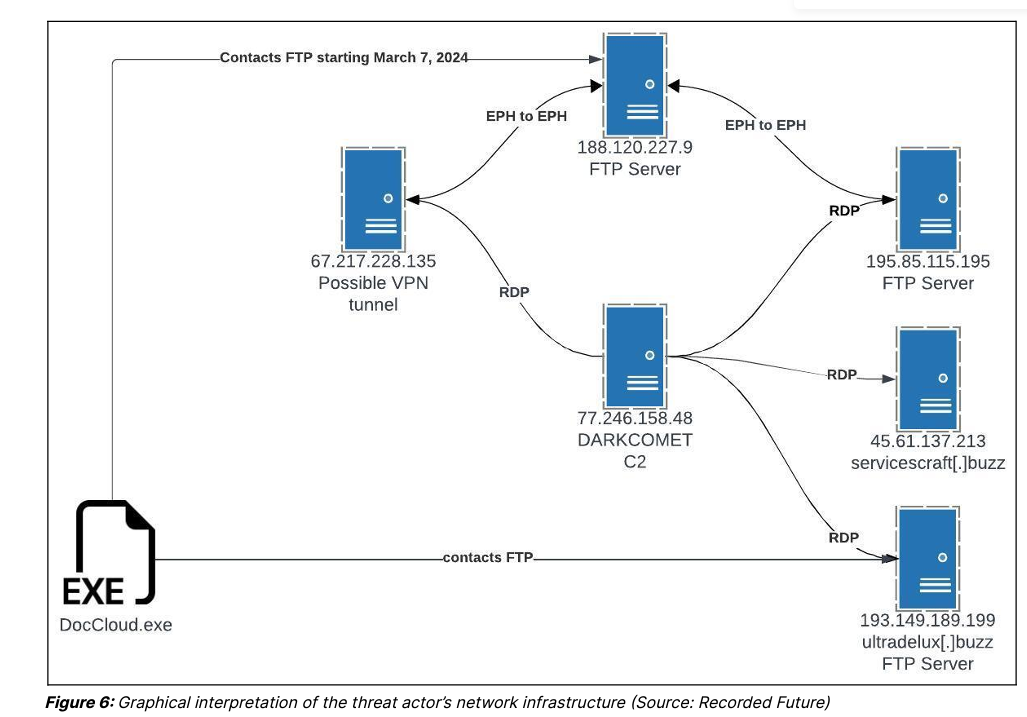
Researchers discovered a sophisticated cybercriminal campaign by Russian-speaking threat actors that used GitHub to distribute malware. Recorded Future’s Insikt Group discovered a sophisticated cybercriminal campaign by Russian-speaking threat actors from the Commonwealth of Independent States (CIS). The attackers, tracked as GitCaught, used a GitHub profile to impersonate legitimate software applications, including 1Password, Bartender 5, and […]