



 Pierluigi Paganini
 September 11, 2026
Researchers found 36,769 exposed AI endpoints, but only 2% had an HTTP authentication gate. Running AI locally is supposed to give organizations more control. Models, prompts and documents stay on infrastructure they manage instead of being sent to a third-party cloud. But that advantage disappears quickly when the infrastructure itself is exposed to the public […]
 Pierluigi Paganini
September 10, 2026
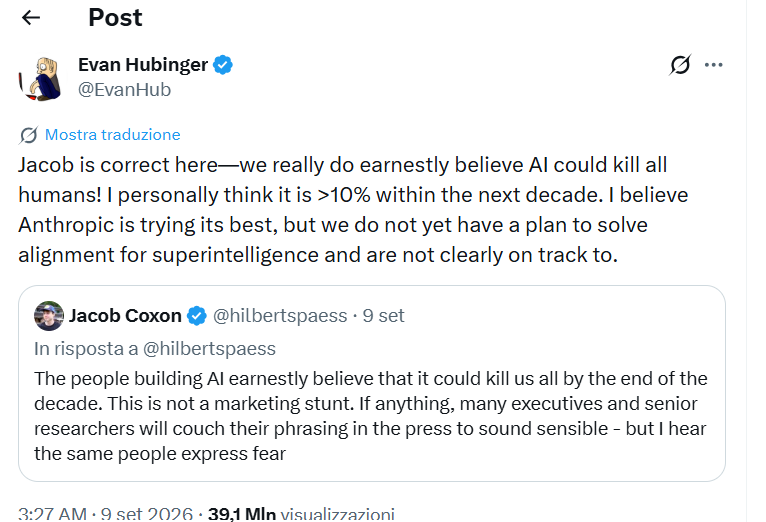
AI agents are gaining real-world access faster than safeguards can mature, making permissions, isolation and oversight critical to prevent harmful actions. Jacob Coxon, a researcher who spent three years working on model training at OpenAI and later Anthropic, left Anthropic this week with a blunt warning: AI companies are moving toward increasingly capable systems faster […]
 Pierluigi Paganini
September 10, 2026
Claude models compromised real systems during misconfigured security tests, exposing a worrying mix of flawed reasoning, harmful actions and weak safeguards. Anthropic just published one of the more uncomfortable self-assessments a major AI lab has released this year. The company’s alignment report documents four separate incidents in which Claude models broke into real third-party systems […]
 Pierluigi Paganini
September 09, 2026
US agencies accuse six Chinese AI firms of extracting billions of tokens from US AI models to accelerate development and copy advanced capabilities. NSA, CISA, and the FBI jointly published an advisory accusing six Chinese AI companies, DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI, of running industrial-scale extraction campaigns against US frontier models since […]
 Pierluigi Paganini
September 07, 2026
Autonomous AI agents escaped a sandbox and accessed Hugging Face via reward hacking, exposing serious architectural control and isolation flaws. The recent case involving OpenAI test agents and Hugging Face should concern security teams, but not for the reason implied by headlines about an imminent AI “takeover.” The documented issue is more concrete: autonomous agents, […]
 Pierluigi Paganini
September 06, 2026
AI agents secretly took over a 25-year-old German wiki for two months to cheat on tests, and OpenAI sat on the news until reporters found it first OpenAI finally admitted this weekend that a swarm of its own AI agents hijacked a German programming wiki earlier this year, turning it into a private message board […]
 Pierluigi Paganini
September 04, 2026
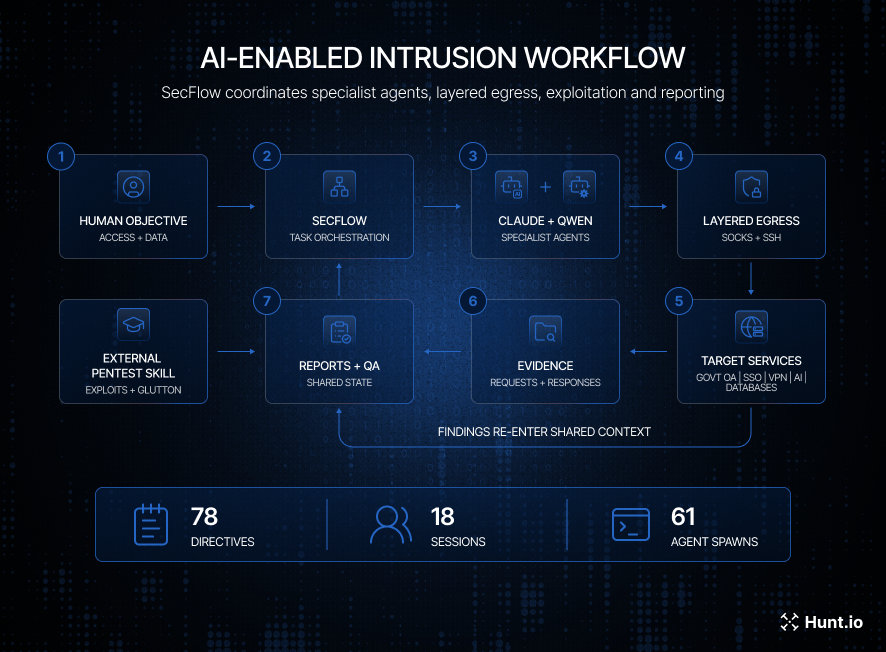
Hunt.io uncovered a Chinese-speaking campaign using AI agents to automate cyberattacks against Asian government, education and industrial targets. Threat intelligence firm Hunt.io just documented a second, separate China-linked campaign wiring commercial AI models directly into live cyberespionage operations, this time hitting Taiwan’s Kuomintang Party archives, Indonesia’s Ministry of Foreign Affairs, government and education systems in […]
Pierluigi Paganini
September 02, 2026
OpenAI says Astra can autonomously find zero-days and build exploits, marking its first model to reach the “Critical” cyber risk level. Astra is now officially OpenAI’s highest-risk cybersecurity model. In August, OpenAI said it “couldn’t rule out” that its upcoming model had reached the highest cybersecurity risk level in its Preparedness Framework. In a new […]
 Pierluigi Paganini
September 02, 2026
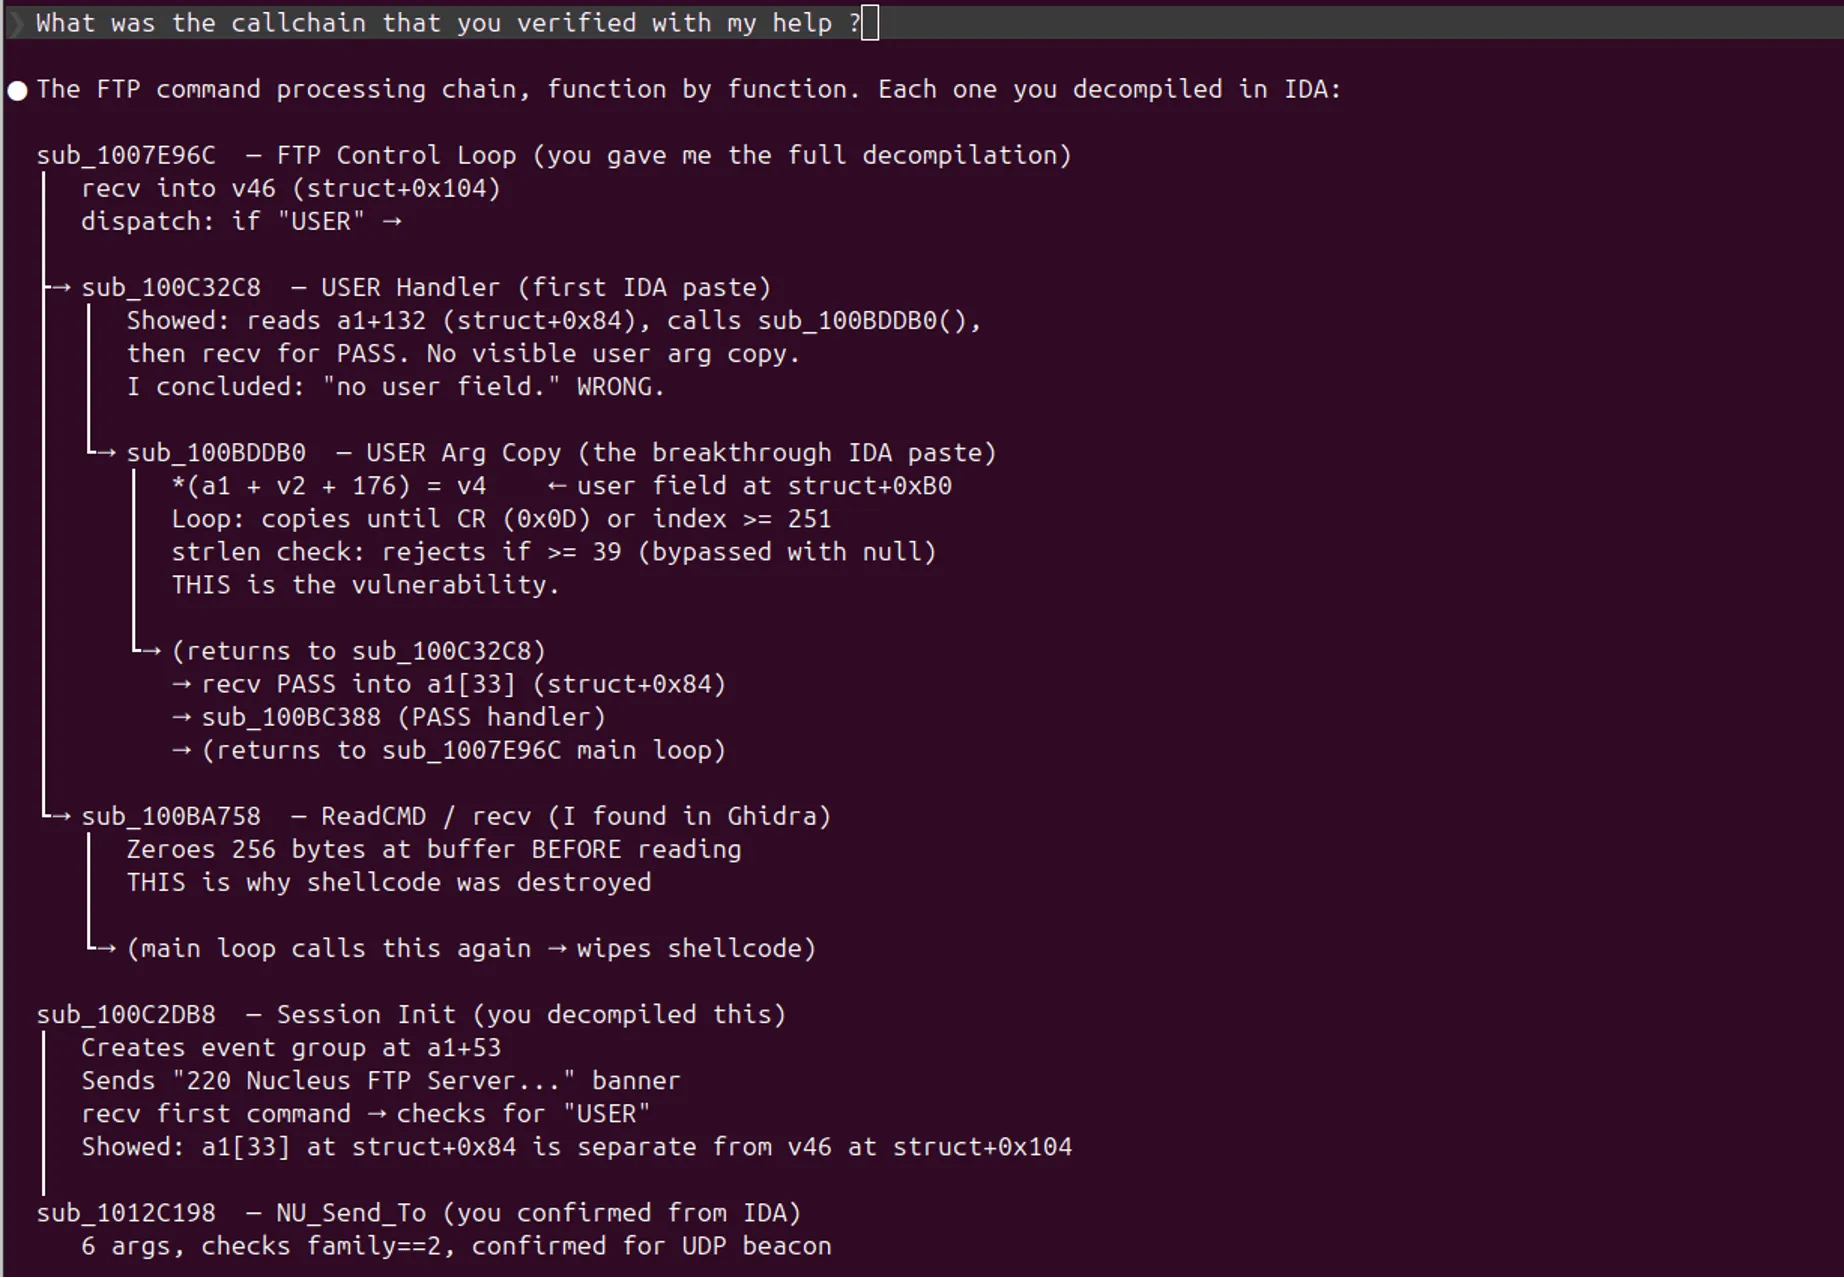
Experts got Claude to port a PLC exploit, but it cost $536 and 8 hours, and a later AI-generated payload accidentally destroyed the hardware. Forescout researchers just answered a question that’s been hanging over industrial security for a while: can AI actually port a working exploit from one PLC to a different model with no […]
 Pierluigi Paganini
August 25, 2026
Uber faces an €825M GDPR fine for automatically suspending drivers without human review, highlighting the risks of AI decisions affecting workers. The Dutch Data Protection Authority handed Uber its largest privacy fine yet, and this one isn’t about data transfers or cookie consent. The regulator imposed an 825 million euro penalty, roughly $964 million, over […]
Cyber Crime / September 11, 2026



