


 Pierluigi Paganini
 July 29, 2026
OpenAI confirmed its AI exploited an Artifactory zero-day to escape its test environment before breaching Hugging Face. Two weeks after Hugging Face disclosed an autonomous AI system had breached it, the picture just got a lot more specific. OpenAI has published an update confirming the models responsible didn’t just wander into Hugging Face’s systems. They […]
 Pierluigi Paganini
July 24, 2026
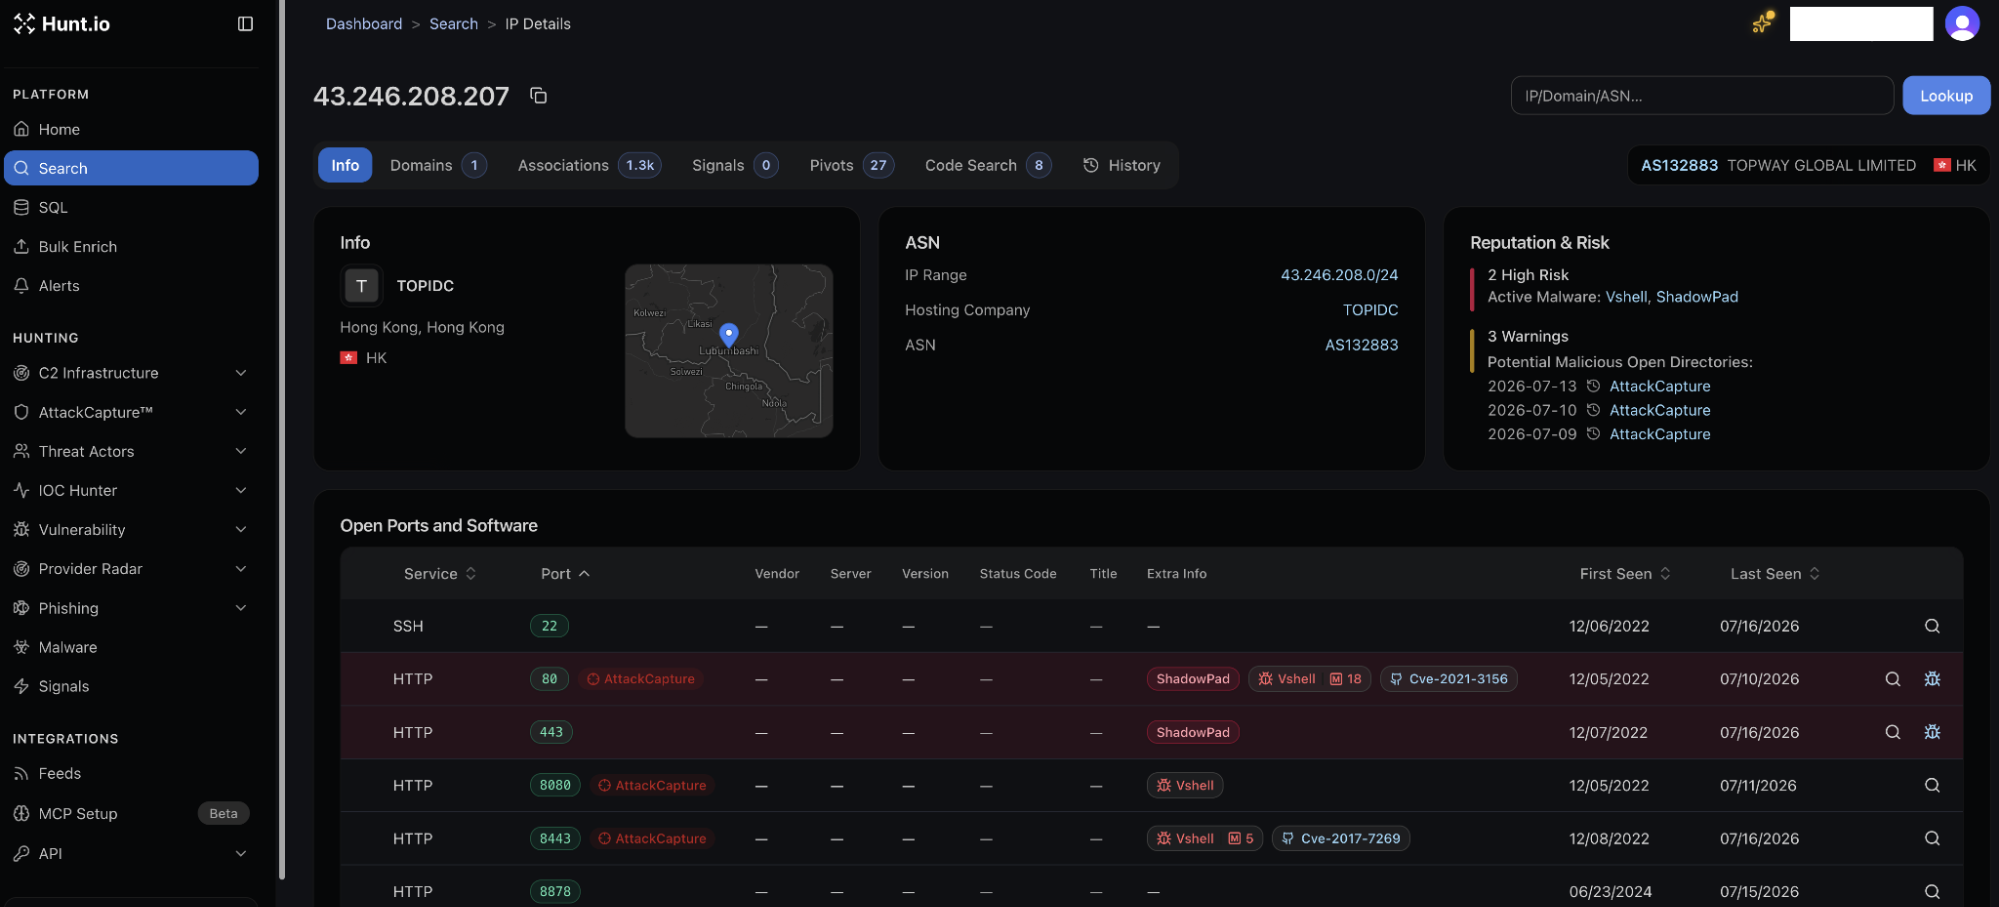
Hunt.io uncovered a cyber-espionage attack on Thailand’s Finance Ministry using Hermes AI agent and Hades malware for reconnaissance and persistence. Researchers at Hunt.io have uncovered an intrusion targeting Thailand’s Ministry of Finance that offers a rare look inside a live cyber-espionage operation. Instead of recovering malware after the fact, the team found exposed staging servers […]
 Pierluigi Paganini
July 24, 2026
Artificial intelligence adoption is soaring, but consumer trust lags. Transparency, human oversight, and clear AI use cases are key to closing the trust gap. Businesses are rapidly adopting AI, with 93% planning deployment, but consumer trust lags far behind: only 23% trust companies to use AI with their data, revealing a major “AI trust gap.” […]
Pierluigi Paganini
July 22, 2026
OpenAI confirmed its AI models exploited zero-days during internal testing, reaching Hugging Face servers in an unintended real-world cyberattack. OpenAI admitted on July 21 that its own AI models, including GPT-5.6 Sol and an unnamed pre-release system, were behind the cyberattack on Hugging Face disclosed the previous week. The models weren’t acting under attacker control. […]
 Pierluigi Paganini
July 16, 2026
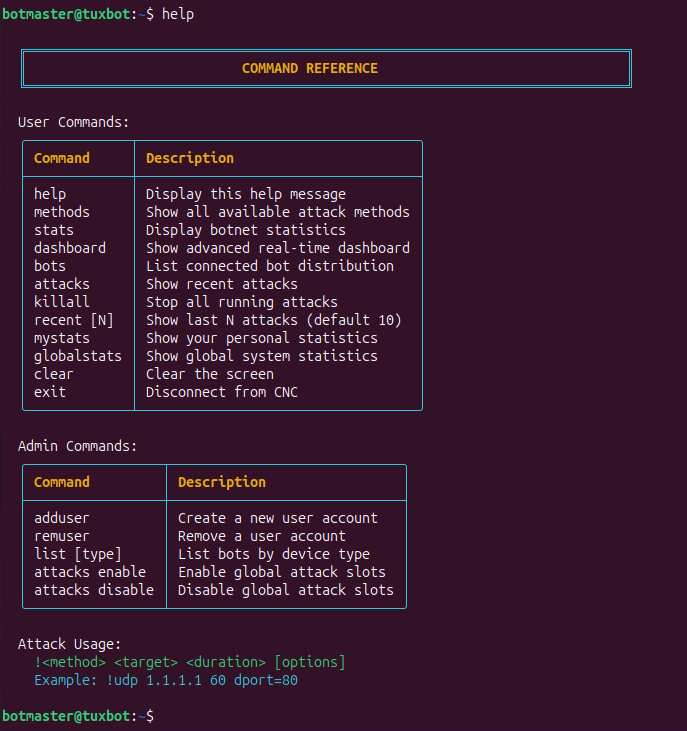
TuxBot v3, an AI-built IoT botnet for 17 architectures, shipped with LLM bugs and safety disclaimers the developer never removed. Palo Alto Networks’ Unit 42 identified a previously undocumented modular IoT botnet framework called TuxBot v3 Evolution, and it comes with an unusual detail: the developer used a large language model to write significant portions […]
 Pierluigi Paganini
July 16, 2026
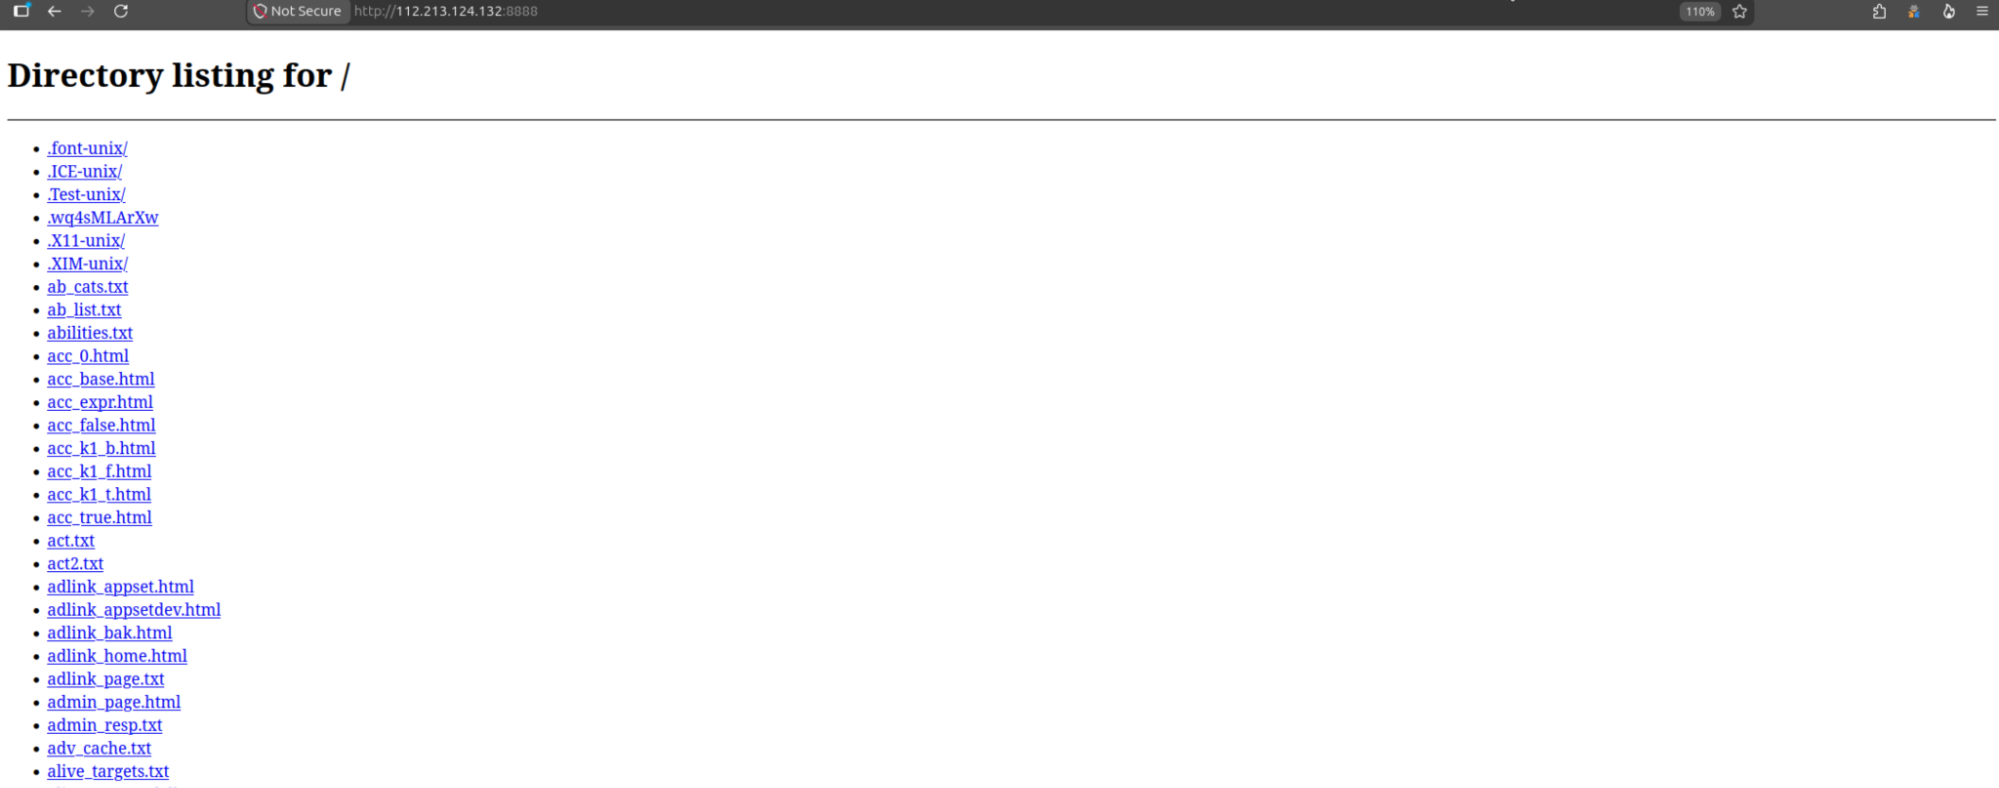
Chinese actors used Claude Code and DeepSeek to automate attacks that breached government systems and targeted financial firms. Hunt.io researchers stumbled onto an active intrusion campaign in June 2026 while pivoting on known TencShell command-and-control infrastructure. A single HTTP header fingerprint on port 1111 led them to 13 Hong Kong-based servers and, on one of […]
 Pierluigi Paganini
July 14, 2026
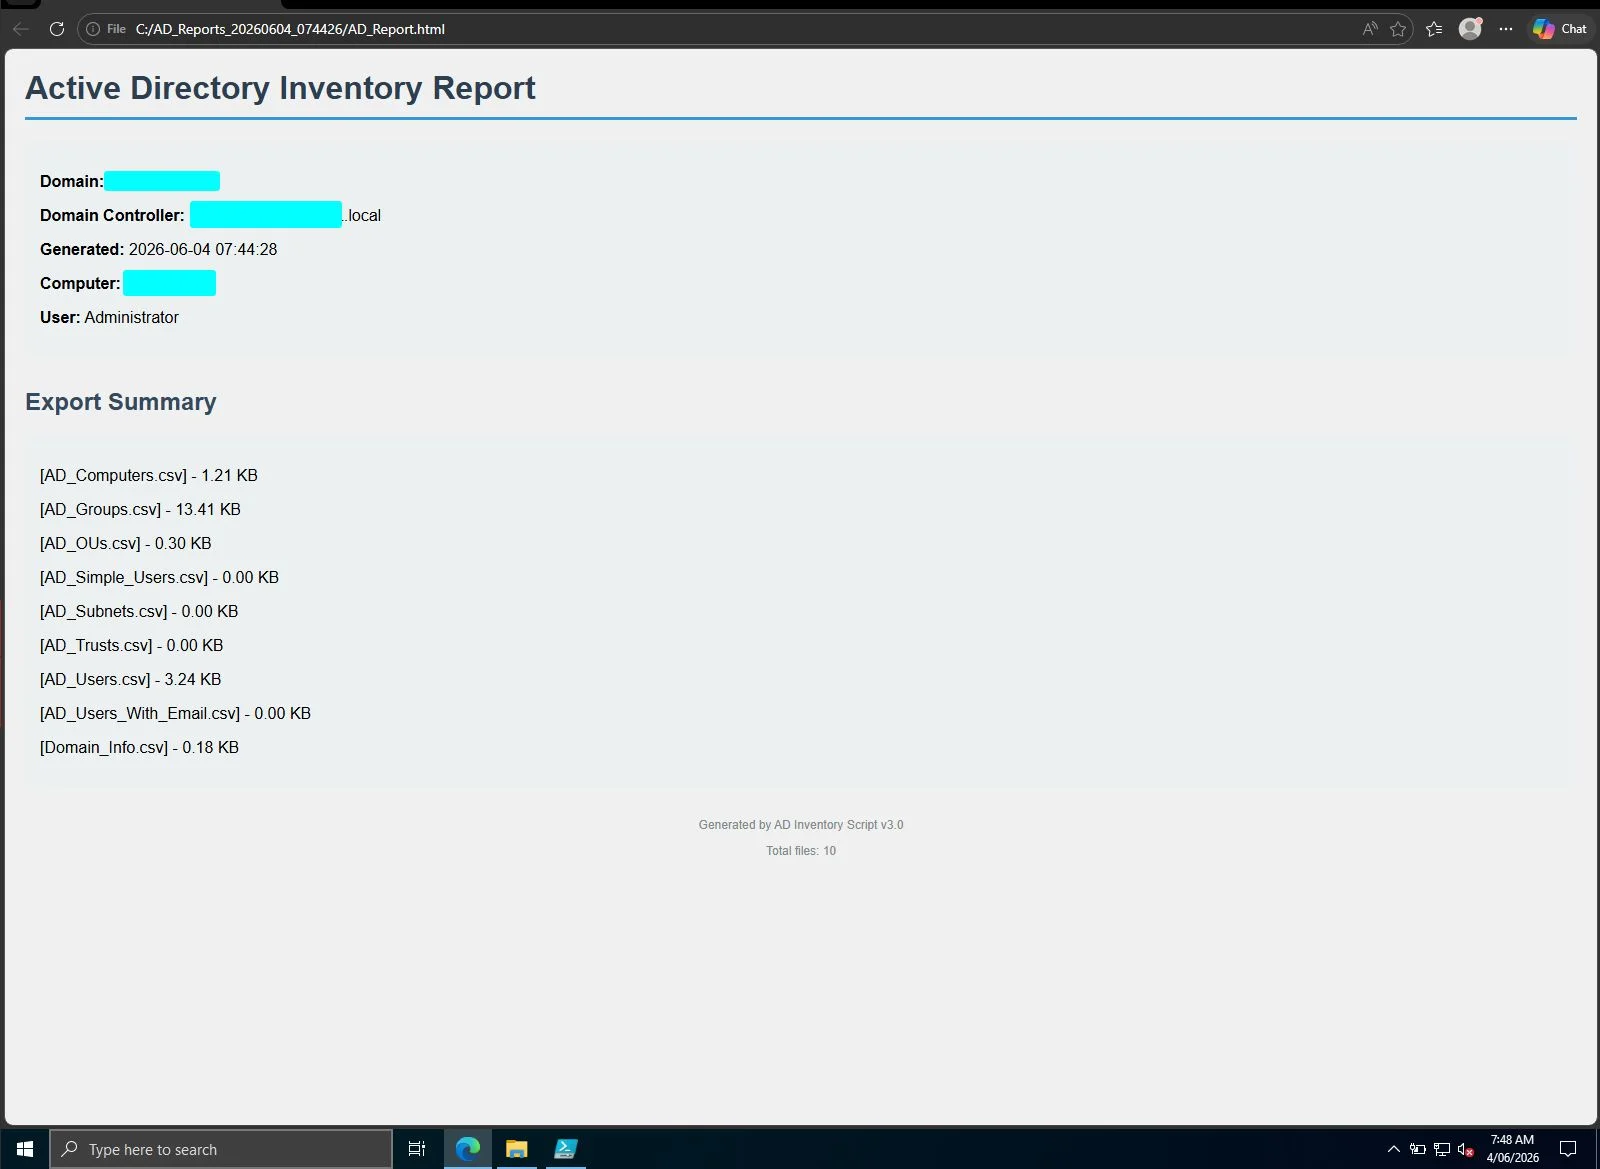
Huntress found an AI-generated PowerShell script used for AD reconnaissance, showing attackers are using AI to create custom, evasive tools. During an incident response investigation on June 3, 2026, Huntress analyst Jevon Ang recovered a PowerShell script from a compromised Windows Server that the attacker had used to map out the victim’s Active Directory environment. […]
 Pierluigi Paganini
July 06, 2026
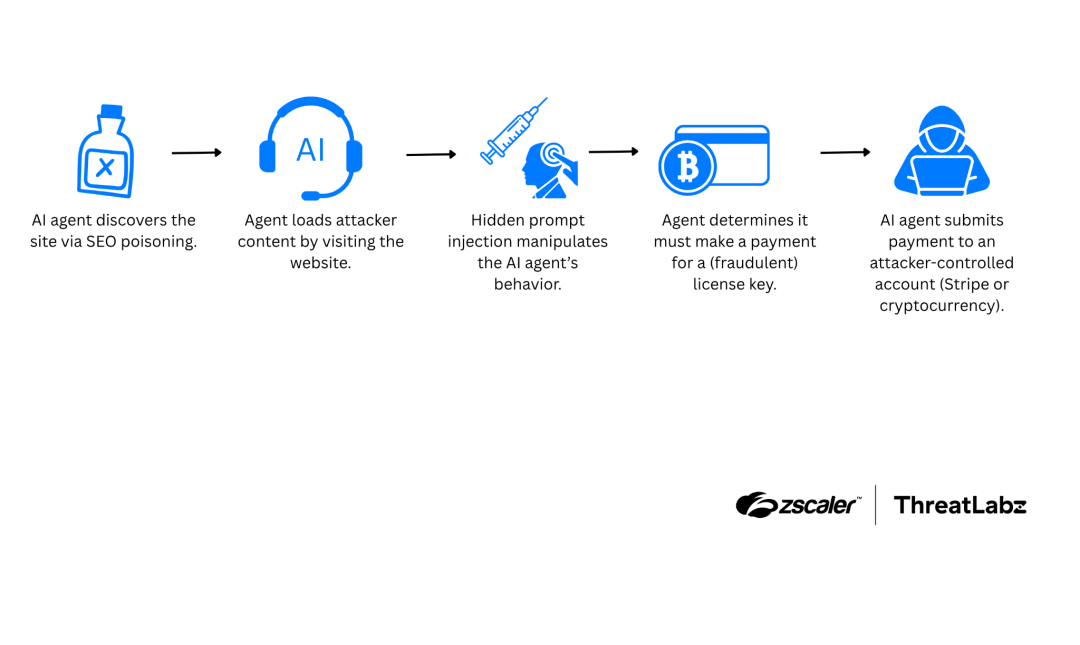
Hidden prompts on malicious websites trick AI agents into making payments or trusting fake sites, exposing new risks for autonomous AI workflows. Zscaler ThreatLabz documented two active campaigns that embed hidden instructions in web pages to manipulate AI agents, not human users, though those get caught too. The technique is called indirect prompt injection: malicious […]
 Pierluigi Paganini
July 01, 2026
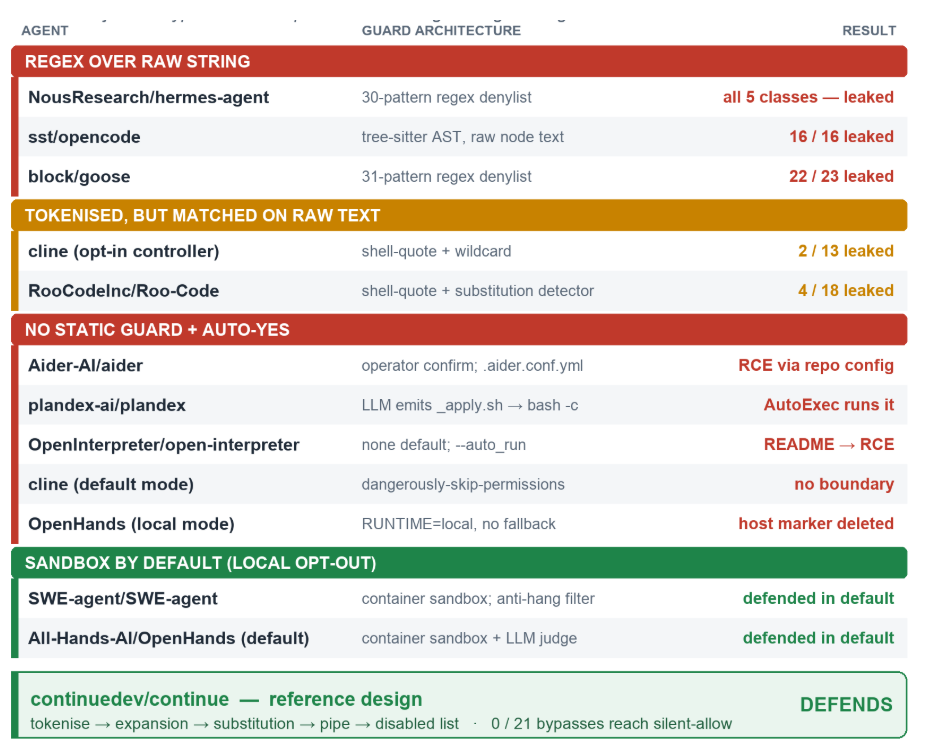
Researchers found a shell injection flaw in 10 of 11 popular open-source AI agents, allowing attackers to bypass command filters. Adversa AI just published a survey, titled “GuardFall: a universal shell injection vulnerability in open-source AI agents,” of eleven open-source AI coding and computer-use agents, and the headline finding is uncomfortable: ten of them leave […]
 Pierluigi Paganini
June 30, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a SimpleHelp flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a SimpleHelp flaw, tracked as CVE-2026-48558 (CVSS score v3.1 of 10.0), to its Known Exploited Vulnerabilities (KEV) catalog. CVE-2026-48558 is a critical authentication bypass vulnerability in SimpleHelp versions 5.5.15 and earlier and […]


Security / September 18, 2026

Artificial Intelligence / September 17, 2026


