 Pierluigi Paganini
 April 10, 2023
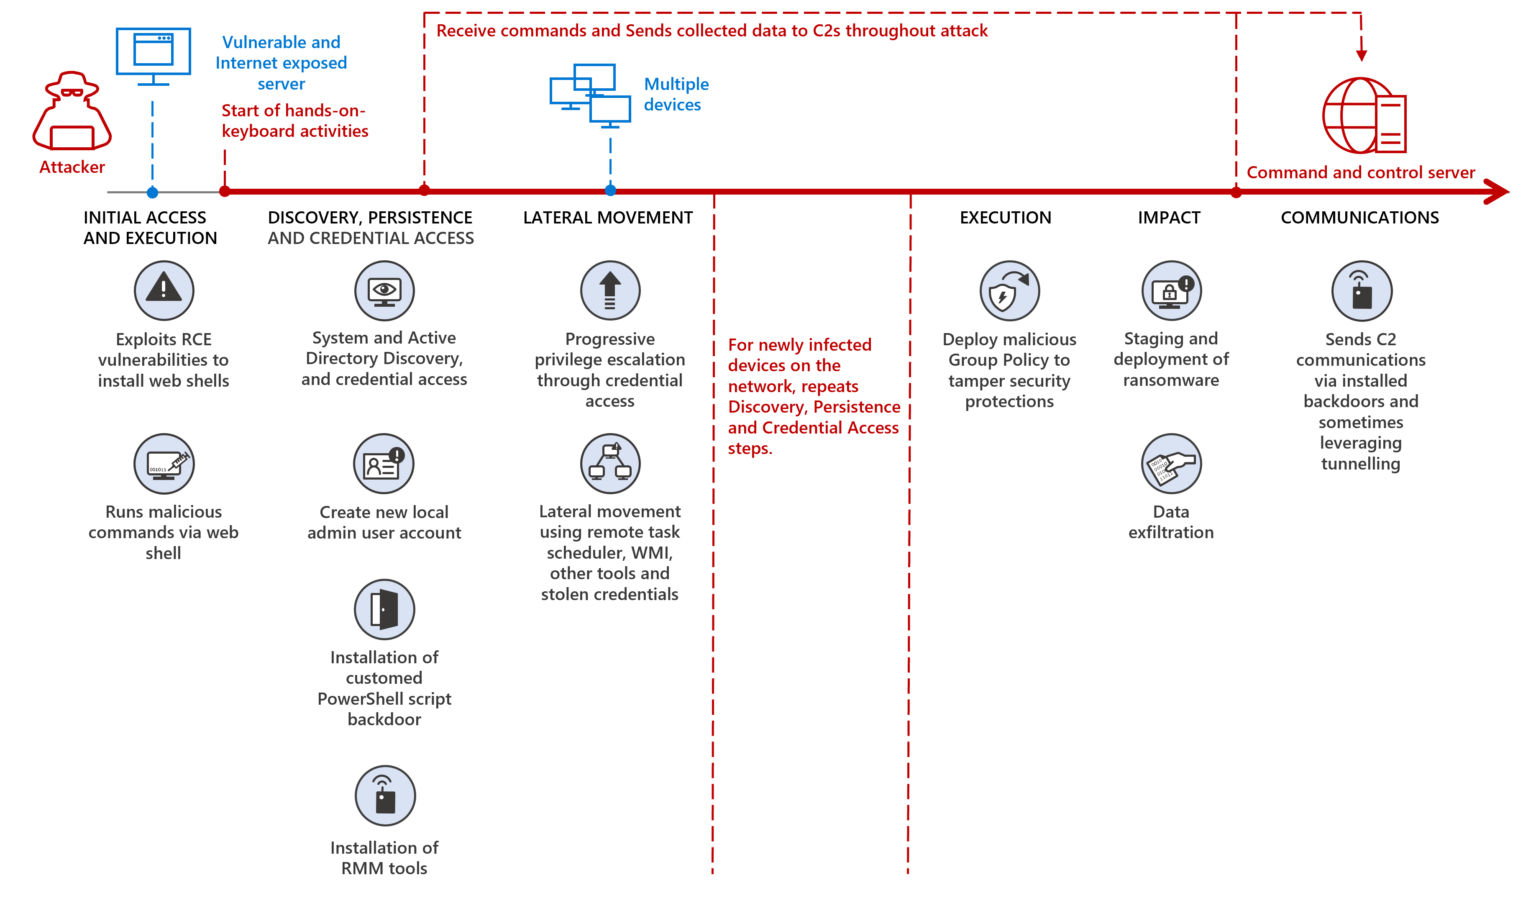
Iran-linked APT group MERCURY is behind destructive attacks on hybrid environments masquerading as a ransomware operation. The Microsoft Threat Intelligence team observed a series of destructive attacks on hybrid environments that were carried out by MuddyWater APT group (aka MERCURY). Threat actors masqueraded the attacks as a standard ransomware operation. MERCURY (aka MuddyWater, SeedWorm and TEMP.Zagros) has been active since […]
 Pierluigi Paganini
April 06, 2023
Google’s Threat Analysis Group (TAG) warns of a North Korea-linked cyberespionage group tracked as ARCHIPELAGO. Google’s Threat Analysis Group (TAG) is warning of the North Korea-linked ARCHIPELAGO group that is targeting government and military personnel, think tanks, policy makers, academics, and researchers in South Korea, the US and elsewhere. Google experts are tracking ARCHIPELAGO since […]
 Pierluigi Paganini
March 28, 2023
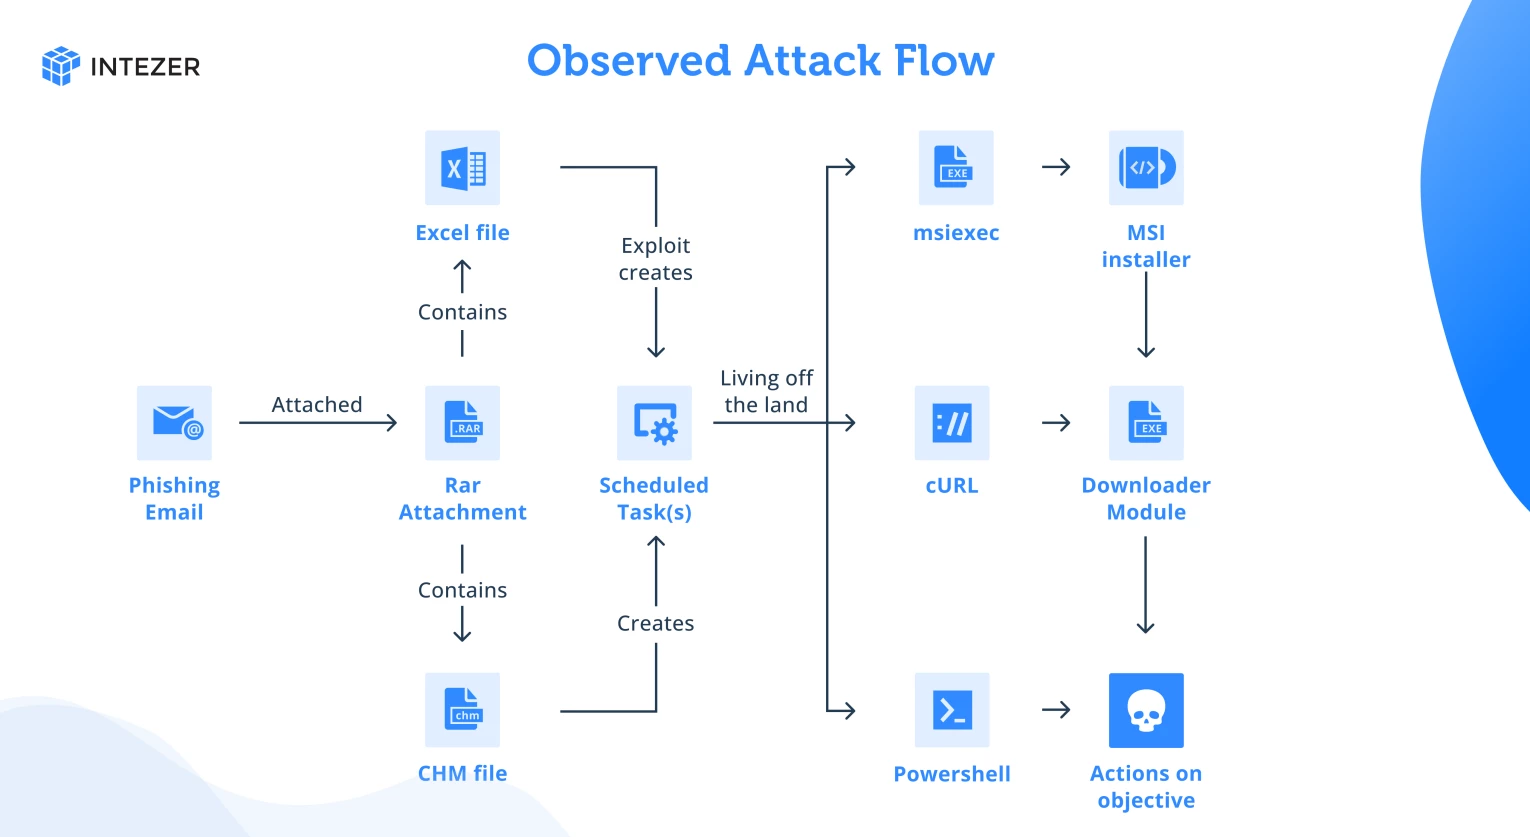
Intezer researchers reported that a South Asian espionage group, tracked as Bitter, is targeting the Chinese nuclear energy industry. Intezer researchers uncovered a cyberespionage campaign targeting the Chinese nuclear energy sector, they linked it to the Bitter APT group. The Bitter APT group is a South Asian cyberespionage group active since at least 2021. The group […]
 Pierluigi Paganini
March 27, 2023
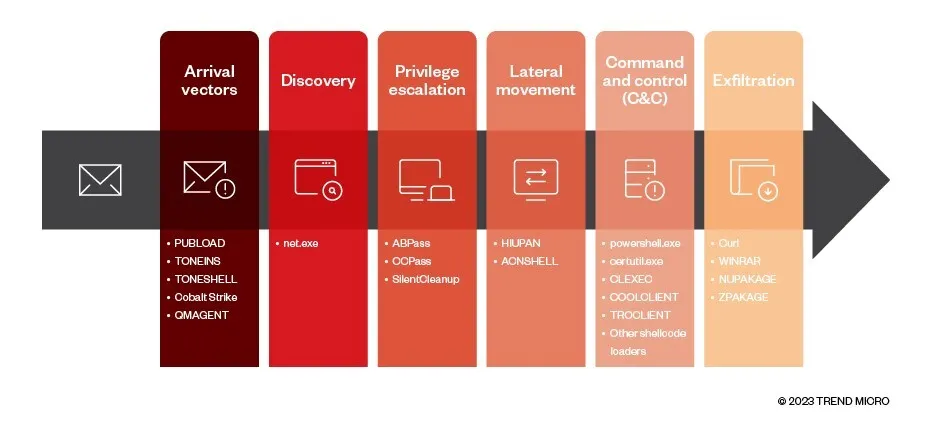
China-linked Earth Preta cyberespionage group has been observed adopting new techniques to bypass security solutions. Trend Micro researchers reported that the China-linked Earth Preta group (aka Mustang Panda) is actively changing its tools, tactics, and procedures (TTPs) to bypass security solutions. Earth Preta, also known as “RedDelta” or “Bronze President,” has been active since at least […]
 Pierluigi Paganini
March 15, 2023
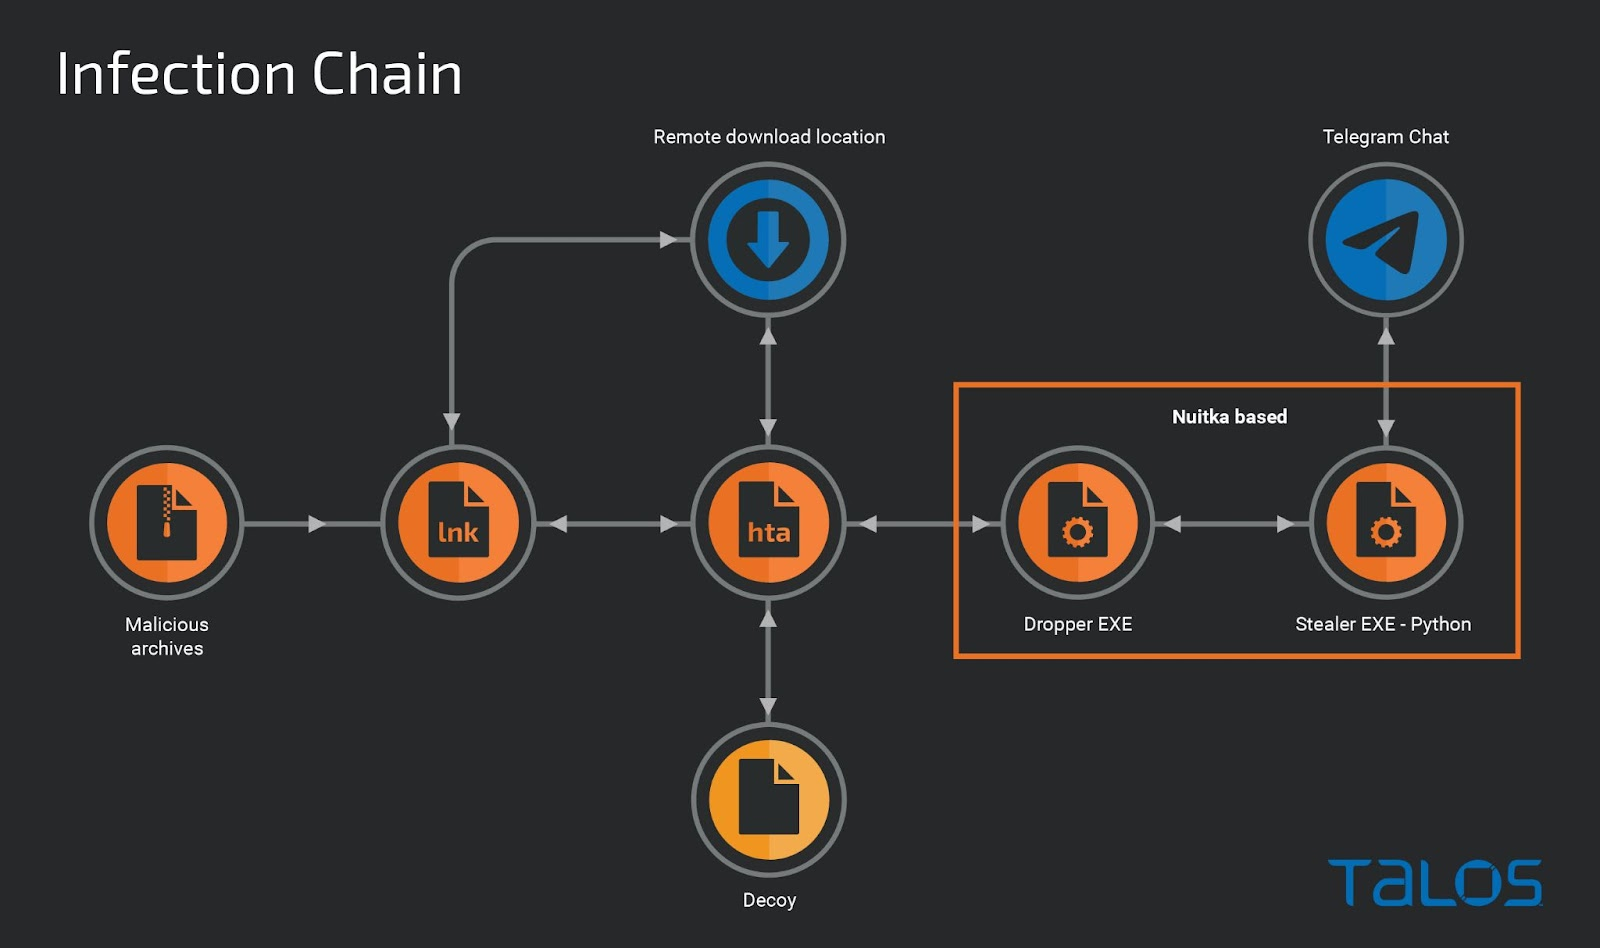
A new APT group, dubbed YoroTrooper, has been targeting government and energy organizations across Europe, experts warn. Cisco Talos researchers uncovered a new cyber espionage group targeting CIS countries, embassies and EU health care agency since at least June 2022. The APT group focuses on government or energy organizations in Azerbaijan, Tajikistan, Kyrgyzstan and other Commonwealth […]
 Pierluigi Paganini
March 08, 2023
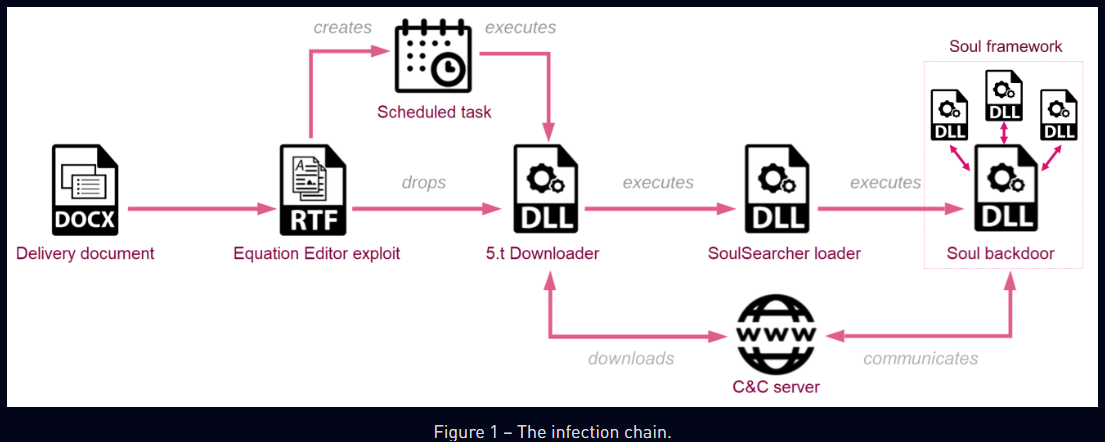
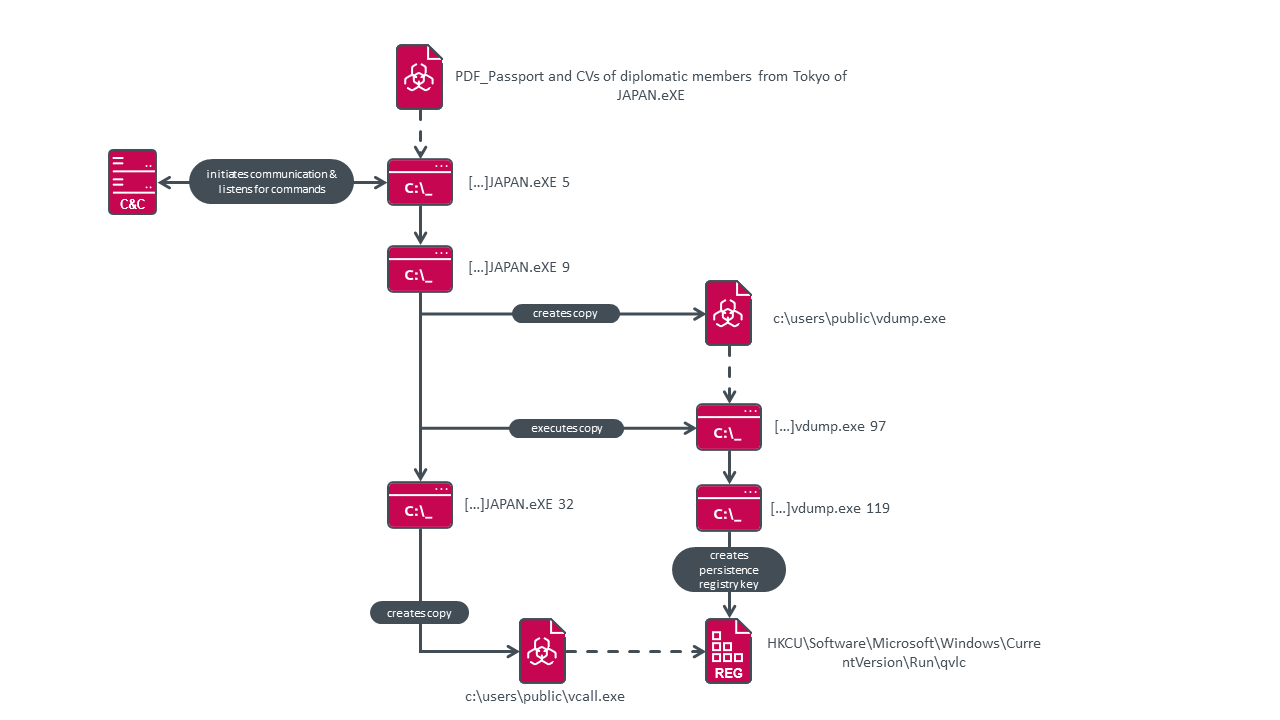
China-linked APT group Sharp Panda targets high-profile government entities in Southeast Asia with the Soul modular framework. CheckPoint researchers observed in late 2022, a campaign attributed to the China-linked APT group Sharp Panda that is targeting a high-profile government entity in the Southeast Asia. The state-sponsored hackers used a new version of the SoulSearcher loader, which eventually loads a new […]
 Pierluigi Paganini
March 03, 2023
China-Linked Mustang Panda APT employed MQsTTang backdoor as part of an ongoing campaign targeting European entities. China-linked Mustang Panda APT group has been observed using a new backdoor, called MQsTTang, in attacks aimed at European entities. The hacking campaign began in January 2023, ESET researchers pointed out that the custom backdoor MQsTTang is not based on existing families […]
 Pierluigi Paganini
February 19, 2023
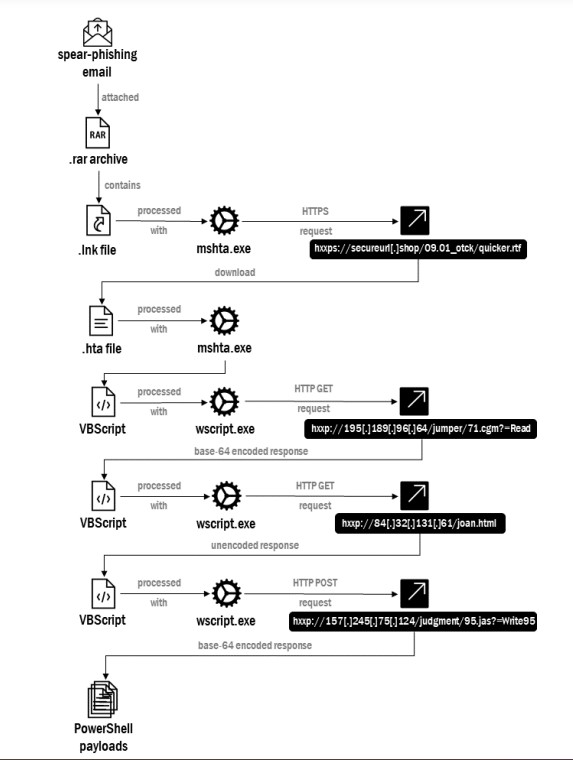
A joint report published by ENISA and CERT-EU warns of Chinese APTs targeting businesses and government organizations in the European Union. The European Union Agency for Cybersecurity (ENISA) and CERT-EU warn of multiple China-linked threat actors targeting businesses and government organizations in the EU. The joint report focus on cyber activities conducted by multiple Chinese […]
 Pierluigi Paganini
February 03, 2023
Russia-linked threat actor Gamaredon employed new spyware in cyber attacks aimed at public authorities and critical information infrastructure in Ukraine. The State Cyber Protection Centre (SCPC) of Ukraine warns of a new wave of targeted attacks conducted by the Russia-linked APT group Gamaredon (aka Shuckworm, Actinium, Armageddon, Primitive Bear, UAC-0010, and Trident Ursa). The attacks aimed at public authorities and critical information […]
 Pierluigi Paganini
January 30, 2023
The Ukrainian (CERT-UA) discovered five different wipers deployed on the network of the country’s national news agency, Ukrinform. On January 17, 2023, the Telegram channel “CyberArmyofRussia_Reborn” reported the compromise of the systems at the Ukrainian National Information Agency “Ukrinform”. The Ukrainian Computer Emergency Response Team (CERT-UA) immediately investigated the claims and as of January 27, […]