Pierluigi Paganini
 November 15, 2022
A suspected China-linked APT group breached a digital certificate authority in Asia as part of a campaign aimed at government agencies since March 2022. State-sponsored actors compromised a digital certificate authority in a country in Asia as part of a cyber espionage campaign aimed at multiple government agencies in the region, Symantec warns. Symantec attributes […]
 Pierluigi Paganini
November 15, 2022
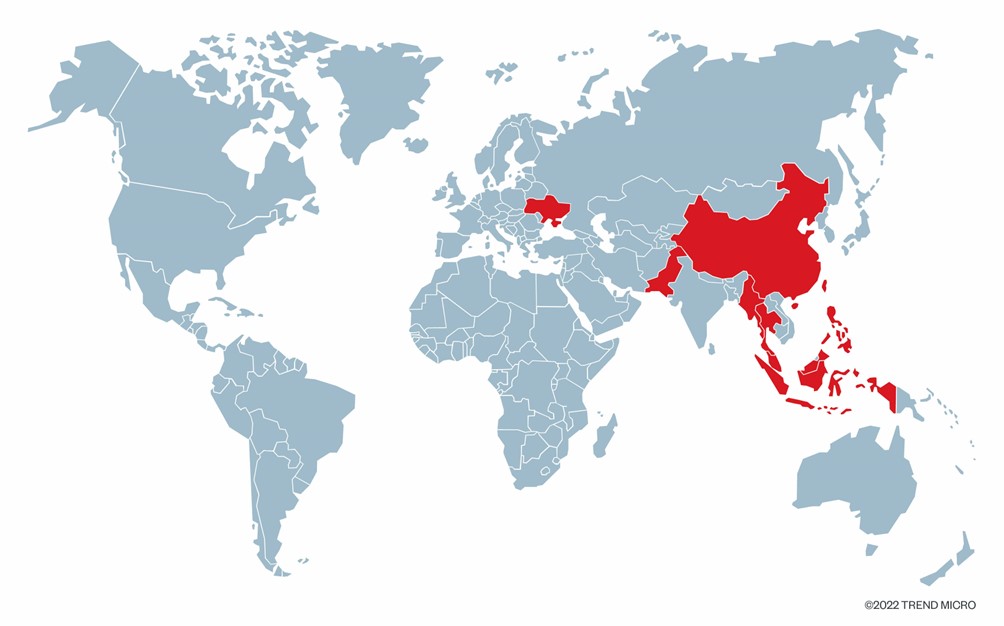
Trend Micro reported that the Earth Longzhi group, a previously undocumented subgroup of APT41, targets Ukraine and Asian Countries. Early this year, Trend Micro investigated a security breach suffered by a company in Taiwan. Threat actors employed a custom Cobalt Strike loader in the attack. Further analysis, revealed that the same threat actor targeted multiple regions […]
 Pierluigi Paganini
November 11, 2022
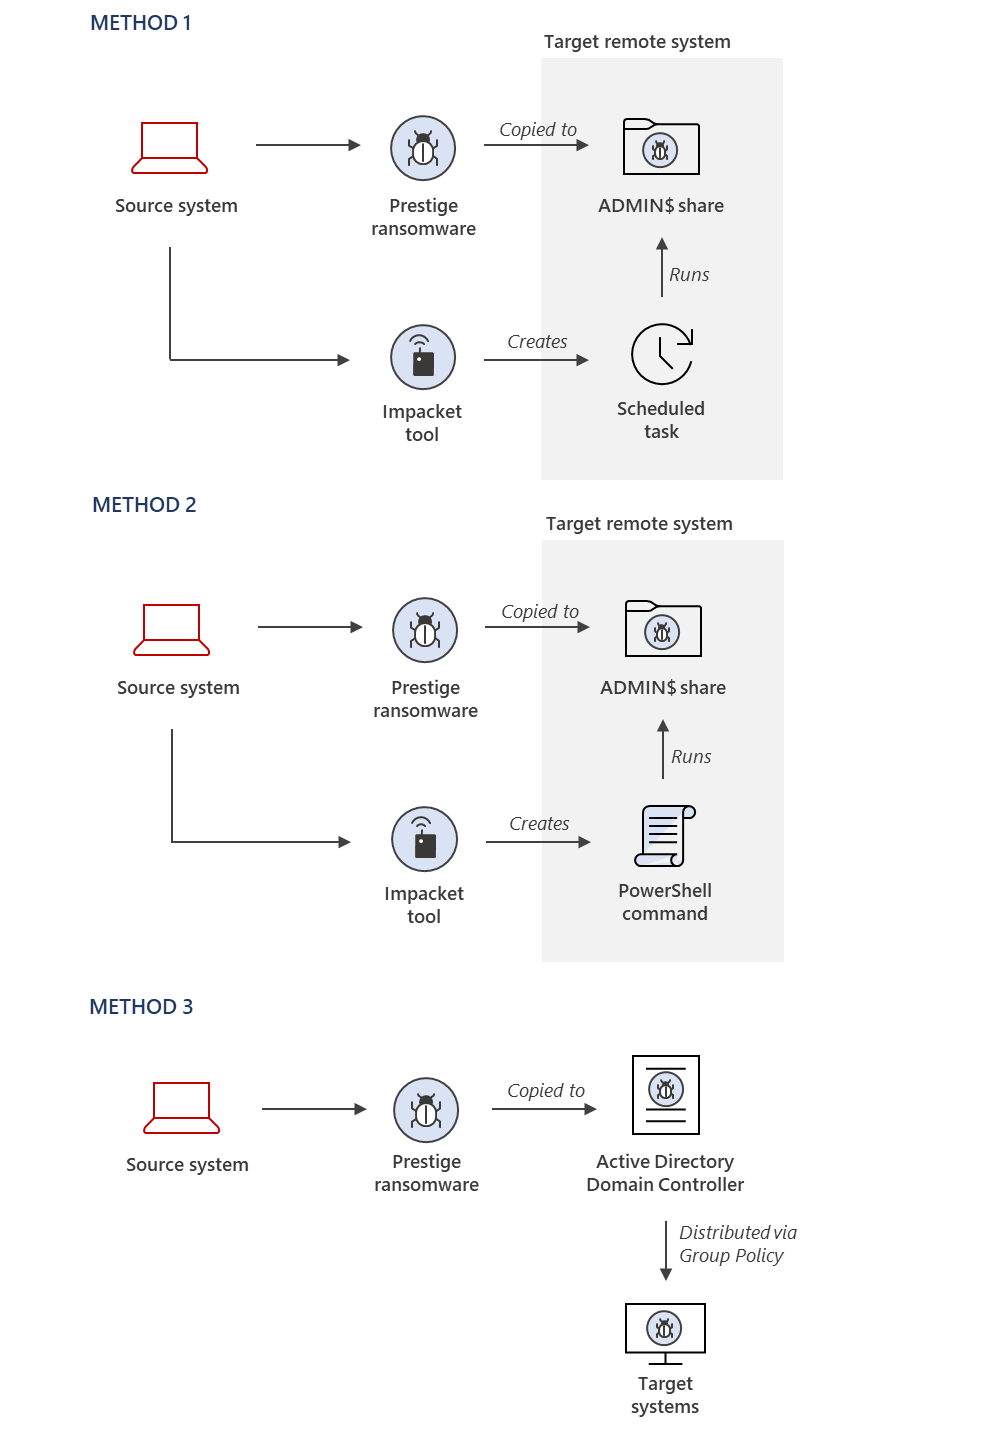
Microsoft linked Prestige ransomware attacks against organizations in Ukraine and Poland to Russia-linked threat actors. In Mid-October, Microsoft Threat Intelligence Center (MSTIC) researchers uncovered previously undetected ransomware, tracked as Prestige ransomware, employed in attacks targeting organizations in the transportation and related logistics industries in Ukraine and Poland. The Prestige ransomware first appeared in the threat […]
 Pierluigi Paganini
October 13, 2022
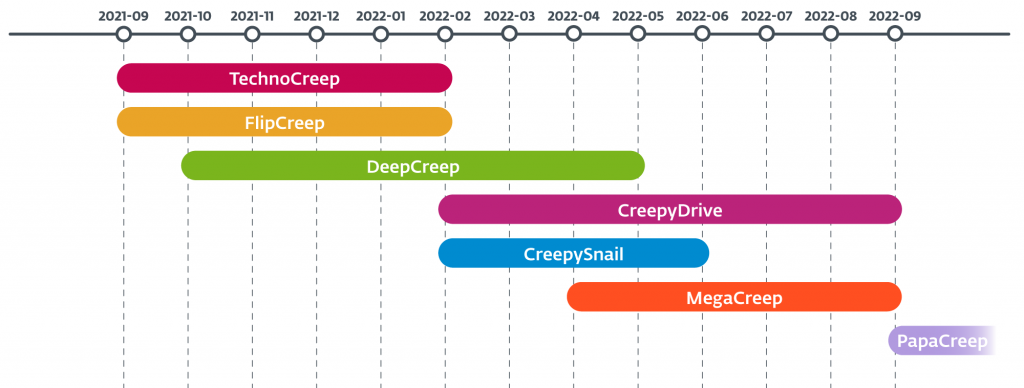
The Budworm espionage group resurfaced targeting a U.S.-based organization for the first time, Symantec Threat Hunter team reported. The Budworm cyber espionage group (aka APT27, Bronze Union, Emissary Panda, Lucky Mouse, TG-3390, and Red Phoenix) is behind a series attacks conducted over the past six months against a number of high-profile targets, including the government of […]
 Pierluigi Paganini
October 13, 2022
An APT group tracked as Polonium employed custom backdoors in attacks aimed at Israelian entities since at least September 2021. POLONIUM APT focused only on Israeli targets, it launched attacks against more than a dozen organizations in various industries, including engineering, information technology, law, communications, branding and marketing, media, insurance, and social services. Microsoft MSTIC […]
 Pierluigi Paganini
September 28, 2022
The Russia-linked APT28 group is using mouse movement in decoy Microsoft PowerPoint documents to distribute malware. The Russia-linked APT28 employed a technique relying on mouse movement in decoy Microsoft PowerPoint documents to deploy malware, researchers from Cluster25 reported. Cluster25 researchers were analyzing a lure PowerPoint document used to deliver a variant of Graphite malware, which is known to be used […]
 Pierluigi Paganini
September 27, 2022
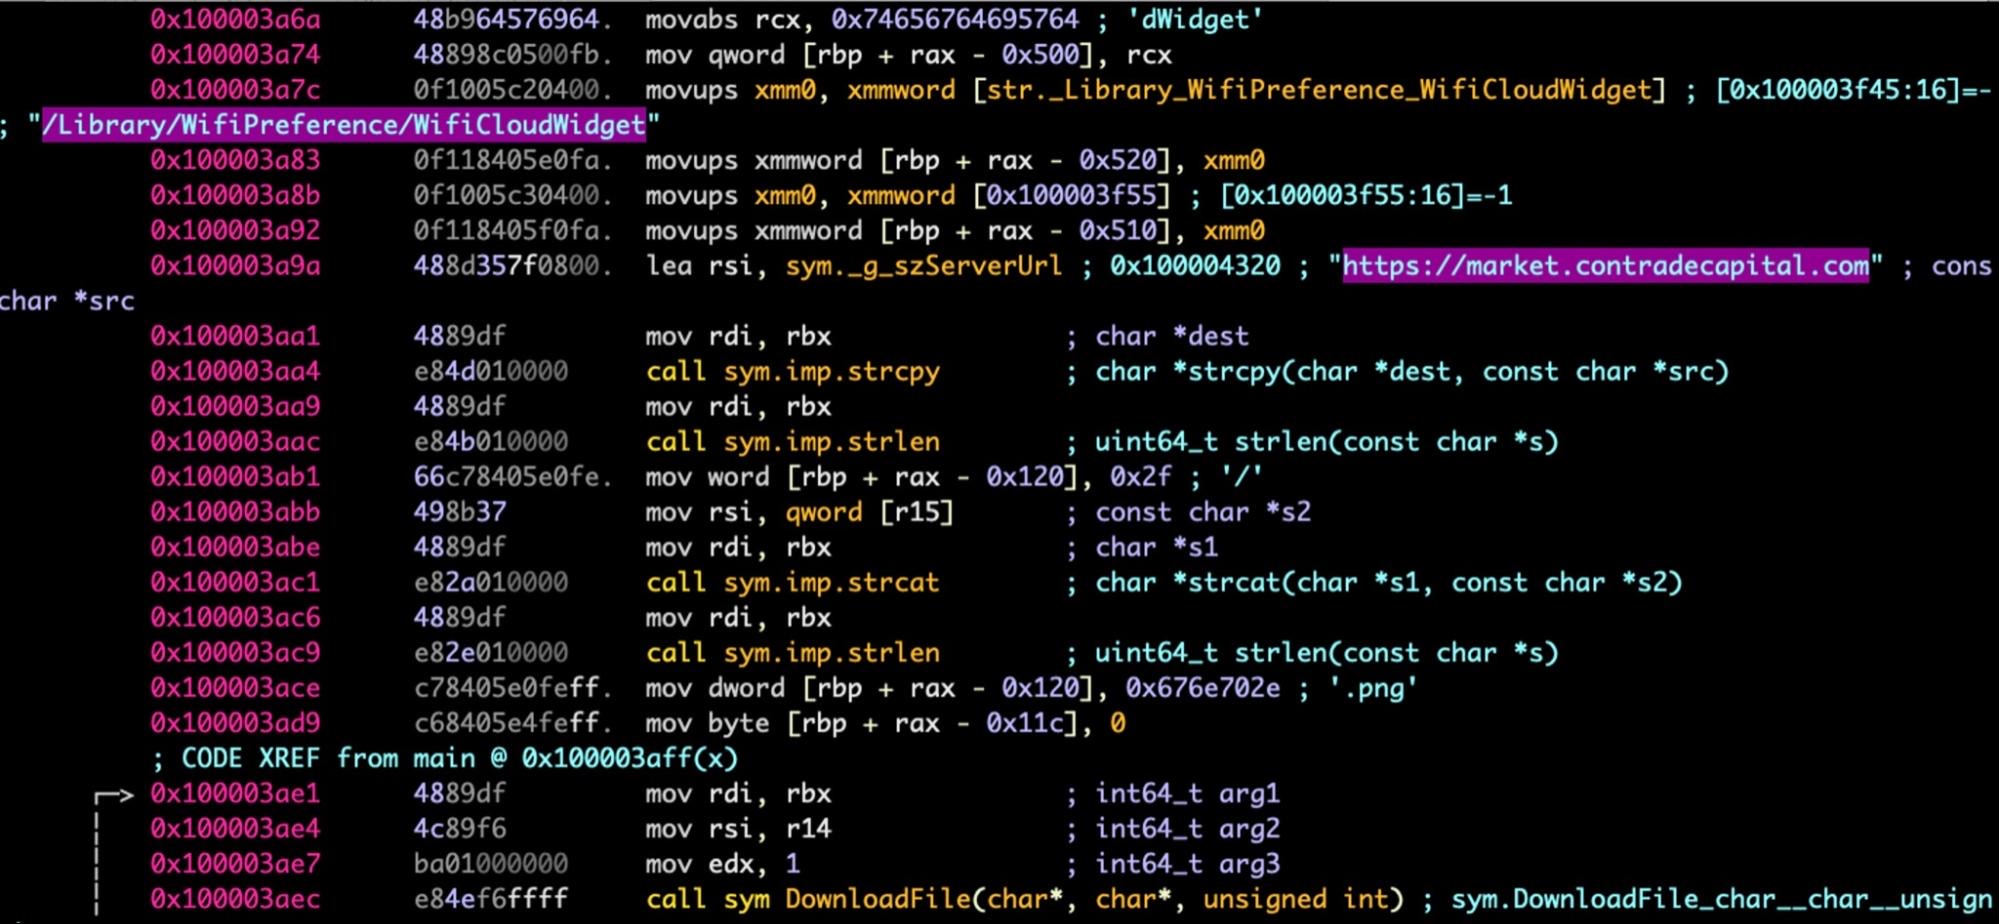
North Korea-linked Lazarus APT group is targeting macOS Users searching for jobs in the cryptocurrency industry. North Korea-linked Lazarus APT group continues to target macOS with a malware campaign using job opportunities as a lure. The attackers aimed at stealing credentials for the victims’ wallets. Last week, SentinelOne researchers discovered a decoy documents advertising positions […]
 Pierluigi Paganini
September 26, 2022
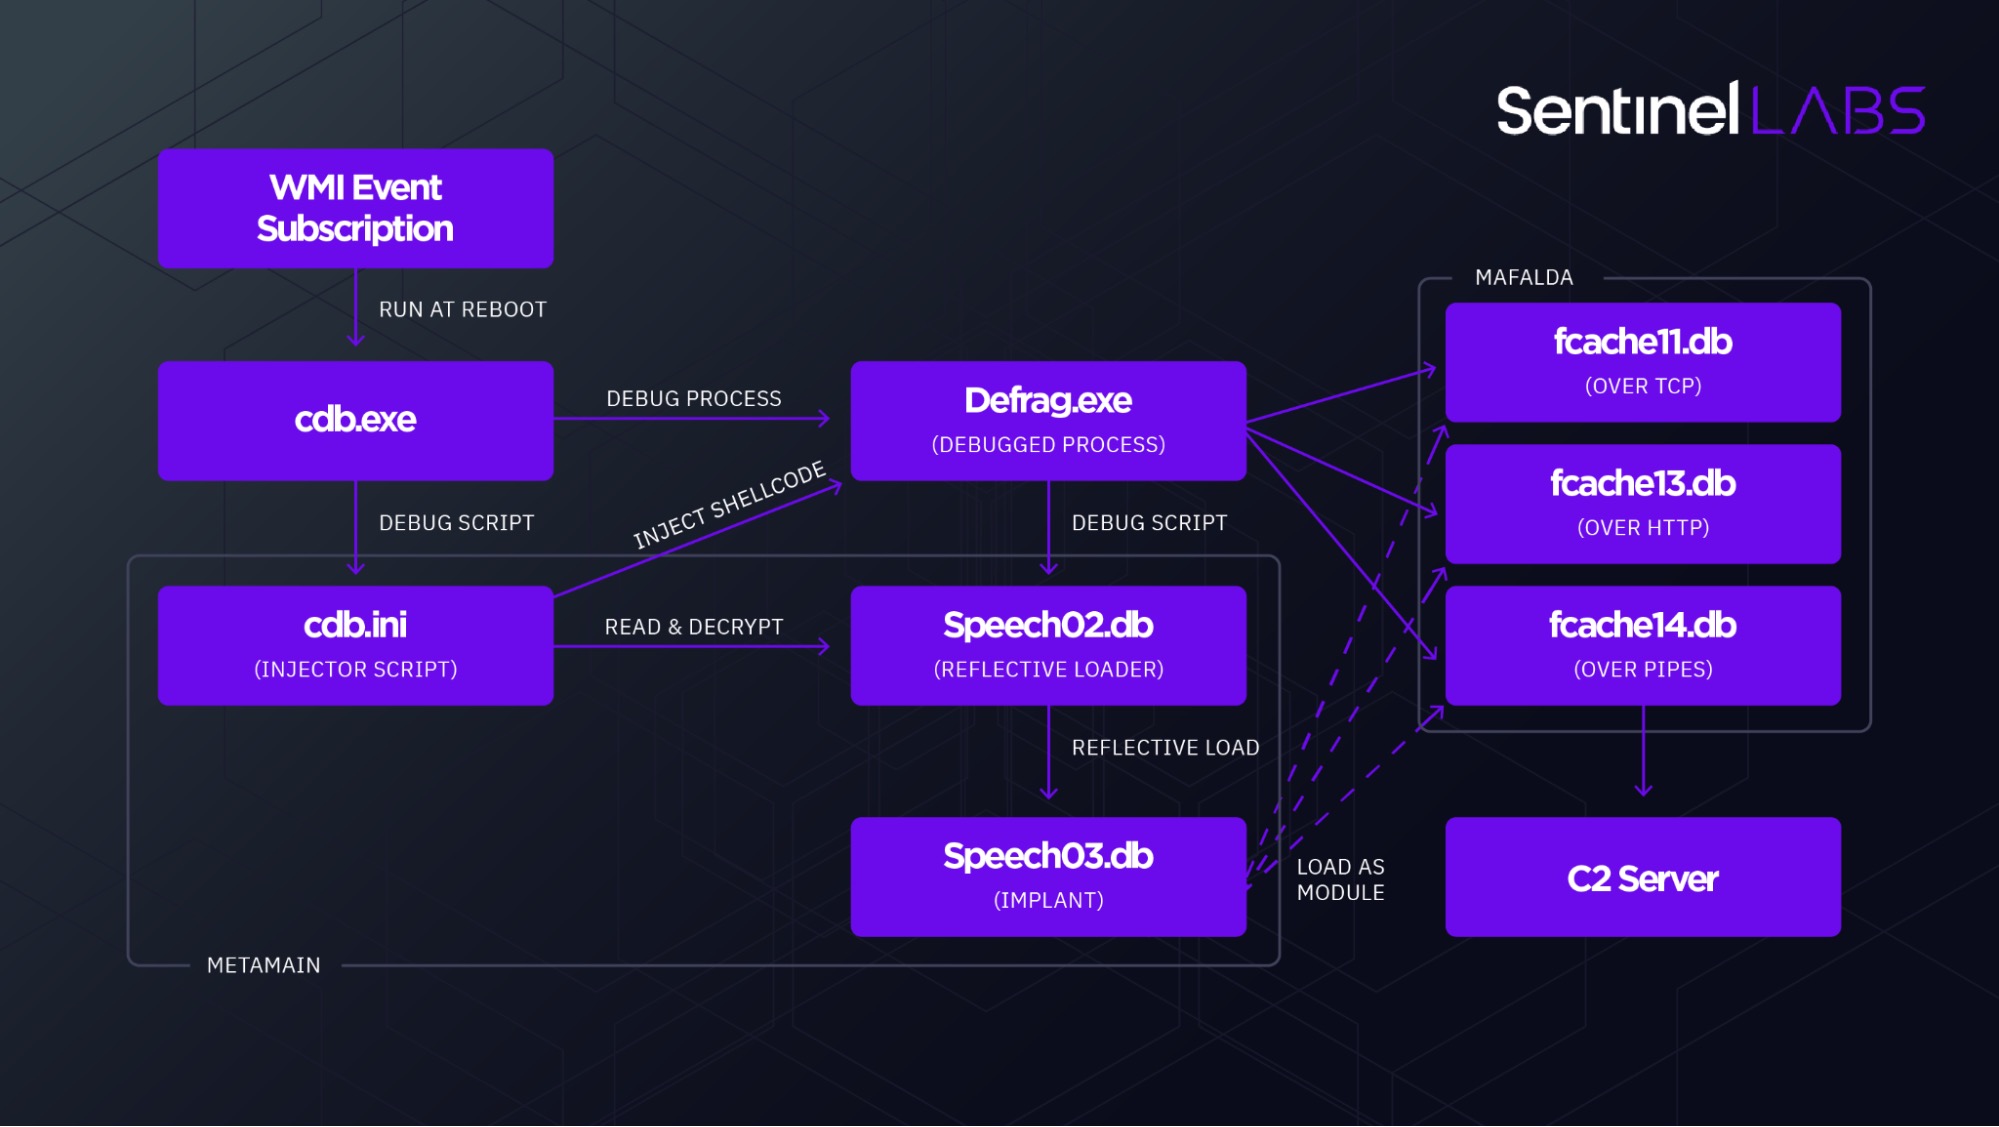
A previously undetected hacking group, tracked as Metador, has been targeting telecommunications, internet services providers (ISPs), and universities for about two years. SentinelLabs researchers uncovered a never-before-seen threat actor, tracked as Metador, that primarily targets telecommunications, internet service providers, and universities in several countries in the Middle East and Africa. The experts pointed out that […]
 Pierluigi Paganini
September 20, 2022
Russia-linked APT group Sandworm has been observed impersonating telecommunication providers to target Ukrainian entities with malware. Russia-linked cyberespionage group Sandworm has been observed impersonating telecommunication providers to target Ukrainian entities with malware. Multiple security firms have reported that the Sandworm APT continues to target Ukraine with multiple means, including custom malware and botnet like Cyclops […]
 Pierluigi Paganini
September 16, 2022
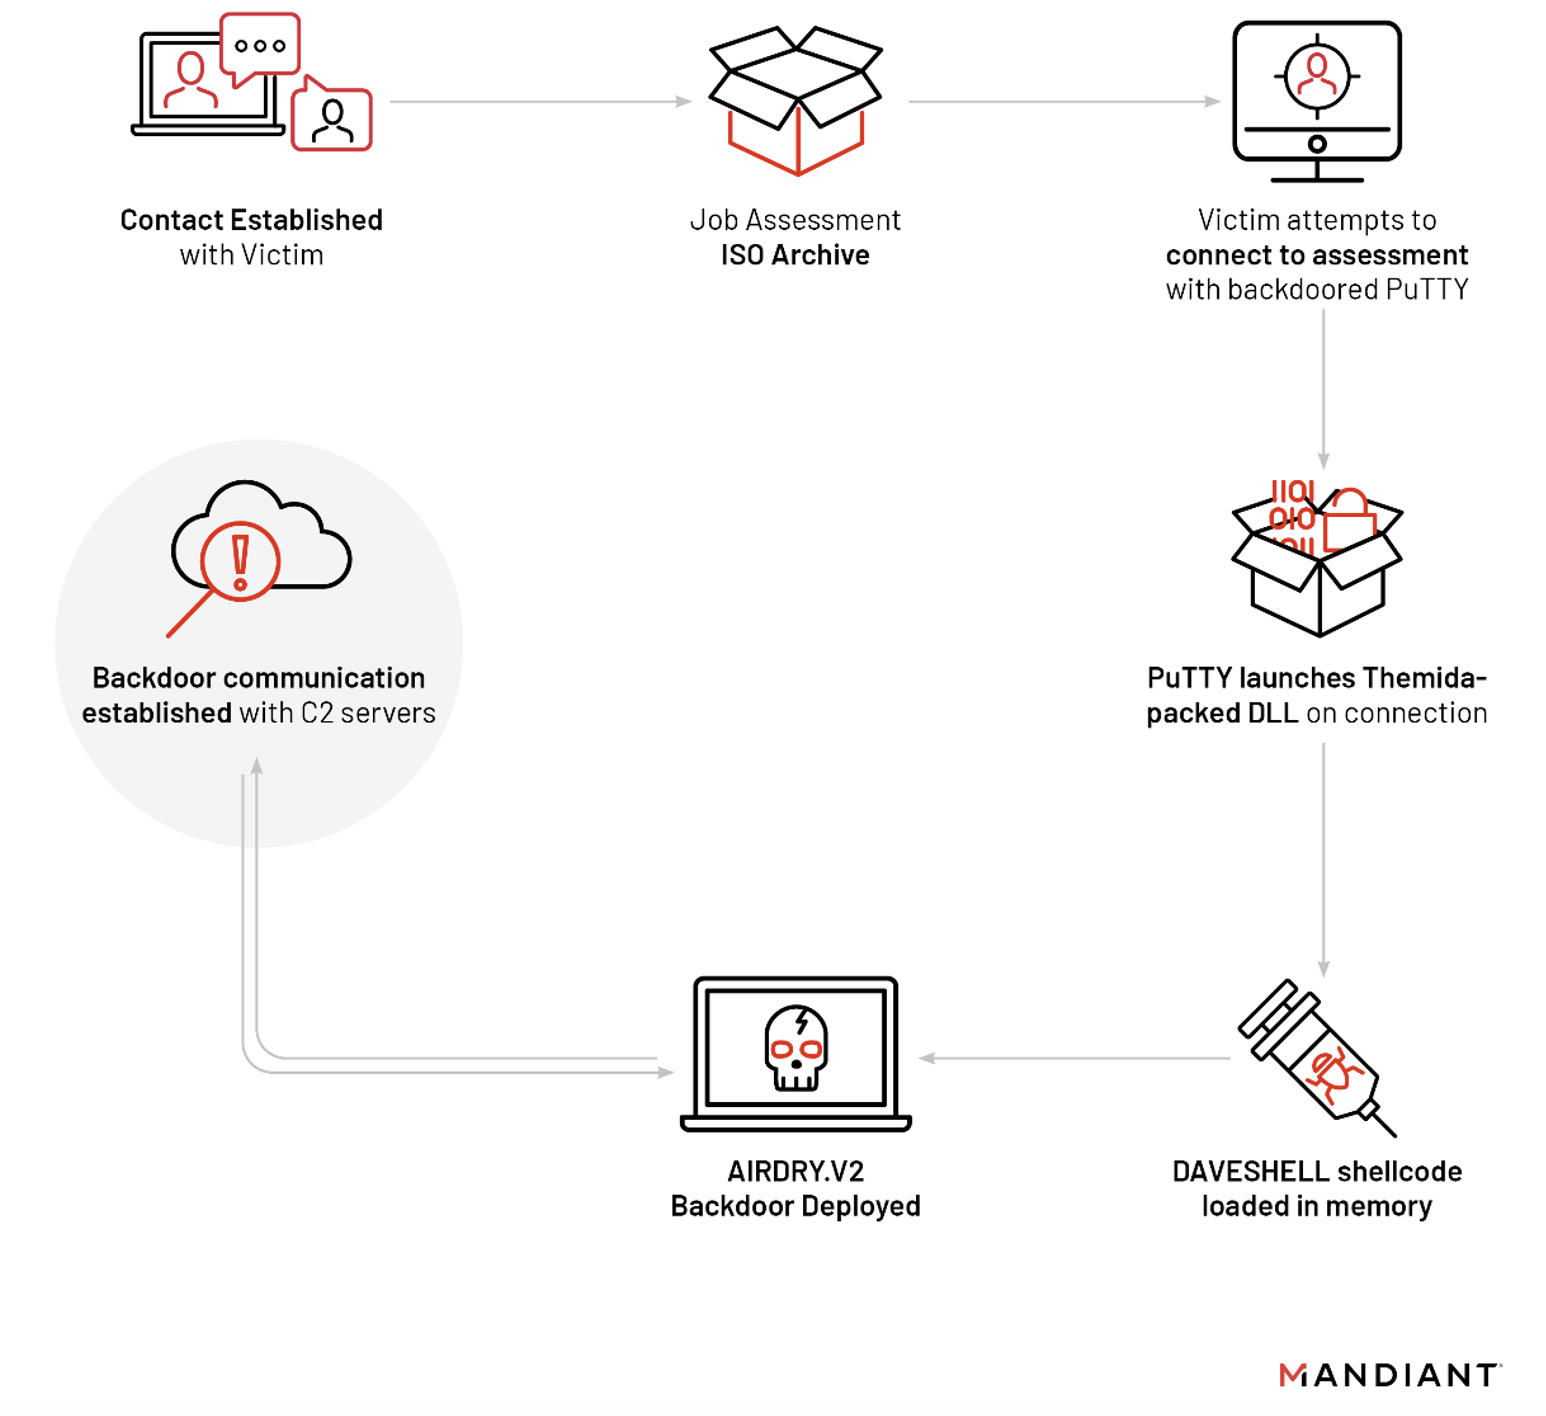
North Korea-linked threat actor UNC4034 is spreading tainted versions of the PuTTY SSH and Telnet client. In July 2022, Mandiant identified a novel spear phish methodology that was employed by North Korea-linked threat actor UNC4034. The attackers are spreading tainted versions of the PuTTY SSH and Telnet client. The attack chain starts with a fake […]