 Pierluigi Paganini
 August 15, 2022
Microsoft disrupted a hacking operation linked conducted by Russia-linked APT SEABORGIUM aimed at NATO countries. The Microsoft Threat Intelligence Center (MSTIC) has disrupted activity by SEABORGIUM (aka ColdRiver, TA446), a Russia-linked threat actor that is behind a persistent hacking campaign targeting people and organizations in NATO countries. SEABORGIUM has been active since at least 2017, […]
 Pierluigi Paganini
July 31, 2022
North Korea-linked threat actor SharpTongue is using a malicious extension on Chromium-based web browsers to spy on victims’ email accounts. North Korea-linked actor SharpTongue has been using a malicious extension on Chromium-based web browsers to spy on victims’ Gmail and AOL email accounts. Researchers from cybersecurity firm Volexity tracked the threat actors as SharpTongue, but […]
 Pierluigi Paganini
July 17, 2022
Researchers from Proofpoint warn that various APT groups are targeting journalists and media organizations since 2021. Proofpoint researchers warn that APT groups are regularly targeting and posing as journalists and media organizations since early 2021. The media sector is a privileged target for this category of attackers due to the access its operators have to […]
 Pierluigi Paganini
July 07, 2022
US authorities have issued a joint advisory warning of North Korea-linked APTs using Maui ransomware in attacks against the Healthcare sector. The FBI, CISA, and the U.S. Treasury Department issued a joint advisory that warn of North-Korea-linked threat actors using Maui ransomware in attacks aimed at organizations in the Healthcare sector. “The Federal Bureau of […]
 Pierluigi Paganini
June 26, 2022
China-linked APT Bronze Starlight is deploying post-intrusion ransomware families as a diversionary action to its cyber espionage operations. Researchers from Secureworks reported that a China-linked APT group, tracked as Bronze Starlight (APT10), is deploying post-intrusion ransomware families to cover up the cyber espionage operations. The experts observed an activity cluster involving post-intrusion ransomware such as […]
 Pierluigi Paganini
June 23, 2022
China-linked APT group Tropic Trooper has been spotted previously undocumented malware written in Nim language. Check Point Research uncovered an activity cluster with ties to China-linked APT Tropic Trooper (aka Earth Centaur, KeyBoy, and Pirate Panda) which involved the use of a previously undescribed loader (dubbed “Nimbda”) written in Nim language. The Tropic Trooper APT has been active at least […]
 Pierluigi Paganini
June 14, 2022
Organizations face the constant need to protect these APIs from attacks so they can protect organizational data. Organizations are rapidly opening their ecosystem through Application Programming Interfaces (API) by ensuring seamless access to data and interaction with external software components and services. APIs are the gateway to providing the high security of data in an […]
 Pierluigi Paganini
June 13, 2022
China-linked Gallium APT employed a previously undocumented RAT, tracked as PingPull, in recent cyber espionage campaign targeting South Asia, Europe, and Africa. China-linked Gallium APT (aka Softcell) used a previously undocumented remote access Trojan dubbed PingPull in recent attacks aimed at organizations in Southeast Asia, Europe, and Africa. Researchers from Palo Alto Networks defined the […]
 Pierluigi Paganini
June 11, 2022
Iran-linked Lyceum APT group uses a new .NET-based DNS backdoor to target organizations in the energy and telecommunication sectors. The Iran-linked Lyceum APT group, aka Hexane or Spilrin, used a new .NET-based DNS backdoor in a campaign aimed at companies in the energy and telecommunication sectors, ZScaler researchers warn. The activity of the Lyceum APT […]
 Pierluigi Paganini
June 03, 2022
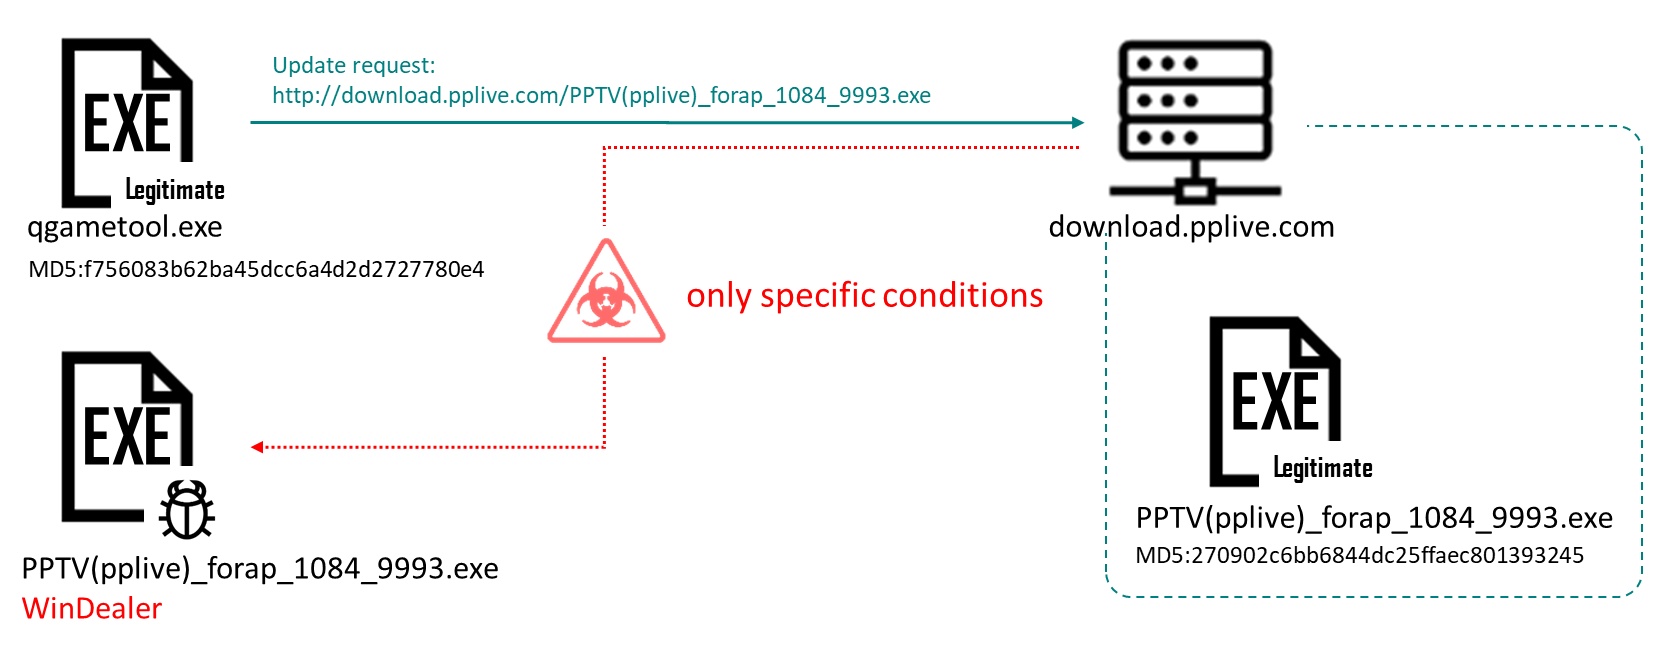
Chinese LuoYu Hackers Using Man-on-the-Side Attacks to Deploy WinDealer Backdoor An “extremely sophisticated” China-linked APT tracked as LuoYu was delivering malware called WinDealer via man-on-the-side attacks. Researchers from Kaspersky have uncovered an “extremely sophisticated” China-linked APT group, tracked as LuoYu, that has been observed using a malicious Windows tool called WinDealer. LuoYu has been active since at […]