 Pierluigi Paganini
 October 01, 2020
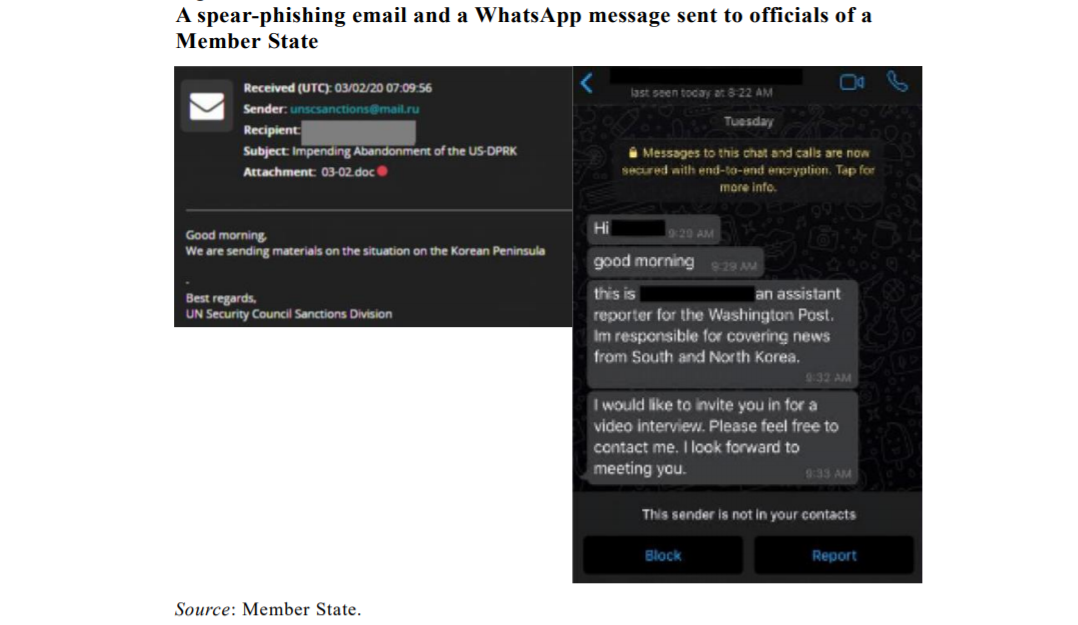
North Korea-linked APT group targeted UN Security Council officials over the past year, states a report from the United Nations organ. A North-Korea-linked cyber espionage group has launched spear-phishing attacks aimed at compromising tens of officials from the United Nations Security Council. The campaign targeted at least 28 UN officials, including at least 11 individuals […]
 Pierluigi Paganini
September 27, 2020
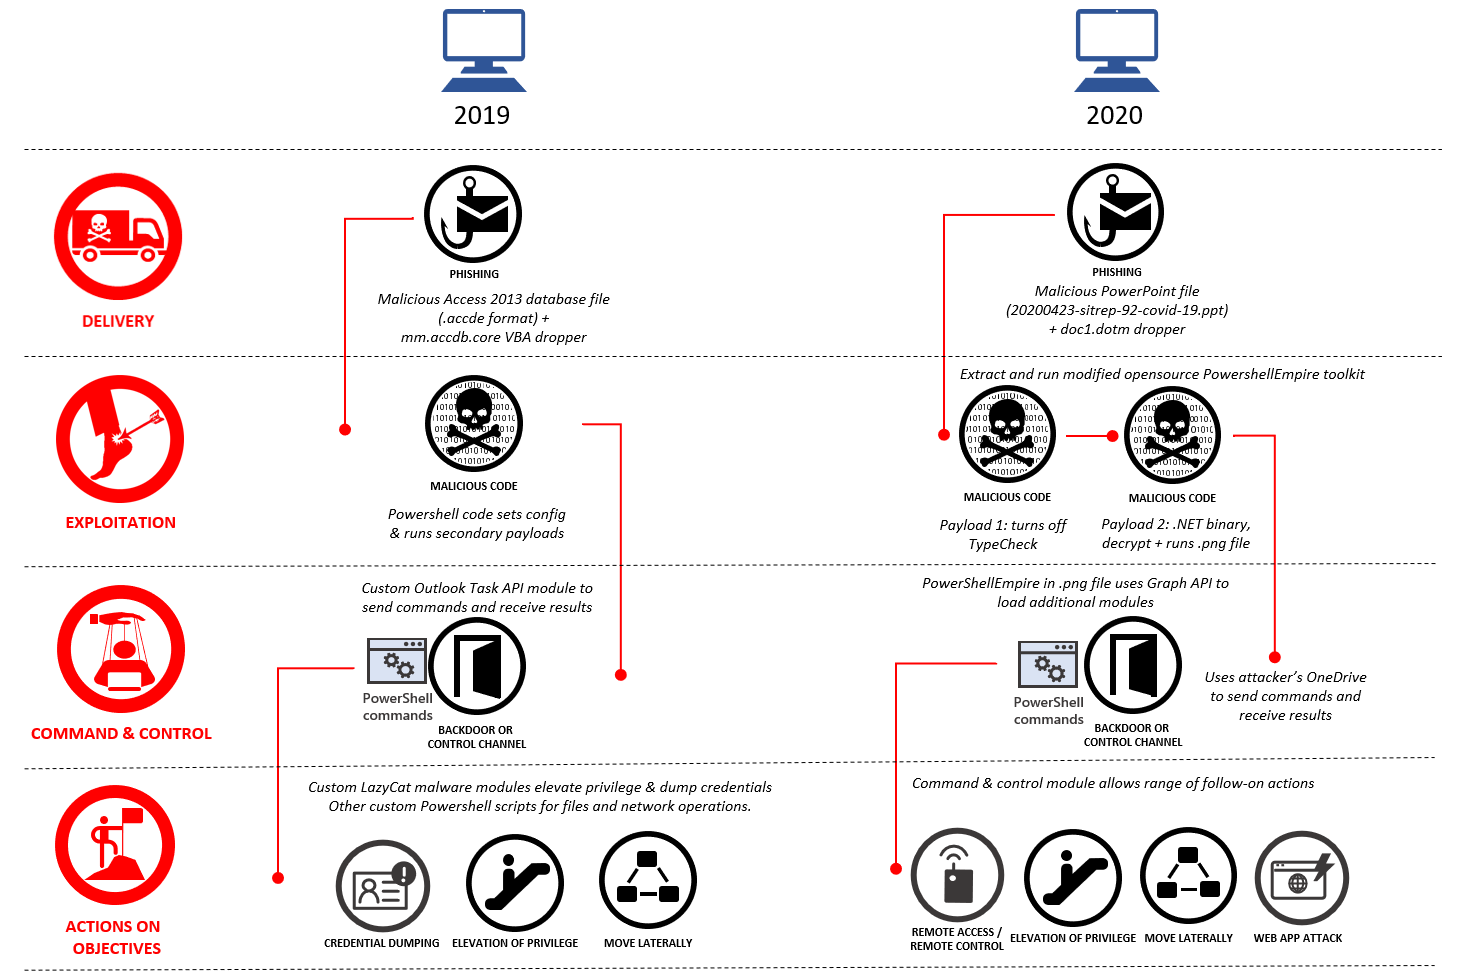
Microsoft removed 18 Azure Active Directory applications from its Azure portal that were created by a Chinese-linked APT group Gadolinium. Microsoft announced this week to have removed 18 Azure Active Directory applications from its Azure portal that were created by a China-linked cyber espionage group tracked as APT group Gadolinium (aka APT40, or Leviathan). The 18 […]
 Pierluigi Paganini
September 20, 2020
A new round of the weekly SecurityAffairs newsletter arrived! Every week the best security articles from Security Affairs free for you in your email box. Gaming hardware manufacturer Razer suffered a data leak CIRWA Project tracks ransomware attacks on critical infrastructure Popular Marketing Tool exposes data of users of dating sites Staples discloses data breach […]
 Pierluigi Paganini
September 15, 2020
CISA published an advisory on China-linked groups targeting government agencies by exploiting flaws in Microsoft Exchange, Citrix, Pulse, and F5 systems. CISA published a security advisory warning of a wave of attacks carried out by China-linked APT groups affiliated with China’s Ministry of State Security. Chinese state-sponsored hackers have probed US government networks looking for vulnerable networking […]
 Pierluigi Paganini
September 11, 2020
Microsoft reveals that state-sponsored hackers had tried to breach email accounts belonging to people involved in the US election. Microsoft announced to have detected a new wave of attacks carried out by Chinese, Iranian, and Russian state-sponsored hackers against the US election. Threat actors had tried to compromise email accounts belonging to people associated with […]
 Pierluigi Paganini
August 26, 2020
A hack-for-hire group, tracked as DeathStalker, has been targeting organizations in the financial sector since 2012 Kaspersky researchers say. DeathStalker is a hack-for-hire group discovered by Kaspersky, it has been targeting organizations worldwide, mainly law firms and financial entities, since 2012. Victim organizations are small and medium-sized businesses located in Argentina, China, Cyprus, India, Israel, […]
 Pierluigi Paganini
August 26, 2020
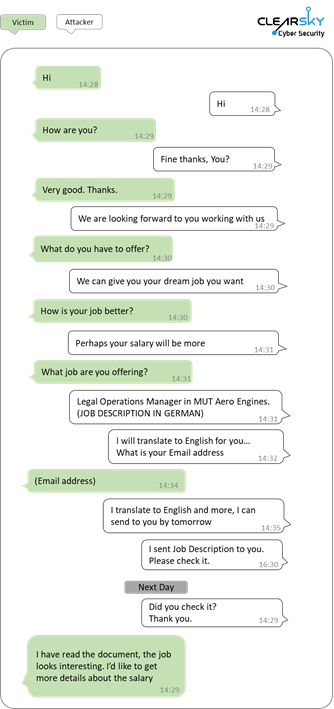
North Korea-linked Lazarus APT group targets cryptocurrency organizations with fake job offers in an ongoing spear-phishing campaign. North Korea-linked Lazarus APT group (aka HIDDEN COBRA) has been observed while using LinkedIn lures in a spear-phishing campaign targeting the cryptocurrency organizations worldwide, including in the United States, the United Kingdom, Germany, Singapore, the Netherlands, Japan. The activity of […]
 Pierluigi Paganini
August 14, 2020
Since January 2020, the North Korea-linked Lazarus APT has successfully compromised dozens of organizations in Israel and other countries. The Israeli defence ministry announced on Wednesday that it had foiled a cyber attack carried out by a foreign threat actor targeting the country’s defence manufacturers. According to the officials, the attack was launched by “an […]
Pierluigi Paganini
August 14, 2020
China-linked threat actor tracked as CactusPete was employing an updated backdoor in recent attacks targeting military and financial organizations in Eastern Europe. A China-linked APT group, tracked by Kaspersky as CactusPete (aka Karma Panda or Tonto Team), was observed using an updated backdoor in recent attacks targeting military and financial organizations in Eastern Europe. The […]
 Pierluigi Paganini
August 13, 2020
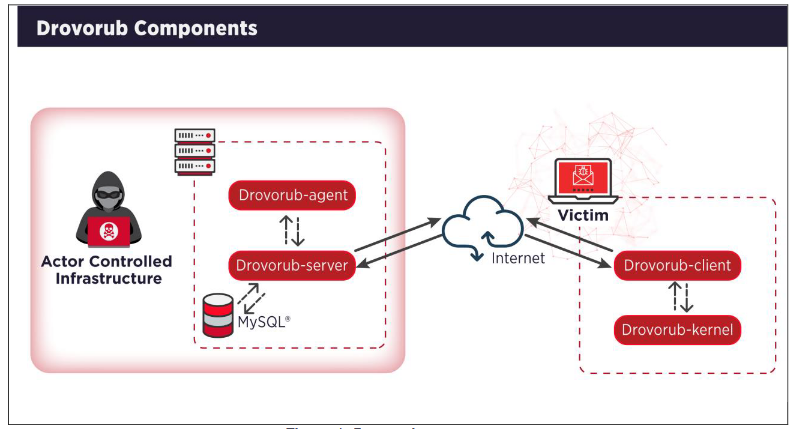
The FBI and NSA issue joint alert related to new Linux malware dubbed Drovorub that has been used by the Russia-linked APT28 group. The FBI and NSA have published a joint security alert containing technical details about a new piece of Linux malware, tracked as Drovorub, allegedly employed by Russia-linked the APT28 group. The name […]