 Pierluigi Paganini
 December 15, 2019
Iran telecommunications minister announced that for the second time in a week Iran has foiled a cyber attack against its infrastructure. Iran has foiled a new cyber-attack, the country’s telecommunications minister Mohammad Javad Azari-Jahromi says. A few days ago, the Iranian telecommunications minister Mohammad Javad Azari Jahromi, announced that the Islamic Republic had recently thwarted […]
 Pierluigi Paganini
December 12, 2019
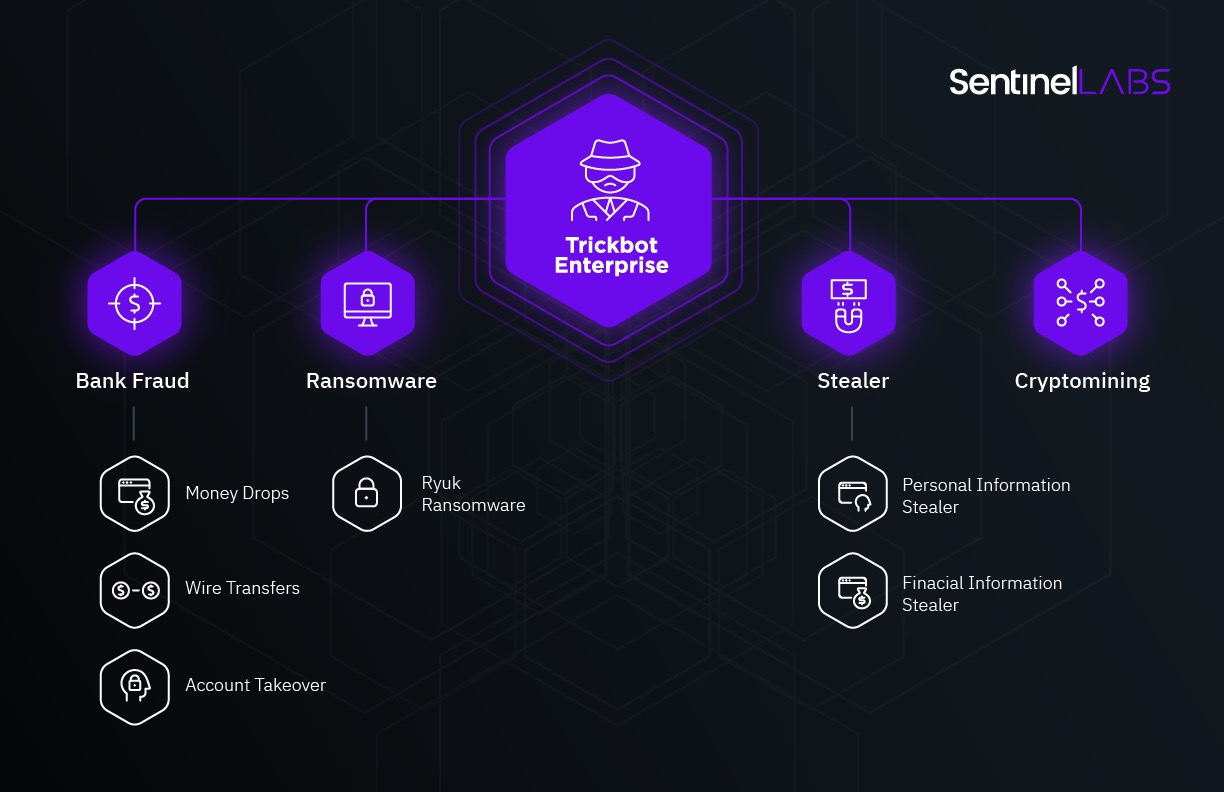
For the first time, experts shed the light on the link between the TrickBot gang and the North Korea-linked APT group Lazarus. Security experts Sentinelone have published a report that for the first time sheds the light on the link between the TrickBot crimeware and the North Korea-linked APT group Lazarus. For the first time, experts shed the light on the link between […]
 Pierluigi Paganini
December 07, 2019
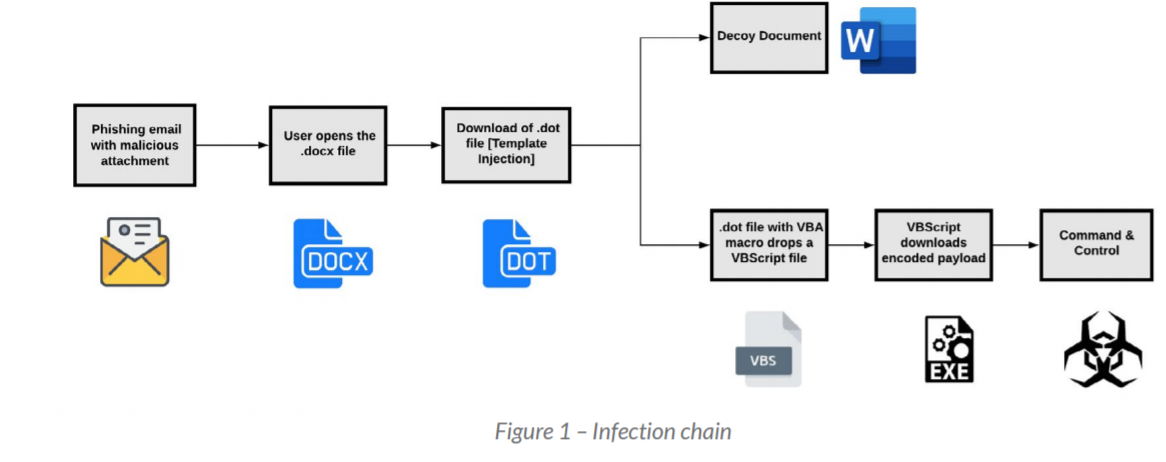
Russia-linked Gamaredon cyberespionage group has been targeting Ukrainian targets, including diplomats, government and military officials. Russia linked APT group tracked as Gamaredon has been targeting several Ukrainian diplomats, government and military officials, and law enforcement. The Gamaredon attacks against Ukraine don’t seem to have stopped. In June malware researchers from Cybaze-Yoroi spotted a new suspicious […]
 Pierluigi Paganini
December 05, 2019
Experts spotted a piece of malware dubbed ZeroCleare that has been used in highly targeted attacks aimed at energy and industrial organizations in the Middle East. Security experts at IBM X-Force found a piece of malware dubbed ZeroCleare (the name ZeroCleare comes from the path in the binary file) that has been used in highly targeted […]
 Pierluigi Paganini
November 29, 2019
Group-IB, has analyzed key recent changes to the global cyberthreat landscape in the “Hi-Tech Crime Trends 2019/2020” report. Group-IB, a Singapore-based cybersecurity company that specializes in preventing cyberattacks, has analyzed key recent changes to the global cyberthreat landscape. According to Group-IB’s experts, the most frustrating trend of 2019 was the use of cyberweapons in military operations. The […]
 Pierluigi Paganini
November 25, 2019
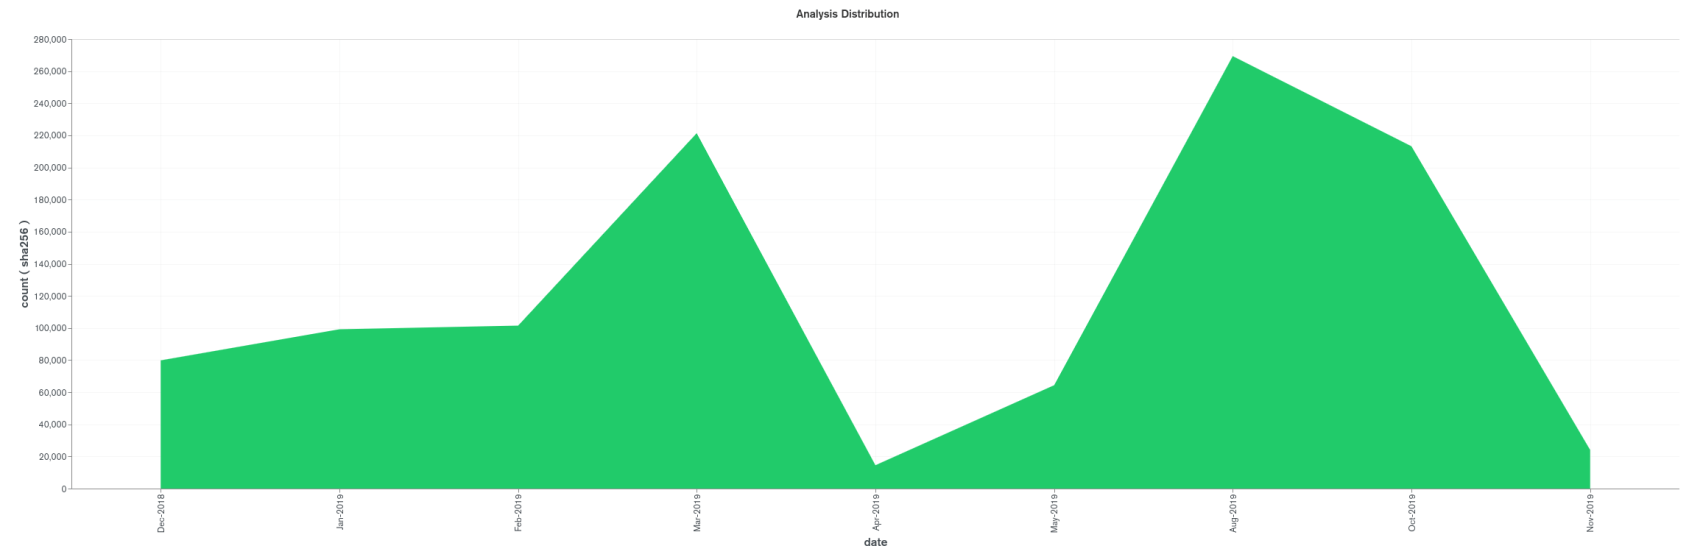
Malware Hunter – One year after its launch, Marco Ramilli shared the results of its project that has analyzed more than 1 Million malware samples. Malware Hunter – One year ago I decided to invest in static Malware Analysis automation by setting up a full-stack environment able to grab samples from common opensources and to […]
 Pierluigi Paganini
November 15, 2019
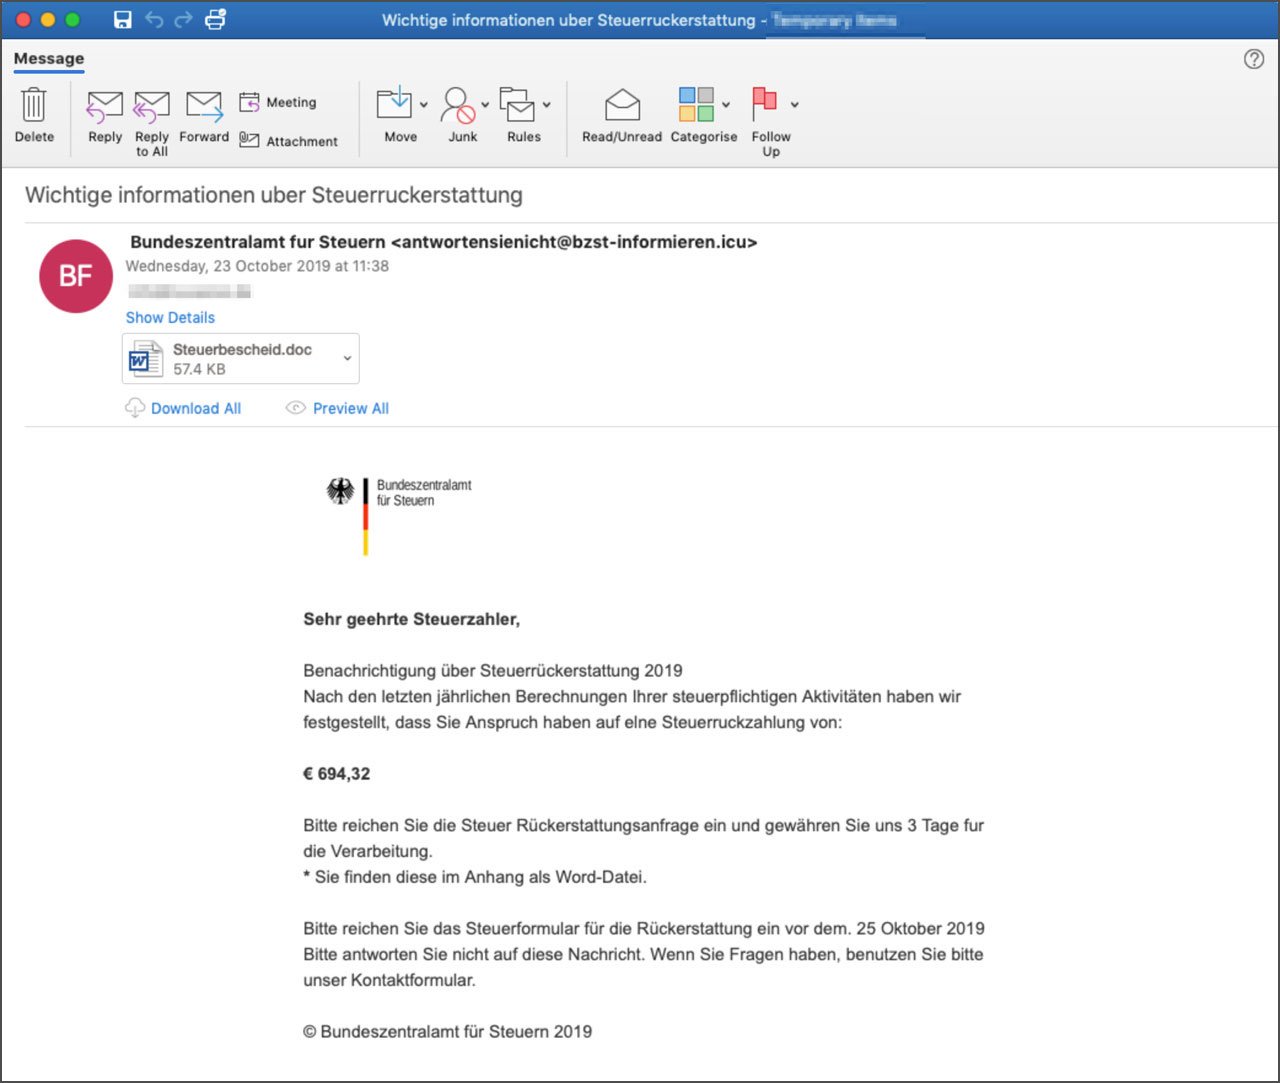
A new threat actor tracked as TA2101 is conducting malware campaigns using email to impersonate government agencies in the United States, Germany, and Italy. A new threat actor, tracked as TA2101, is using email to impersonate government agencies in the United States, Germany, and Italy to multiple families of malware, deliver ransomware, and banking Trojans. The […]
 Pierluigi Paganini
November 05, 2019
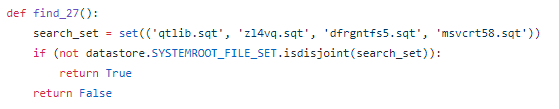
Kaspersky discovered a previously unknown APT group, tracked as DarkUniverse, by analyzing Shadow Brokers’ “Lost in Translation” data dump. In 2017, a hacker group known as the Shadow Brokers stolen malware and hacking tools from the arsenal of the NSA-Linked Equation Group, then it published online the data dump called “Lost in Translation.” The dump […]
 Pierluigi Paganini
October 31, 2019
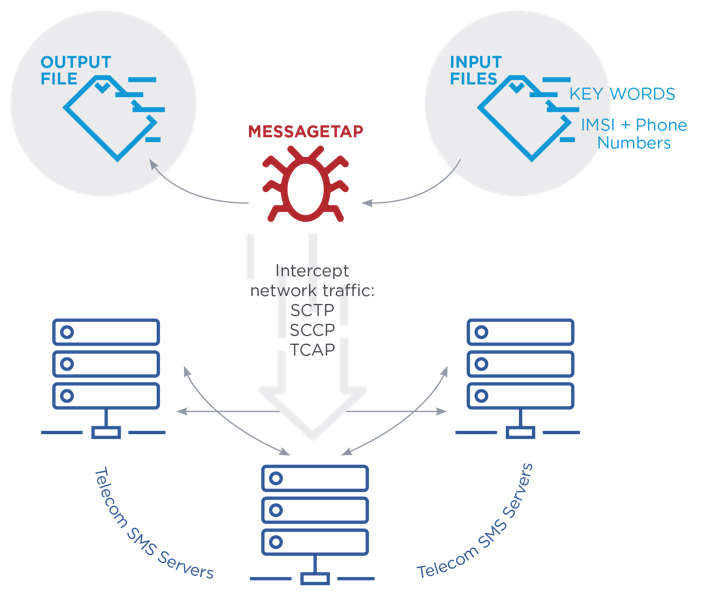
China-linked APT41 group is targeting telecommunications companies with a new piece of malware used to spy on text messages of highly targeted individuals. Researchers at FireEye discovered a new backdoor tracked as MessageTap that China-linked APT41 group are using to spy on text messages sent or received by highly targeted individuals The experts found the […]
 Pierluigi Paganini
October 25, 2019
Experts at Fortinet analyzed NukeSped malware samples that share multiple similarities with malware associated with North Korea-linked APTs. Fortinet has analyzed the NukeSped RAT that is believed to be a malware in the arsenal of the Lazarus North-Korea linked APT group. The attribution to the Lazarus group is based on the similarities with other malware […]