 Pierluigi Paganini
 October 15, 2019
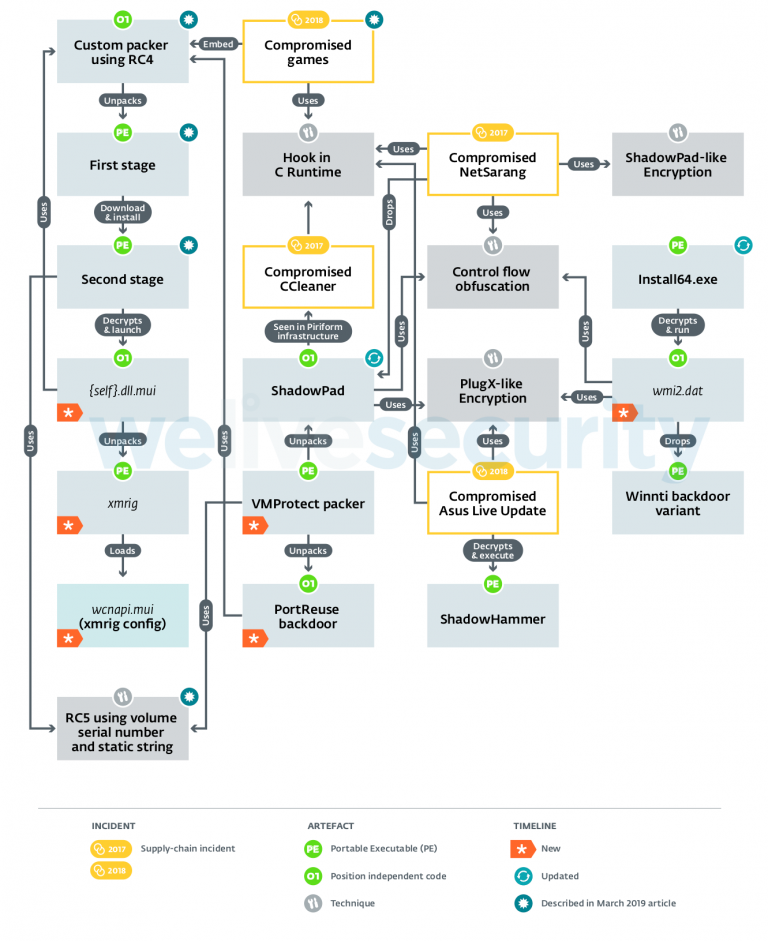
Winnti Group is back with a new modular Win backdoor that was used to infect the servers of a high-profile Asian mobile hardware and software manufacturer. Security experts at ESET revealed that Winnti Group continues to update its arsenal, they observed that the China-linked APT group using a new modular Windows backdoor that they used to infect the […]
 Pierluigi Paganini
October 13, 2019
Iran-linked APT group Charming Kitten employed new spear-phishing methods in attacks carried out between August and September. Security experts at ClearSky analyzed attacks recently uncovered by Microsoft that targeted a US presidential candidate, government officials, journalists, and prominent expatriate Iranians. Microsoft Threat Intelligence Center (MSTIC) observed the APT group making more than 2,700 attempts to […]
 Pierluigi Paganini
October 12, 2019
FireEye Mandiant discovered that the FIN7 hacking group added new tools to its cyber arsenal, including a module to target remote administration software of ATM vendor. Security experts at FireEye Mandiant discovered that the FIN7 hacking group has added new tools to its arsenal, including a new loader and a module that hooks into the legitimate […]
 Pierluigi Paganini
October 09, 2019
NSA is warning of multiple state-sponsored cyberespionage groups exploiting enterprise VPN Flaws Last week, the UK’s National Cyber Security Centre (NCSC) reported that advanced persistent threat (APT) groups have been exploiting recently disclosed VPN vulnerabilities in enterprise VPN products in attacks in the wild. Threat actors leverage VPN vulnerabilities in Fortinet, Palo Alto Networks and Pulse Secure, to […]
 Pierluigi Paganini
October 06, 2019
The UK’s National Cyber Security Centre (NCSC) warns of attacks exploiting recently disclosed VPN vulnerabilities in Fortinet, Palo Alto Networks and Pulse Secure According to the UK’s National Cyber Security Centre (NCSC), advanced persistent threat (APT) groups have been exploiting recently disclosed VPN vulnerabilities in enterprise VPN products in attacks in the wild. Threat actors […]
 Pierluigi Paganini
October 03, 2019
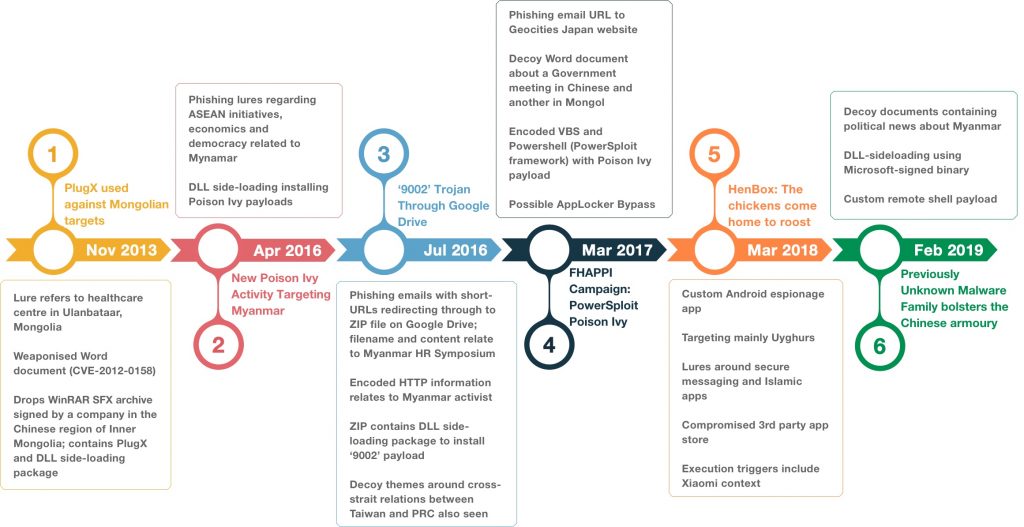
Security experts linked a number of cyber-espionage campaigns observed over the years to the same Chinese threat actor, tracked as PKPLUG. Security experts linked a number of cyber-espionage campaigns observed over the years to the same Chinese threat actor, tracked as PKPLUG. The name comes from the threat actor using PlugX inside ZIP archives containing […]
 Pierluigi Paganini
September 26, 2019
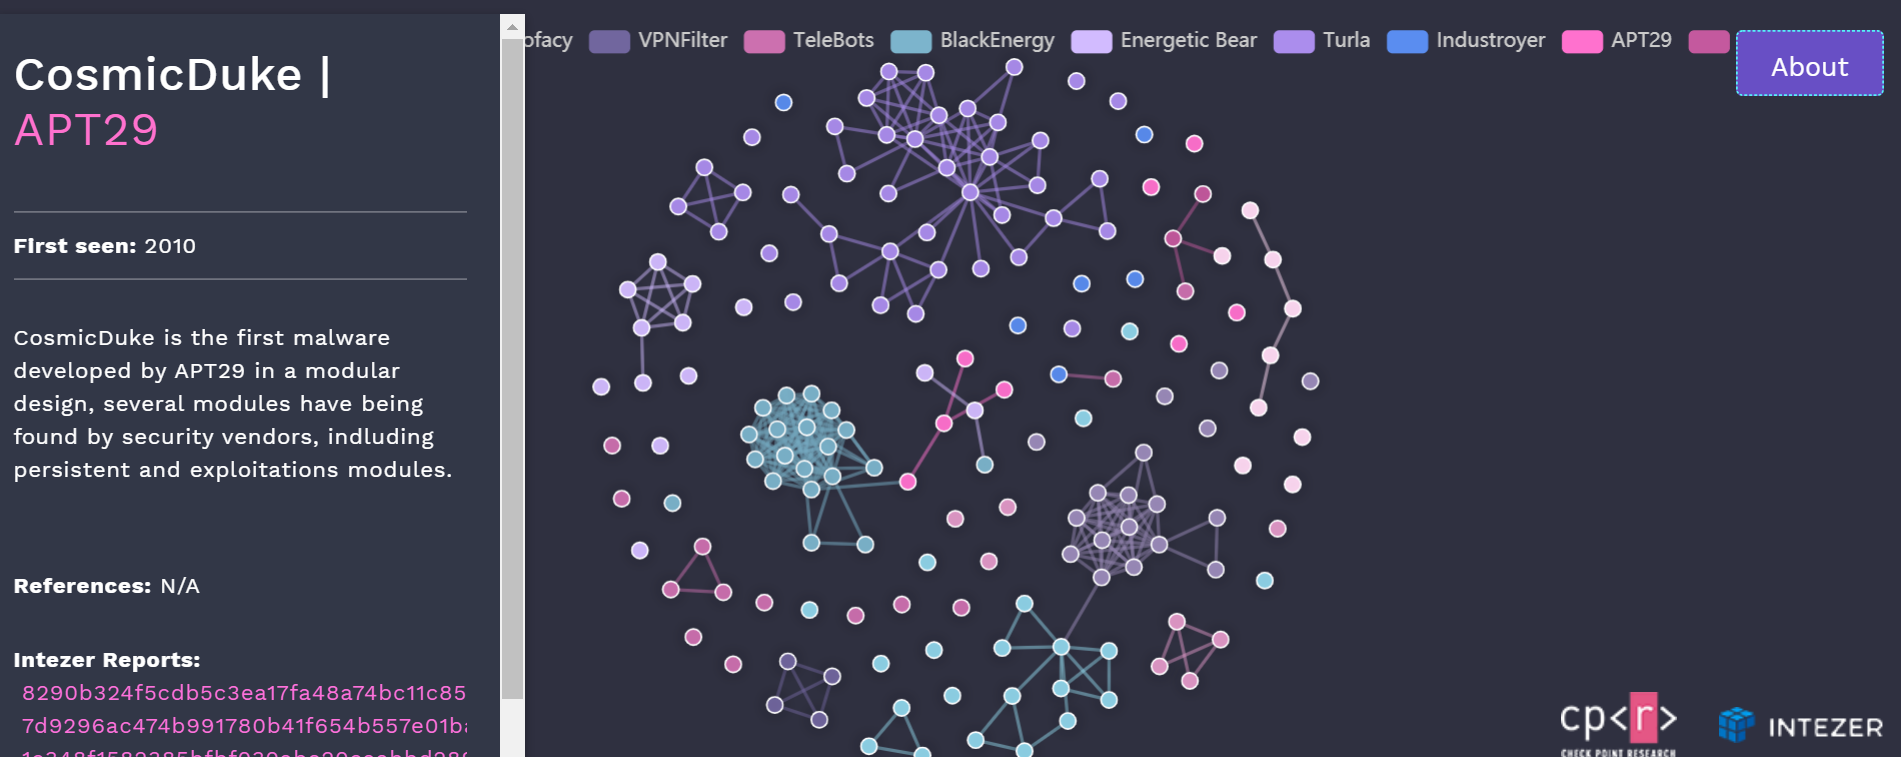
A joint research from Intezer and Check Point Research shows connections between nearly 2,000 malware samples developed by Russian APT groups. A joint research from Intezer and Check Point Research shed light on Russian hacking ecosystem and reveals connections between nearly 2,000 malware samples developed by Russian APT groups. The report is extremely interesting because gives to the analysts […]
 Pierluigi Paganini
September 24, 2019
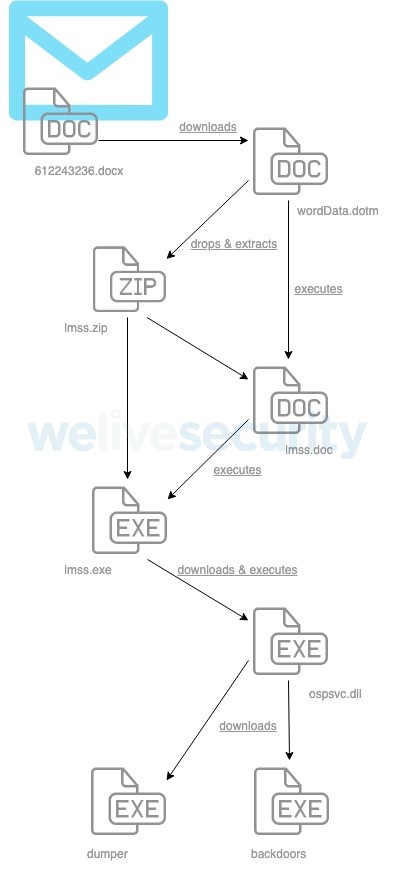
Security experts at ESET have uncovered a new campaign carried out by Russia-linked Fancy Bear APT group aimed at political targets. Security researchers at ESET have uncovered a new campaign carried out by Russia-linked Fancy Bear APT group (i.e. APT28, Sednit, Sofacy, Zebrocy, and Strontium) aimed at political targets. In the recent attacks, the hackers […]
 Pierluigi Paganini
September 24, 2019
Kaspersky experts spotted a new piece of ATM malware, dubbed ATMDtrack, that was developed and used by North Korea-linked hackers. Kaspersky researchers discovered a new piece of ATM malware, tracked as ATMDtrack, that was developed and used by North Korea-linked hackers. Threat actors deployed the malware on ATM systems to steal payment card details of […]
 Pierluigi Paganini
September 23, 2019
Symantec spotted a new threat actor, tracked as TortoiseShell, that is compromising IT providers to target their specific customers. Symantec researchers spotted a new threat group, tracked as TortoiseShell, that is compromising IT providers to target their specific customers. The group was first spotted in 2018, but experts speculate that it has been active for […]