 Pierluigi Paganini
 September 17, 2019
Australia ‘s intelligence is sure that China is behind the cyberattacks that hit its parliament and political parties, but decided to not publicly accuse it. According to the Reuters agency, Australia’s intelligence has evidence that the attacks that hit its parliament and political parties were orchestrated by China. Anyway the Australian government decided to not […]
 Pierluigi Paganini
September 13, 2019
The US Treasury placed sanctions on three North Korea-linked hacking groups, the Lazarus Group, Bluenoroff, and Andarial. The US Treasury sanctions on three North Korea-linked hacking groups, the Lazarus Group, Bluenoroff, and Andarial. The groups are behind several hacking operations that resulted in the theft of hundreds of millions of dollars from financial institutions and cryptocurrency exchanges […]
 Pierluigi Paganini
August 27, 2019
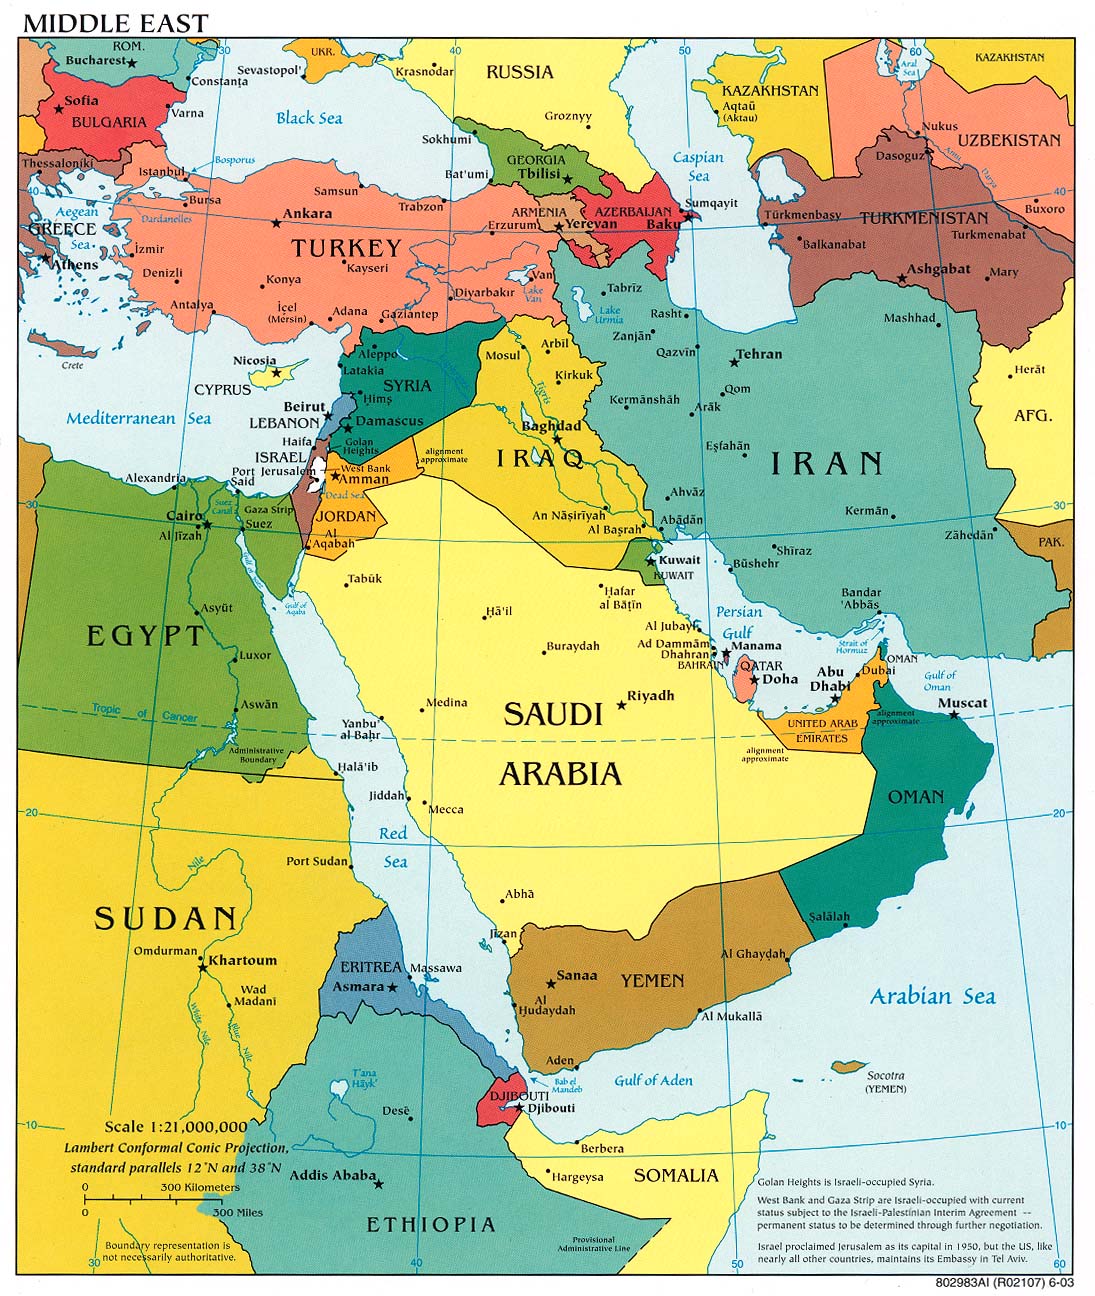
A recently reported APT group dubbed Lyceum group targets Oil and Gas organizations in the Middle East with simple techniques. The activity of the Lyceum APT group was first documented earlier in August by researchers at ICS security firm Dragos that tracked it as Hexane. Security experts at Dragos Inc. reported that Hexane is targeting organizations […]
 Pierluigi Paganini
August 07, 2019
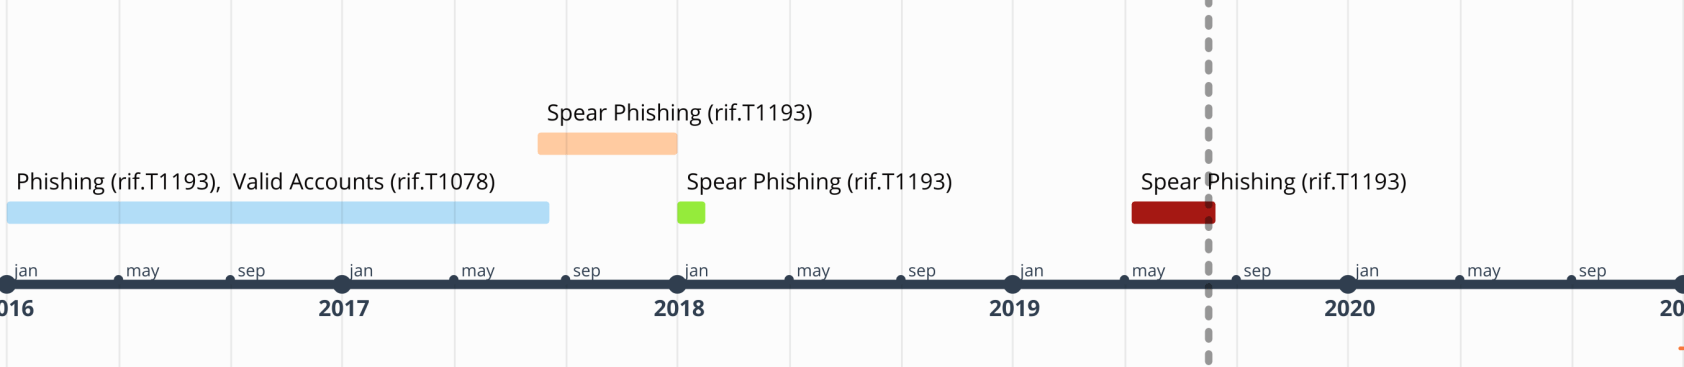
Security researcher Marco Ramilli presents a comparative analysis of attacks techniques adopted by the Iran-Linked OilRig APT group. Today I’d like to share a comparative analysis of OilRig techniques mutation over time. In particular I will refer to great analyses made by Paloalto UNIT 42 plus my own ones (HERE, HERE, HERE, etc..) and more personal thoughts. I would define this group […]
 Pierluigi Paganini
August 05, 2019
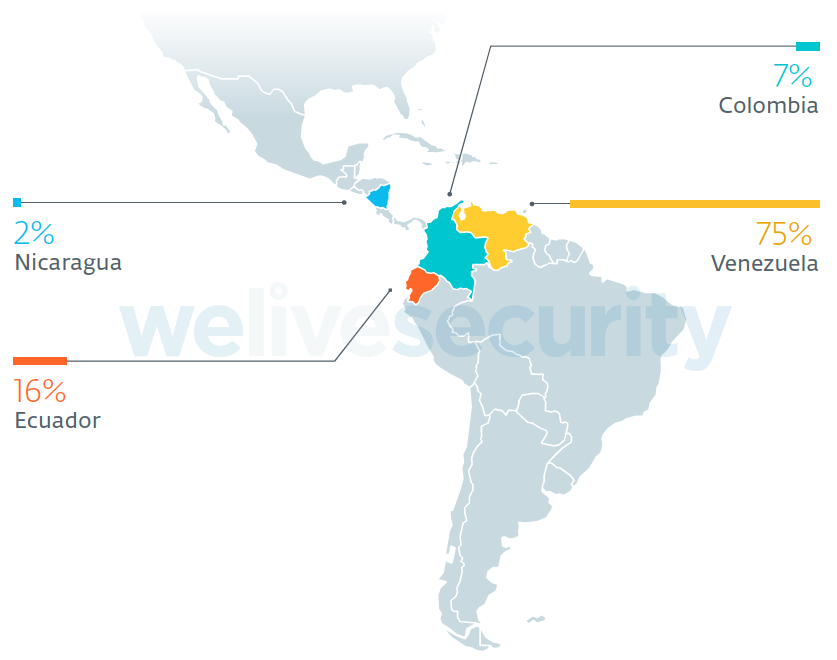
Security experts from ESET uncovered a cyber-espionage group tracked as Machete that stole sensitive files from the Venezuelan military. Security experts from ESET reported that a cyberespionage group tracked as Machete has stolen sensitive files from the Venezuelan military. The group has been active since 2010 and hit military organizations and other high-profile targets worldwide. […]
 Pierluigi Paganini
July 18, 2019
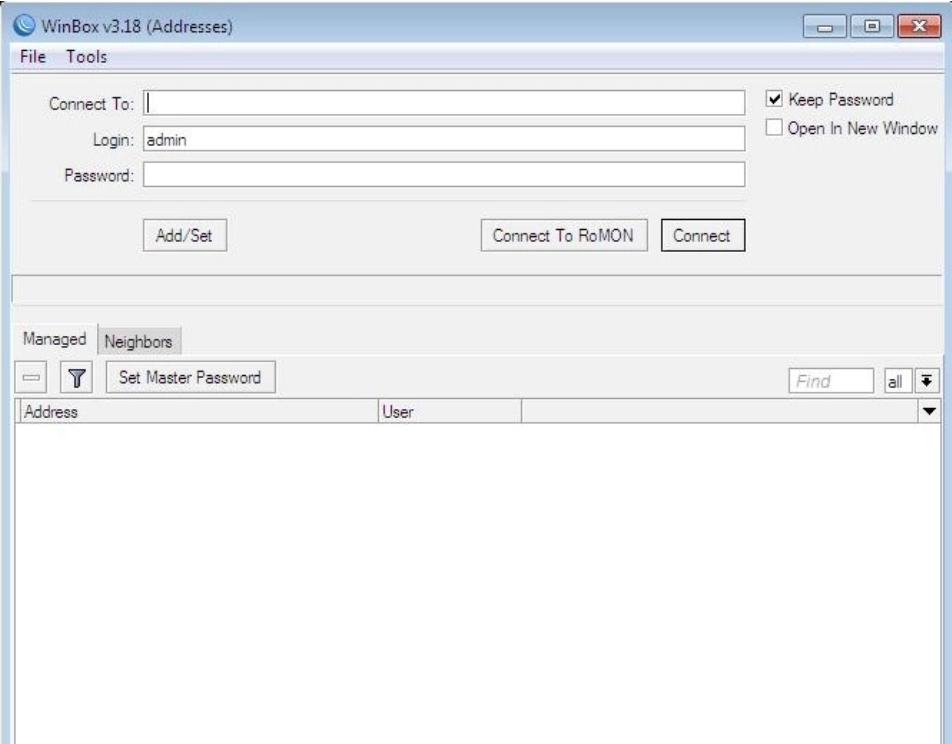
Experts at AT&T’s Alien Labs recently discovered an ongoing campaign conducted by StrongPity threat actor that abuses malicious WinBox installers to infect victims. AT&T’s Alien Labs experts recently discovered an ongoing campaign conducted by StrongPity APT group that abuses malicious WinBox installers to infect victims. The activity of the group was initially uncovered in 2016 […]
 Pierluigi Paganini
July 17, 2019
Kaspersky researchers revealed that since earlier this year, Russia-linked APT group Turla used new variants of the KopiLuwak Trojan in targeted attacks. Security experts at Kaspersky revealed that the Russia-linked APT group Turla used new variants of the KopiLuwak Trojan in targeted attacks since early 2019. The Turla APT group (aka Snake, Uroburos, Waterbug, Venomous Bear and KRYPTON) has been active since at least 2007 targeting […]
 Pierluigi Paganini
July 12, 2019
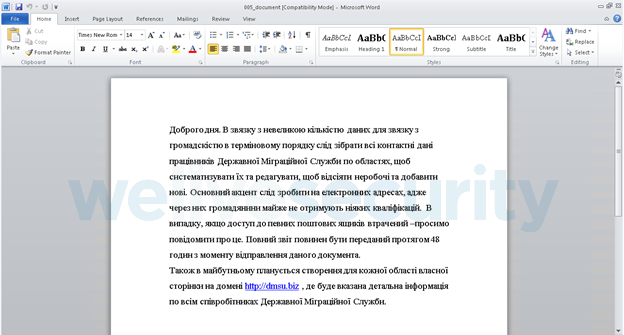
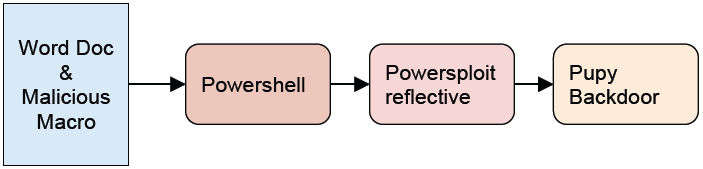
The CVE-2019-1132 flaw addressed by Microsoft this month was exploited by Buhtrap threat actor to target a government organization in Eastern Europe. Microsoft Patch Tuesday updates for July 2019 address a total of 77 vulnerabilities, including two privilege escalation flaws actively exploited in the wild. The first vulnerability, tracked as CVE-2019-1132, affects the Win32k component and could be […]
 Pierluigi Paganini
July 09, 2019
The malware samples shared by USCYBERCOM last week were first detected in December 2016 in attacks attributed to Iran-linked APT33. Last week the United States Cyber Command (USCYBERCOM) uploaded to VirusTotal a malware used by Iran-linked APT33 group in attacks in Dec 2016 and Jan 2017. Now experts at Kaspersky confirmed that the malware was […]
 Pierluigi Paganini
July 07, 2019
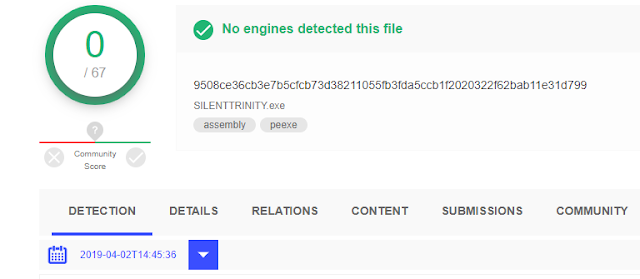
Croatia government agencies have been targeted by unknown hackers with a new piece of malware tracked as SilentTrinity. A mysterious group of hackers carried out a series of cyber attacks against Croatian government agencies, infecting employees with a new piece of malware tracked as SilentTrinity. The SilentTrinity malware can take control over an infected computer, […]