 Pierluigi Paganini
 July 03, 2019
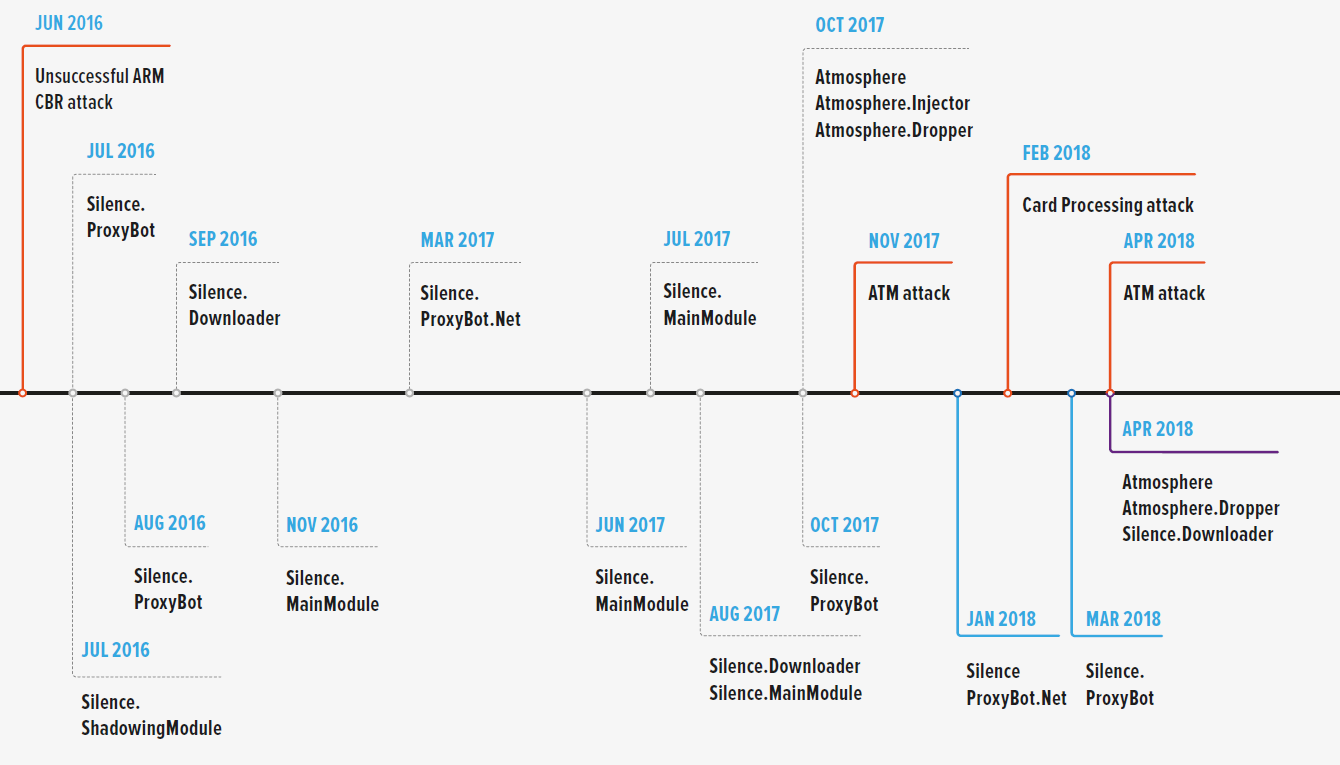
Group-IB believes Silence APT, the Russian-speaking cybercriminal gang, is likely to be behind the attack on Dutch Bangla Bank’s ATMs resulting in the theft of $3M, Group-IB, an international company that specializes in preventing cyber attacks, has established that Silence APT, a Russian-speaking cybercriminal group is likely to be behind the brazen attack on Dutch […]
 Pierluigi Paganini
June 28, 2019
Allegedly Western nation-state actors breached the systems of Russian tech giant Yandex in 2018, the attack involved a new variant of the Regin malware. According to the Reuters, Western state-sponsored hackers breached the systems of the Russian tech giant Yandex in 2018, the attack involved a new variant of the Regin malware. The Regin malware has been […]
 Pierluigi Paganini
June 08, 2019
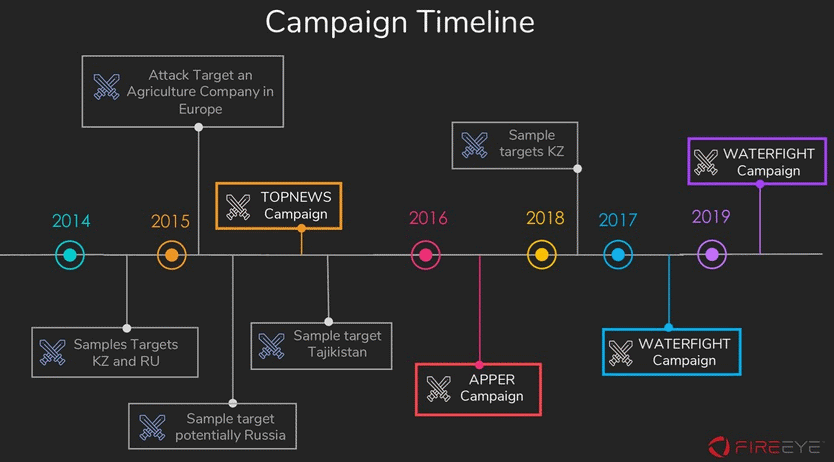
A security researcher found new evidence of activities conducted by the ICEFOG APT group, also tracked by the experts as Fucobha. Chi-en (Ashley) Shen, a senior security researcher at FireEye, collected evidence that demonstrates that China-linked APT group ICEFOG (aka Fucobha) is still active. The activities of the APT group were first uncovered by Kaspersky […]
 Pierluigi Paganini
June 04, 2019
A few hours ago, a new email hacking tool dubbed Jason and associated with the OilRig APT group was leaked through the same Telegram channel used to leak other tools. A new email hacking tool associated with the Iran-linked OilRig APT group was leaked through the same Telegram channel that in April leaked the source […]
Pierluigi Paganini
May 30, 2019
Chinese Cyber-Spies Target Government Organizations in Middle East Chinese APT group Emissary Panda has been targeting government organizations in two different countries in the Middle East. Experts at Palo Alto Networks reported that the Chinese APT group Emissary Panda (aka APT27, TG-3390, Bronze Union, and Lucky Mouse) has been targeting government organizations in two different […]
 Pierluigi Paganini
May 21, 2019
A recent MuddyWater campaign tracked as BlackWater shows that the APT group added new anti-detection techniques to its arsenal. Security experts at Cisco Talos attributed the recently spotted campaign tracked as “BlackWater” to the MuddyWater APT group (aka SeedWorm and TEMP.Zagros). The researchers also pointed out that the cyber espionage group has been updating its tactics, techniques, […]
 Pierluigi Paganini
May 20, 2019
Security researchers from Chronicle, Alphabet’s cyber-security division, have spotted a Linux variant of the Winnti backdoor. Security experts from Chronicle, the Alphabet’s cyber-security division, have discovered a Linux variant of the Winnti backdoor. It is the first time that researchers found a Linux version of the backdoor user by China-linked APT groups tacked as Winnti. […]
 Pierluigi Paganini
May 17, 2019
The German newspaper Der Spiegel revealed that the software company behind TeamViewer was compromised in 2016 by Chinese hackers. China-linked hackers breached German software company behind TeamViewer in 2016, this news was reported by the German newspaper Der Spiegel According to the media outlet, Chinese state-sponsored hackers used the Winnti trojan malware to infect the systems […]
 Pierluigi Paganini
May 14, 2019
The North Korea-linked APT group ScarCruft (aka APT37 and Group123) continues to expand its arsenal by adding a Bluetooth Harvester. North Korea-linked APT group ScarCruft (aka APT37, Reaper, and Group123) continues to expand its arsenal by adding a Bluetooth Harvester. ScarCruft has been active since at least 2012, it made the headlines in early February […]
 Pierluigi Paganini
May 07, 2019
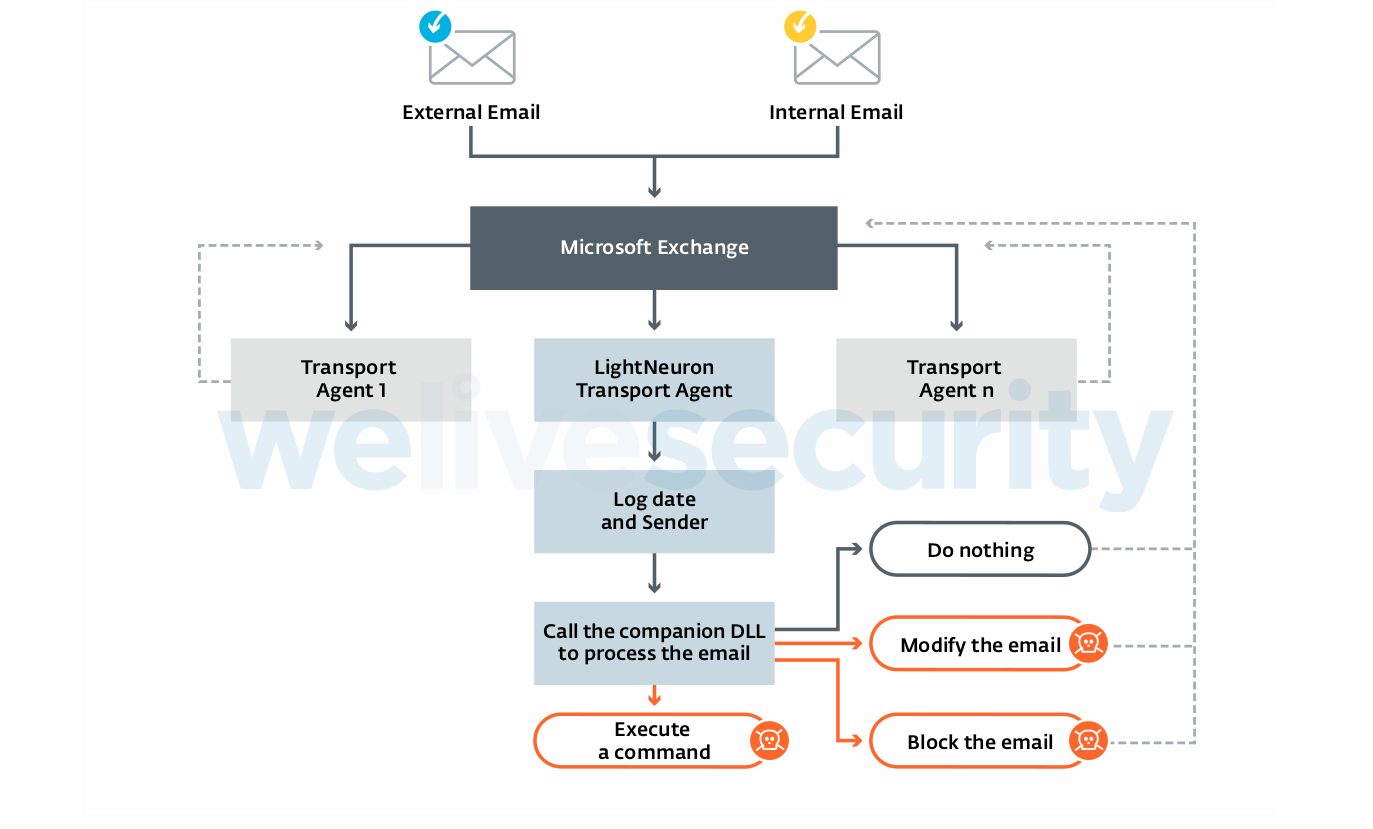
Russia-linked APT group Turla has been using a sophisticated backdoor, dubbed LightNeuron, to hijack Microsoft Exchange mail servers. Russia-linked APT group Turla has been using a sophisticated backdoor, dubbed LightNeuron, to hijack Microsoft Exchange mail servers. Turla group (also known as Waterbug, Venomous Bear and KRYPTON) has been active since at least 2007 targeting government […]