 Pierluigi Paganini
 May 05, 2017
According to experts from the Fox-IT firm, the notorious Russian Snake APT group is ready to target also Mac users with a new variant of its malicious code. The sophisticated Russian Snake APT group is back and is leveraging on new malware to target Mac users.The Snake APT group, also known as Turla or Uroburos, has ported its Windows […]
 Pierluigi Paganini
May 03, 2017
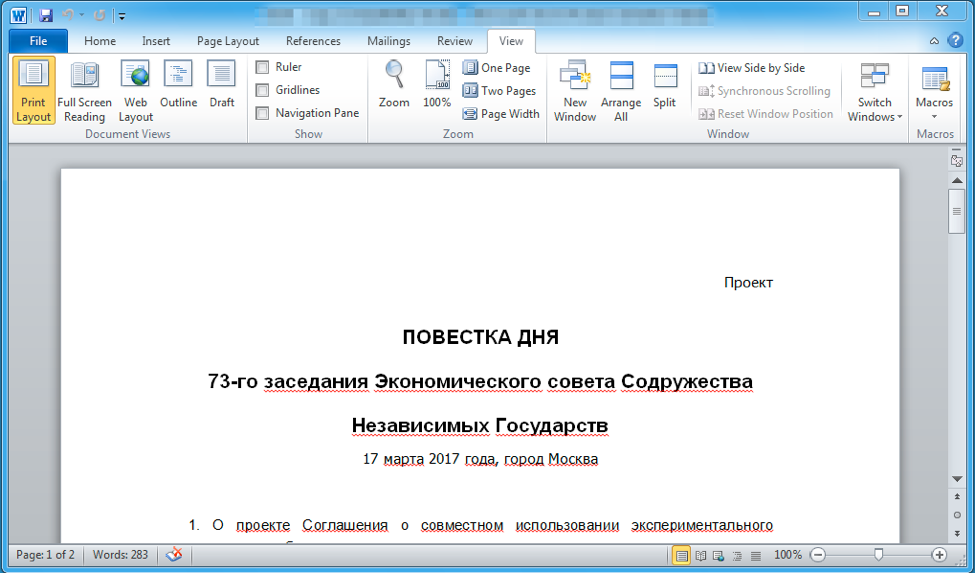
Malware researchers at security firm ProofPoint reported the Chinese TA459 APT has exploited the CVE-2017-0199 vulnerability to target Financial firms. The notorious cyber espionage group tracked as TA459 APT has targeted analysts working at major financial firms using the recently patched CVE-2017-0199 Microsoft Office vulnerability. Experts at Proofpoint published a detailed analysis of the espionage campaign conducted […]
 Pierluigi Paganini
May 02, 2017
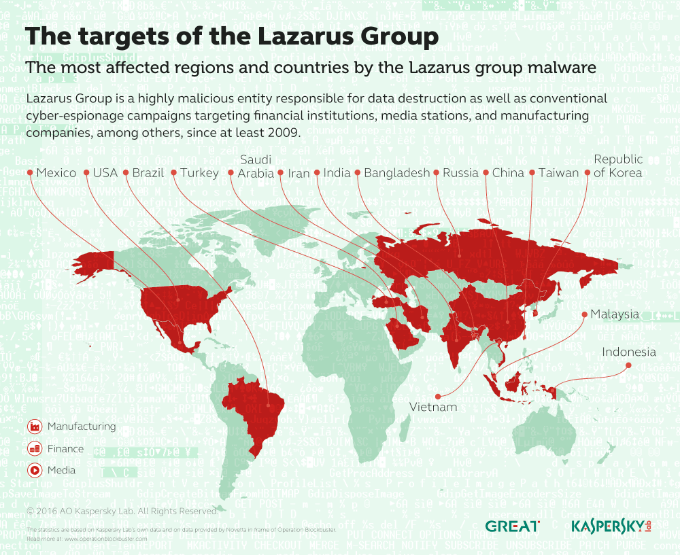
Kaspersky is currently monitoring the activities of more than 100 threat actors, from the From Lazarus APT to StoneDrill. According to the experts from KasperskyLab, the infamous Lazarus APT group, aka BlueNoroff, is the most dangerous threat against financial institutions worldwide. The activity of the Lazarus Group surged in 2014 and 2015, its members used mostly custom-tailored malware […]
 Pierluigi Paganini
April 22, 2017
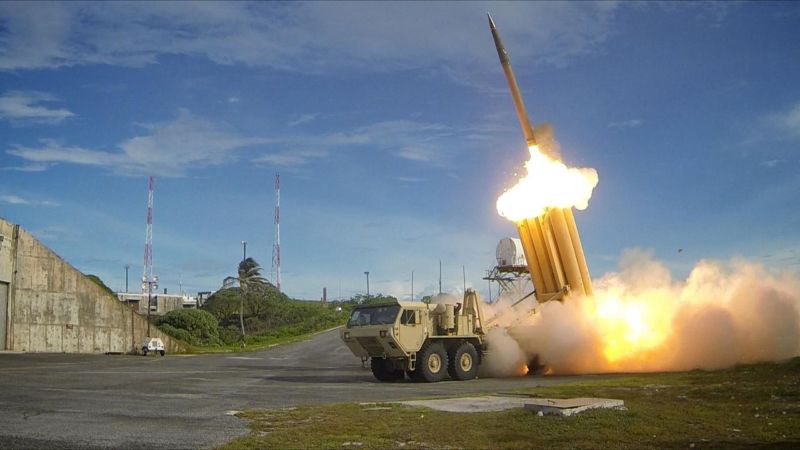
According to researchers at FireEye, Chinese hackers targeted the South Korean Terminal High Altitude Area Defense (THAAD) missile system. According to a new investigation conducted by security firm FireEye, Chinese hackers are trying to hack systems used by South Korea military to interfere with the deployment of an anti-ballistic weapons system. The news was confirmed […]
 Pierluigi Paganini
April 04, 2017
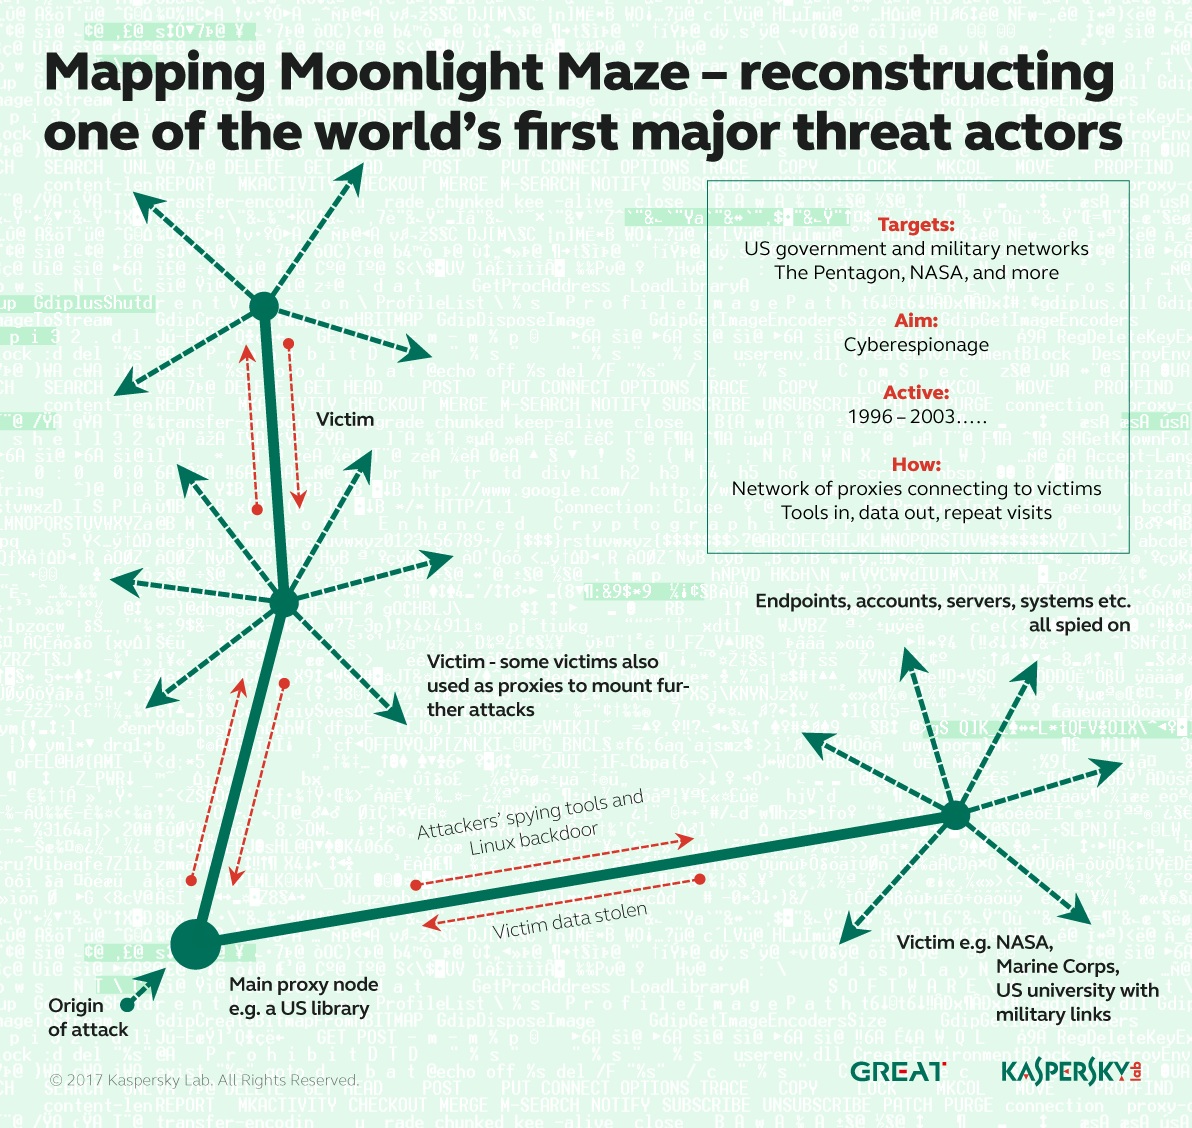
Experts at Kaspersky presented the findings of its research that definitively connect the Moonlight Maze cyber espionage campaigns to the Turla APT group. One year ago, the researcher Thomas Rid at the Security Analyst Summit disclosed the alleged links between the Moonlight Maze cyber espionage operation of mid 1990s and the Turla APT. Today at […]
 Pierluigi Paganini
March 23, 2017
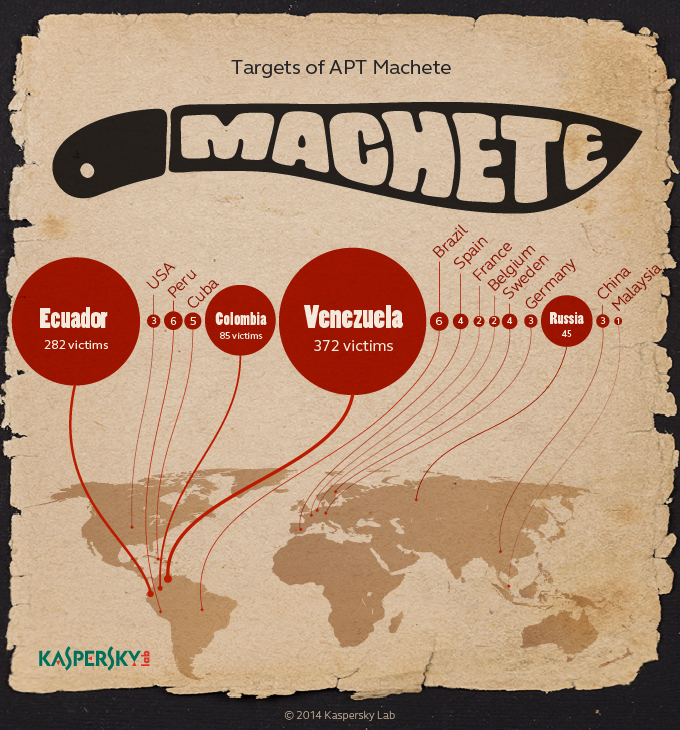
The threat group behind the Machete cyber espionage campaign first spotted in 2014 continues to target entities in Spanish-speaking countries. According to the researchers at security firm Cylance Threat actors behind the cyber espionage campaign dubbed Machete continue to target entities in Spanish-speaking countries. The Machete campaign was first uncovered by the researchers at Kaspersky in August 2014 and […]
 Pierluigi Paganini
March 21, 2017
The role of China (PRC) in the worldwide cyber espionage game of conditioning political life: when reserved information are brandished against the political opponent. In the days of testimony of U.S. Federal investigators about the role played during the last year by Russians, their alleged cyber operation is once again under examination. The mainstream media […]
 Pierluigi Paganini
March 17, 2017
New APT Campaign based on Poison Ivy RAT with C&C in China has been reversed by MalwareMustDie who shared a lot of interesting details about the attack vectors and reverse techniques. Our travel along the great analysis of a fresh, new insidious APT China campaign. An ordinary case of phishing? At the beginning, it seemed […]
 Pierluigi Paganini
February 17, 2017
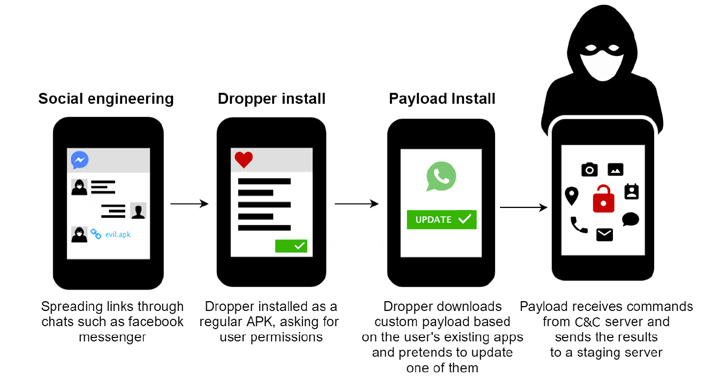
A group of hackers tracked as ViperRAT is spying on the Israeli military by hacking into the soldiers’ personal Android mobile devices. A group of hackers, tracked as ViperRAT, is spying on the Israeli military by hacking into the soldiers’ personal Android mobile devices to track their activities and steal sensitive data. Experts from security firms […]
 Pierluigi Paganini
January 19, 2017
Ukrenergo confirmed that preliminary results of its investigation showed that the Ukraine power outage that occurred in December was caused by hackers. In December 2016, the Government Ukraine energy company Ukrenergo suffered a severe power outage that affected the ”North” substation at Pivnichna. The incident caused blackouts in the city of Kyiv and neighboring regions. The […]
Security / November 02, 2026