 Pierluigi Paganini
 August 11, 2014
Researchers at FireEye have uncovered a new campaign dubbed Poisoned Hurricane characterized by the use of some clever techniques to avoid being detected. Security experts at FireEye revealed that several Internet infrastructure service providers in the United States and Asia, a financial institution, a government organization located in Asia and a US-based media company suffered […]
 Pierluigi Paganini
August 02, 2014
The Kaspersky Lab Team has issued a report which includes details of the investigation related to the Energetic Bear – Crouching Yeti APT campaign. Energetic Bear, aka Crouching Yeti, is the recently discovered APT campaign that targeted energy companies, manufacturers, industrial, pharmaceutical, construction, and many IT companies. Security experts have analyzed the Energetic Bear APT campaign, which appears […]
 Pierluigi Paganini
July 07, 2014
Cisco’s Threat Research Analysis and Communications (TRAC) uncovered an extremely targeted spear phish attack on high-profit companies in Europe. A new APT has been discovered by CISCO targeting high-profit companies in Europe, including businesses working in banking, oil and entertainment industries. The attackers adopted as attack vector the email in a spear phishing campaign. According to the alert […]
 Pierluigi Paganini
May 07, 2014
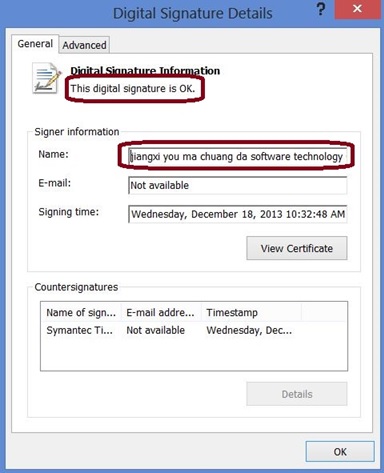
Security experts at McAfee Labs have discovered a new cyber espionage based on the malware digitally signed with stolel certificates. A recent research of McAfee Labs has identified a series of spear phishing attacks against non governmental entities and activists, the offensives which interested mainly organizations in China were conducted using malicious code signed with stolen digital […]
 Pierluigi Paganini
March 27, 2014
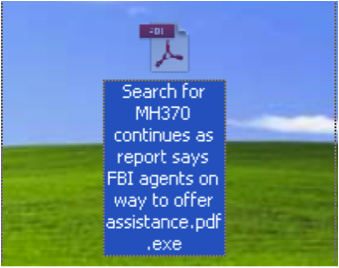
Security experts at FireEye uncovered a cyber espionage campaign based on multiple MH370 themed spear phishing emails. Security researchers at FireEye have revealed a link between a recent spear phishing campaign on Malaysian Airlines flight MH370 and the attacks conducted by some advanced persistent threat (APT) attackers. The mysterious skyjacking of the Boeing 777-200 aircraft of Malaysian Airlines, flight MH370, is considered one of the events […]
 Pierluigi Paganini
March 06, 2014
FireEye issued the 2013 Advanced Threat Report, the study provides a high-level overview of the computer network attacks by APTs discovered by the company. Today I desire to analyze with you the data proposed by FireEye in the 2013 Advanced Threat Report (ATR), the study provides a high-level overview of the computer network attacks discovered […]
 Pierluigi Paganini
February 11, 2014
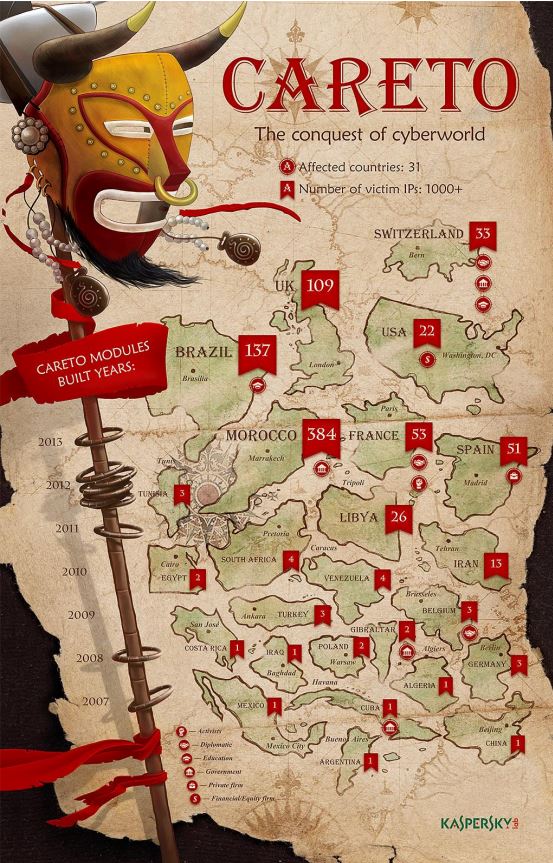
Speaking at Kaspersky Lab’s Industry Analyst Summit,Costin Raiu revealed details on The Mask campaign, the most sophisticated operation they’ve seen to date. The Kaspersky team recently announced to have detected a new significant APT campaign dubbed The Mask or “Careto” (Spanish for “Ugly Face” or “Mask”), a group of high-level state-sponsored hackers have been targeting government agencies, […]
 Pierluigi Paganini
February 09, 2014
Speaking at Kaspersky Lab’s Industry Analyst Summit Costin Raiu, revealed that the cost for APT campaign is dramatically dropping. The cost of developing advanced malware has fallen dramatically malicious code like Stuxnet and Flame are today economically more affordable. It has been estimated that the expense for the development of a cyber weapon like Stuxnet,or for a […]
 Pierluigi Paganini
February 04, 2014
Adobe has released security updates for Adobe Flash Player to fix a critical vulnerability exploited in a sophisticated cyber espionage campaign. Adobe has released today a new patch for the Flash Player product to fix a vulnerability which is currently being exploited. The vulnerability (CVE-2014-0497), allows an attacker to remotely take control of the targeted system […]
 Pierluigi Paganini
January 31, 2014
Andreas Lindh has discovered serious vulnerabilities in an unknown number of 3G/4G USB modems that can be exploited by attackers for spear phishing attacks. The researcher Andreas Lindh has discovered serious vulnerabilities in an unknown number of 3G and 4G USB modems that can be exploited by attackers to steal user’s credential. The expert has found a Cross Site […]
Malware / November 02, 2026
Security / November 02, 2026