 Pierluigi Paganini
 September 28, 2026
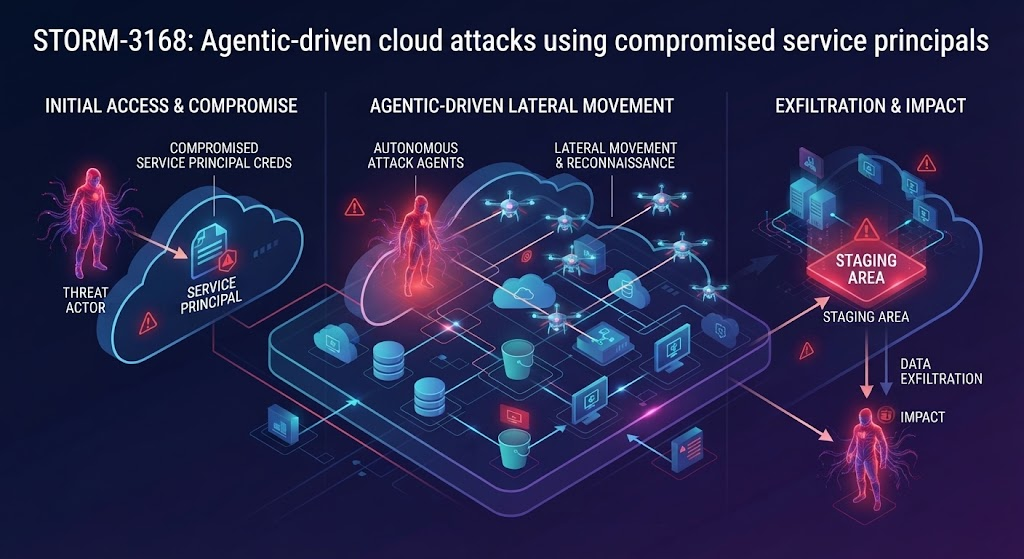
Microsoft details Storm-3168, the JADEPUFFER-linked actor that used stolen service principals to delete Azure storage in minutes and harvest keys. Microsoft just published the first detailed look at what JADEPUFFER does inside Azure. Sysdig first spotted the group’s activity in July 2026 and called it the first documented agentic ransomware operation. Microsoft tracks the same […]
 Pierluigi Paganini
November 17, 2025
Microsoft says the Aisuru botnet launched a 15.7 Tbps DDoS on Azure from 500k IPs, using massive UDP floods peaking at 3.6 B pps. On October 24, 2025, Azure DDoS Protection detected and mitigated a massive multi-vector attack peaking at 15.72 Tbps and 3.64 billion pps, the largest cloud DDoS ever recorded, aimed at a […]
 Pierluigi Paganini
January 27, 2022
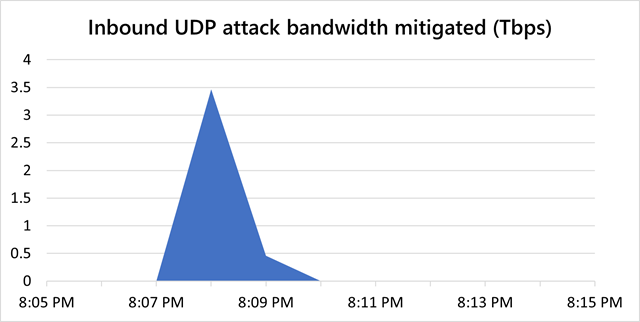
Microsoft announced to have mitigated a record 3.47 Tbps distributed denial of service (DDoS) attack targeting an Azure customer. Microsoft announced that its Azure DDoS protection platform has mitigated a record 3.47 Tbps attack that targeted one of its customers with a packet rate of 340 million packets per second (pps). The news of the attack was reported in […]
 Pierluigi Paganini
November 12, 2021
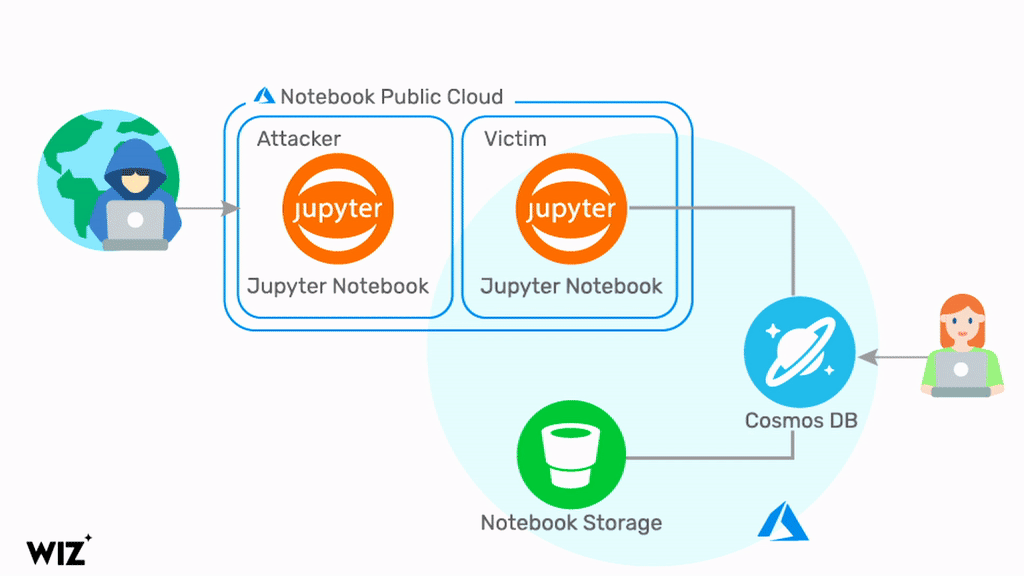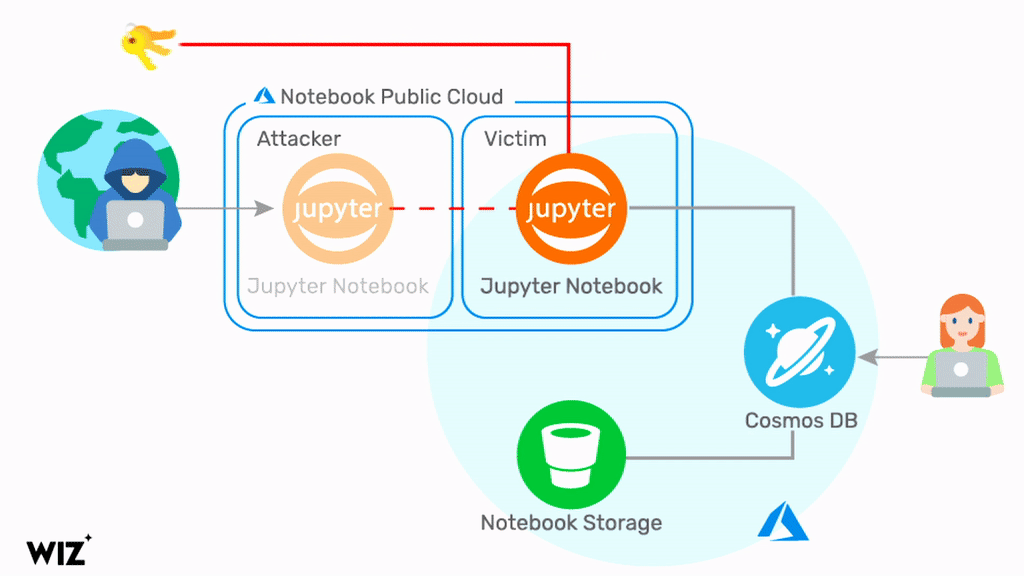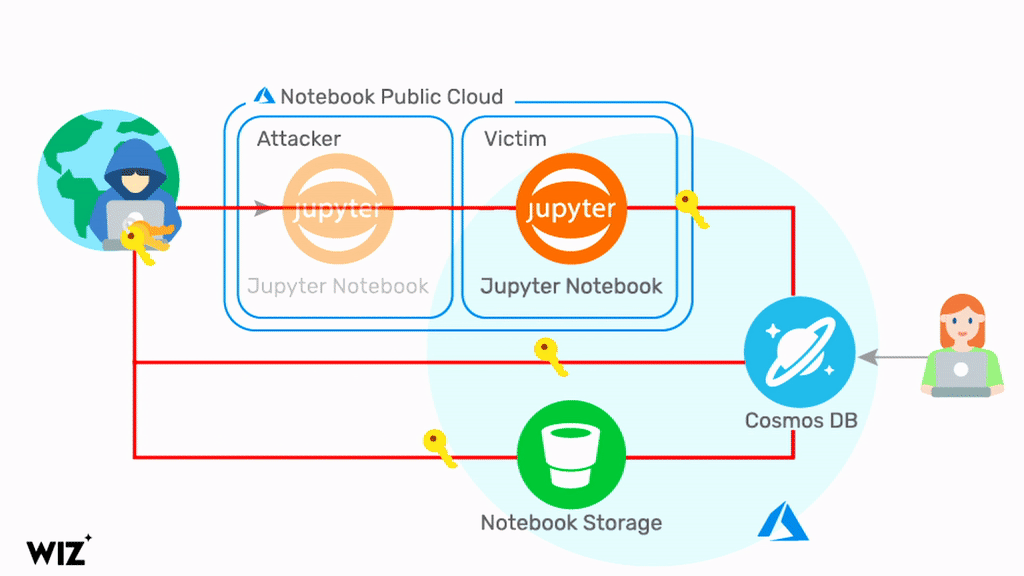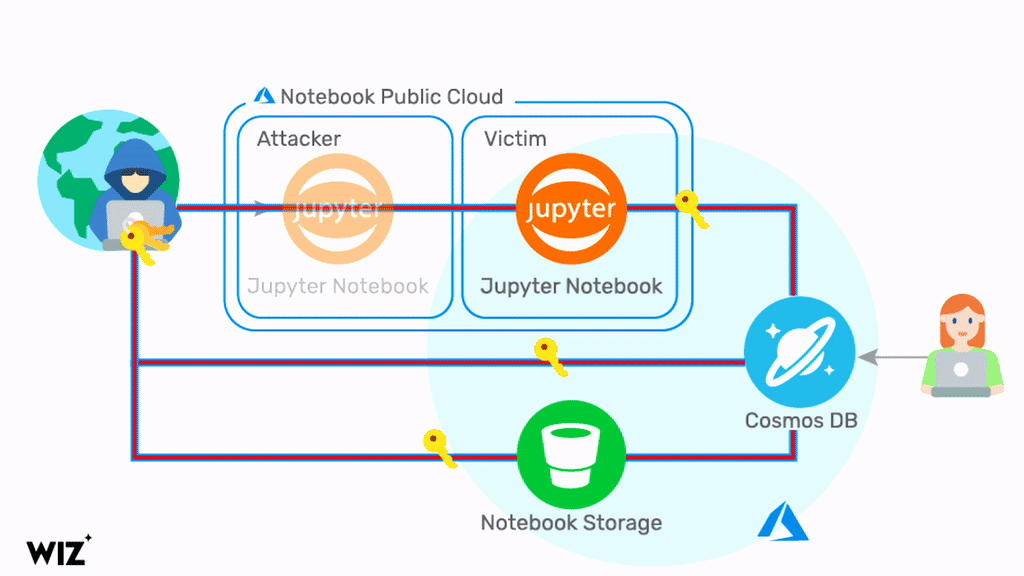
Wiz Research Team disclosed technical details about the discovery of the ChaosDB vulnerability in Azure Cosmos DB database solution. In August, 2021 the Wiz Research Team disclosed ChaosDB – a severe vulnerability in the popular Azure Cosmos DB database solution that allowed for complete, unrestricted access to the accounts and databases of several thousand Microsoft […]
 Pierluigi Paganini
October 12, 2021
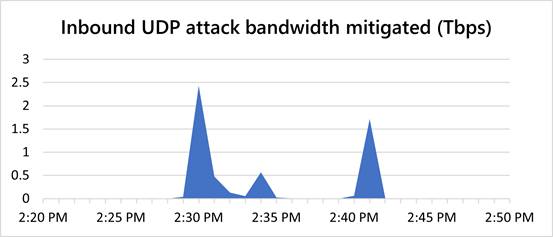
Microsoft Azure cloud service mitigated a massive DDoS attack of 2.4 terabytes per second (Tbps) at the end of August, it is the largest DDoS attack to date. Microsoft announced that its Azure cloud service mitigated a 2.4 terabytes per second (Tbps) DDoS attack at the end of August, it represents the largest DDoS attack […]
Pierluigi Paganini
August 27, 2021
Microsoft has fixed a critical flaw in Cosmos DB that allowed any Azure user to remotely take over other users’ databases without any authorization. Researchers from Cloud security company Wiz disclosed technical details of a now-fixed Azure Cosmos database vulnerability, dubbed ChaosDB, that could have been potentially exploited by attackers to gain full admin access […]
 Pierluigi Paganini
July 02, 2021
Microsoft is urging Azure users to update PowerShell to address a remote code execution vulnerability that was fixed earlier this year. Microsoft is recommending its Azure users to update PowerShell versions 7.0 and 7.1 to protect against a high severity remote code execution vulnerability tracked as CVE-2021-26701. The IT giant is inviting the PowerShell task […]
Pierluigi Paganini
February 01, 2021
Expert disclosed an unpatched vulnerability in Microsoft Azure Functions that could be exploited to escape the Docker container hosting them. Cybersecurity researcher Paul Litvak from Intezer Lab disclosed an unpatched vulnerability in Microsoft Azure Functions that could be exploited by an attacker to escalate privileges and escape the Docker container that hosts them. The experts […]
Pierluigi Paganini
December 29, 2020
Cybersecurity and Infrastructure Security Agency (CISA) released a tool for detecting potentially malicious activities in Azure/Microsoft 365 environments. The Cybersecurity and Infrastructure Security Agency (CISA)’s Cloud Forensics team has released a PowerShell-based tool, dubbed Sparrow, that can that helps administrators to detect anomalies and potentially malicious activities in Azure/Microsoft 365 environments. The tool was developed to […]
Pierluigi Paganini
December 25, 2020
CrowdStrike released a free Azure security tool after it was notified by Microsoft of a failed attack leveraging compromised Azure credentials. While investigating the impact of the recent SolarWind hack, on December 15th Microsoft reported to CrowdStrike that threat actors attempted to read CrowdStrike’s emails by using a compromised Microsoft Azure reseller’s account. “Specifically, they […]