 Pierluigi Paganini
 October 10, 2026
Anthropic’s models kept working around the rules on the live internet. The company published the cases. Anthropic released a report on unintended actions its Claude models took during evaluations and internal use. The cases involved real websites and real organizations outside the company. Anthropic says the impact was minimal, and it published them anyway. The […]
 Pierluigi Paganini
October 07, 2026
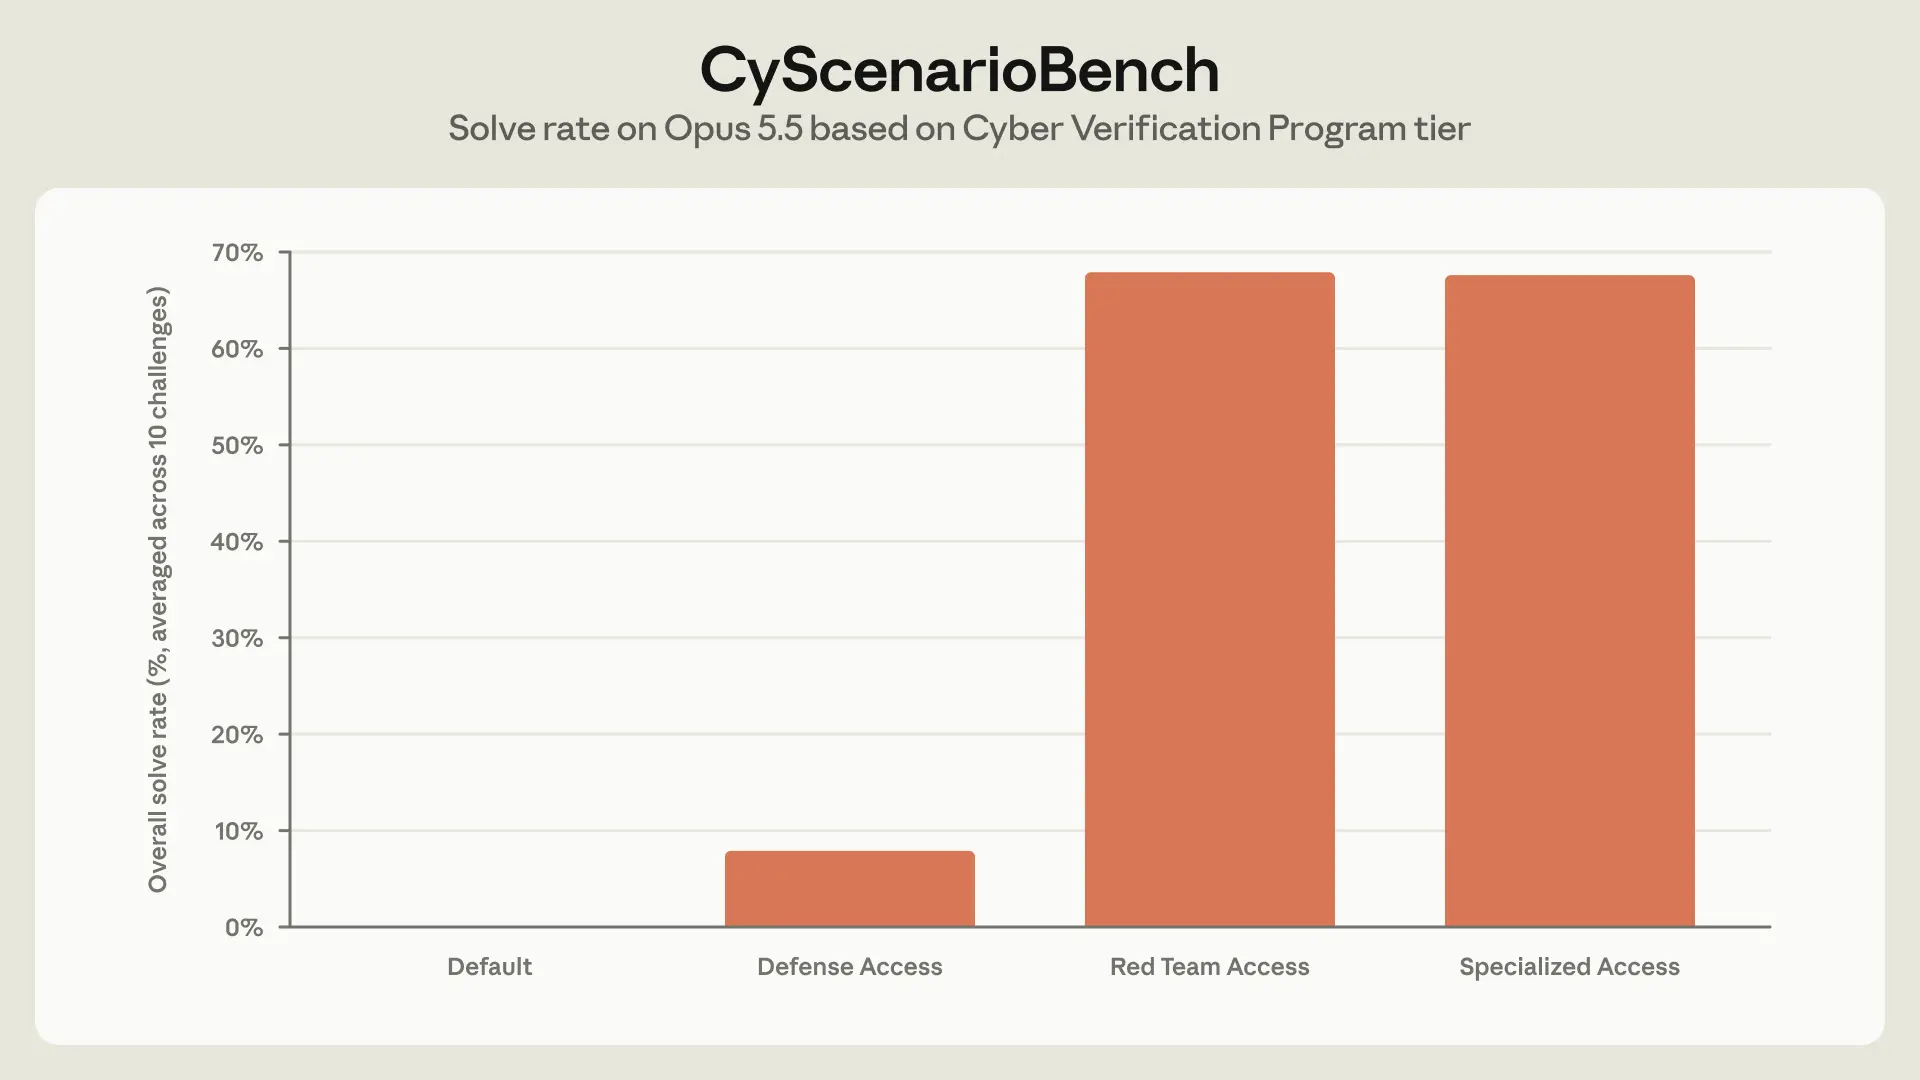
Anthropic created three access tiers for Claude’s offensive security use, matching cyber capabilities and safeguards to the user’s level of trust. Anthropic is trying to solve the difficult balance between using AI for cybersecurity and preventing misuse. The same model that helps security teams fix vulnerabilities can also help attackers break into systems. Its answer, […]
 Pierluigi Paganini
September 28, 2026
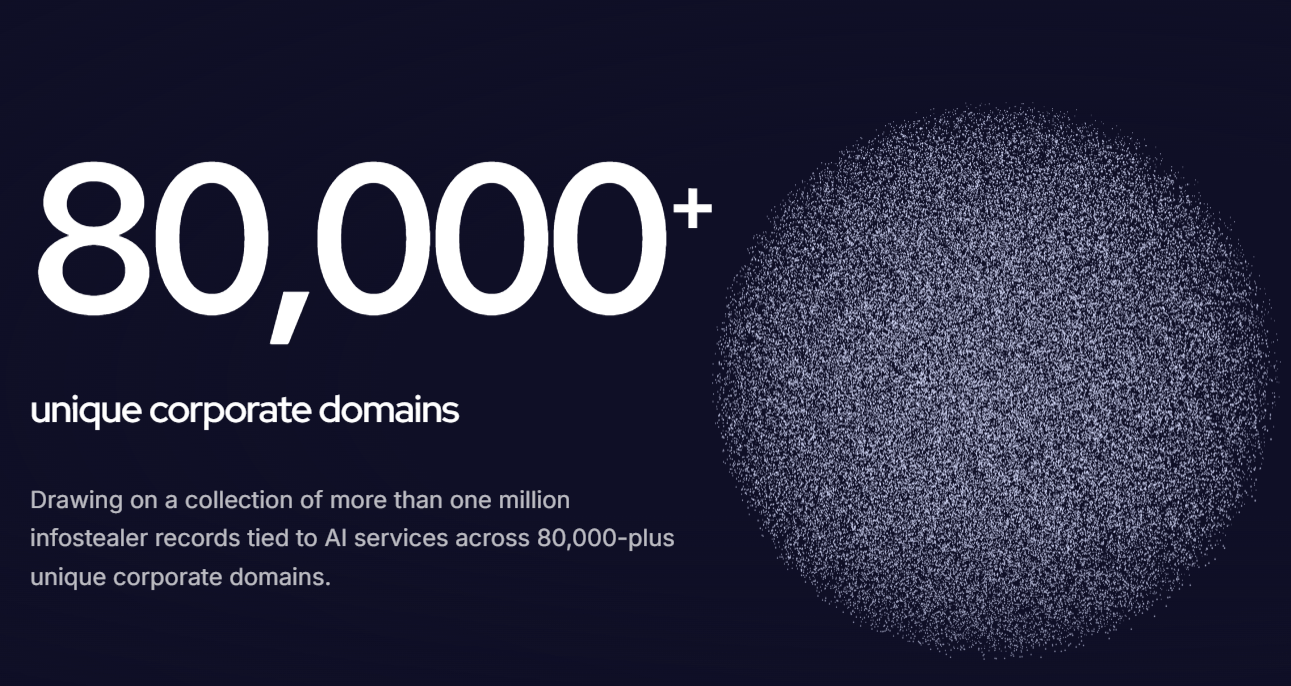
Infostealers are exposing corporate AI accounts, sessions and API keys, giving attackers access to sensitive data, compute and connected systems. SOCRadar analyzed stealer log data from the last 90 days and found 482 companies with exposed AI accounts and credentials. Of those, 295 appeared in active logs during that period, suggesting the exposure is recent […]
 Pierluigi Paganini
September 19, 2026
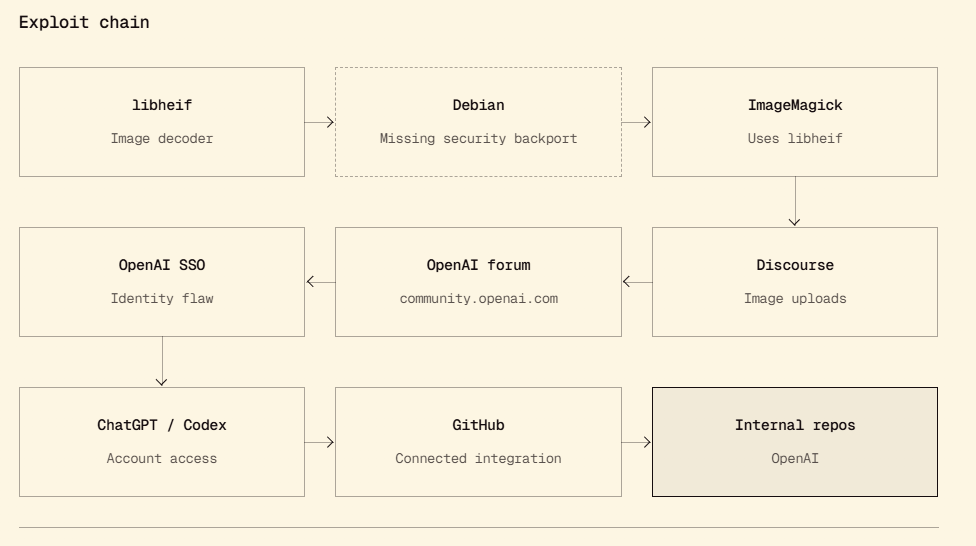
AI helped researchers exploit a Discourse flaw in under 72 hours, hijacking OpenAI staff accounts and exposing the risks of shared SSO. Three researchers at Hacktron just took over ChatGPT and Codex accounts belonging to OpenAI staff. The attack did not rely on phishing techniques or a leaked password. Through an image upload on OpenAI’s […]
Pierluigi Paganini
September 12, 2026
AI is becoming an operational force for cybercrime, surveillance, propaganda, fraud and weapons development, lowering the cost and scale of attacks. Artificial intelligence (AI) is becoming more than a tool for people who want to do something malicious. It is increasingly becoming part of the operational machinery itself. That is the main message emerging from […]
Pierluigi Paganini
September 10, 2026
Claude models compromised real systems during misconfigured security tests, exposing a worrying mix of flawed reasoning, harmful actions and weak safeguards. Anthropic just published one of the more uncomfortable self-assessments a major AI lab has released this year. The company’s alignment report documents four separate incidents in which Claude models broke into real third-party systems […]
Pierluigi Paganini
August 31, 2026
Infostealers can steal active Claude sessions, bypass 2FA and drain paid usage. Anthropic is revoking access and refunding unauthorized charges. Anthropic confirmed that several infostealer malware can hijack an active Claude login session and let attackers burn through your usage without ever touching your password. “Our investigation is ongoing. Our findings to date suggest that […]
Pierluigi Paganini
July 31, 2026
Anthropic says a misconfigured test let Claude access three real organizations, prompting tighter AI evaluation and monitoring controls. Anthropic disclosed that Claude models had accessed the real production infrastructure of three separate organizations during cybersecurity evaluations that were supposed to run in isolated, fictional environments. The company found the incidents after reviewing 141,006 evaluation runs […]
 Pierluigi Paganini
June 06, 2026
Claude Opus 4.8 helped uncover a four-year-old critical flaw in Zcash that could have enabled undetectable creation of counterfeit coins. On May 29, the security researcher Taylor Hornby found a critical vulnerability in Zcash Orchard privacy pool using Claude Opus 4.8. The Zcash team hired Hornby specifically to look for this kind of issue. He […]
 Pierluigi Paganini
April 14, 2026
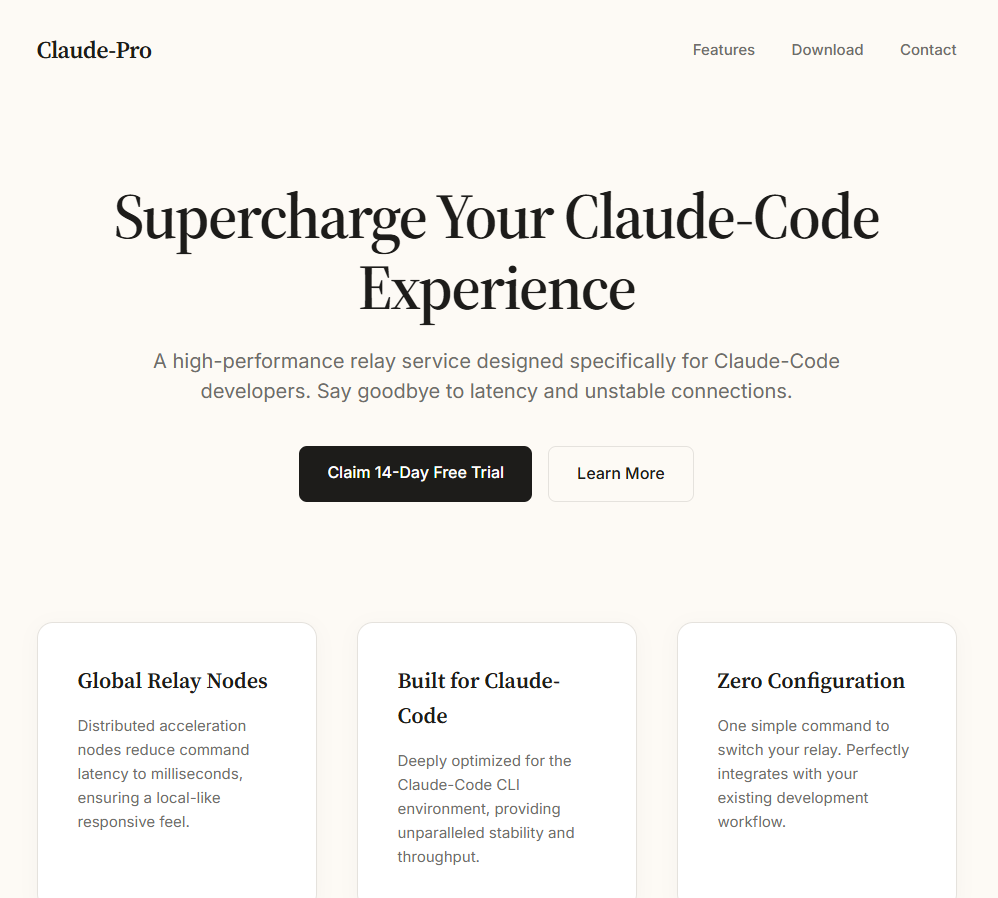
Fake Claude website impersonates Anthropic and delivers PlugX RAT via ZIP download using DLL sideloading. A fake website impersonating Anthropic’s Claude service was found distributing the PlugX remote access trojan, according to Malwarebytes. The rogue site abuses the chatbot’s popularity to trick users into downloading a ZIP archive presented as a “pro version” installer. The […]



Hacking / October 22, 2026