 Pierluigi Paganini
 October 07, 2026
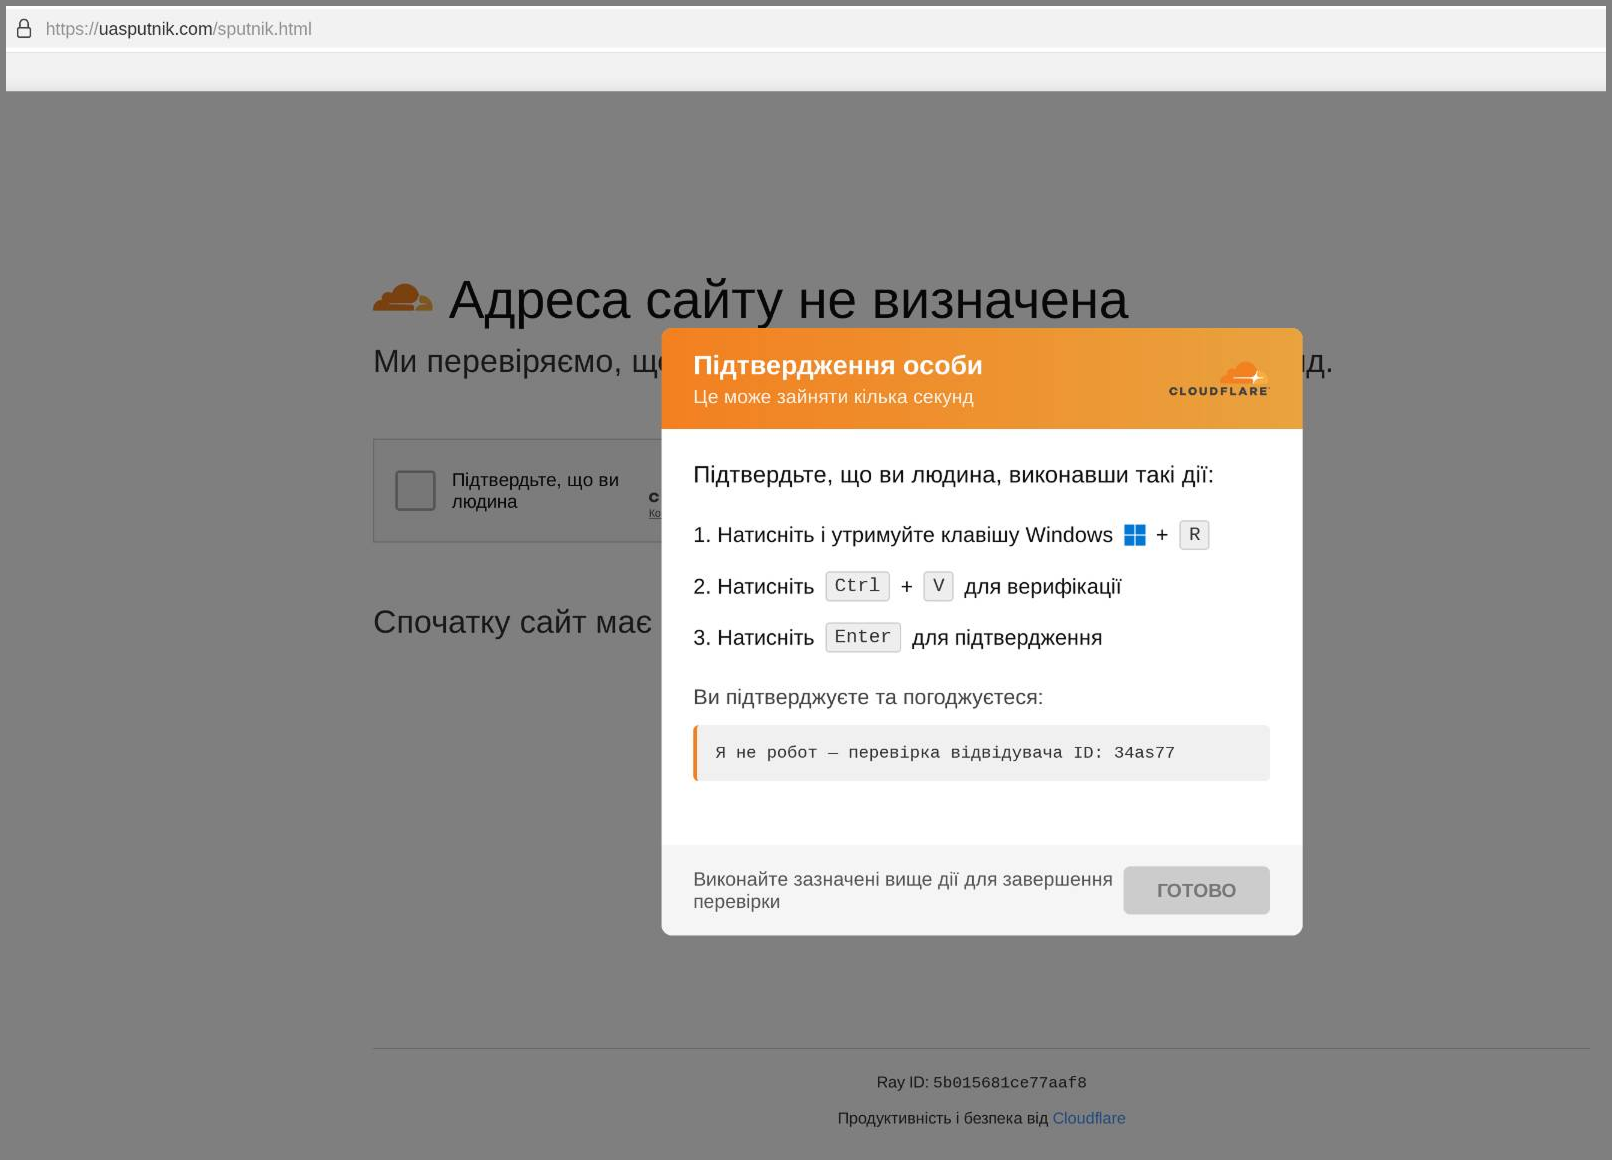
Over 100 hacked websites used fake Cloudflare checks to trick visitors into installing LunexStealer through ClickFix commands. The lure is the now-familiar ClickFix technique, dressed up as Cloudflare’s standard bot check. The fake page asks you to run a command, supposedly to confirm you’re not a bot, and that command quietly downloads and installs an […]
 Pierluigi Paganini
September 25, 2026
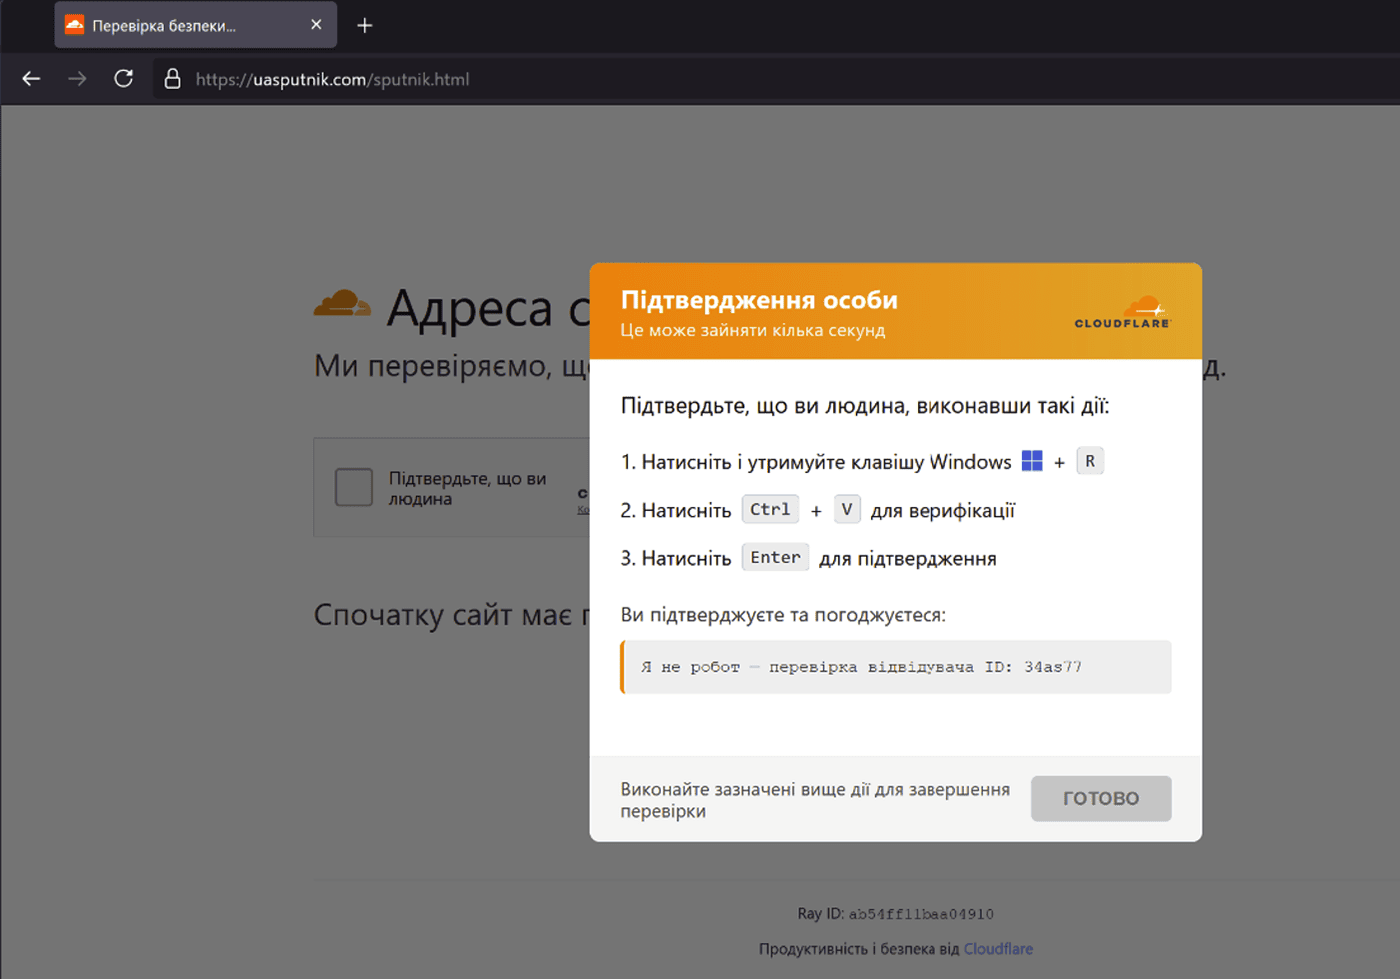
Attackers hijacked Ukrainian websites to deliver a fake Cloudflare CAPTCHA that installs Psychedelic Stealer and steals browser and crypto credentials. Psychedelic Stealer is being distributed through compromised Ukrainian business websites. Attackers injected hidden iframes into legitimate pages and used them to display a fake Cloudflare verification screen to visitors. The affected sites included a hair-treatment […]
 Pierluigi Paganini
September 21, 2026
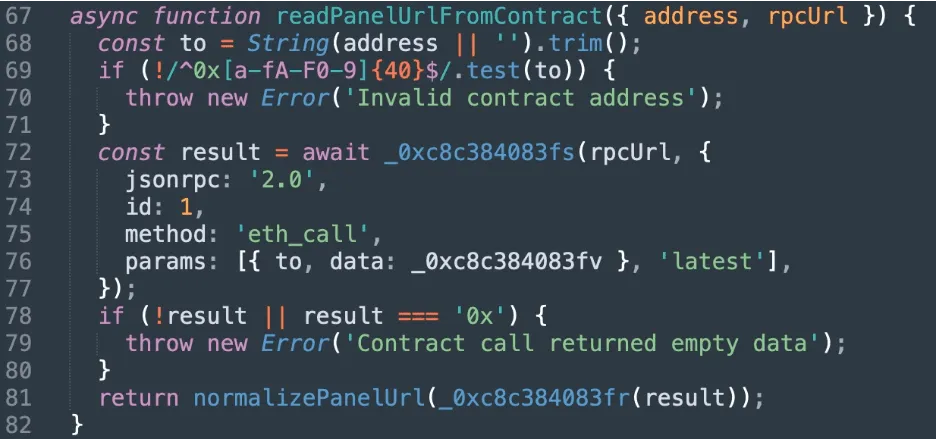
Blackpoint uncovers ChainScript, a Node.js RAT that queries a Polygon smart contract to find and rotate its command server. Blackpoint’s Adversary Pursuit Group was chasing a ClickFix campaign spreading an unknown RAT namend ChainScript. The malicious code is a previously undocumented Node.js remote access trojan that hides its command server on a public blockchain. The […]
 Pierluigi Paganini
September 18, 2026
A Brevo supply-chain attack used compromised Cloudflare access to inject malware into websites, potentially affecting over 100,000 sites. Brevo, formerly known as Sendinblue, is a French cloud-based marketing and customer communication platform whose clients include eBay, Louis Vuitton and Michelin. The company was first compromised on September 10, when attackers exploited a vulnerability in its […]
 Pierluigi Paganini
August 19, 2026
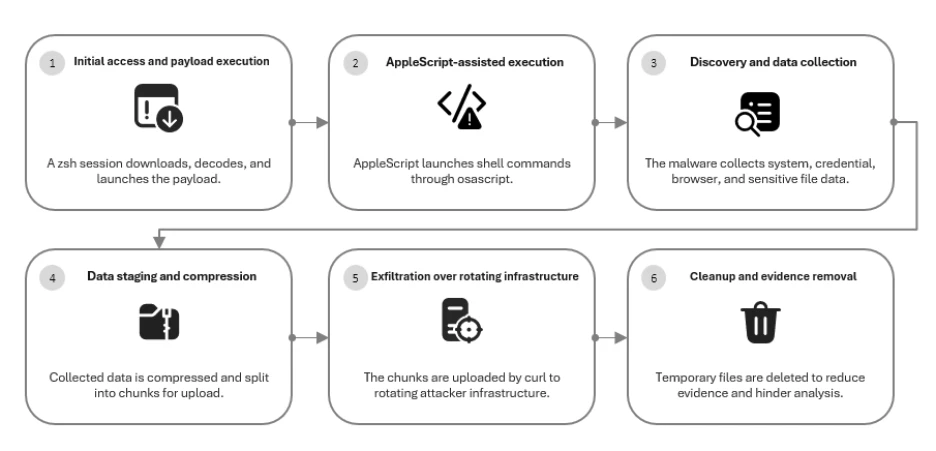
Microsoft tracked over 30 MacSync Stealer domains by focusing on behavioral patterns, revealing a campaign targeting passwords, keys, wallets and other data. Domain blocking is a losing game when the thing you’re blocking can register a new domain faster than you can add it to a list. That’s the exact problem Microsoft Defender Experts ran […]
 Pierluigi Paganini
August 01, 2026
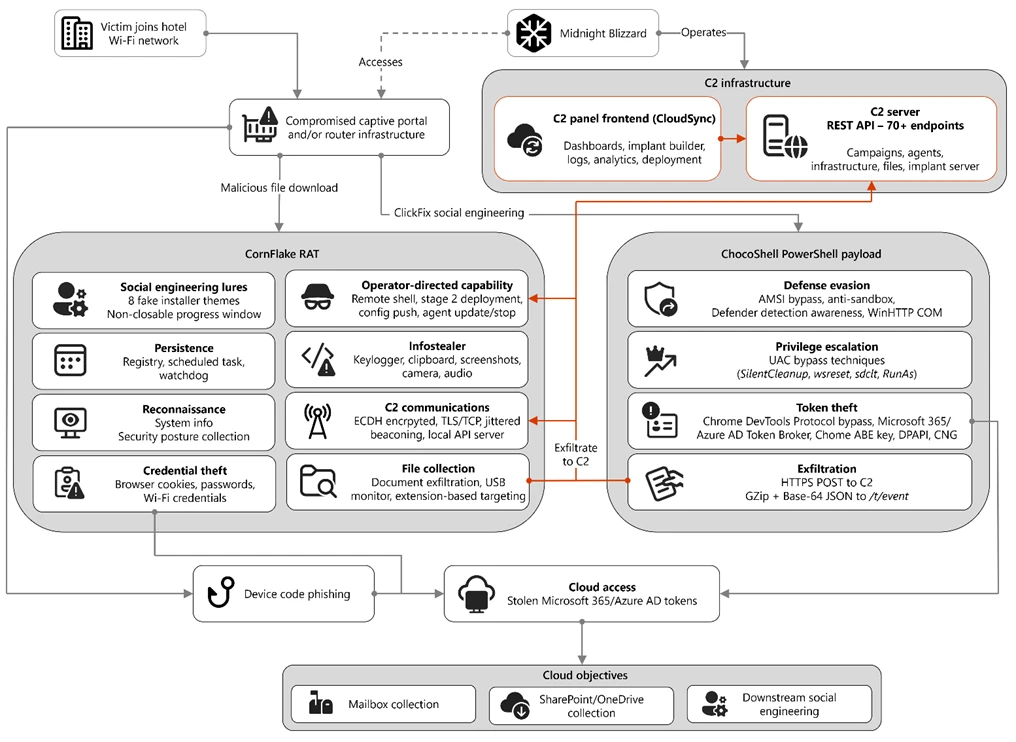
Microsoft says Russian hackers hijacked hotel Wi-Fi portals to spread malware and steal Microsoft 365 tokens from travelers. Microsoft Threat Intelligence disclosed CaptiveCrunch, a campaign it attributes to Storm-2945, an operational sub-cluster of Midnight Blizzard, the Russian SVR-linked group also known as APT29 and Cozy Bear. Since early May 2026, Storm-2945 has been manipulating DNS […]
 Pierluigi Paganini
July 30, 2026
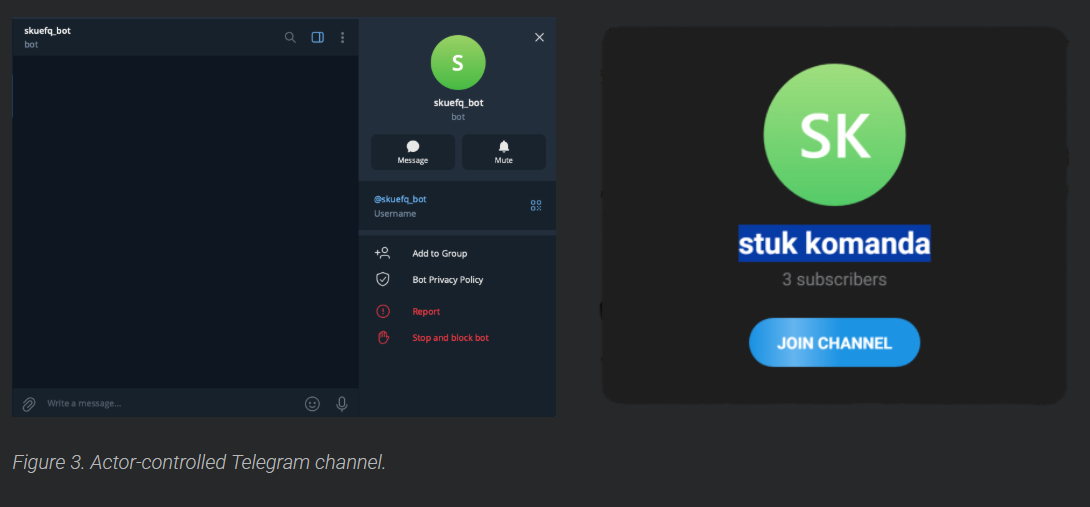
Brand impersonation now drives initial access, using fake sites and apps to deliver malware, making rapid takedowns essential to disrupt attacks. Attackers recently poisoned more than 700 websites, including sites run by Harvard, Oxford, and DuckDuckGo. They used a fake Cloudflare page to trick visitors into running a ClickFix attack that installed malware. Researchers tracing […]
 Pierluigi Paganini
July 17, 2026
Russian-speaking UAT-11795 spreads trojanized Zoom, Webex, and MobaXterm installers to deliver Starland RAT and the WLDR memory-only implant. Cisco Talos researchers published a detailed technical report on July 16 disclosing UAT-11795, a financially motivated, Russian-speaking threat actor that has been running a malware campaign against users in the United States and Europe since at least […]
 Pierluigi Paganini
May 25, 2026
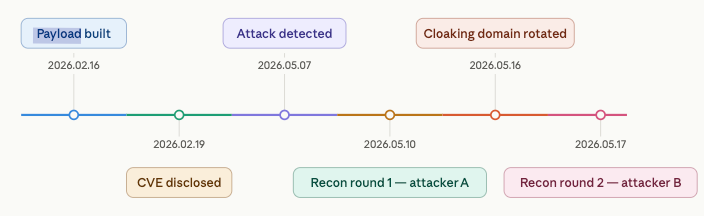
Attackers are exploiting the patched Ghost CMS flaw CVE-2026-26980, compromising over 700 unpatched sites, including universities. Threat actors are actively exploiting a security flaw, tracked as CVE-2026-26980, in Ghost CMS that was fixed months ago in real attacks against unpatched websites. According to Qianxin, the campaign has already affected more than 700 sites, including well-known organizations and […]
 Pierluigi Paganini
May 25, 2026
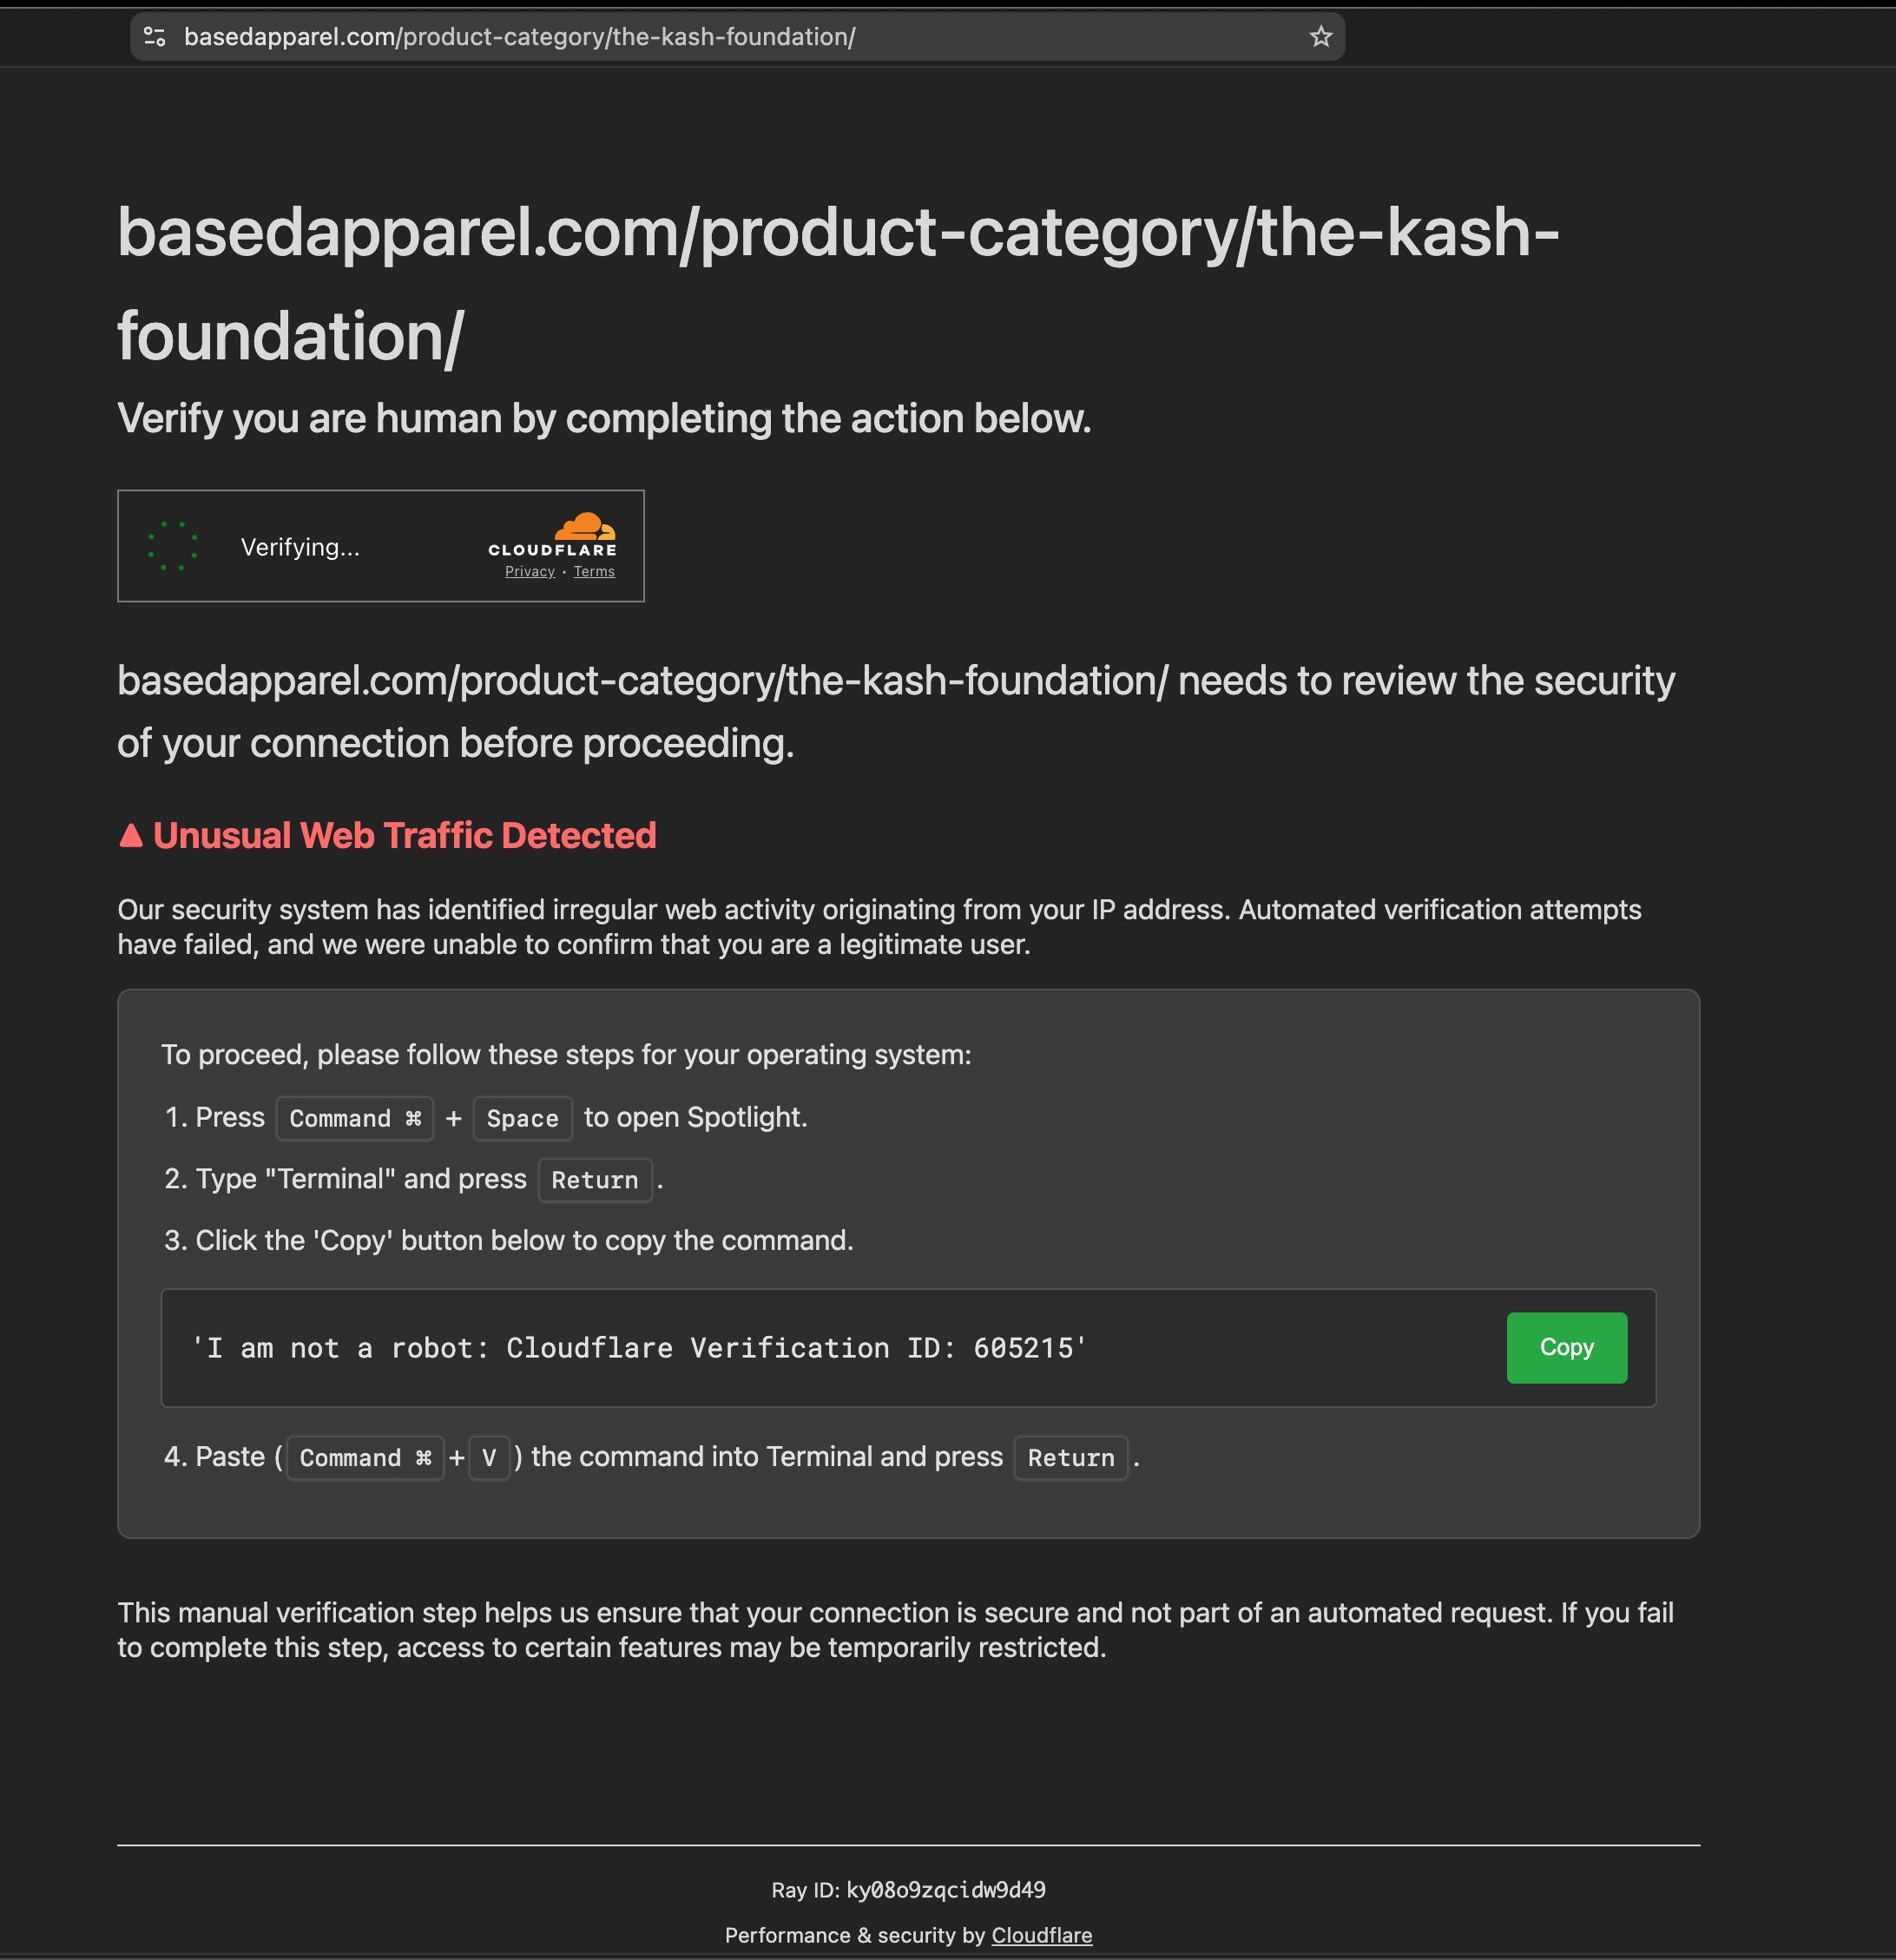
FBI director site went offline after a hack used a fake Cloudflare page to trick users into running a ClickFix attack that installed malware. The merchandise website of FBI director Kash Patel (basedapparel[.]com) was taken offline on Friday after reports that it had been compromised by hackers using it to spread malware. The malware was […]