 Pierluigi Paganini
 February 02, 2019
Researchers at the CenturyLink Threat Research Labs discovered that the operators of the TheMoon IoT botnet are offering it as a service. Experts at the CenturyLink Threat Research Labs observed a new evolution for the TheMoon IoT botnet, operators added a previously undocumented module that allows them to offer it with a malware-as-a-service model. The […]
 Pierluigi Paganini
January 28, 2019
The Cobalt cybercrime gang has been using Google App Engine to distribute malware through PDF decoy documents. The Cobalt hacking group has been using Google App Engine to distribute malware through PDF decoy documents. The group targeted more than 20 other government and financial institutions worldwide. Cobalt crime gang is a Russian hacking crew that […]
 Pierluigi Paganini
January 25, 2019
Security experts from Cybaze-Yoroi ZLab investigated two malicious spam campaigns delivering Java RAT that show some similarities. Introduction During the last weeks, the Cybaze-Yoroi ZLab researchers identified infection attempts aimed to install RAT malware directed to the naval industry sector. The malicious email messages contained a particular Adwind/JRat variant delivered via several methods tailored to […]
 Pierluigi Paganini
January 20, 2019
Bulgaria has extradited a Russian hacker that was indicted by a US court for mounting a sophisticated hacking scheme to the United States. According to the Russian embassy in Washington, the Russian hacker Alexander Zhukov was extradited on January 18. The Russian embassy has chosen to disclose the news on the VK social network, the […]
 Pierluigi Paganini
January 14, 2019
The City Hall of Del Rio, a city in and the county seat of Val Verde County, Texas, was hit by a ransomware attack, operations were suspended. Last week, the City Hall of Del Rio, a city in and the county seat of Val Verde County, Texas, was hit by a ransomware attack. On Thursday, tens of computers at […]
 Pierluigi Paganini
January 14, 2019
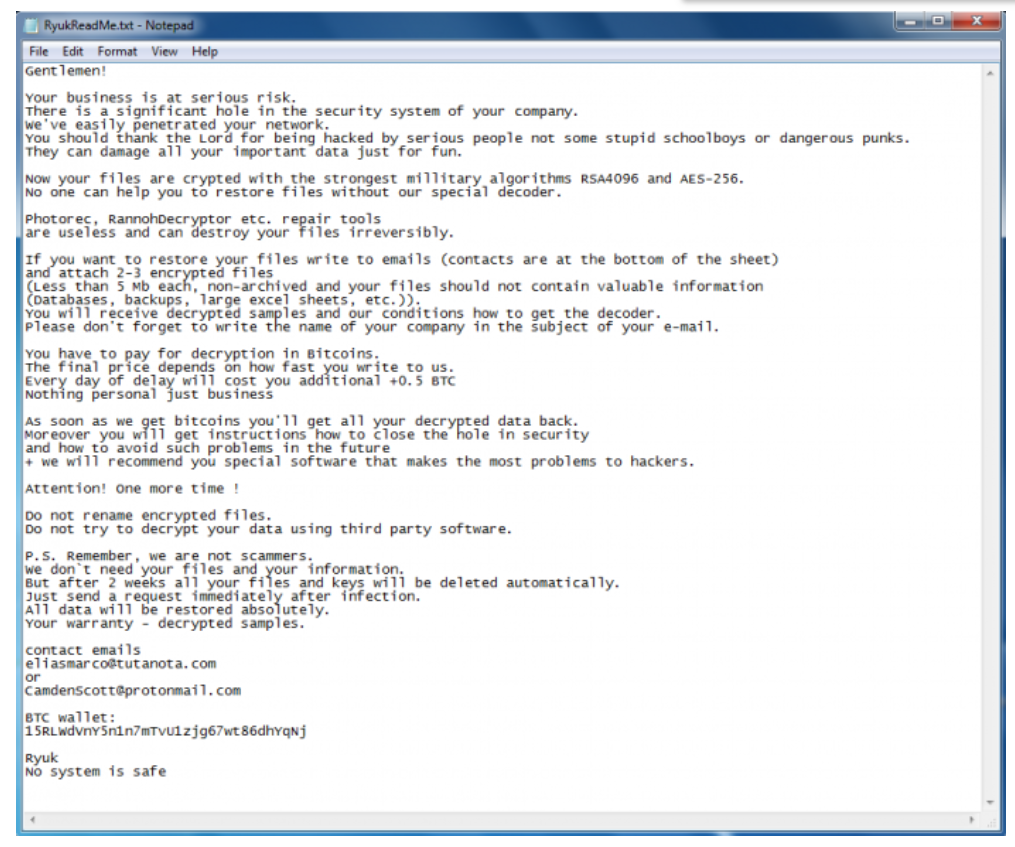
FireEye and CrowdStrike discovered that threat actors behind the Ryuk ransomware are working with another cybercrime gang to gain access to target networks. In August 2018, security experts from Check Point uncovered a ransomware-based campaign aimed at organizations around the world conducted by North Korea-linked threat actor. This is the first time that a security firm […]
 Pierluigi Paganini
January 13, 2019
Proofpoint analyzed two strains of malware tracked as ServHelper and FlawedGrace distributed through phishing campaigns by the TA505 crime gang. Security researchers at Proofpoint researchers discovered two strains of malware tracked as ServHelper and FlawedGrace distributed through phishing campaigns by the TA505 crime gang. The ServHelper is a backdoor, experts analyzed two variants of it, while […]
 Pierluigi Paganini
January 11, 2019
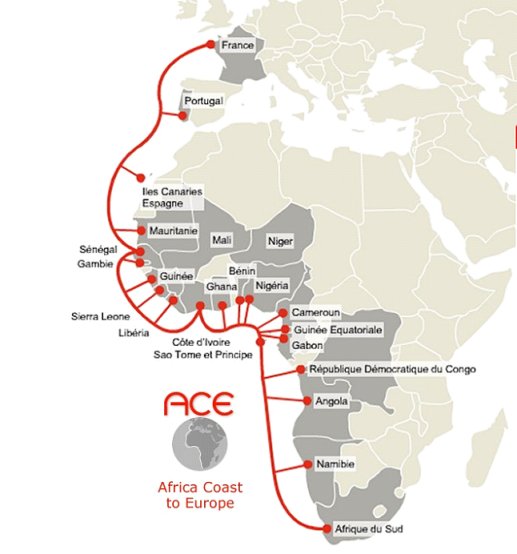
The British hacker Daniel Kaye has been sentenced to 32 months in prison for the cyberattack on Liberian telecom firms. The British hacker Daniel Kaye (29) has been sentenced to 32 months in prison for the 2016 attack that took down telecommunications services in Liberia. Kaye pleaded guilty in December to two charges under the Computer Misuse […]
 Pierluigi Paganini
January 04, 2019
A new variant of the NRSMiner is infecting users in the southern region of Asia, most of the victims are in Vietnam (54%), Iran (16%) and Malaysia (12%). The new version leverages the EternalBlue exploit to spread, experts observed that the threat also updates existing NRSMiner installs. ETERNALBLUE is an NSA exploit that made the headlines […]
 Pierluigi Paganini
January 02, 2019
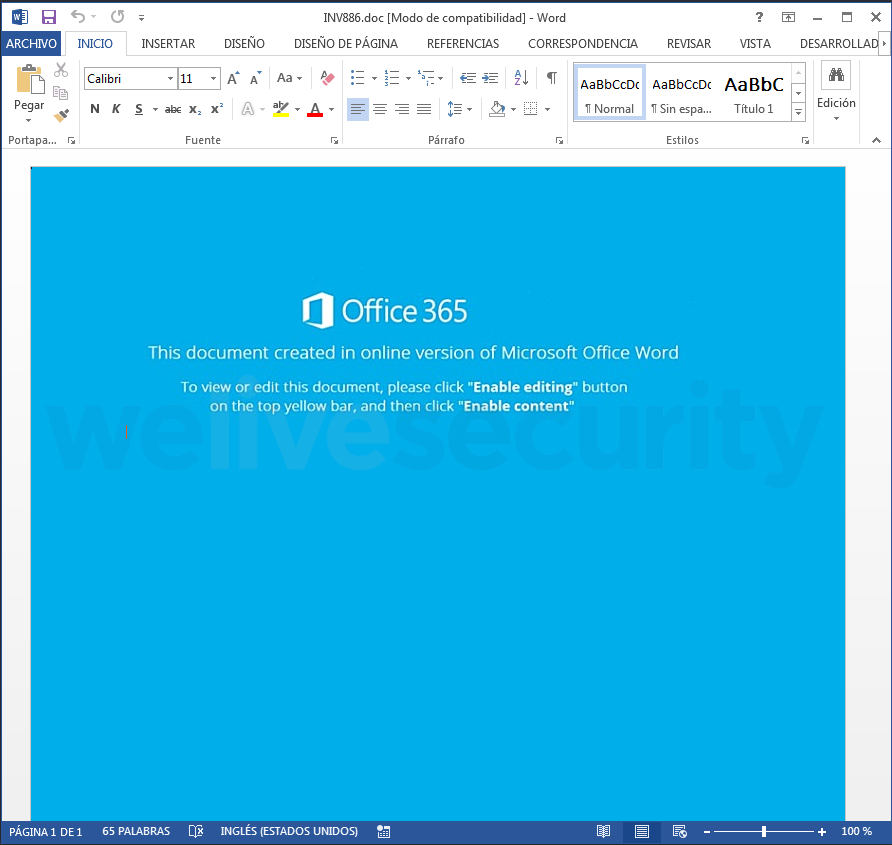
ESET analyzed the distribution technique used by cyber criminals in new Emotet campaign that has recently affected various countries in Latin America. In November, experts from ESET uncovered a massive spam campaign that was distributing the Emotet malware. The campaign targeted several users in some Latin American countries and ESET shared details on the propagation used […]