 Pierluigi Paganini
 June 21, 2014
The FBI has formed a new cybercrime task force with the NYPD and the Metropolitan Transit Authority to investigate on cyber crimes. Cybercrime is considered by governments an emergency to mitigate urgently, criminal activities are causing large losses to the global economy as reported in the recent report published by McAfee. The FBI created a […]
 Pierluigi Paganini
June 20, 2014
Hosting service Code Spaces goes out of business due to a cyber attack after an attempt of extortion by a gang of cyber criminals. Code Spaces, a code-hosting and software collaboration platform, has been brought down by a serious cyber attack which has caused its out of business, the attackers have deleted the data and […]
 Pierluigi Paganini
June 19, 2014
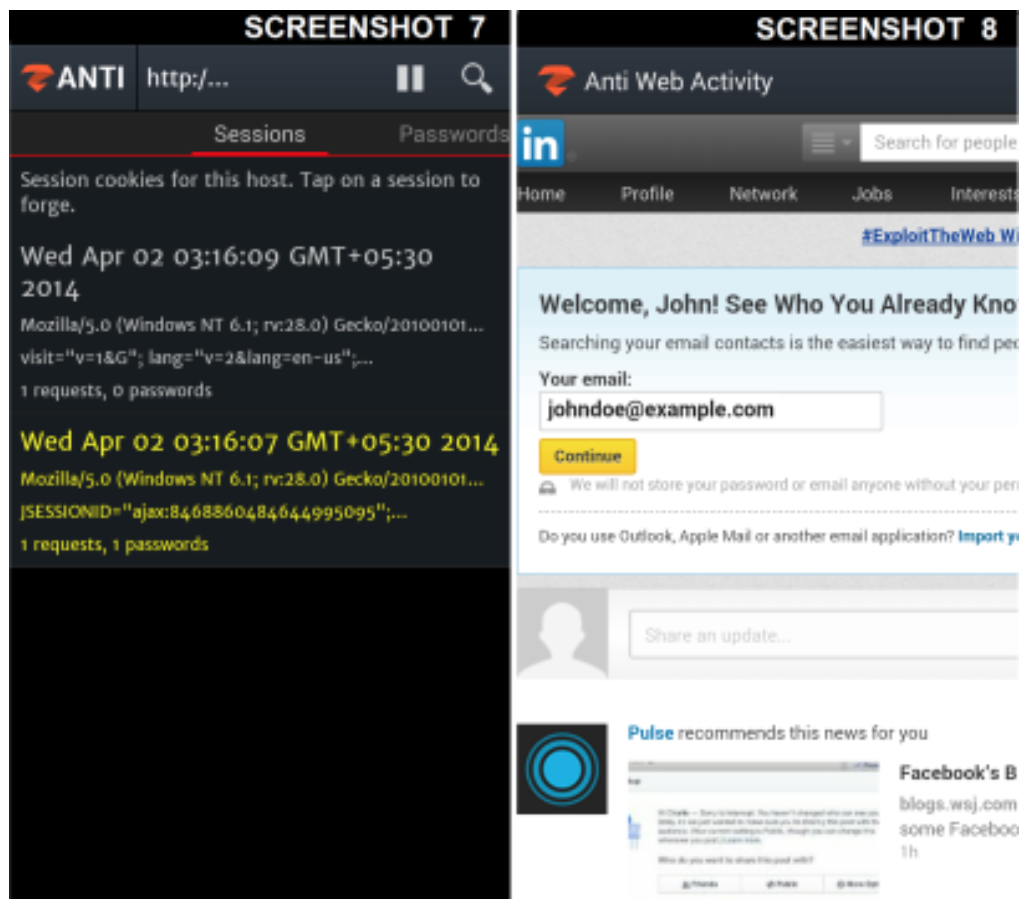
Security experts at Zimperium firm revealed that LinkedIn users could be potentially vulnerable to Man-in-the-Middle attacks leveraging an SSL stripping. A new research is scaring users of LinkedIn revealing that they could be potentially vulnerable to Man-in-the-Middle (MITM) attacks leveraging an SSL stripping. Despite the US security firm Zimperium reported the problem to LinkedIn more than a […]
 Pierluigi Paganini
June 18, 2014
The Italian security firm Tiger Security issued a report on the current state of cyber attacks against the organization of the Brazil 2014 World Cup. The Italian firm Tiger Security is one of the companies in charge to monitor cyber security of the Brazil 2014 World Cup, in these hours its experts have issued an interesting report titled […]
 Pierluigi Paganini
June 18, 2014
The American multinational giant AT&T confirmed to have suffered a data breach last April, personal data of an unknown number of users was exposed. The American multinational telecommunications corporation AT&T confirmed to have suffered a data breach last April, personal information of an unknown number of users was accessed by employees of one of its contractor. AT&T […]
 Pierluigi Paganini
June 17, 2014
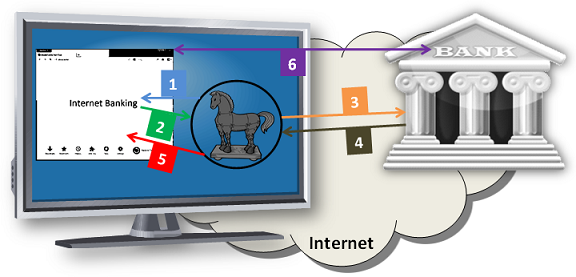
Security experts at CSIS in Denmark have discovered a new piece of banking malware, dubbed Dyreza, which implements browser hooking to defeat SSL. Dyreza is the name of a new banking Trojan which is targeting numerous financial institutions, including Bank of America, Citibank, Natwest, RBS and Ulsterbank. Dyreza captured the attention of security researchers due the technique it […]
 Pierluigi Paganini
June 16, 2014
Security Experts at Trend Micro have discovered different World Cup themed malicious application targeting Android mobile devices. The World Cup 2014 is an excellent occasion for cyber criminals to trick users with social engineering techniques into downloading any kind of malicious content. Of course mobile users are a privileged target for cyber criminals, different World Cup-themed […]
 Pierluigi Paganini
June 15, 2014
Experts at Kaspersky Lab are following the evolution of Svpeng Android malware, born as banking trojan and evolved in ransomware which hit US customers. The mobile malware Svpeng is evolving and recent versions were adapted to classic extortion scheme targeting Android devices in the US. Svpeng was detected for the first time one year ago […]
 Pierluigi Paganini
June 14, 2014
The malware specialists at Trend Micro noticed that malicious agent BKDR_VAWTRAK is abusing a Windows feature SRP to prevent victims’ defense systems. Experts at Trend Micro have discovered that Japanese Internet users are being infected by a trojan, dubbed BKDR_VAWTRAK, which uses Windows to try to defeat security software on infected machines. Like many other […]
 Pierluigi Paganini
June 13, 2014
Prolexic security and engineering response team has issued a study on the possible uses of Zeus malware, remarking that its success is the versatility. Zeus malware never dies, it seems the title of a film, but the reality goes over the fiction, despite the recent success of law enforcement agencies in the takeover of Gameover […]