


 Pierluigi Paganini
 September 23, 2026
Microsoft, Coinbase and law enforcement took down EvilTokens, a phishing kit that compromised 12,000 inboxes through device-code phishing and AI. EvilTokens showed up in February 2026 and moved fast. Within months it had compromised more than 12,000 inboxes across over 10,000 organizations. Microsoft says the EvilTokens platform, operated by Storm-2992, is a phishing-as-a-service kit sold […]
 Pierluigi Paganini
February 16, 2025
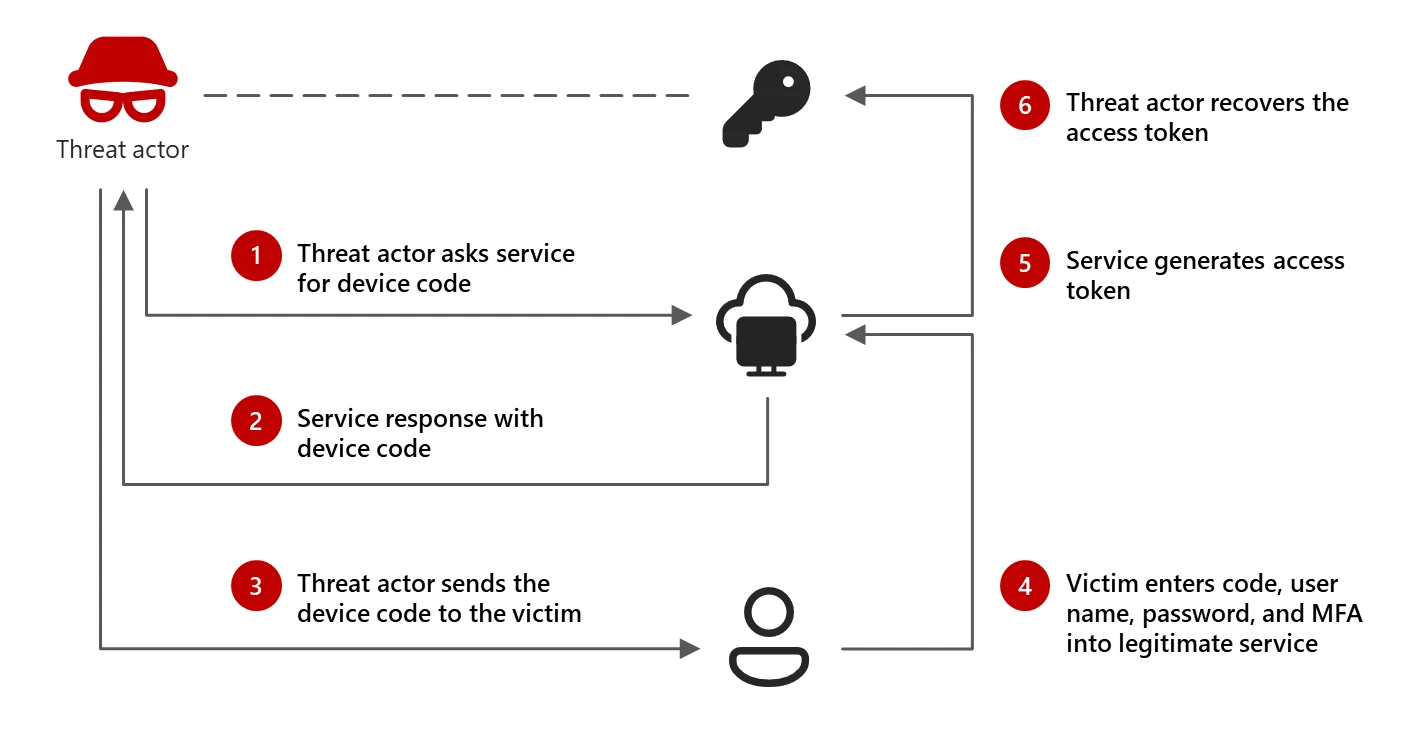
Russia-linked group Storm-2372 used the device code phishing technique since Aug 2024 to steal login tokens from governments, NGOs, and industries. Microsoft Threat Intelligence researchers warn that threat actor Storm-2372, likely linked to Russia, has been targeting governments, NGOs, and various industries across multiple regions since August 2024. The attackers employ a phishing technique called […]





