



 Pierluigi Paganini
 October 18, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter IronChain Ransomware Threatens Businesses with Permanent Data Loss and Costly Downtime AI models may be capable of self-replicating without access to a datacenter XWorm Reborn: From infostealer to surveillance platform Hirudo: From Fake Updates […]
 Pierluigi Paganini
October 18, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. North Korean IT Workers Used Stolen US Identities to Earn $3 Million U.S. CISA adds Fortinet Multiple […]
 Pierluigi Paganini
October 17, 2026
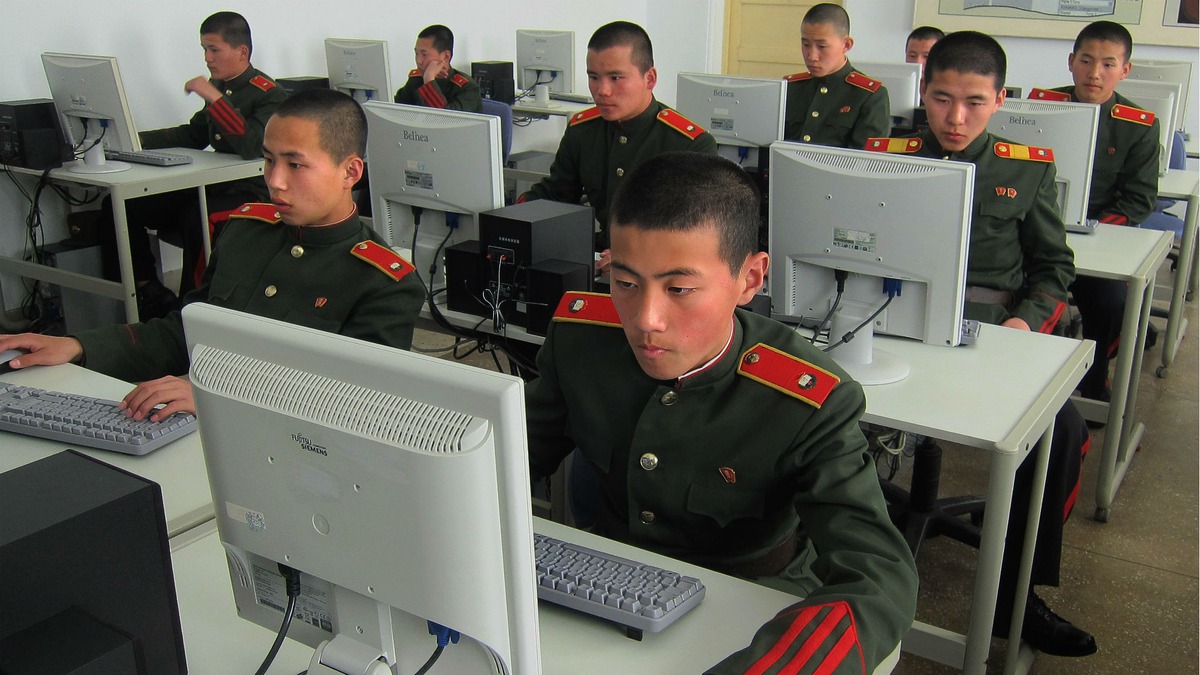
The FBI raided 40 Texas homes over a North Korean scheme that used fake IT workers to target 70 US companies and generate $3 million. The Justice Department (DoJ) announced coordinated enforcement actions this week targeting North Korea’s long-running scheme to place fake IT workers inside American companies. Two US nationals were arrested, 14 people […]
 Pierluigi Paganini
October 17, 2026
A cyber incident at a BAE Systems subsidiary just stopped every bankruptcy court in the US from sending notices, and the problem started a week ago. A security incident at BAE Systems Inc., the US subsidiary of British defense contractor BAE Systems, has taken the Bankruptcy Noticing Center offline since October 9. The Bankruptcy Noticing […]
 Pierluigi Paganini
October 16, 2026
Burger King Japan disclosed a breach exposing 11.18 million app users’ personal data after attackers accessed its membership system in early October. Burger King Japan has disclosed a data breach that exposed the personal information of approximately 11.18 million official app members. Burger King Japan, the company operating the fast-food chain in the country, said […]
 Pierluigi Paganini
October 16, 2026
F5 addressed multiple vulnerabilities, including critical RCE flaws in NGINX that attackers could exploit without authentication. Security and application delivery firm F5 announced fixes for eleven security issues in NGINX. Among them, critical vulnerabilities tracked as CVE-2026-15176 and CVE-2026-93479 could be exploited without authentication via crafted HTTP requests. Under certain conditions beyond their control, an […]
 Pierluigi Paganini
October 16, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Atlassian flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Atlassian flaw, tracked as CVE-2026-21589 (CVSS score of 9.3), to its Known Exploited Vulnerabilities (KEV) catalog. In early October, threat actors started exploiting CVE-2026-21589, a critical arbitrary file access flaw […]
 Pierluigi Paganini
October 16, 2026
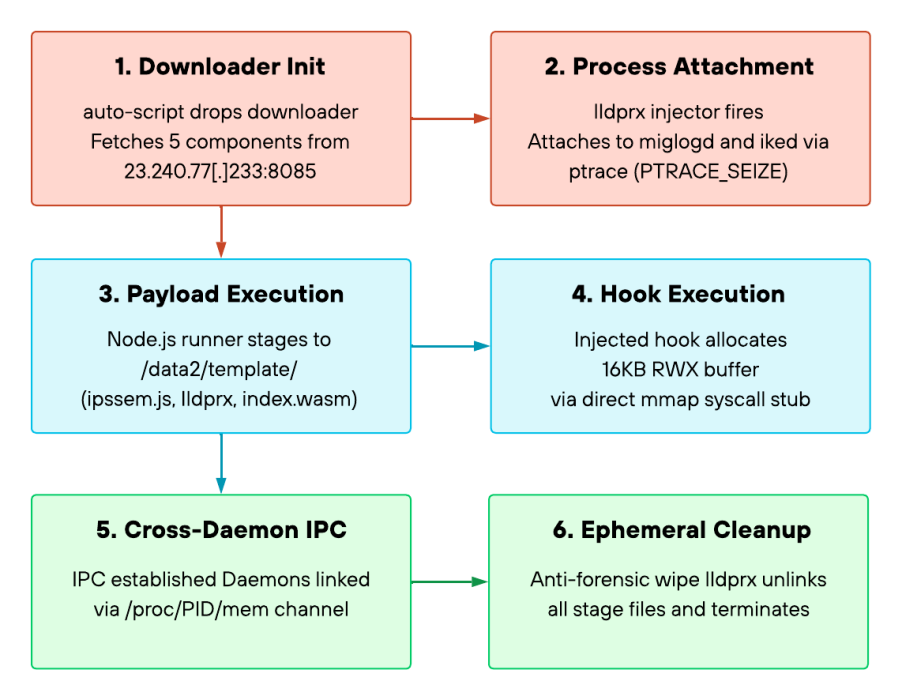
PEERSTITCH malware exploited FortiManager to expose 500+ firewalls, evade detection inside FortiOS memory, and maintain stealthy access. PEERSTITCH, a stealthy implant deployed during a prolonged intrusion, helped attackers maintain access to a telecom managed service provider after compromising its FortiManager appliance. Palo Alto Networks Unit 42 documented the operation, which began in September 2024 and […]
 Pierluigi Paganini
October 16, 2026
The regulated utility company CenterPoint Energy says a data breach exposed the personal information of more than 1 million people in Texas. CenterPoint Energy is a regulated utility company used to deliver natural gas and electricity infrastructure, maintain power grids and pipelines, and restore service across parts of Texas, Indiana, Ohio, and Minnesota. The organization […]
Pierluigi Paganini
October 15, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Palo Alto Networks PAN-OS, Ahsay AhsayCBS, and Cisco Secure Email Gateway flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Cisco confirmed this week that threat actors are exploiting a critical vulnerability […]






