 Pierluigi Paganini
 February 18, 2021
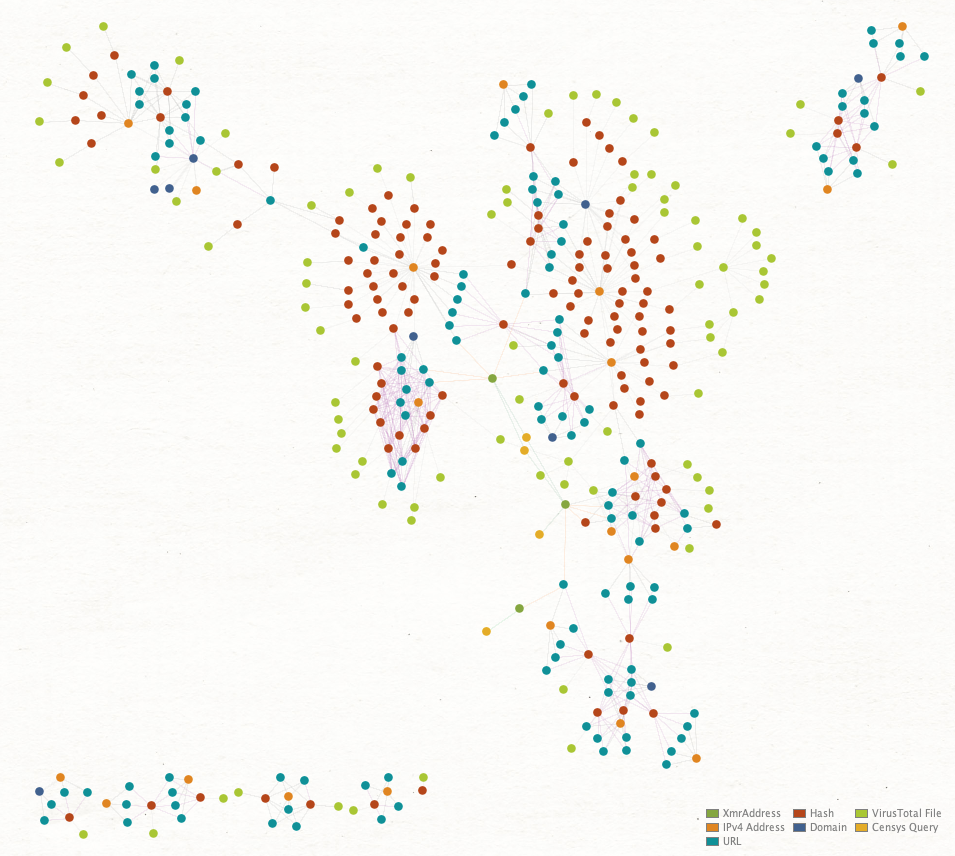
PaloAlto Network warns of the WatchDog botnet that uses exploits to take over Windows and Linux servers and mine cryptocurrency. Security researchers at Palo Alto Networks uncovered a cryptojacking botnet, tracked as WatchDog, that is targeting Windows and Linux systems. WatchDog is one of the largest and longest-lasting Monero cryptojacking operations uncovered by security experts, […]
 Pierluigi Paganini
February 18, 2021
The OpenSSL Project addressed three vulnerabilities, including two denial-of-service (DoS) issues and a bug in the SSLv2 rollback protection. The OpenSSL Project released security patches to address three vulnerabilities, two denial-of-service (DoS) flaws, and an incorrect SSLv2 rollback protection issue. The fist vulnerability, tracked as CVE-2021-23841, is a NULL pointer dereference issue that can be […]
 Pierluigi Paganini
February 17, 2021
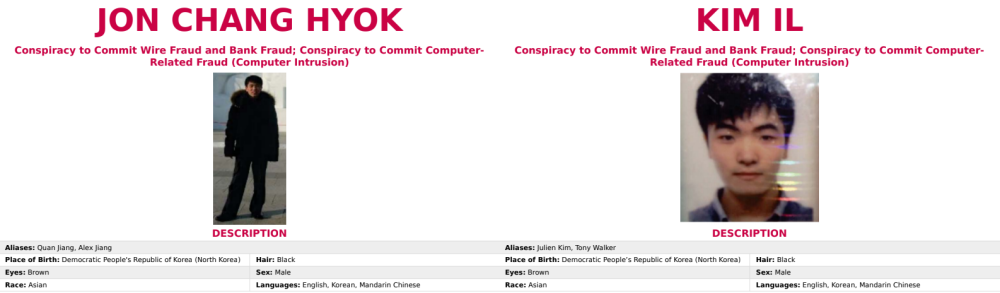
The US DOJ charged three members of the North Korea-linked Lazarus Advanced Persistent Threat (APT) group. The U.S. Justice Department indicted three North Korean military intelligence officials, members of the Lazarus APT group, for their involvement in cyber-attacks, including the theft of $1.3 billion in money and crypto-currency from organizations around the globe. The indictment […]
 Pierluigi Paganini
February 17, 2021
Malvertising gang ScamClub has exploited an unpatched zero-day vulnerability in WebKit-based browsers in a campaign aimed at realizing online gift card scams. The Malvertising gang ScamClub has abused an unpatched zero-day vulnerability in WebKit-based browsers to bypass security measures and redirect users from legitimate sites to websites hosting online gift card scams. The malvertising campaign […]
 Pierluigi Paganini
February 17, 2021
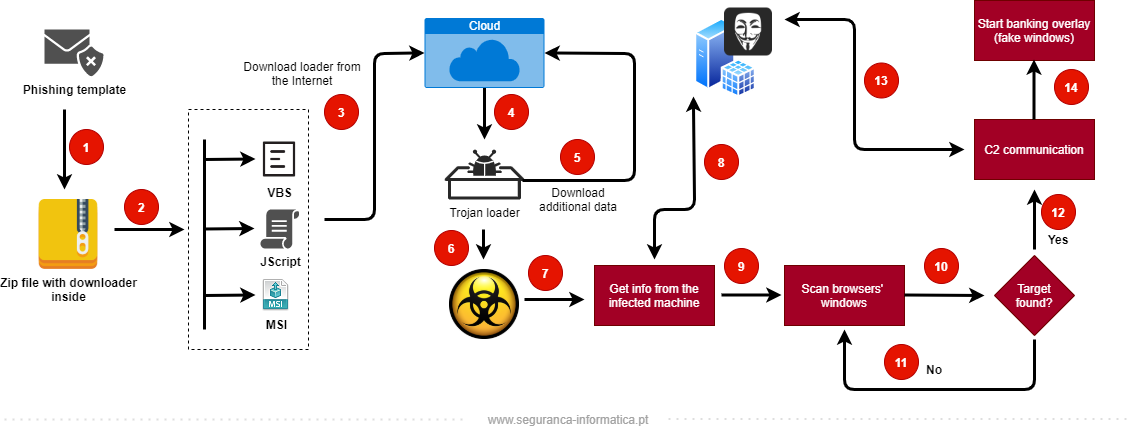
Latin American Javali trojan weaponizing Avira antivirus legitimate injector to implant malware In the last few years, many banking trojans developed by Latin American criminals have increased in volume and sophistication. Although exists a strong adoption of technologies with the goal of protecting the final user such as plugins, tokens, e-tokens, two-factor-authentication mechanisms, CHIP, PIN […]
 Pierluigi Paganini
February 16, 2021
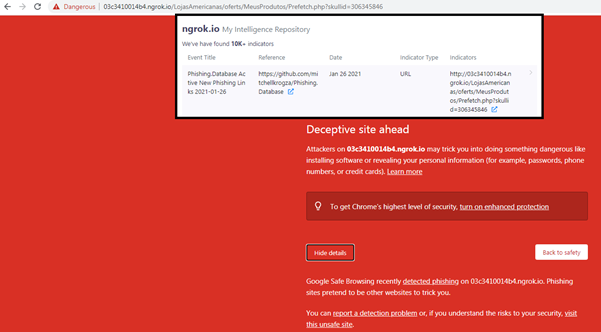
Researchers from threat intelligence Cyble have discovered threat actors abusing the Ngrok platform in a fresh phishing campaign. Researchers at the threat intelligence firm Cyble discovered a new wave of phishing attacks targeting multiple organizations that are abusing the ngrok platform, a secure and introspectable tunnel to the localhost. ngrok is a cross-platform application used to […]
 Pierluigi Paganini
February 16, 2021
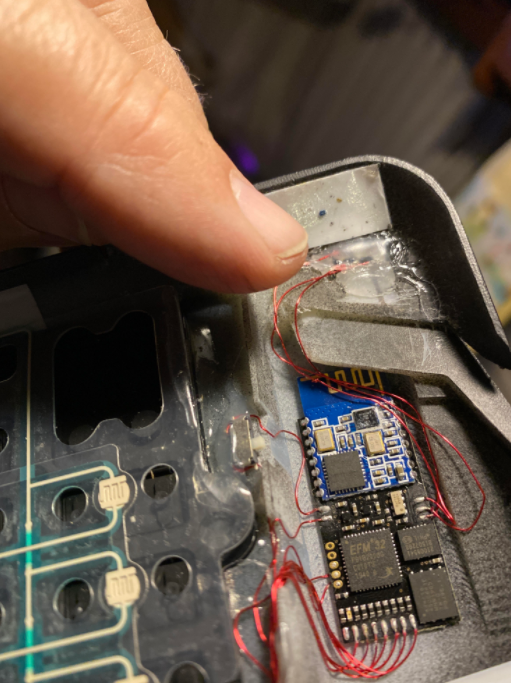
Experts discovered a new Bluetooth overlay skimmer that interferes with the ability of the terminal to read chip-based cards, forcing the use of the stripe. The popular investigator Brian Krebs reported the discovery of a new Bluetooth overlay skimmer that interfered with the terminal’s ability to read chip-based cards, forcing the use of the magnetic […]
 Pierluigi Paganini
February 15, 2021
VMware released security patches for a potentially serious vulnerability affecting the vSphere Replication product. VMware has recently released security patches to address a serious command injection vulnerability, tracked as CVE-2021-21976, in its vSphere Replication product. VMware vSphere Replication is an extension to VMware vCenter Server that provides hypervisor-based virtual machine replication and recovery. vSphere Replication […]
 Pierluigi Paganini
February 15, 2021
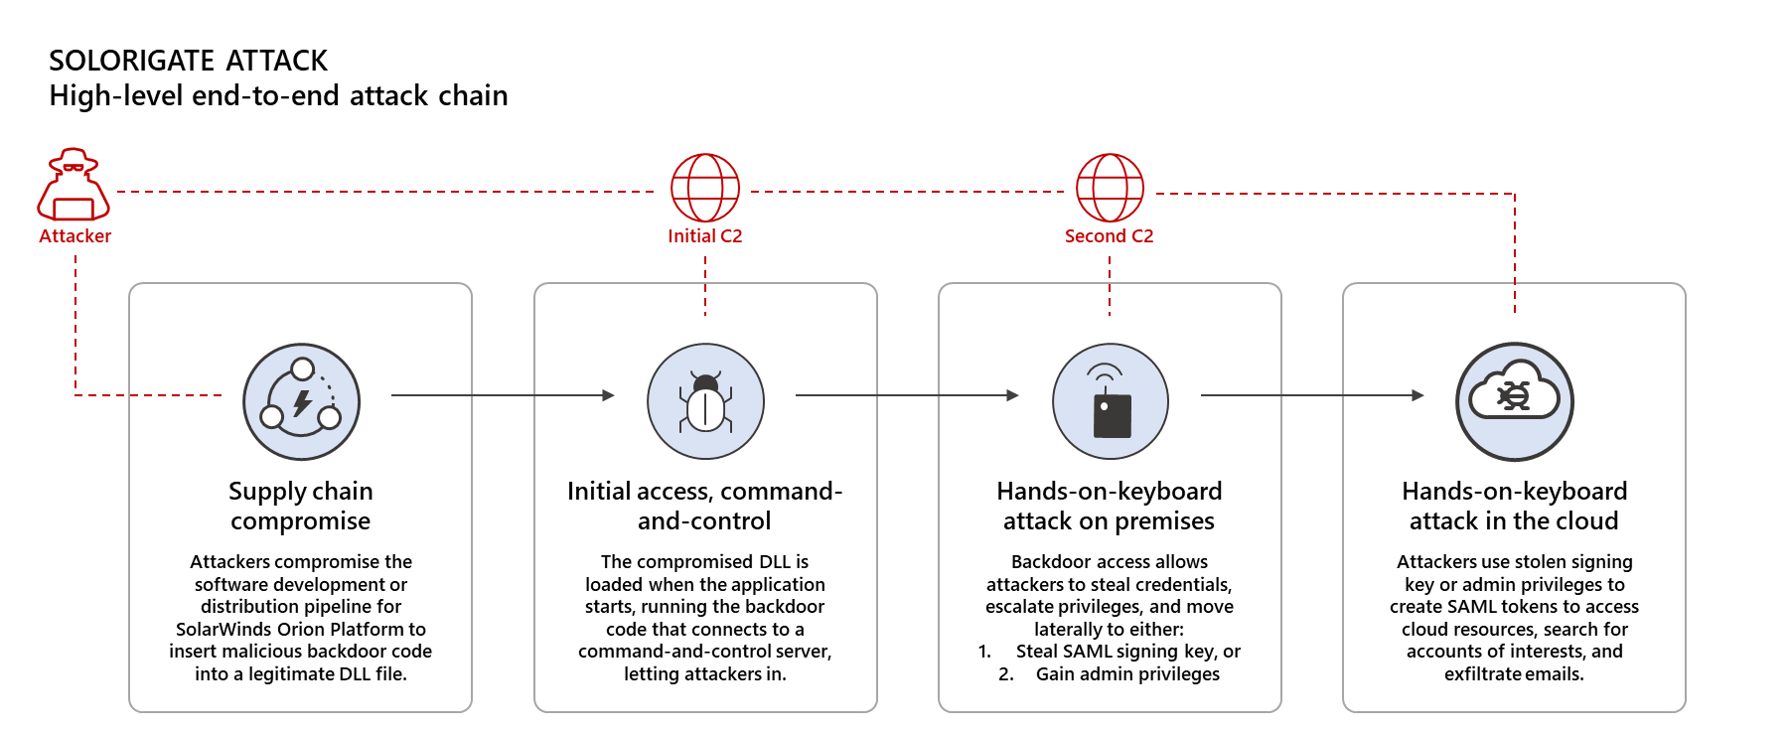
Microsoft says it found 1,000-plus developers’ fingerprints on the SolarWinds attack Microsoft’s analysis of the SolarWinds supply chain attack revealed that the code used by the threat actors was the work of a thousand developers. Microsoft president Brad Smith provided further details about the investigation of the SolarWinds supply chain attack, the company’s analysis of […]
 Pierluigi Paganini
February 15, 2021
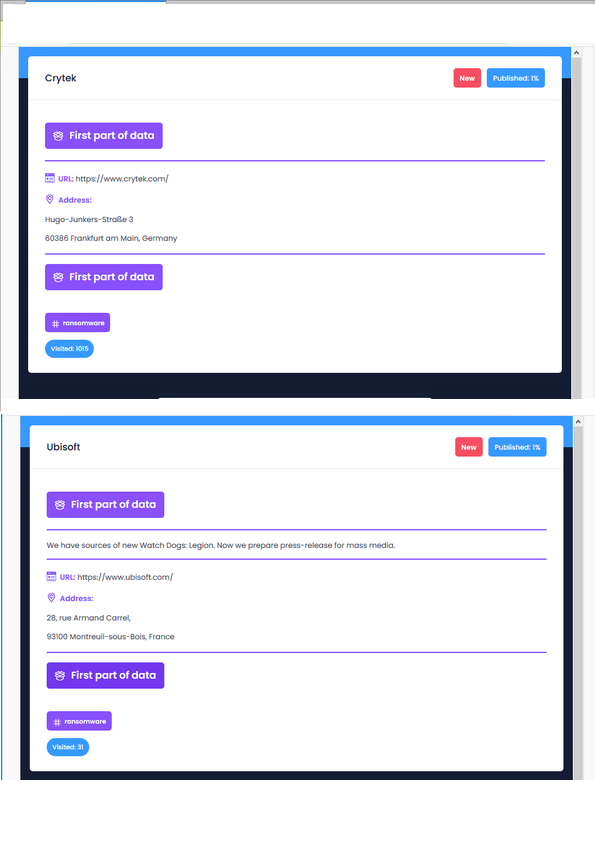
An international operation conducted in Ukraine and France lead to the arrest of criminals believed to be affiliated with the Egregor RaaS. Some affiliated with the Egregor RaaS, not the main ransomware gang, have been arrested as a result of a joint operation conducted by law enforcement in Ukraine and France. Authorities did not reveal […]