 Pierluigi Paganini
 March 12, 2020
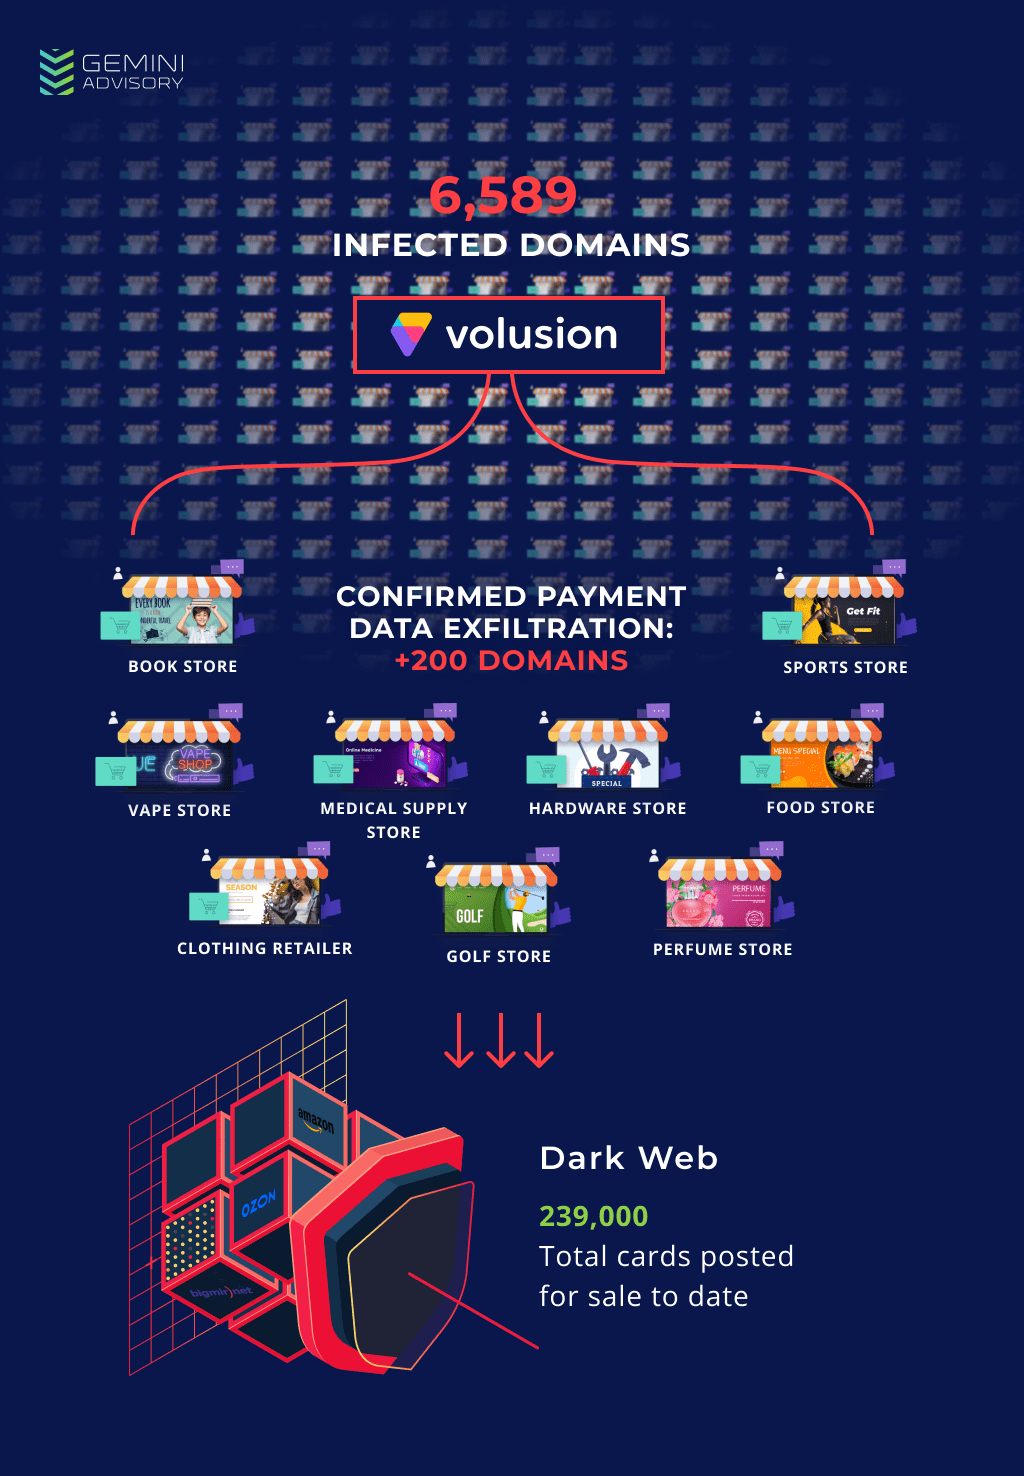
Security experts have discovered that card data stolen last year from Volusion-hosted online stores is now available for sale on the dark web. Experts from the threat intel firm Gemini Advisory have discovered that card data stolen last year from Volusion-hosted online stores have surfaced on the dark web. Volusion is a privately-held technology company that […]
 Pierluigi Paganini
March 11, 2020
Antivirus maker Avast has disabled a core component of its antivirus to address a severe vulnerability that would have allowed attackers to control users’ PC. The Antivirus maker Avast has disabled a major component of its antivirus engine to address a severe vulnerability that would have allowed attackers to hack into users’ PCs. The issue […]
 Pierluigi Paganini
March 11, 2020
The WordPress plugin ‘ThemeREX Addons’ is affected by a critical vulnerability that could allow remote attackers to execute arbitrary code. A critical vulnerability in the WordPress plugin known as ThemeREX Addons could be exploited for remote code execution. The plugin is currently installed on tens of thousands of websites and according to the security firm […]
 Pierluigi Paganini
March 11, 2020
The European Network of Transmission System Operators for Electricity (ENTSO-E) disclose a security breach this week. The European Network of Transmission System Operators for Electricity (ENTSO-E) revealed this week that threat actors penetrated its network. ENTSO-E, the European Network of Transmission System Operators, represents 43 electricity transmission system operators (TSOs) from 36 countries across Europe, […]
 Pierluigi Paganini
March 11, 2020
A flaw in the impacting Avast and AVG AntiTrack privacy software could expose users to browser hijacking and Man-in-The-Middle (MiTM) attacks. Security expert David Eade has discovered a vulnerability (CVE-2020-8987) in Avast and AVG AntiTrack privacy software that could expose end-users to Man-in-The-Middle (MiTM) attacks, browser session hijack, with consequent exposure of sensitive data. “A […]
 Pierluigi Paganini
March 10, 2020
Today Microsoft accidentally leaked info about a new wormable vulnerability (CVE-2020-0796) in the Microsoft Server Message Block (SMB) protocol. Today Microsoft accidentally leaked info on a security update for a wormable vulnerability in the Microsoft Server Message Block (SMB) protocol. The issue, tracked as CVE-2020-0796, is pre- remote code execution vulnerability that resides in the Server […]
 Pierluigi Paganini
March 10, 2020
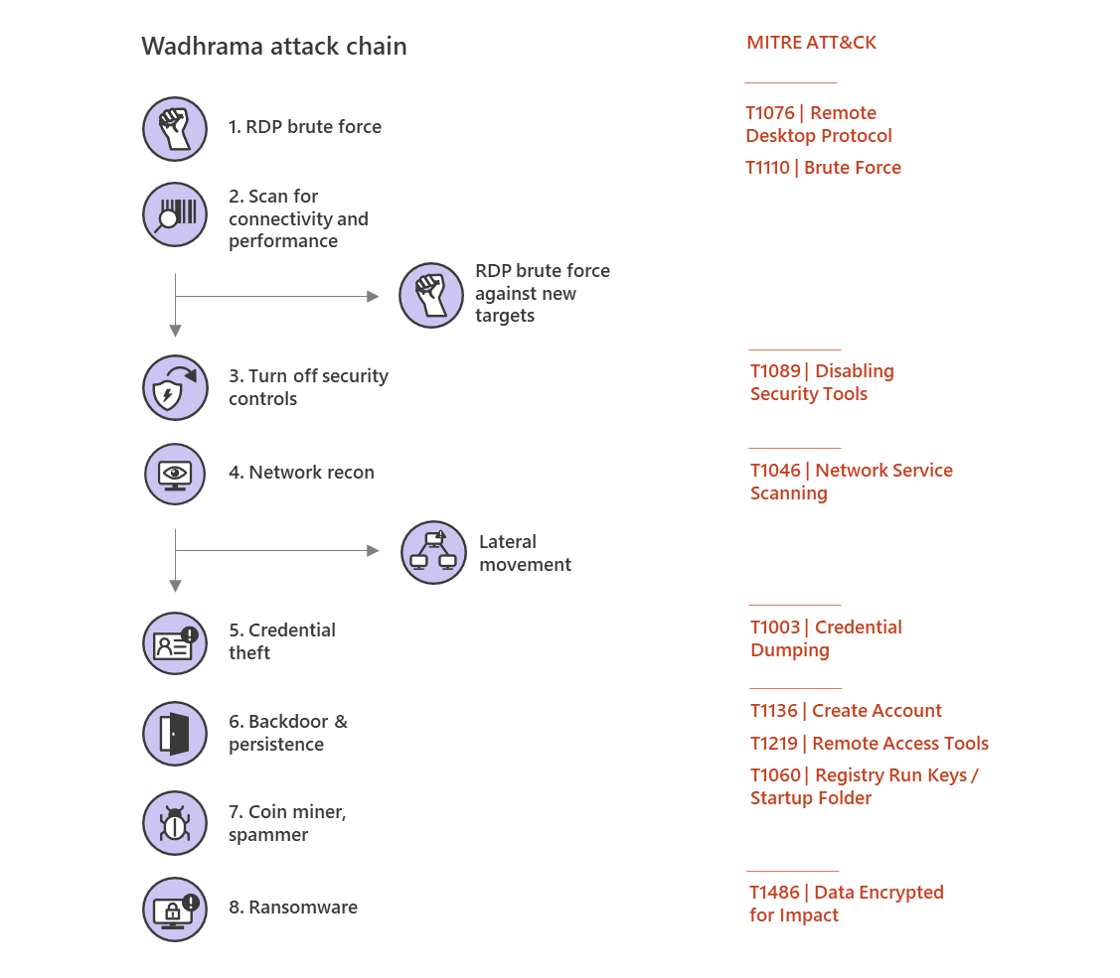
Microsoft is warning of human-operated ransomware, this kind of attack against businesses is becoming popular in the cybercrime ecosystem. Human-operated ransomware is a technique usually employed in nation-state attacks that is becoming very popular in the cybercrime ecosystem. In human-operated ransomware attack scenario, attackers use stolen credentials, exploit misconfiguration and vulnerabilities to access target networks, […]
 Pierluigi Paganini
March 08, 2020
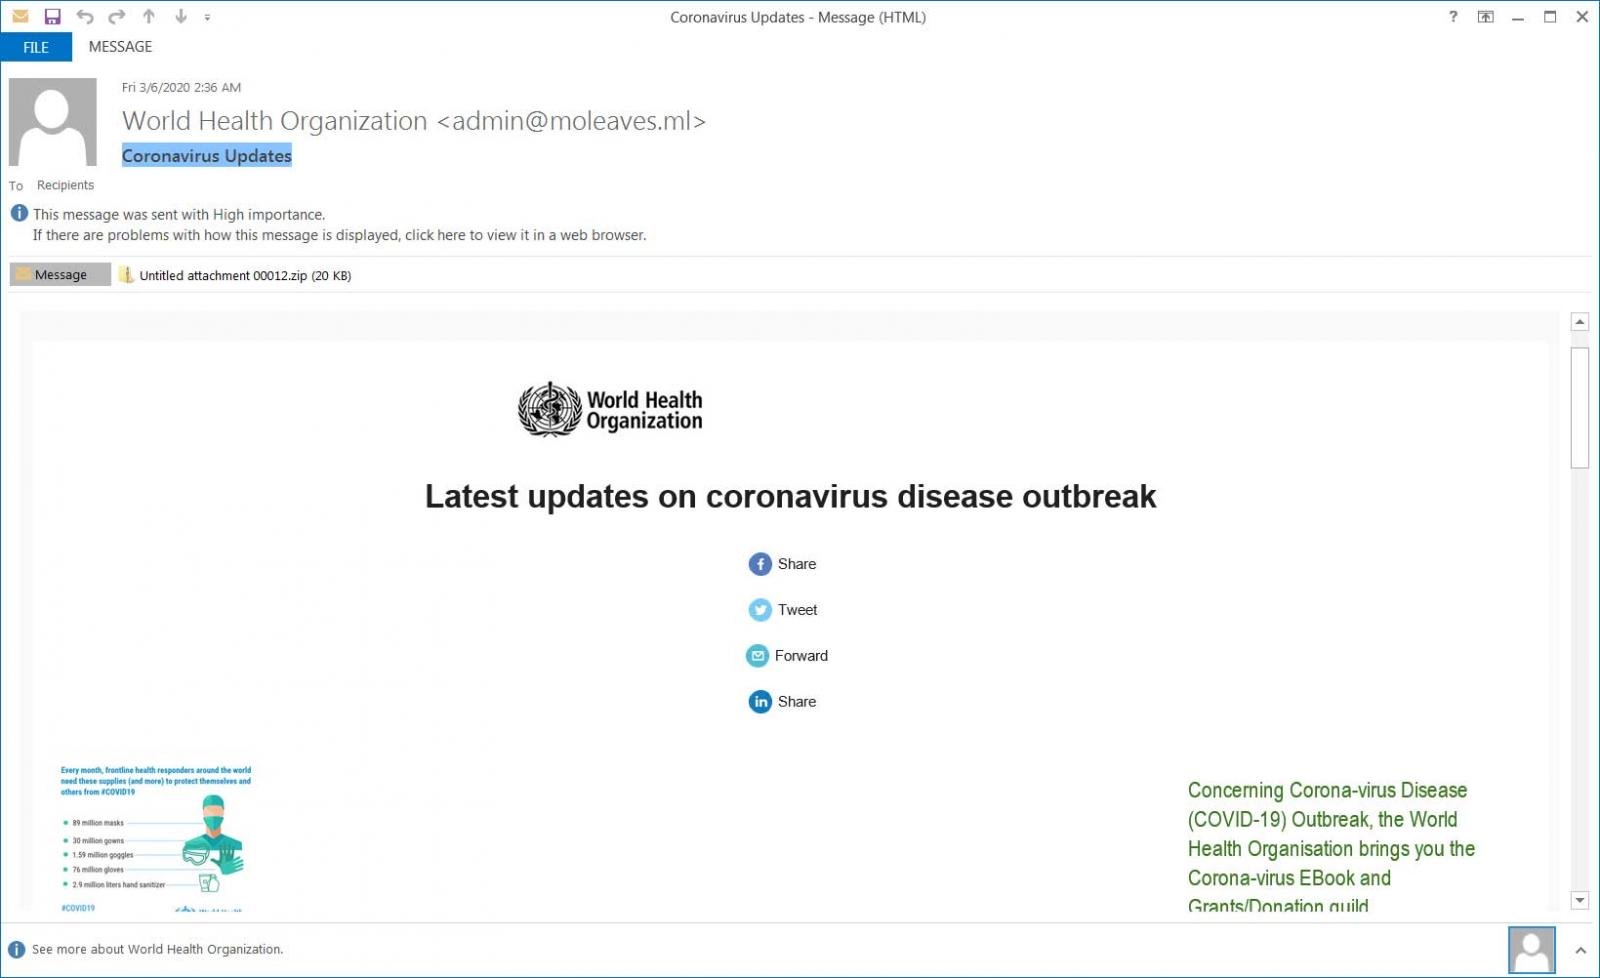
Experts uncovered a new Coronavirus (COVID-19)-themed campaign that is distributing a malware downloader that delivers the FormBook information-stealing Trojan. Experts at MalwareHunterTeam uncovered a new malspam campaign exploiting the fear in the Coronavirus (COVID-19) to deliver malware. The campaign uses emails that pretend being sent by members of the World Health Organization (WHO), the messages […]
 Pierluigi Paganini
March 05, 2020
New problems for the wireless carrier T-Mobile that disclosed a data breach that exposed some of the customers’ personal information. The wireless carrier T-Mobile was victims of a sophisticated cyber attack that targeted its email vendor. A data breach notification published by the telecommunications giant on its website revealed that the security breach impacted both employees […]
 Pierluigi Paganini
March 05, 2020
Cisco has released security updates to fix multiple vulnerabilities in various products, including two remote code execution flaws in Webex Player. The two remote code execution vulnerabilities fixed by Cisco have been tracked CVE-2020-3127 and CVE-2020-3128 respectively. The vulnerabilities have been rated as high severity and received a CVSS score of 7.8. The vulnerabilities are caused by the […]
Malware / September 25, 2026
Malware / September 25, 2026