


 Pierluigi Paganini
 December 11, 2019
Microsoft’s December 2019 Patch Tuesday updates fix a total of 36 flaws, including CVE-2019-1458 Windows zero-day exploited in North Korea-linked attacks Microsoft’s December 2019 Patch Tuesday updates address a total of 36 flaws, including a Windows zero-day, tracked as CVE-2019-1458 exploited in attacks linked to North Korea. The vulnerability could be exploited to execute arbitrary […]
 Pierluigi Paganini
December 10, 2019
Microsoft revealed that 44 million Microsoft Azure AD and Microsoft Services accounts were vulnerable to account hijacking. Microsoft discovered that 44 million Microsoft Azure AD and Microsoft Services accounts were vulnerable to account hijacking because of using of compromised passwords. Experts from the Microsoft threat research team analyzed a database containing 3 billion leaked credentials […]
 Pierluigi Paganini
December 10, 2019
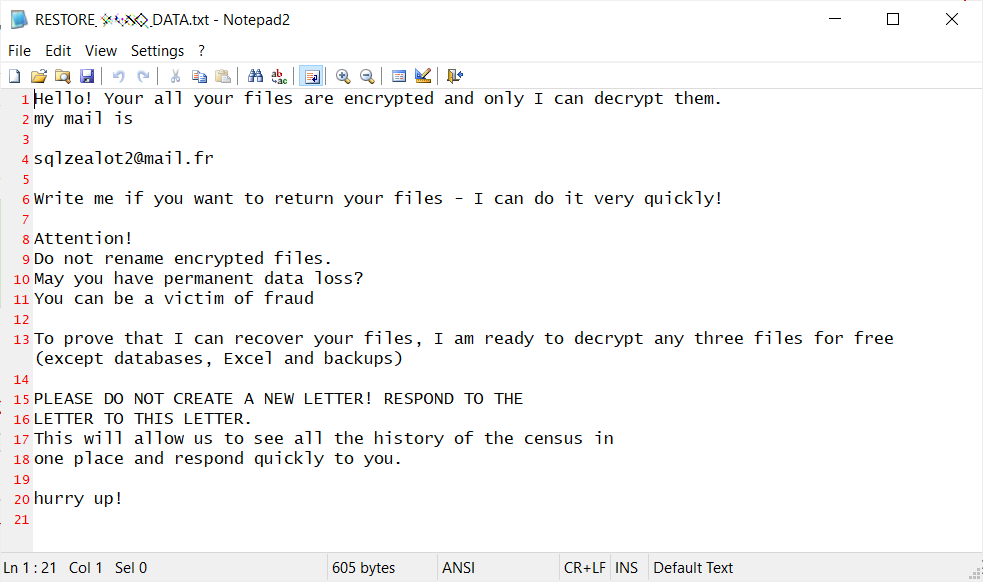
Experts spotted a new piece of the Snatch ransomware that reboots computers it infects into Safe Mode to bypass resident security solutions. Researchers discovered a new strain of the Snatch ransomware that reboots computers it infects into Safe Mode to bypass resident security solutions and encrypt files on the system. The malware attempts to exploit […]
 Pierluigi Paganini
December 10, 2019
The city of Pensacola, Florida, had been hit by a cyberattack, just days after a Saudi officer killed three American sailors at the city’s naval base. The city of Pensacola has been hit by a cyber attack over the weekend, the incident took place around 1:30 a.m. on Saturday. City IT staff has been working to restore […]
 Pierluigi Paganini
December 09, 2019
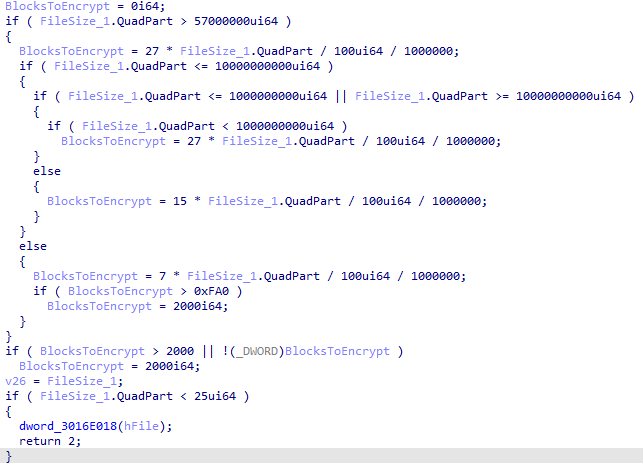
Emsisoft warns that a bug in the decrypter app of the Ryuk ransomware could damage large files making it impossible to decrypt them. Experts from Antivirus maker Emsisoft discovered a bug in the decrypter app of the infamous Ryuk ransomware. The app is provided by Ryuk operators to victims to recover their files once they […]
 Pierluigi Paganini
December 09, 2019
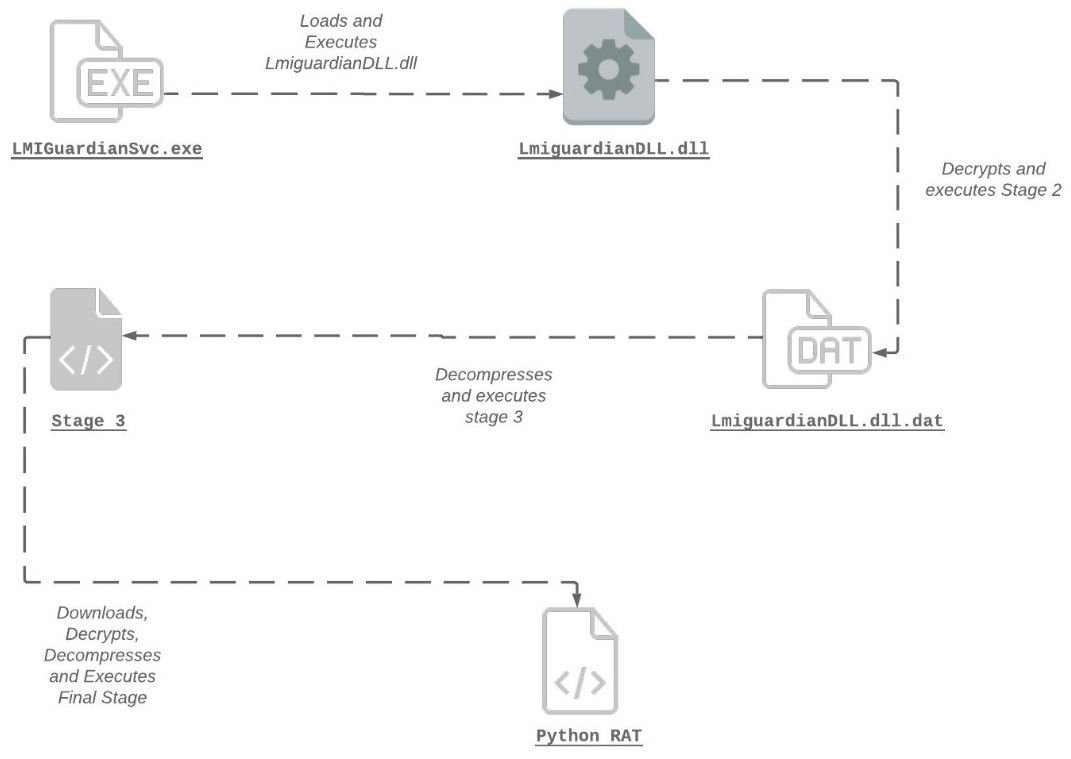
Researchers discovered a new Python-based RAT dubbed PyXie that has been used in campaigns targeting a wide range of industries. Experts at BlackBerry Cylance have spotted a new Python-based remote access Trojan (RAT) that has been used in campaigns targeting a wide range of industries. PyXie has been first observed in the wild in 2018, […]
 Pierluigi Paganini
December 09, 2019
Google addressed a critical vulnerability, tracked as CVE-2019-2232, that could trigger a permanent denial of service (DoS) condition in Android. Google released December 2019 security updates for its Android mobile OS that addressed several flaws, including a critical vulnerability, tracked as CVE-2019-2232, that could result in a permanent denial of service (DoS). Google addressed more […]
 Pierluigi Paganini
December 08, 2019
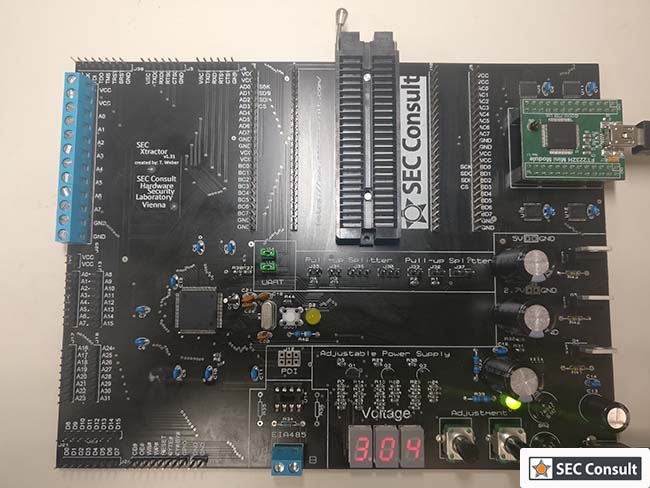
Security and consulting company SEC Consult announced the release of an open-source hardware analysis tool dubbed SEC Xtractor Security firm SEC Consult announced the release of an open-source hardware analysis tool dubbed SEC Xtractor. The tool was initially designed for internal use, and was then adopted for several research projects over the years. The tool […]
 Pierluigi Paganini
December 06, 2019
Researchers discovered a vulnerability tracked as CVE-2019-14899 that can be exploited to hijack active TCP connections in a VPN tunnel Researchers from the University of New Mexico have discovered a vulnerability, tracked as CVE-2019-14899, that can be exploited by an attacker to determine if a user is connected to a VPN and hijack active TCP […]
 Pierluigi Paganini
December 06, 2019
Experts from Qualys Research Labs discovered four high-severity security flaws in OpenBSD, one of which is a type authentication bypass issue. Researchers from Qualys Research Labs discovered four high-severity security vulnerabilities in OpenBSD, a type authentication bypass issue and three privilege escalation bugs. The three issued could be exploited by local users or malware to […]

Security / September 26, 2026
Malware / September 25, 2026
Malware / September 25, 2026


