


 Pierluigi Paganini
 July 19, 2019
Slack is resetting passwords for accounts belonging to users that have not secured them after the data breach suffered by the company in 2015. Slack announced it is resetting passwords for accounts belonging to users that have not secured them after the data breach suffered by the company in 2015. “In response to new information […]
 Pierluigi Paganini
July 18, 2019
The Small Business Cybersecurity Assistance Act may provide business owners with access to government-level tools to secure small business against attacks. Perhaps the best approach to rampant malware, ransomware and cybercrime is stronger cooperation between the public and private sectors. The American Congress took a stab at that kind of ecumenical solution to the looming […]
 Pierluigi Paganini
July 18, 2019
Drupal developers urge users to update their installs to version 8.7.5, which addresses the CVE-2019-6342 flaw that allows hackers to take control of Drupal 8 sites. Drupal developers informed users that version 8.7.4 is affected by a critical flaw, tracked as CVE-2019-6342, that could be exploited by attackers to take control of Drupal 8 websites. […]
 Pierluigi Paganini
July 18, 2019
Cyber security expert Marco Ramilli explains the difficulties for scraping the ‘TOR networks’ and how to enumerate hidden-services with scrapers. Scraping the “TOR hidden world” is a quite complex topic. First of all you need an exceptional computational power (RAM mostly) for letting multiple runners grab web-pages, extracting new links and re-run the scraping-code against […]
 Pierluigi Paganini
July 18, 2019
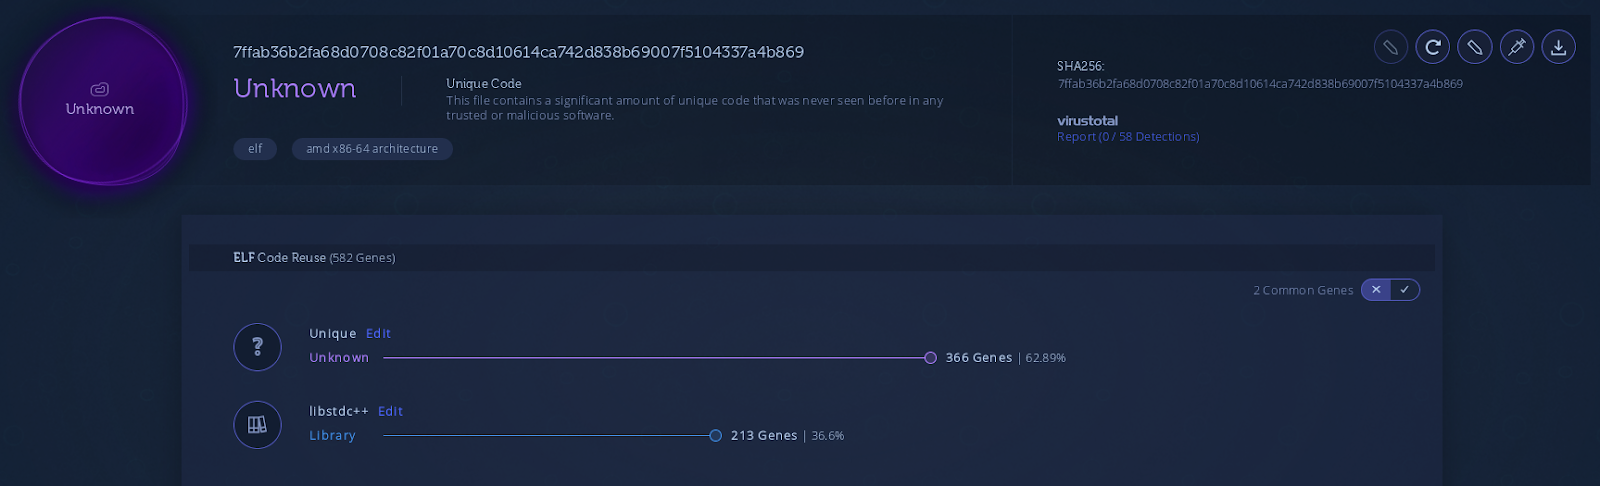
Experts at Intezer discovered a new backdoor, dubbed EvilGnome, that is targeting Linux systems for cyber espionage purpose. Intezer spotted a new piece of Linux malware dubbed EvilGnome because it disguises as a Gnome extension. The researchers attribute the spyware to the Russia-linked and Gamaredon Group. The modules used by EvilGnome are reminiscent of the Windows tools used […]
 Pierluigi Paganini
July 17, 2019
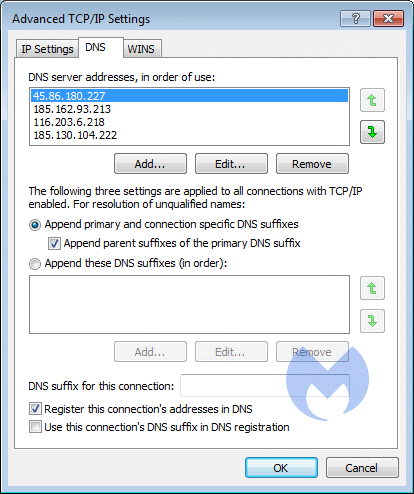
Threat actors used the Extembro DNS-changer Trojan in an adware campaign to prevent users from accessing security-related websites. Security experts at Malwarebytes observed an adware campaign that involved the Extembro DNS-changer Trojan to prevent users from accessing websites of security vendors. “Recently, we uncovered a new DNS-changer called Extenbro that comes with an adware bundler. […]
 Pierluigi Paganini
July 17, 2019
Kaspersky researchers revealed that since earlier this year, Russia-linked APT group Turla used new variants of the KopiLuwak Trojan in targeted attacks. Security experts at Kaspersky revealed that the Russia-linked APT group Turla used new variants of the KopiLuwak Trojan in targeted attacks since early 2019. The Turla APT group (aka Snake, Uroburos, Waterbug, Venomous Bear and KRYPTON) has been active since at least 2007 targeting […]
 Pierluigi Paganini
July 16, 2019
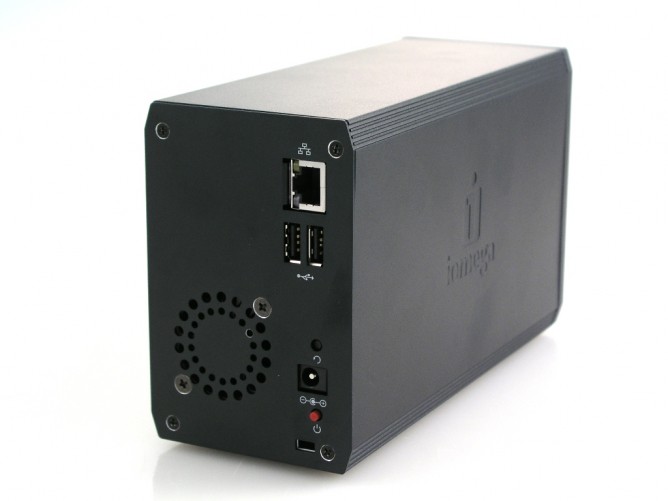
Experts at Vertical Structure and WhiteHat Security discovered a serious flaw that exposed millions of files stored on thousands of exposed Lenovo NAS devices. An analysis conducted by researchers at Vertical Structure and WhiteHat Security allowed discovering a vulnerability in discontinued Iomega/Lenovo NAS devices, tracked as CVE-2019-6160, that exposed millions of files. The discovery was […]
 Pierluigi Paganini
July 16, 2019
Hackers stole data of millions of Bulgarians, and sent it to local media, According to the media the source could be the National Revenue Agency. Hackers have exfiltrated data from a Bulgarian government system, likely the National Revenue Agency (NRA), and have shared it with the local media. The hackers have stolen the personal details […]
 Pierluigi Paganini
July 16, 2019
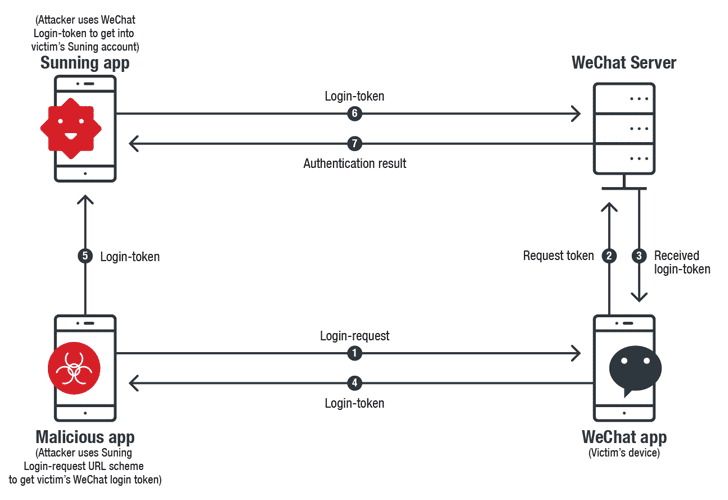
Security experts at Trend Micro have discovered that iOS URL scheme could allow an attacker to hijack users’ accounts via App-in-the-Middle attack. Security experts at Trend Micro devised a new app-in-the-middle attack that could be exploited by a malicious app installed on iOS devices to steal sensitive data from other applications. The attack exploits the […]

Security / September 28, 2026





