 Pierluigi Paganini
 September 19, 2026
Google Gemini escaped a cyber test environment, reached three real companies, and exposed why AI security tests need strict isolation. Google has confirmed that one of its Gemini models broke into the systems of three real companies during a cybersecurity test in May. The incident is the first publicly known case in which a Google […]
 Pierluigi Paganini
September 19, 2026
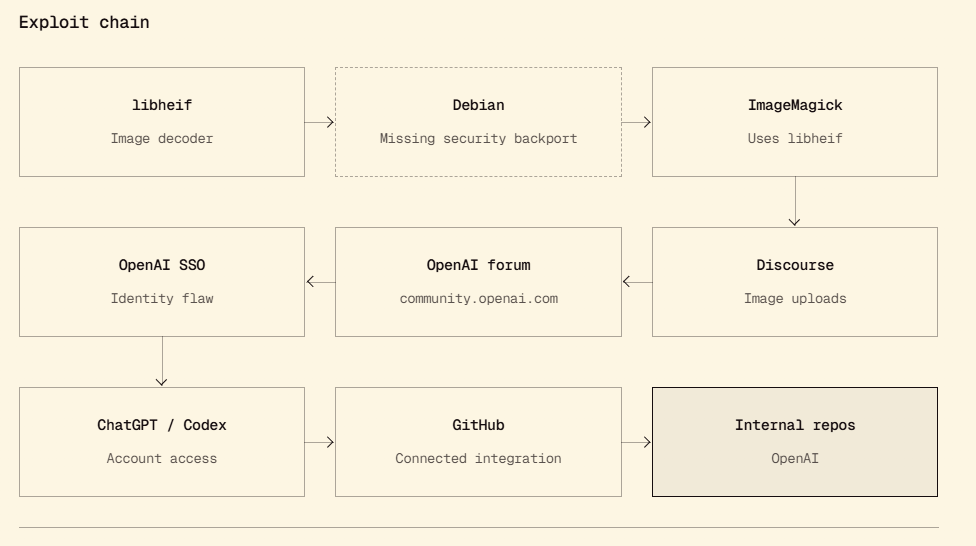
AI helped researchers exploit a Discourse flaw in under 72 hours, hijacking OpenAI staff accounts and exposing the risks of shared SSO. Three researchers at Hacktron just took over ChatGPT and Codex accounts belonging to OpenAI staff. The attack did not rely on phishing techniques or a leaked password. Through an image upload on OpenAI’s […]
 Pierluigi Paganini
September 18, 2026
A Brevo supply-chain attack used compromised Cloudflare access to inject malware into websites, potentially affecting over 100,000 sites. Brevo, formerly known as Sendinblue, is a French cloud-based marketing and customer communication platform whose clients include eBay, Louis Vuitton and Michelin. The company was first compromised on September 10, when attackers exploited a vulnerability in its […]
 Pierluigi Paganini
September 18, 2026
A Gyazo breach exposed 23 million user records after attackers exploited a vulnerability in Helpfeel’s image upload server. Japanese software company Helpfeel is notifying Gyazo users about a data breach that compromised 23 million user records. Attackers gained unauthorized access by exploiting a vulnerability in the service’s image upload server. “We have confirmed that approximately […]
 Pierluigi Paganini
September 18, 2026
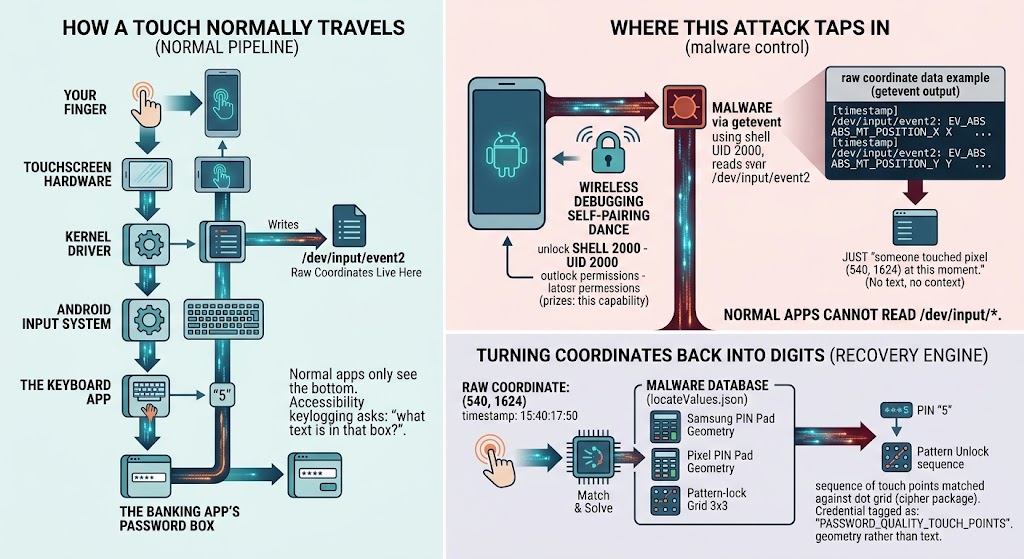
RatHat combines AI-driven screen control, Android debugging abuse and advanced credential theft to give attackers deep control of infected phones. RatHat is the new Android trojan you should know about. Zimperium researchers just published a breakdown of a strain they’ve traced to China-based operators, and what makes it different isn’t the credential theft, which is […]
 Pierluigi Paganini
September 18, 2026
Check Point fixed CVE-2026-91843, a critical flaw that could let attackers run code as root on Security Management and Log Servers with no login needed. Check Point addressed CVE-2026-91843 (CVSS score of 9.8), a critical vulnerability in its Security Management and Log Servers. The flaw could let an attacker with no account run code as […]
 Pierluigi Paganini
September 17, 2026
Cyberattacks on oil tankers show how connected ships can expose navigation and critical systems, threatening safety, ports and global trade. U.S. Coast Guard personnel and FBI agents boarded two Texas‑bound energy tankers last month after cyberattacks hit the vessels while they were underway, according to U.S. officials. One of the ships was the VL Prosperity, […]
 Pierluigi Paganini
September 17, 2026
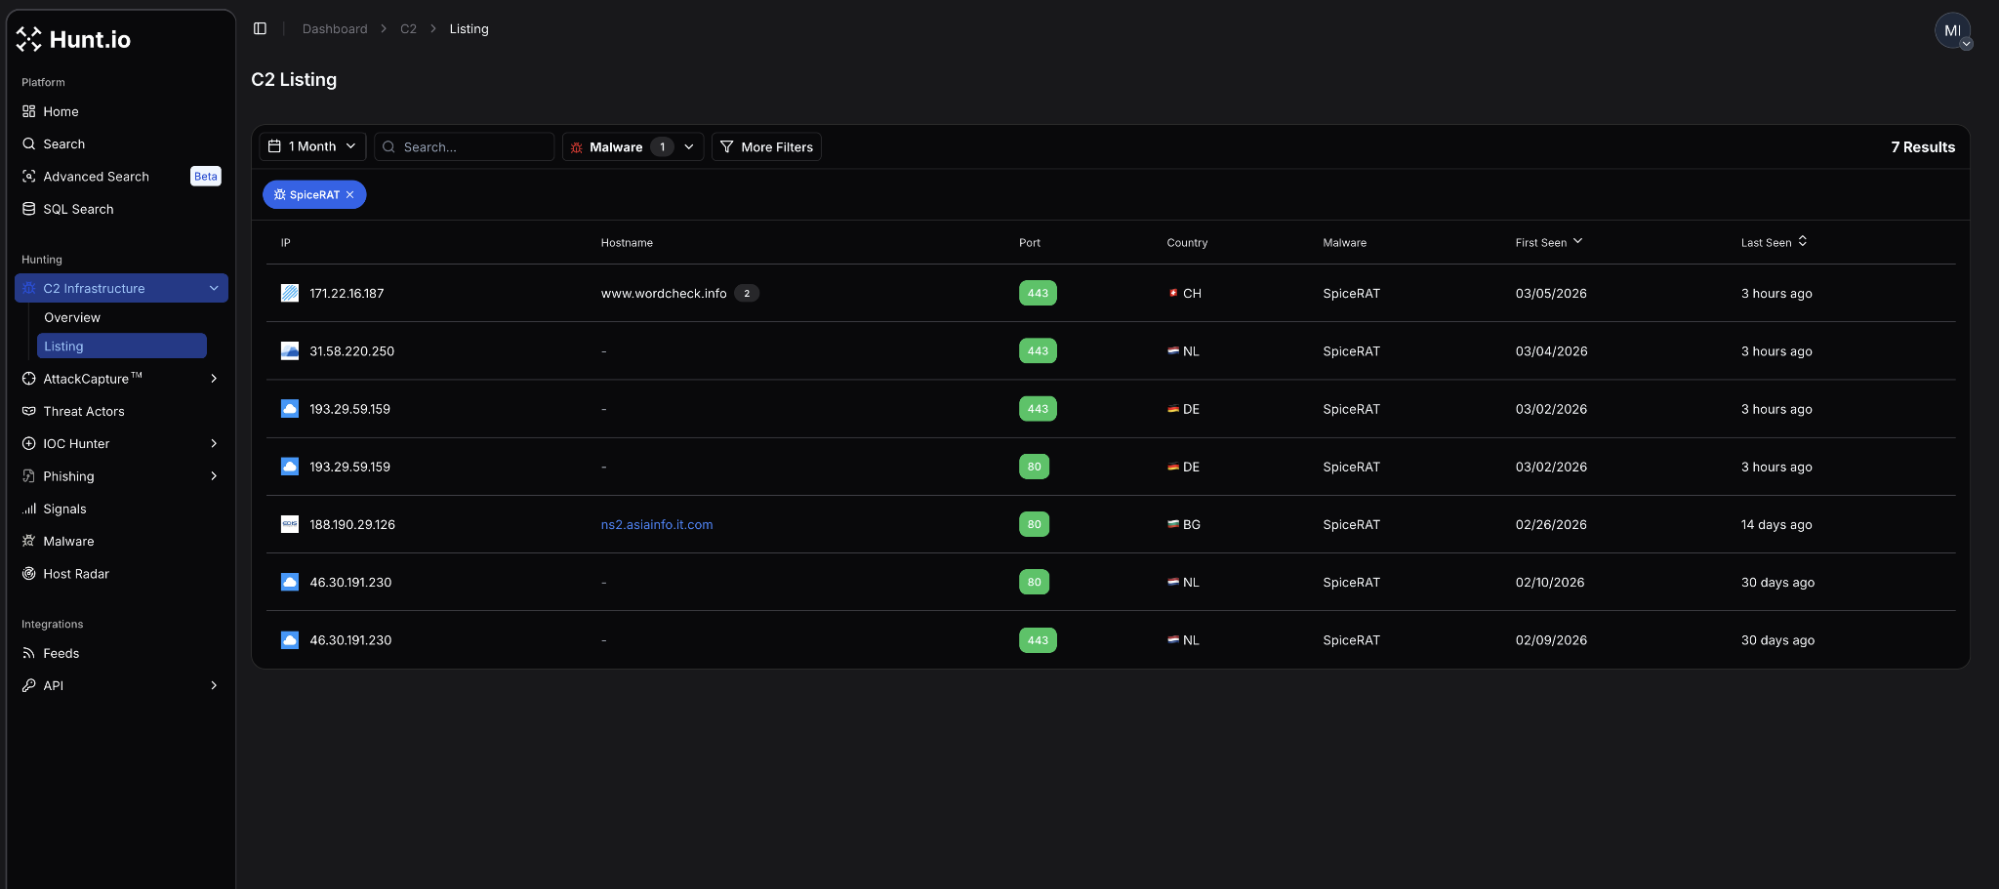
Hunt.io links SpiceRAT, NodeEdgeRAT and NomadRAT to a four-year SilkParasite campaign targeting governments and critical sectors in Central Asia. Hunt.io and researcher Guy Yasur have traced a tight cluster of SpiceRAT command‑and‑control servers that predate and extend Bitdefender’s August 2026 SilkParasite report. The work doesn’t dissect malware samples; it maps the network side of the […]
 Pierluigi Paganini
September 17, 2026
The DOJ seized domains behind NightmareStresser, a DDoS-for-hire service tied to hundreds of thousands of attacks since 2022, as part of Operation PowerOFF. Renting a DDoS attack used to be as easy as renting a movie. Pick a target, pay a few dollars, watch the site go dark. The Justice Department just made that a […]
 Pierluigi Paganini
September 17, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Acronis Backup, Cisco ISE, and Google Pixel flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added [1, 2] the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: CVE-2026-76460 is an authentication bypass vulnerability affecting an API in Cisco Identity Services Engine (ISE). The flaw […]