 Pierluigi Paganini
 May 31, 2016
According to the security firm High-Tech Bridge many of the Alexa Top 10,000 websites are still vulnerable to the OpenSSL flaw CVE-2016-2107. The CVE-2016-2107 flaw affecting the open-source cryptographic library could be exploited to launch a man-in-the-middle attack leveraging on the ‘Padding Oracle Attack’ that can decrypt HTTPS traffic if the connection uses AES-CBC cipher and the server supports AES-NI. According […]
 Pierluigi Paganini
May 30, 2016
Malware researchers are warning Android’s latest permission-granting model in version 6.0 Marshmallow is now been targeted by Mobile malware authors. Android’s latest permission-granting model in version 6.0 Marshmallow is now been targeted by Mobile malware authors. The model will let users grant permissions only when it is required by the app, rather be accepting all […]
 Pierluigi Paganini
May 30, 2016
The US Computer Emergency Response Team has issued a warning after the discovery a security issue the popular medical application MEDHOST PIMS (PIMS). Many security experts believe that medical industry lack of a proper security posture, despite it is a high-tech sector the vast majority of medical equipment was not designed with a security by design […]
 Pierluigi Paganini
May 30, 2016
Mikko Hypponen does not need any introduction, he is a true star, one of those professionals who have indelibly marked the evolution of the cyber security industry. I consider Mikko a legend, and I’m happy to share with you this interview. Enjoy it! Hi Mikko, you are a legend of the hacking community, can […]
 Pierluigi Paganini
May 29, 2016
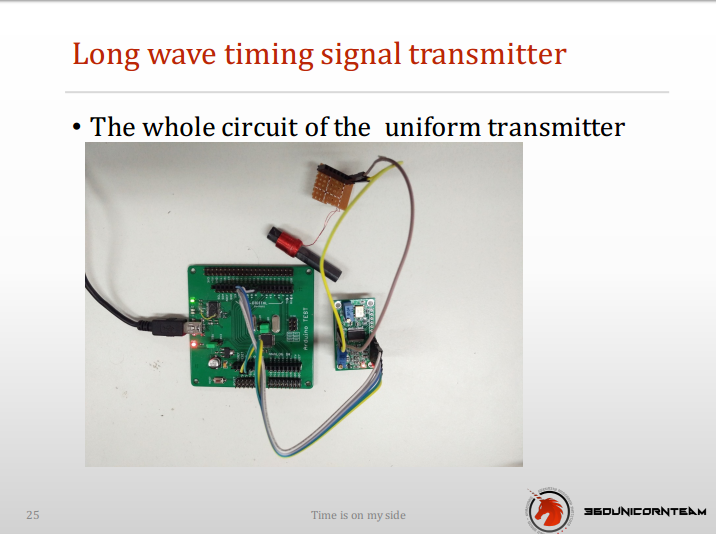
A couple of experts demonstrated how to wirelessly change the time on NTP servers over long distances using an inexpensive equipment. The HACK IN THE BOX conference is a hotbed of interesting hacks, today I will present you the results of a research conducted by the researchers Yuwei Zheng and Haoqi Shan from Qihoo360 firm that explained […]
 Pierluigi Paganini
May 28, 2016
The hacker Peace is offering for sale hundred Million stolen MySpace Passwords on the black marketplace. This is one of the greatest leaks of ever. A few days ago a hacker with the nickname “Peace” offered for sale on the black market 117 million LinkedIn account credentials. The same hacker is offering for sale 360 million emails and […]
 Pierluigi Paganini
May 27, 2016
A fourth Bank in Philippines was a victim of the SWIFT hackers and experts at Symantec confirmed the malware shares code with tools used by the Lazarus group. The list of banks victims of the SWIFT hackers is lengthening, a fourth bank in the Philippines has been a victim of the crew that targeted the SWIFT interbank transfer system. […]
 Pierluigi Paganini
May 27, 2016
The security expert Chilik Tamir from Mi3 Security has devised a new attack dubbed SandJacking to install rogue apps on iOS devices. The security expert Chilik Tamir from Mi3 Security has devised some new attack methods that can be exploited by threat actors to install malicious apps on non-jailbroken iOS devices. Tamir presented his attack methods at […]
Pierluigi Paganini
May 26, 2016
Dozens of HTTPS-protected websites belonging to Visa are vulnerable to Forbidden Attack, nearly 70,000 servers are at risk. A new attack technique dubbed ‘Forbidden attack’ expose dozens of HTTPS Visa sites vulnerable to cyber attacks and roughly another 70,000 servers are at risk. A group of international researchers (Hanno Böck, Aaron Zauner, Sean Devlin, Juraj Somorovsky, […]
 Pierluigi Paganini
May 26, 2016
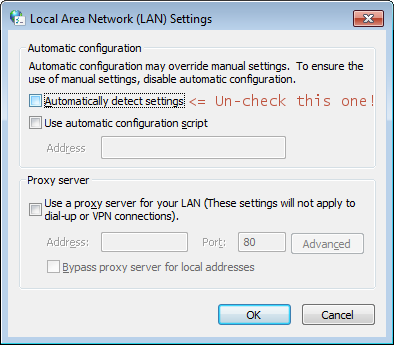
Leaked WPAD queries could result in domain name collisions with internal network naming schemes exposing corporate to MITM attacks. The U.S. Computer Emergency Readiness Team(US-CERT) issued the Alert (TA16-144A) to warn of leaked WPAD queries could result in domain name collisions with internal network naming schemes. The WPAD queries are intended for resolution on private or enterprise DNS […]