 Pierluigi Paganini
 February 04, 2022
Office 365 and Azure Active Directory (Azure AD) customers were the targets of billions of brute-force and phishing attacks last year. Microsoft revealed that Office 365 and Azure Active Directory (Azure AD) customers were the targets of billions of phishing emails and brute force attacks last year. The IT giant added has blocked more than 25.6 billion Azure AD […]
 Pierluigi Paganini
February 03, 2022
Six years ago the Powerful Greek Army (PGA) appeared in the threat landscape. After a long breach the hacker collective is back. I have interviewed them in exclusive … enjoy it! Tell me about your hacker team, which is the motivation behind the attacks? We have many motivations and reasons. First of all, we started […]
 Pierluigi Paganini
February 03, 2022
A China-linked APT group tracked as Antlion used a custom backdoor called xPack that was undetected for months. A China-linked APT group tracked as Antlion is using a custom backdoor called xPack in attacks aimed at financial organizations and manufacturing companies, Symantec researchers reported. The backdoor was undetected for at least 18 months in a […]
 Pierluigi Paganini
February 03, 2022
A cyber attack hit the oil terminals of some of the biggest European ports impacting their operations. Some of the major oil terminals in Western Europe’s biggest ports have been targeted with a cyberattack. Threat actors have hit multiple oil facilities in Belgium’s ports, including Antwerp, which is the second biggest port in Europe after […]
 Pierluigi Paganini
February 03, 2022
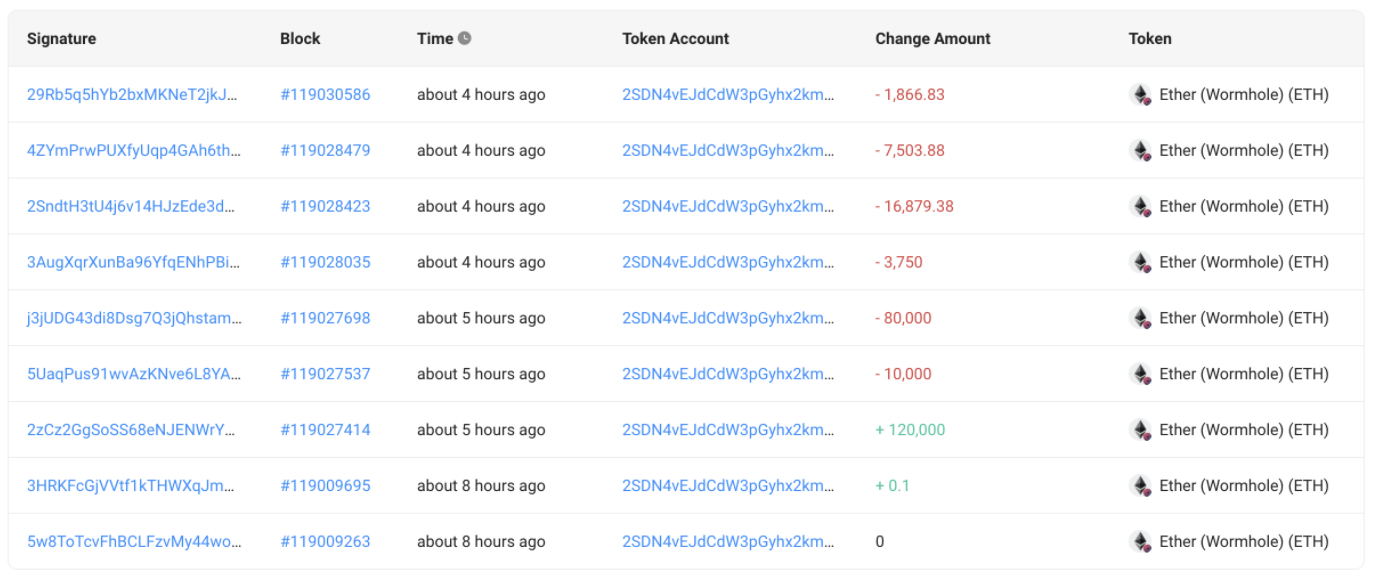
Threat actors have stolen $325 million in cryptocurrency leveraging a bug in the Wormhole communication bridge. Wormhole, one of the most popular bridges that links the Ethereum and Solana blockchains, lost about $325 million in an attack that took place on Wednesday. This is the second-biggest hack of a DeFi platform ever, just after the $600 […]
 Pierluigi Paganini
February 03, 2022
Trend Micro recently addressed two high-severity flaws affecting some of its hybrid cloud security products. Trend Micro released security updates to fix two high-severity vulnerabilities, tracked as CVE-2022-23119 and CVE-2022-23120, affecting some of its hybrid cloud security products. The vulnerabilities affect Deep Security and Cloud One workload security solutions. The flaws were reported by the cybersecurity […]
 Pierluigi Paganini
February 02, 2022
Cyber security team at retail giant Walmart dissected a new ransomware family dubbed Sugar, which implements a ransomware-as-a-service model. The cyber threat team at retail giant Walmart has analyzed a new ransomware family dubbed Sugar, which is offered through a ransomware-as-a-service (RaaS) model. Unlike other ransomware operations, Sugar ransomware appears to primarily focus on individual […]
 Pierluigi Paganini
February 02, 2022
Antivirus firm ESET addressed a local privilege escalation vulnerability, tracked CVE-2021-37852, impacting its Windows clients. Antivirus firm ESET released security patches to address a high severity local privilege escalation vulnerability, tracked CVE-2021-37852, impacting its Windows clients. An attacker can exploit the vulnerability to misuse the AMSI scanning feature to elevate privileges in specific scenarios. “According […]
 Pierluigi Paganini
February 02, 2022
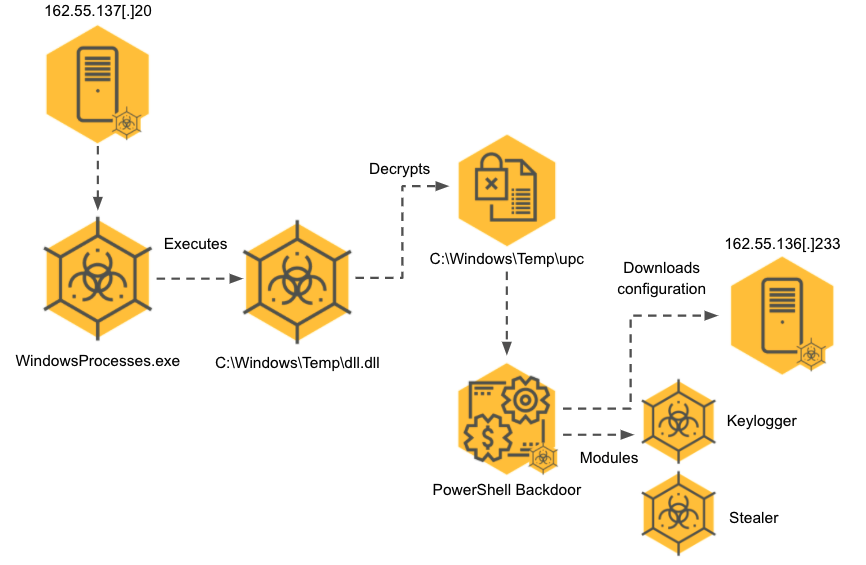
The Cybereason Nocturnus Team reported a spike in the activity of the Iran-linked APT group APT35 (aka Phosphorus or Charming Kitten). The Cybereason Nocturnus Team observed a spike in the activity of the Iran-linked APT group APT35 (aka ‘Charming Kitten‘, ‘Phosphorus‘, Newscaster, and Ajax Security Team) The Phosphorus group made the headlines in 2014 when experts at iSight issued a report describing the most elaborate net-based spying campaign organized […]
 Pierluigi Paganini
February 02, 2022
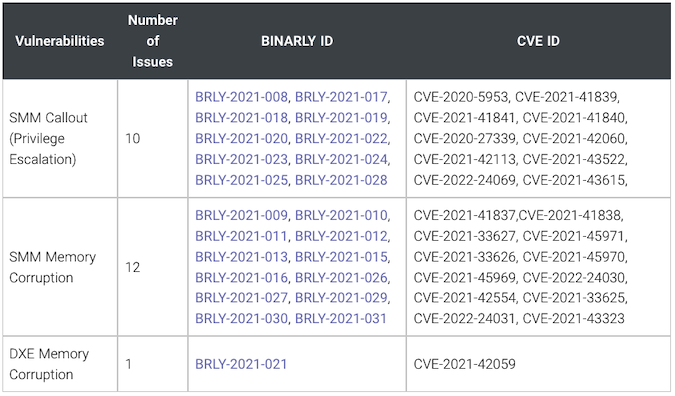
Researchers discovered tens of vulnerabilities in UEFI firmware code used by the major device manufacturers. Researchers at firmware security company Binarly have discovered 23 vulnerabilities in UEFI firmware code used by the major device makers. The vulnerabilities could impact millions of enterprise devices, including laptops, servers, routers, and industrial control systems (ICS). All these vulnerabilities […]
Artificial Intelligence / September 29, 2026
Artificial Intelligence / September 28, 2026