 Pierluigi Paganini
 January 15, 2022
One of the biggest underground carding marketplaces, UniCC, announced it’s shutting down its operations. UniCC, one of the biggest underground carding marketplaces announced it is shutting down. The site was launched in 2013 and according to the Elliptic Threat Intel about $358 million (across Bitcoin, Litecoin, Ether and Dash) in purchases were made through the […]
 Pierluigi Paganini
January 15, 2022
A senior Biden administration official said that the one of the Russian hacker arrested by FSB was behind the Colonial Pipeline attack. Yesterday, the Russian Federal Security Service (FSB) announced to have dismantled the REvil ransomware operation and arrested 14 alleged members of the gang. The group that is behind a long string of attacks […]
 Pierluigi Paganini
January 14, 2022
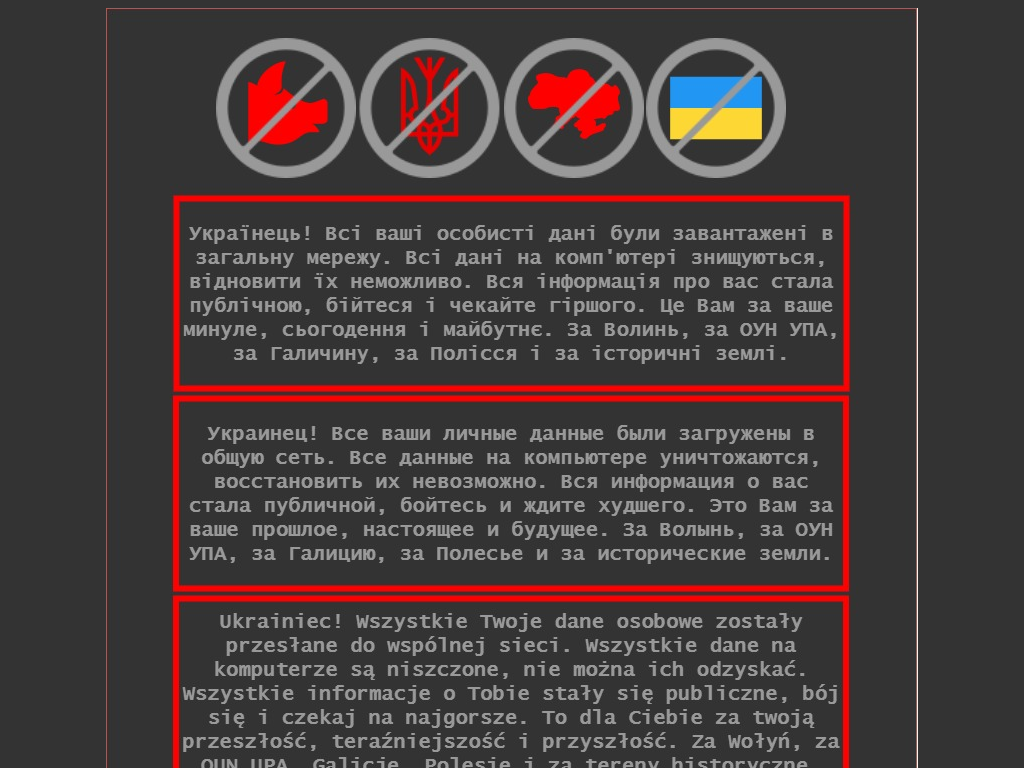
Threat actors defaced multiple Ukrainian government websites after talks between Ukrainian, US, and Russian officials hit a dead this week. Threat actors have defaced multiple websites of the Ukrainian government on the night between January 13 and January 14. The attacks were launched after talks between Ukrainian, US, and Russian officials hit a dead end on Thursday. The […]
 Pierluigi Paganini
January 14, 2022
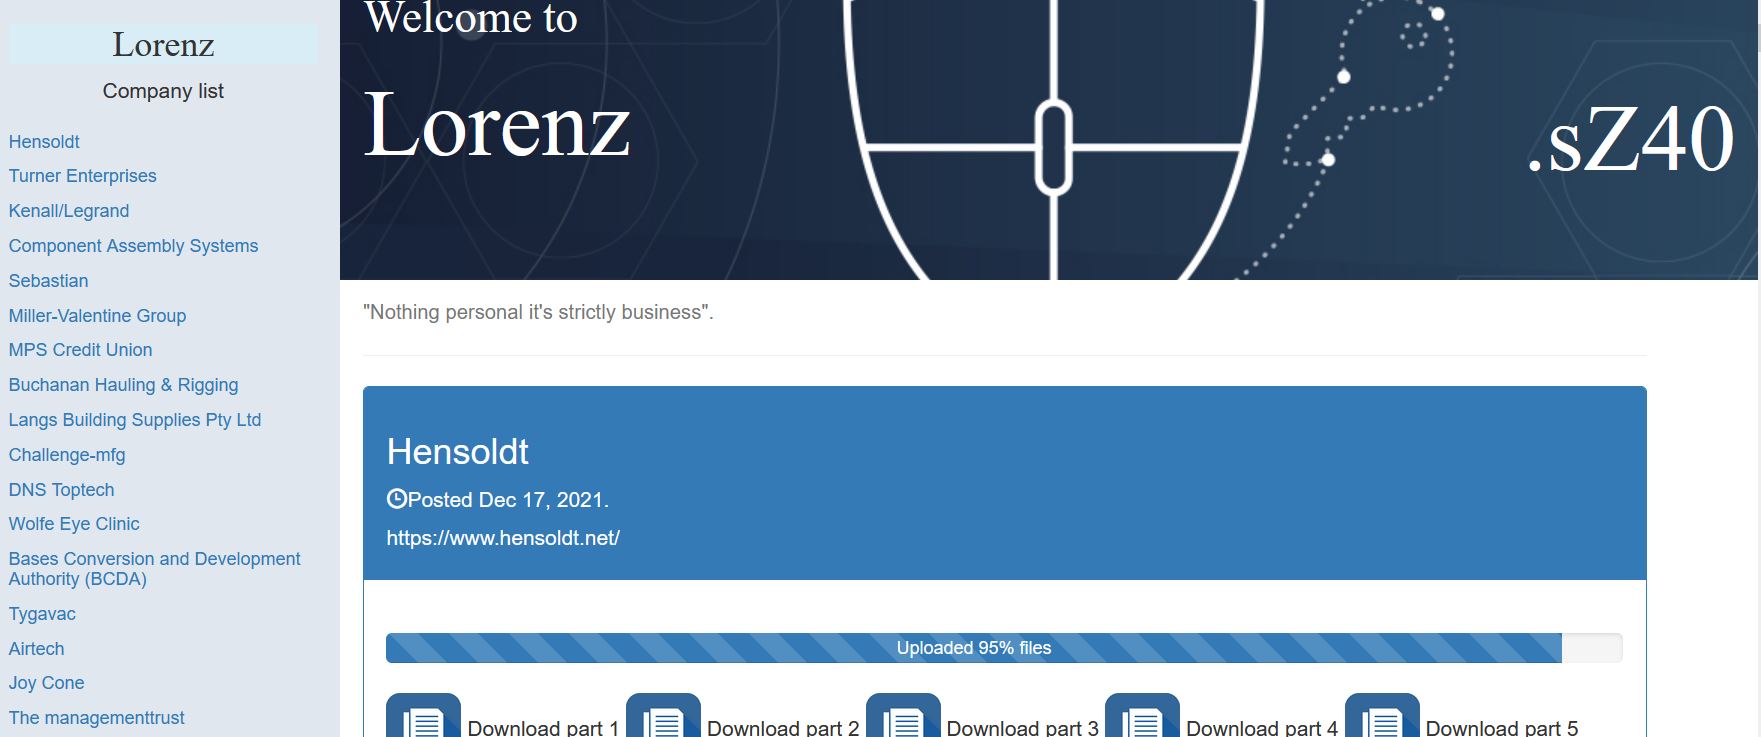
German multinational defense contractor Hensoldt confirmed to that some of its systems were infected by Lorenz ransomware. Hensoldt, a multinational defense contractor, confirmed that some of its UK subsidiary’s systems were infected with Lorenz ransomware. This week a Hensholdt spokesperson confirmed the security breach to BleepingComputer explaining that a small number of mobile devices in its […]
 Pierluigi Paganini
January 14, 2022
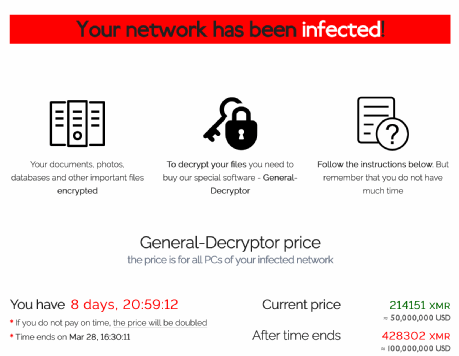
Russia’s FSB announced to have dismantled the REvil ransomware gang, the infamous group behind Kaseya and JBS USA. The Russian Federal Security Service (FSB) announced to have shut down the REvil ransomware gang, the group that is behind a long string of attacks against large organizations, such as Kaseya and JBS USA. The FSB claims to have […]
 Pierluigi Paganini
January 14, 2022
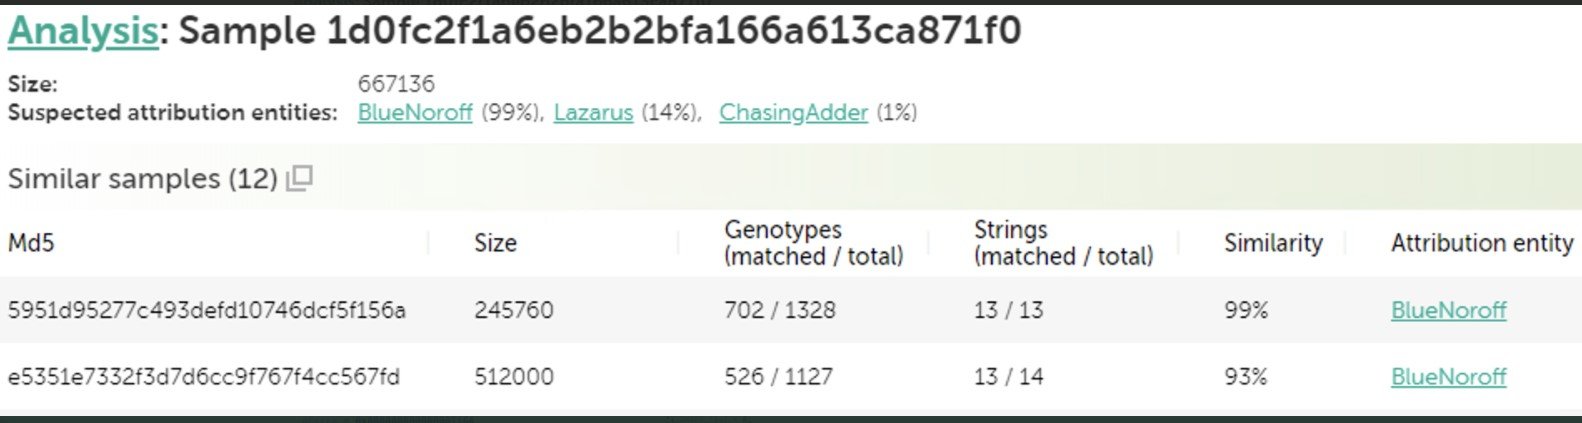
The North Korea-linked APT group BlueNoroff has been spotted targeting cryptocurrency startups with fake MetaMask browser extensions. The North Korea-linked APT group BlueNoroff has been spotted targeting cryptocurrency startups with fake MetaMask browser extensions. The nation-state actor is considered a group that operates under the control of the notorious North Korea-linked Lazarus APT group. The […]
 Pierluigi Paganini
January 14, 2022
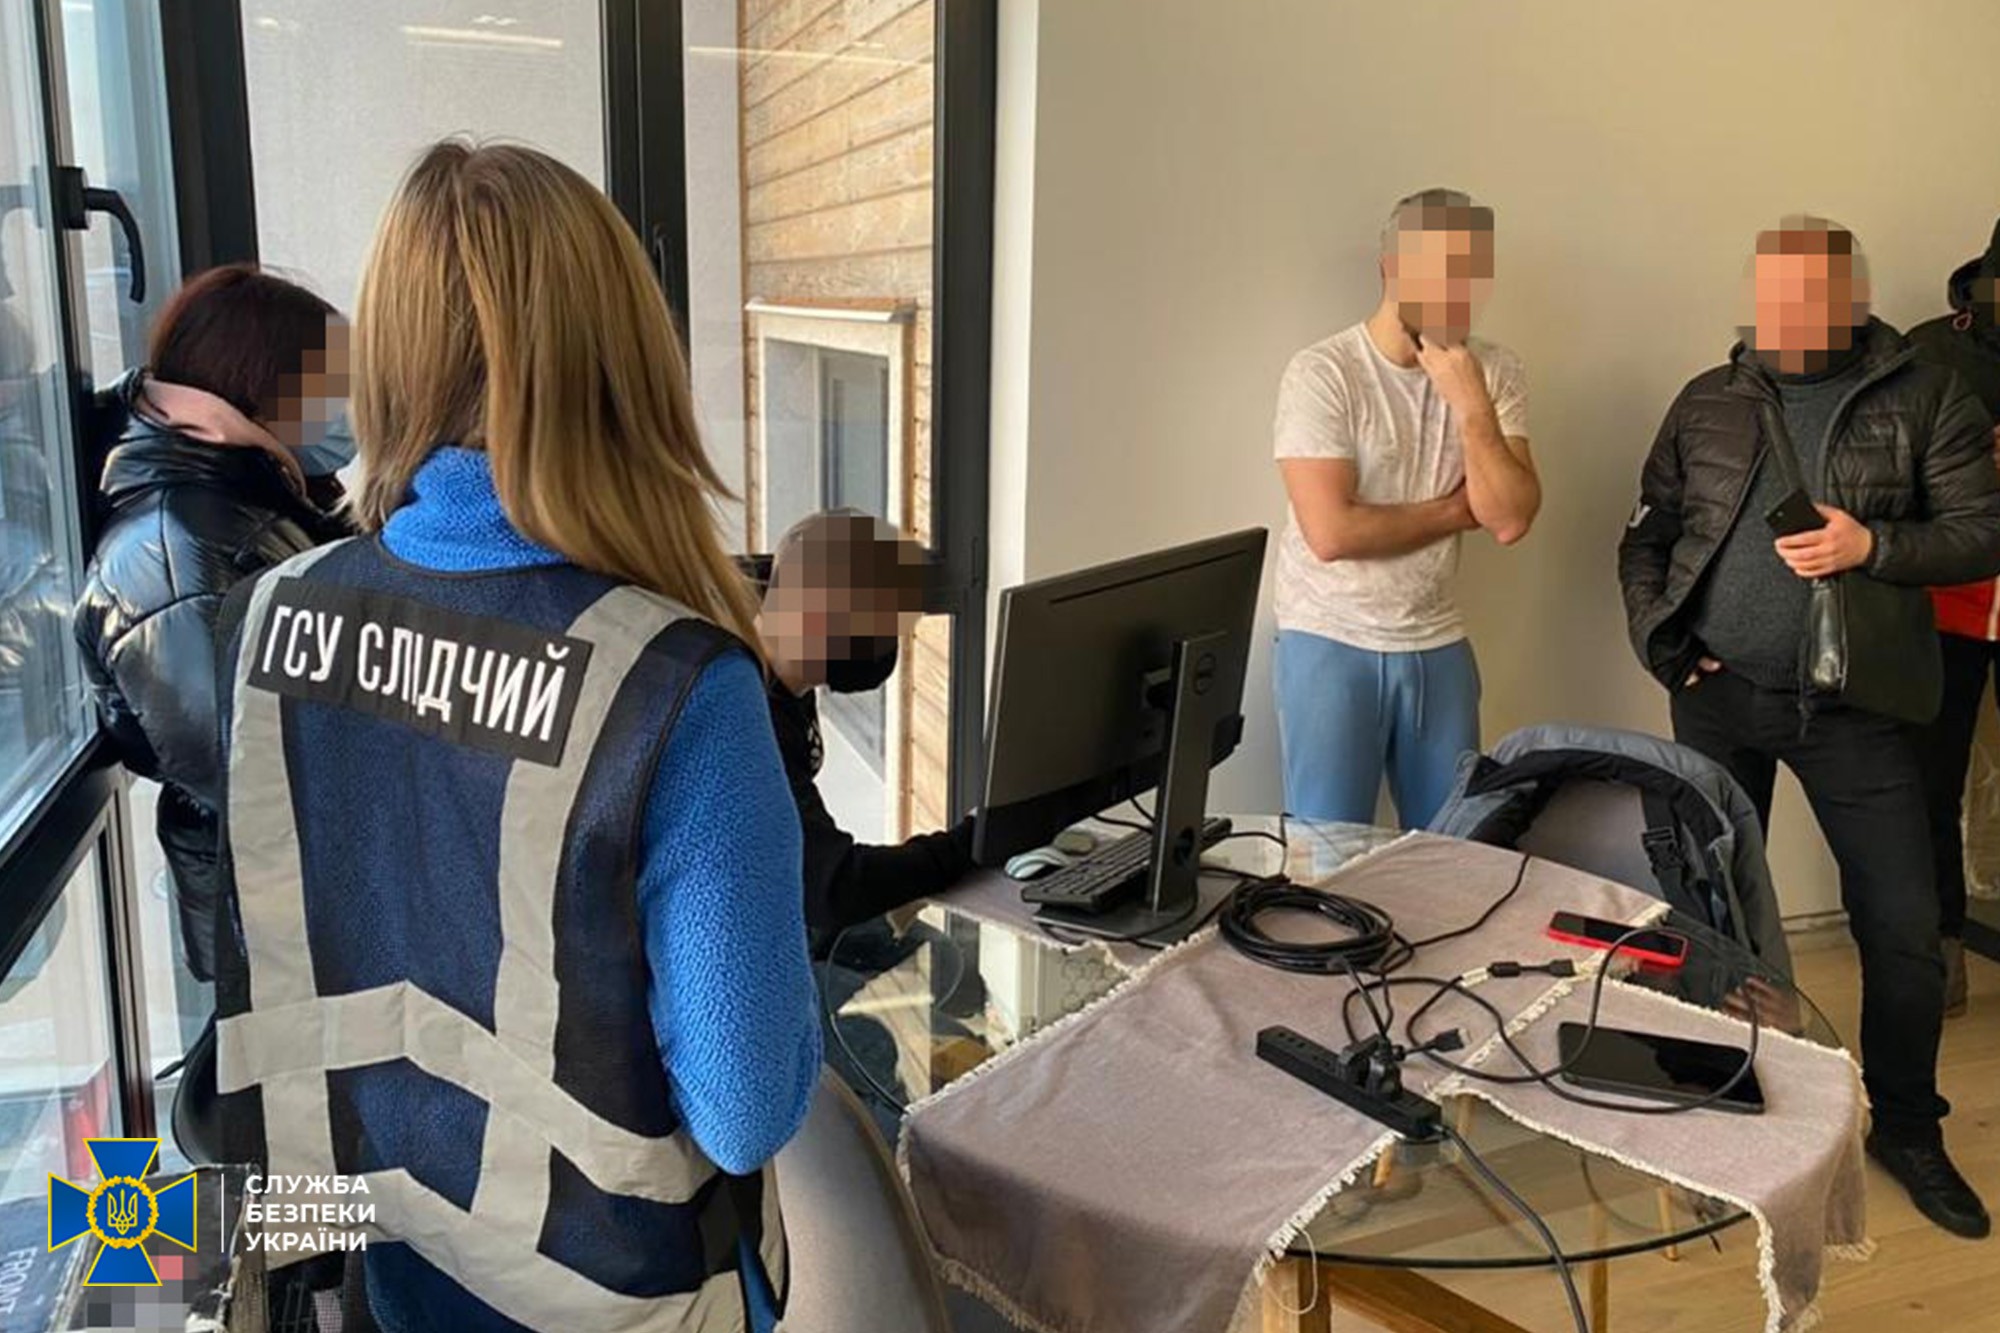
Ukrainian police arrested members of a ransomware gang that targeted at least 50 companies in the U.S. and Europe. Ukrainian police arrested members of a ransomware affiliate group that is responsible for attacking at least 50 companies in the U.S. and Europe. The operation was conducted by the SBU Cyber Department together with the Cyber […]
 Pierluigi Paganini
January 13, 2022
Cisco fixed a critical privilege escalation vulnerability, tracked as CVE-2022-20658, in Unified CCMP and Unified CCDM. Cisco released security patches to address a critical privilege escalation vulnerability, tracked as CVE-2022-20658, in Unified Contact Center Management Portal (Unified CCMP) and Unified Contact Center Domain Manager (Unified CCDM). A remote attacker could exploit the flaw to elevate […]
 Pierluigi Paganini
January 13, 2022
Mozilla addressed18 security vulnerabilities affecting the popular Firefox web browser and the Thunderbird mail program. Mozilla released Firefox 96 that addressed 18 security vulnerabilities in its web browser and the Thunderbird mail program. Nine vulnerabilities addressed by the new release are rated high-severity, the most severe one is a race condition issue tracked as CVE-2022-22746. […]
 Pierluigi Paganini
January 13, 2022
US Cyber Command (USCYBERCOM) has officially linked the Iran-linked MuddyWater APT group to Iran’s Ministry of Intelligence and Security (MOIS). USCYBERCOM has officially linked the Iran-linked MuddyWater APT group (aka SeedWorm and TEMP.Zagros) to Iran’s Ministry of Intelligence and Security (MOIS). The first MuddyWater campaign was observed in late 2017 when targeted entities in the Middle East. The experts called the campaign […]

Hacking / November 05, 2026
Cyber Crime / November 05, 2026